
Archived
blackpill
 shard77/blackpill
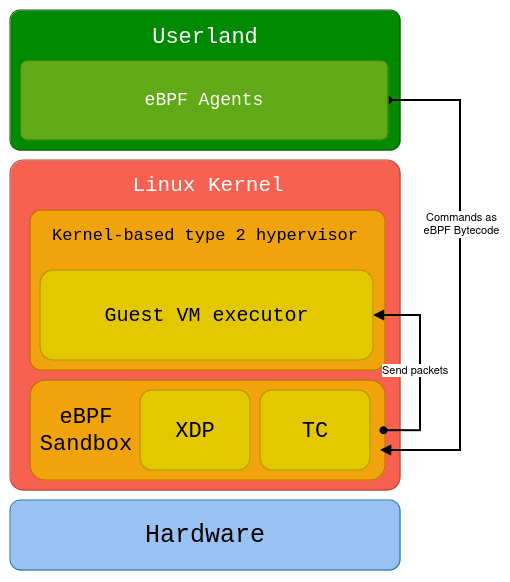
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
binary-exploitationcommand-and-controlids-ips-evasion+7
339
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 cecio/xenoboxx
Hardware Sandbox Toolkit
 oddcod3/phantom-evasion
Python antivirus evasion tool
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!

 egebalci/amber
Reflective PE packer.
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 s0md3v/nano
Nano is a family of PHP web shells which are code golfed for stealth.
 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 wra7h/flavortown
Various ways to execute shellcode