
ShellCodeEmulator
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
126
ohjeongwook/shellcodeemulatorShellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 bootsareme/copyfail-deconstructed
Easy-to-understand version of CVE-2026-31431
 zardus/ctf-tools
Some setup scripts for security research tools.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 saelo/cve-2018-4233
Exploit for CVE-2018-4233, a WebKit JIT optimization bug used during Pwn2Own 2018
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 backdoorskid/customloadimage
Stealthy .NET assembly loading using AssemblyNative::LoadFromBuffer
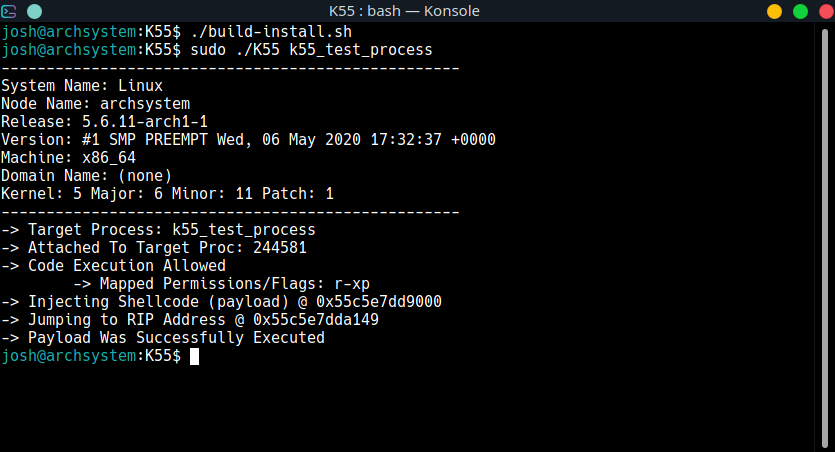
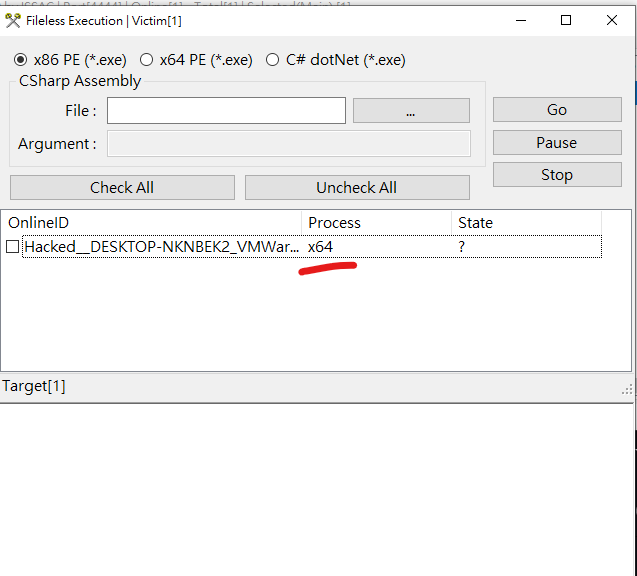 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 jasperla/cve-2017-9101
Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.