
CVE-2025-55182-RCE-shell
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
command-and-controlencryption-decryption-toolsexploitation+5
31
ruoji6/cve-2025-55182-rce-shellBurp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
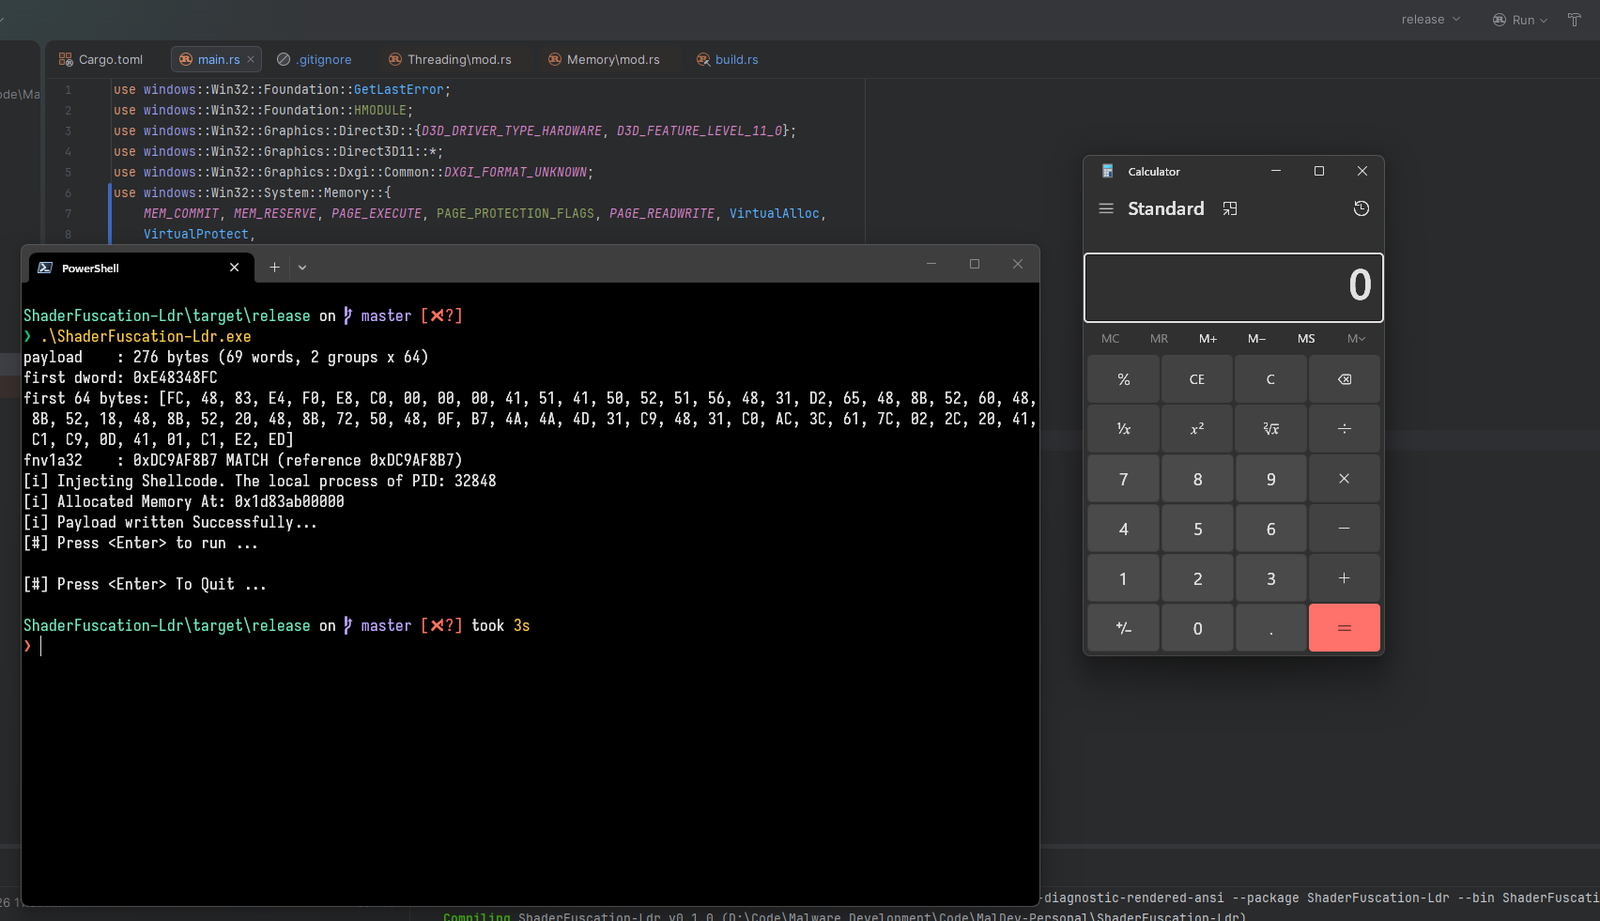 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 d3fudd/cve-2017-7494_sambacry
SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit
 superzerosec/cve-2020-7247
OpenSMTPD version 6.6.2 remote code execution exploit
 infenet/cve-2019-0708
Proof-of-concept exploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP, with shellcode for x86 systems. Intended for authorized security testing…
 passwa11/cve-2023-3519
Python exploit for CVE-2023-3519 targeting Citrix ADC with custom NASM shellcode, PHP backdoor deployment, and SUID privilege escalation.
 hakkuri01/r2rs
Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing
 thecybermind/w48crash
PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.
 aadi0258/exploit-cve-2024-23897
Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 u20024804/bash-4.3-fixed-cve-2014-6271
Patched GNU Bash 4.3 with fix for Shellshock (CVE-2014-6271). Provides a secure Bourne Again SHell with command-line editing, job control, and…
 u20024804/bash-3.2-fixed-cve-2014-6271
Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…
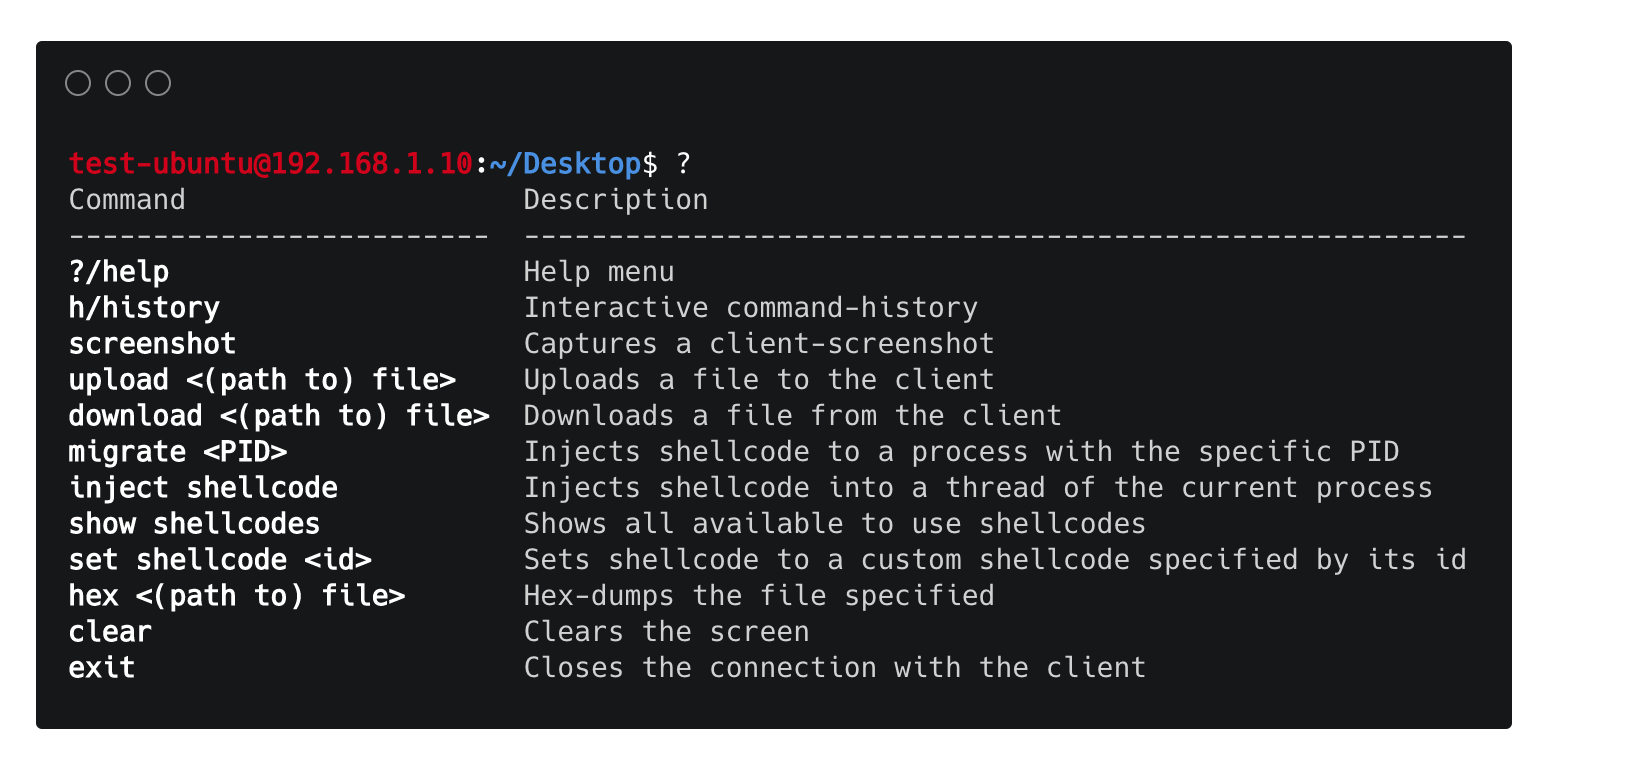 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
