
Analysis-for-stage1-shellcode-loader-from-hacking-
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
binary-analysiseducationmalware-analysis+2
spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-Analysis for stage1 shellcode loader from hacking
 ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflow
Automatic script written in python for CVE-2009-3999
 anonstorks/cve-2025-0282-full-version
# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
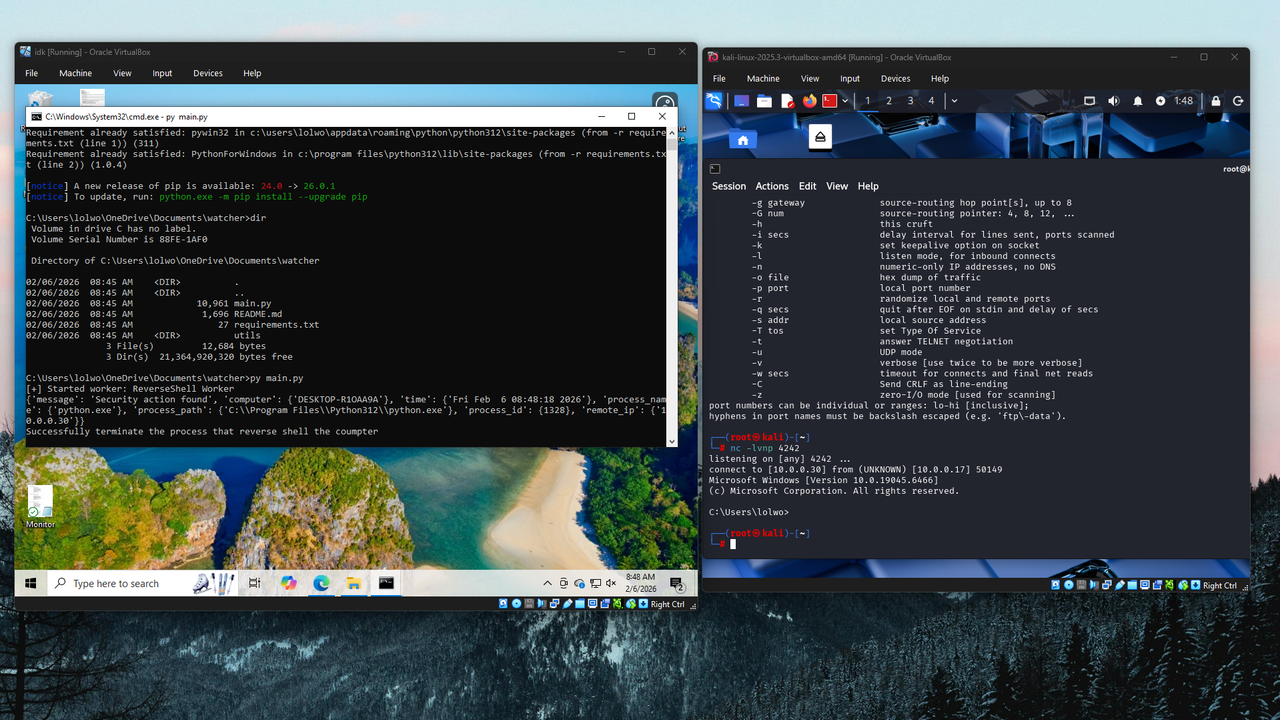 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 gmh5225/cve-2025-48799-
Proof-of-concept exploit for CVE-2025-48799, an Apache Tomcat remote code execution vulnerability. Demonstrates integer overflow exploitation via…
 jgs-developer/cve-2025-5548
Stack-based buffer overflow exploit for FreeFloat FTP Server, demonstrating reverse engineering, EIP control, and shellcode execution for educational…
 arthurhendrich/cve-2022-42475-poc
Exploit for CVE-2022-42475, a pre-auth RCE in FortiOS SSL VPN. Supports validation, benign verification, and full exploitation with connect-back…
 yaldobaoth/cve-2015-1578-poc
This is a proof-of-concept exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation leads to remote…
 davigsantana/cve-2023-50965
STACK BUFFER OVERFLOW EXPLOIT RESULTING IN REMOTE CODE EXECUTION
 u20024804/bash-3.2-fixed-cve-2014-6271
Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…
 u20024804/bash-4.3-fixed-cve-2014-6271
Patched GNU Bash 4.3 with fix for Shellshock (CVE-2014-6271). Provides a secure Bourne Again SHell with command-line editing, job control, and…
 sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
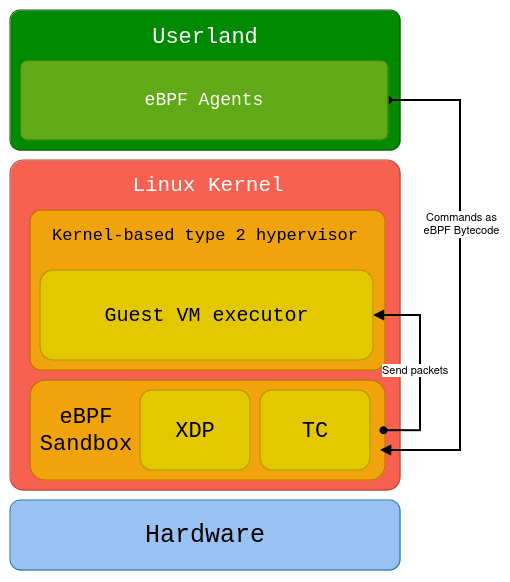 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 sensepost/ruler
A tool to abuse Exchange services