
RpcProxyInvoke
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
binary-exploitationcommand-and-controlexploitation+8
139
klezvirus/rpcproxyinvokeSimple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
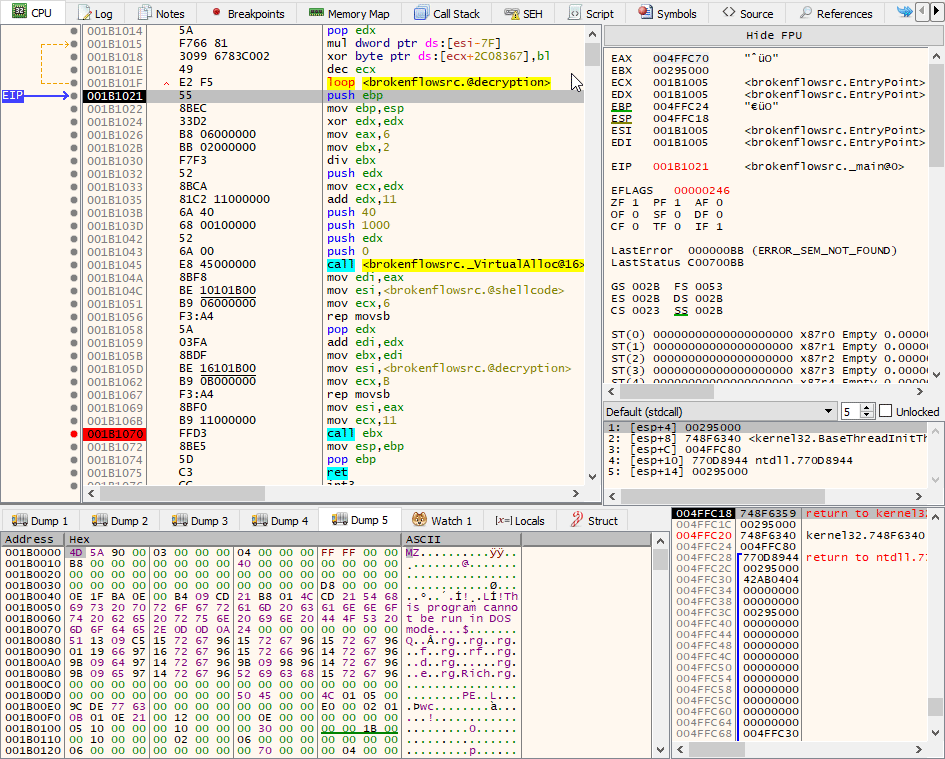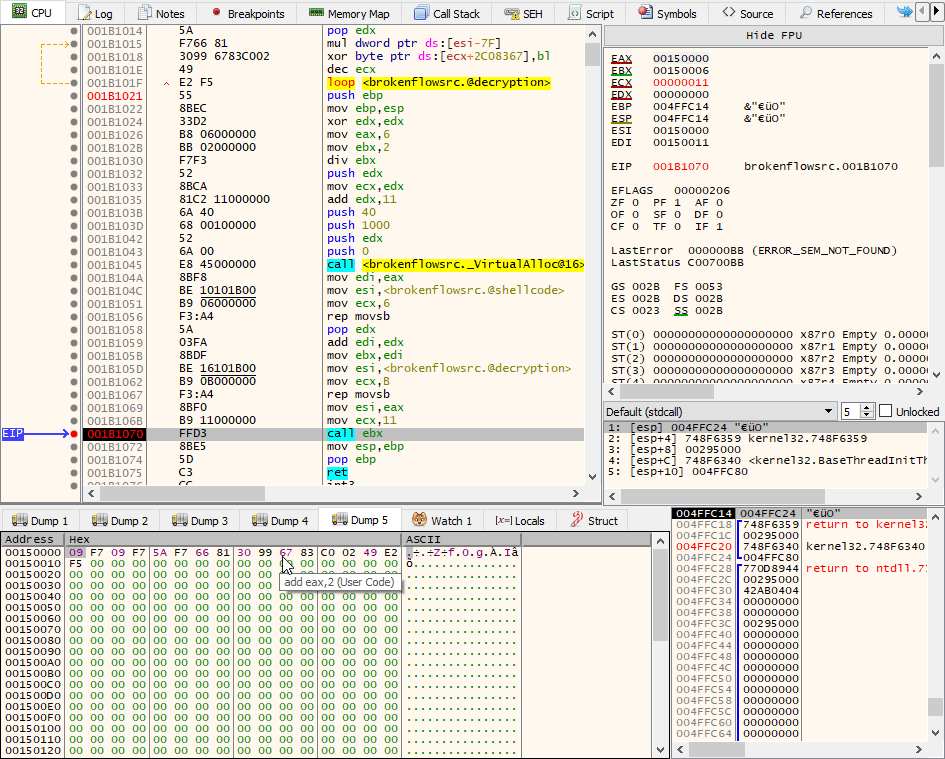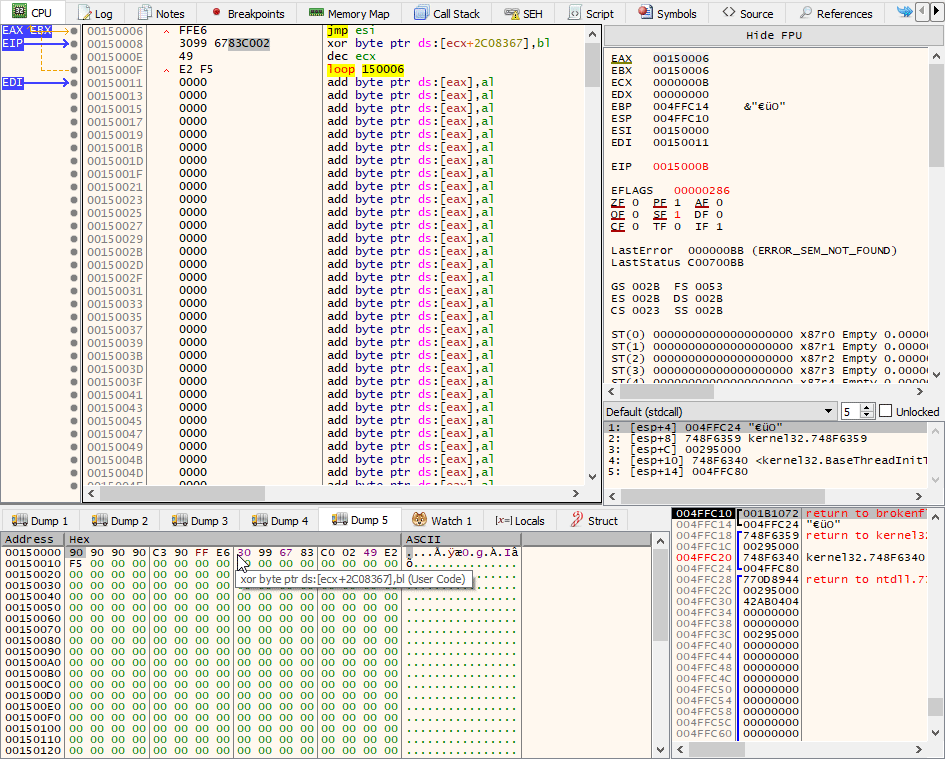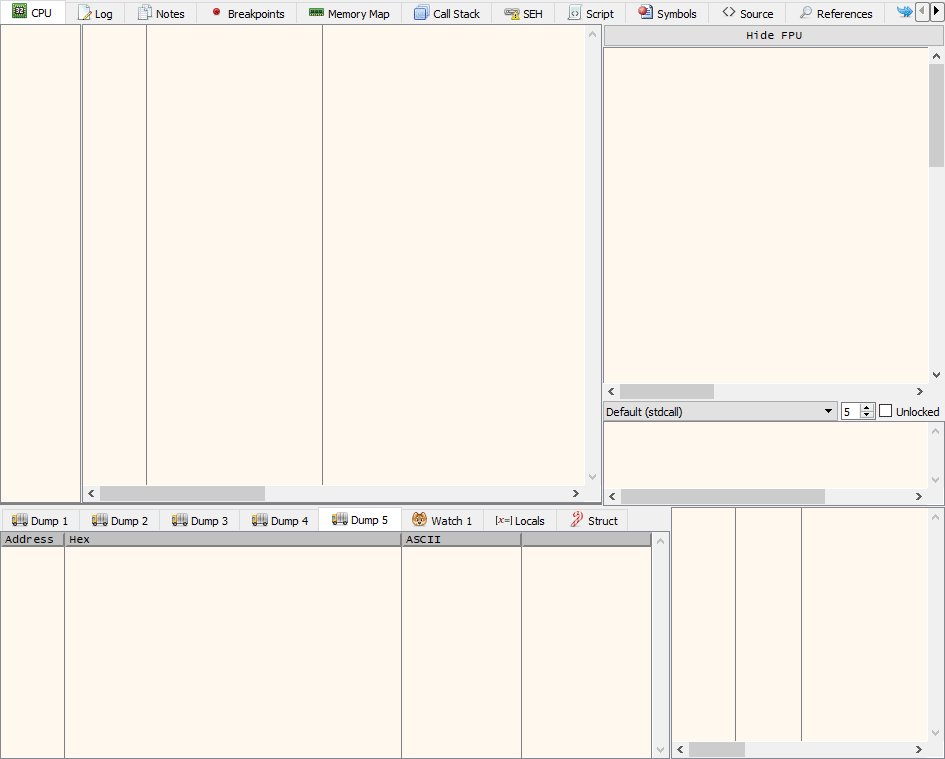 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell

 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
