

Sandman
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
command-and-controlpayload-generationpersistence-mechanisms+2
821
idov31/sandmanNTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
 redcode-labs/gosh
Golang reverse/bind shell generator
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
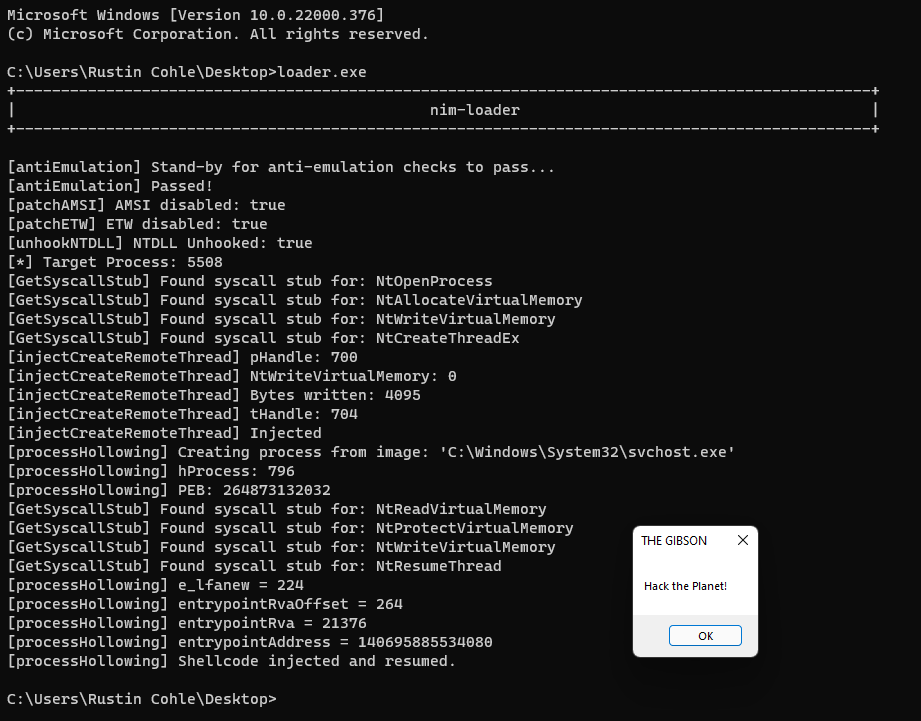 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
 ustayready/wnfexec
WNF Code Execution Library Using C#
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
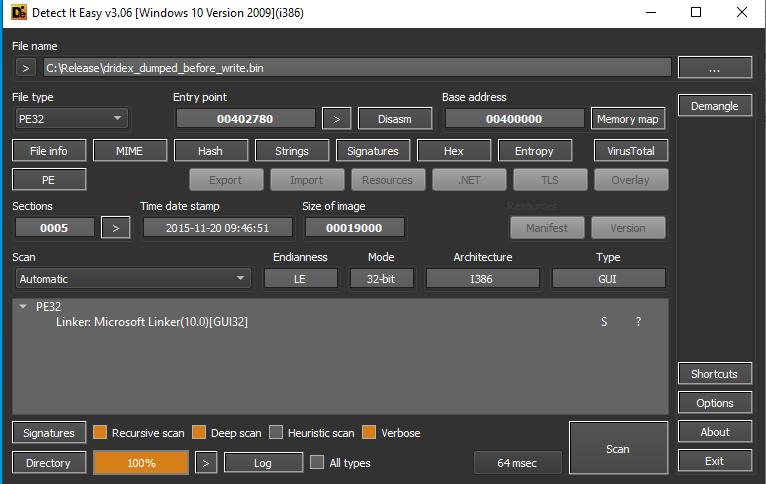 buzzer-re/shinigami
A dynamic unpacking tool
 0xdea/shellcode
A collection of my shellcode samples.
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 aydinnyunus/cve-2024-24576-exploit
CVE-2024-24576 Proof of Concept
 sh4den/cve-2022-23093
The FreeBSD ICMP buffer overflow, freebsd buffer overflow poc
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…