

Pokemon-Shellcode-Loader
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
adversarial-attackpayload-developmentpayload-generation+3
techryptic/pokemon-shellcode-loaderTired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
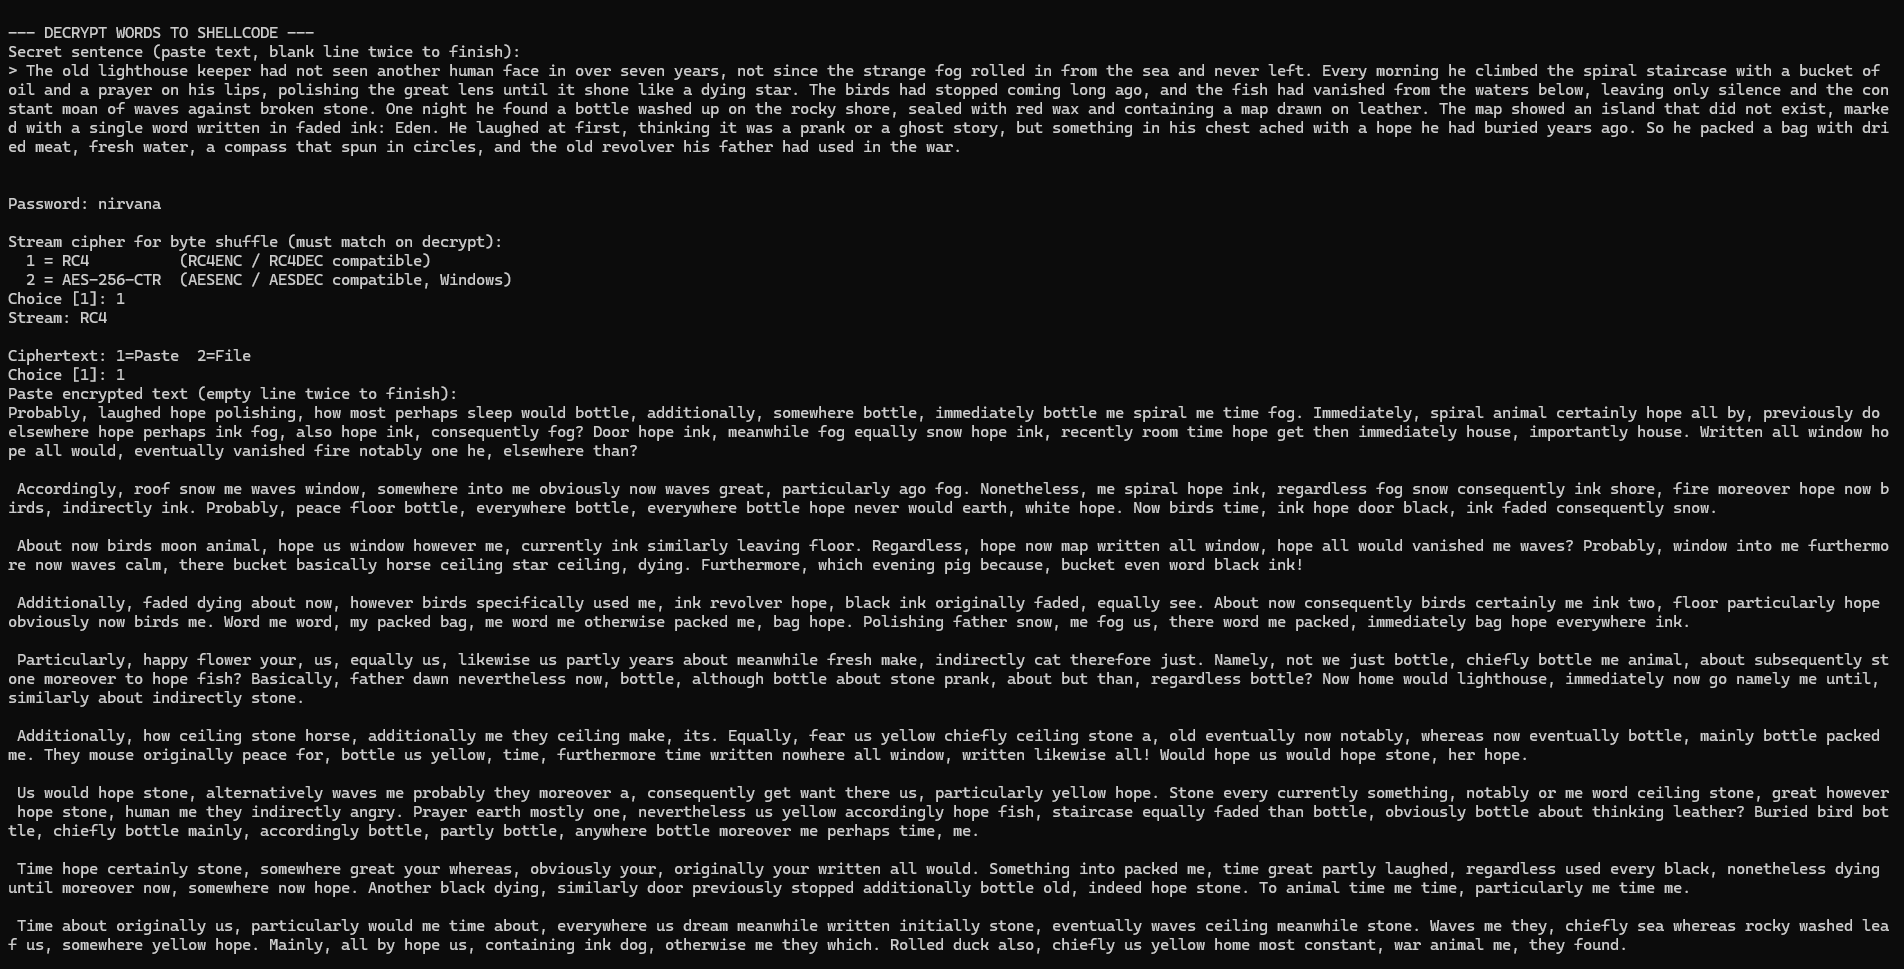 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
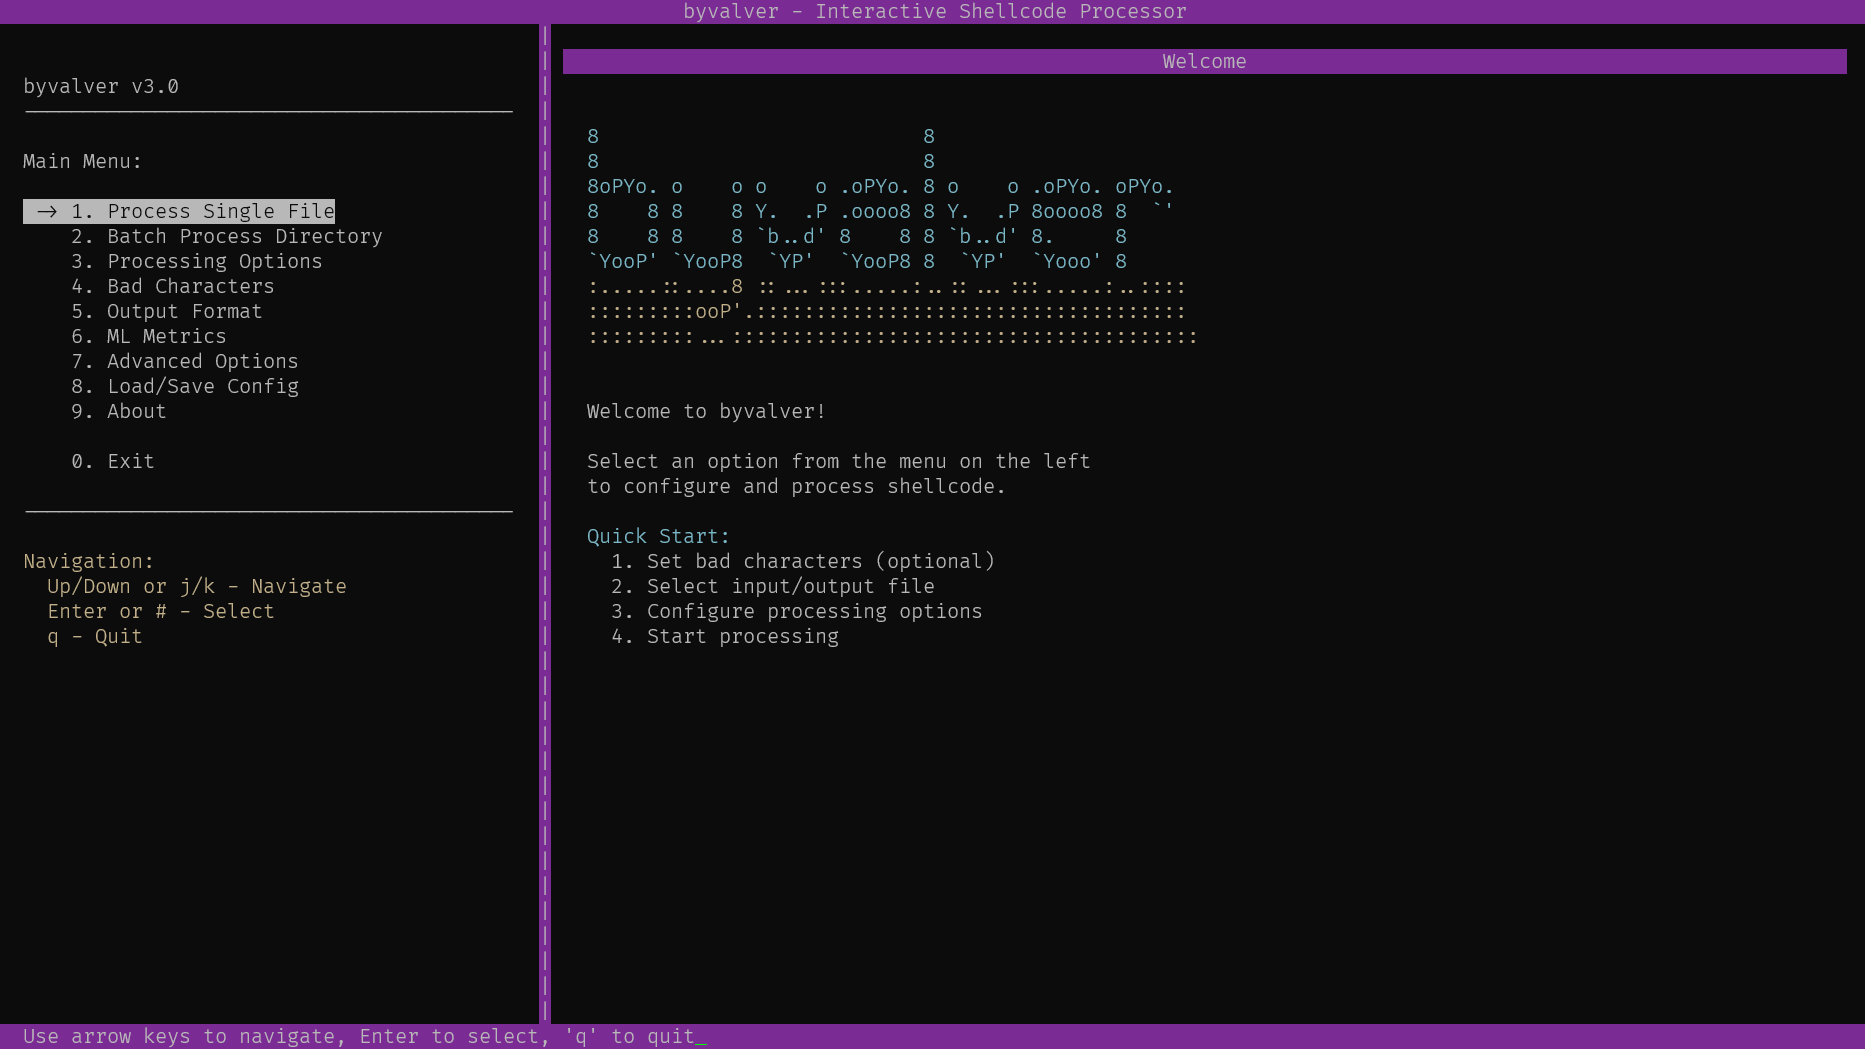 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
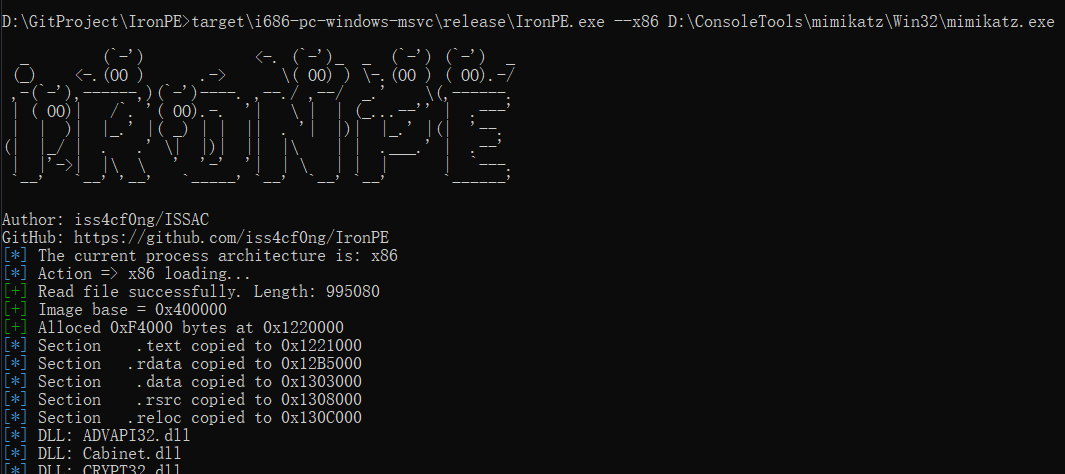 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 m0x41nos/timeafterfree
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 sfewer-r7/cve-2025-22457
PoC for CVE-2025-22457 - A remote unauthenticated stack based buffer overflow affecting Ivanti Connect Secure, Pulse Connect Secure, Ivanti Policy…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 maxpl0it/cve-2019-17026-exploit
An exploit for CVE-2019-17026. It pops xcalc and was tested on Ubuntu (x64).
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
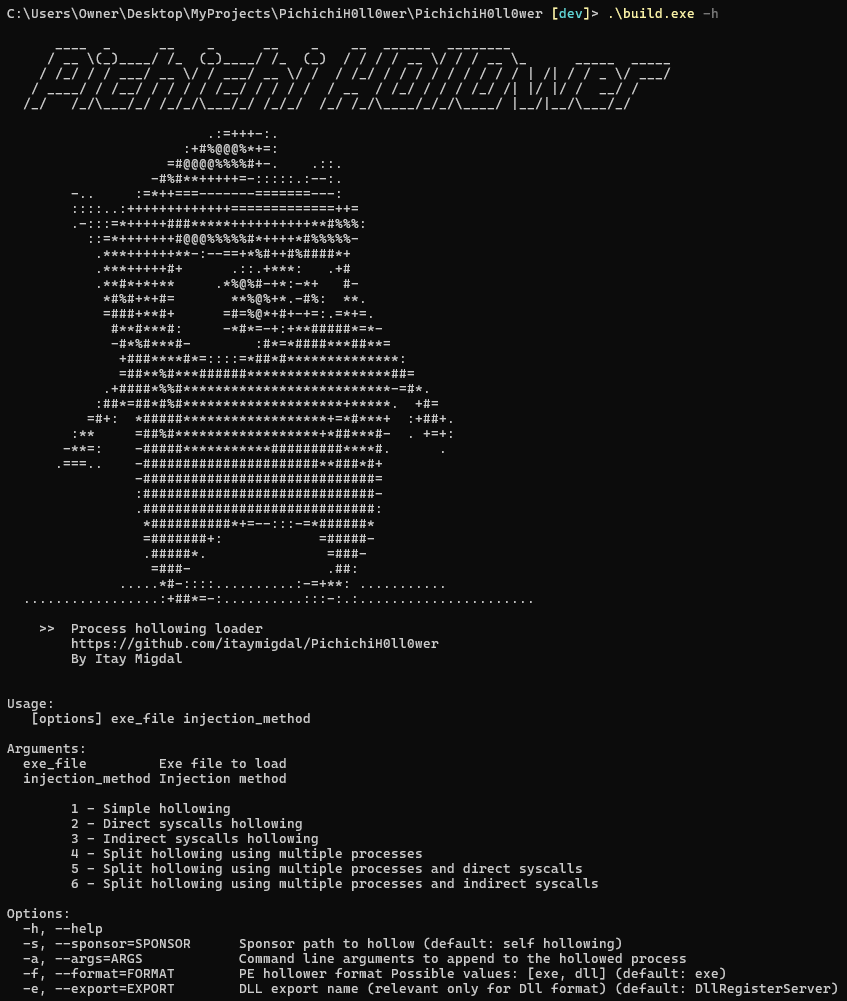 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…