

amber
 egebalci/amber
Reflective PE packer.
binary-exploitationencryption-decryption-toolsexploitation+6
egebalci/amberReflective PE packer.
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
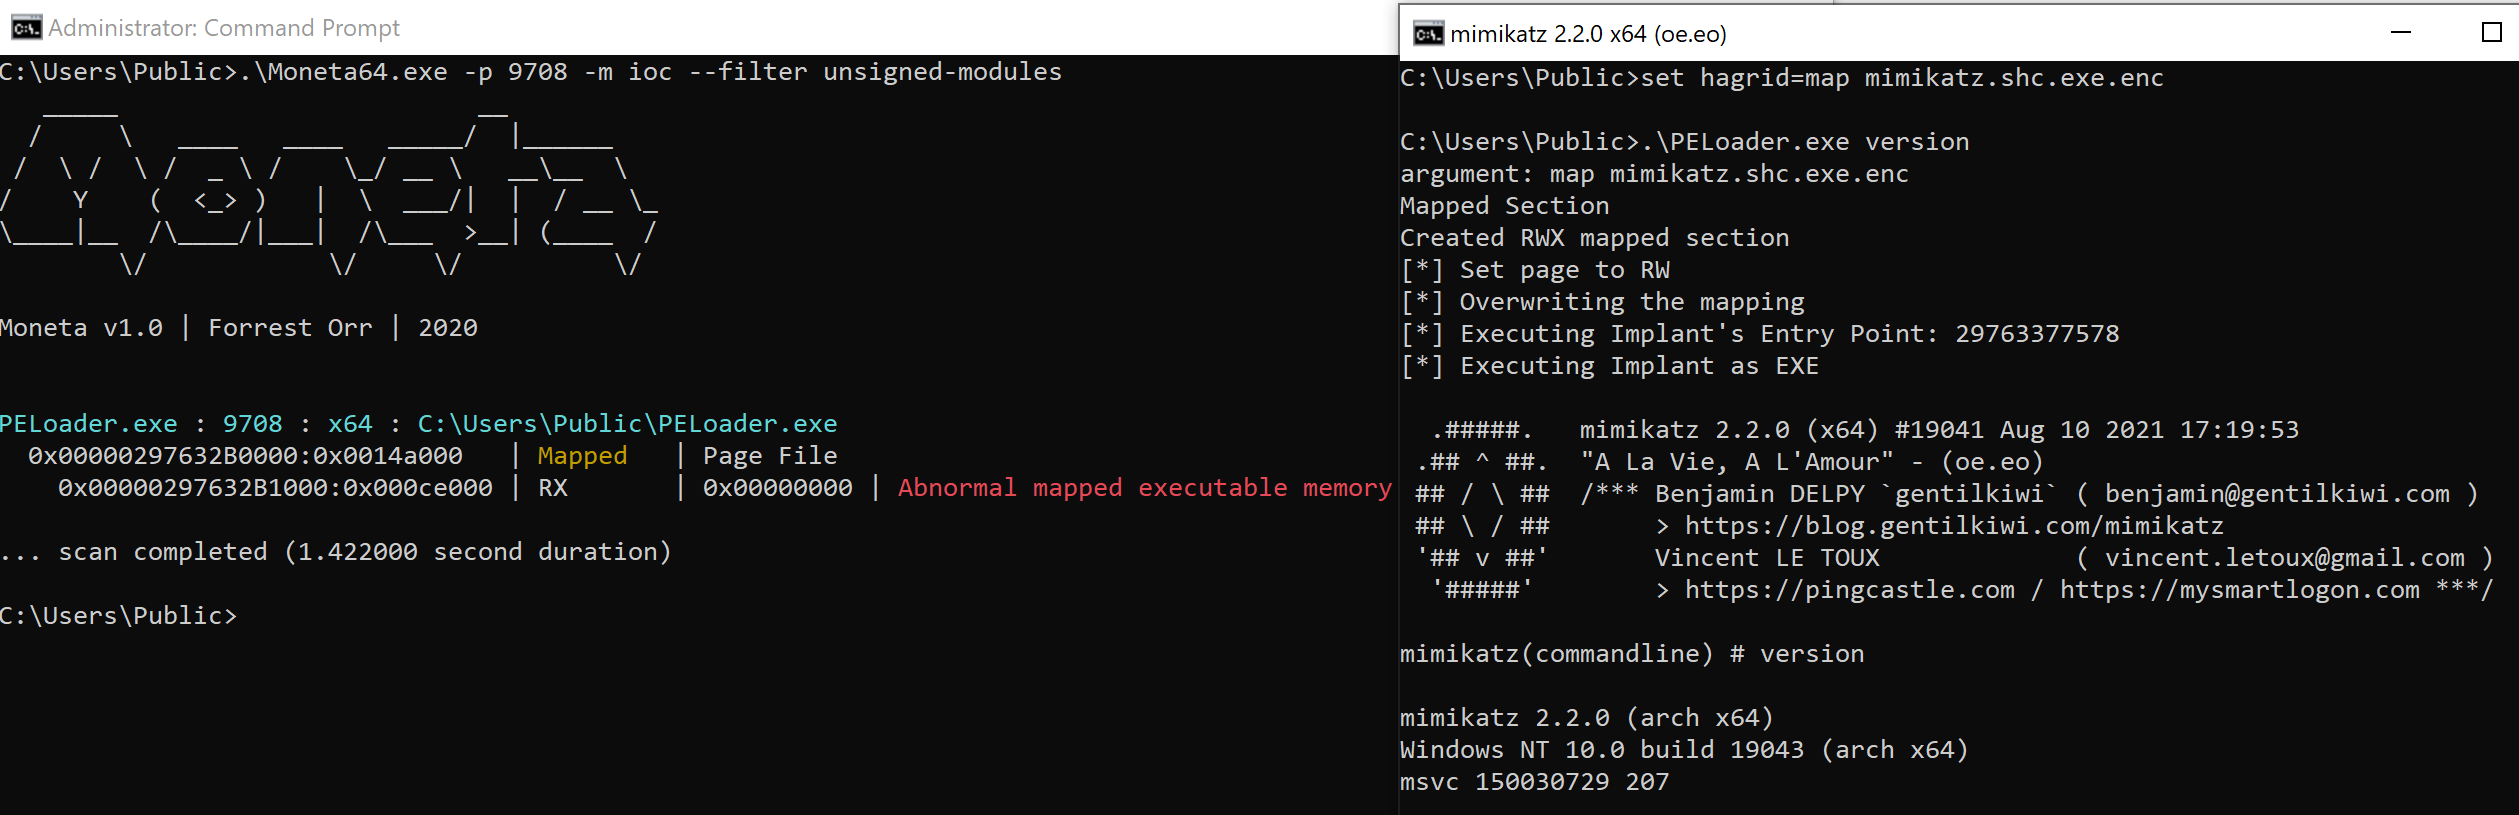 hagrid29/peloader
PE loader with various shellcode injection techniques
 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
 noperator/cve-2019-18935
RCE exploit for a .NET JSON deserialization vulnerability in Telerik UI for ASP.NET AJAX.
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
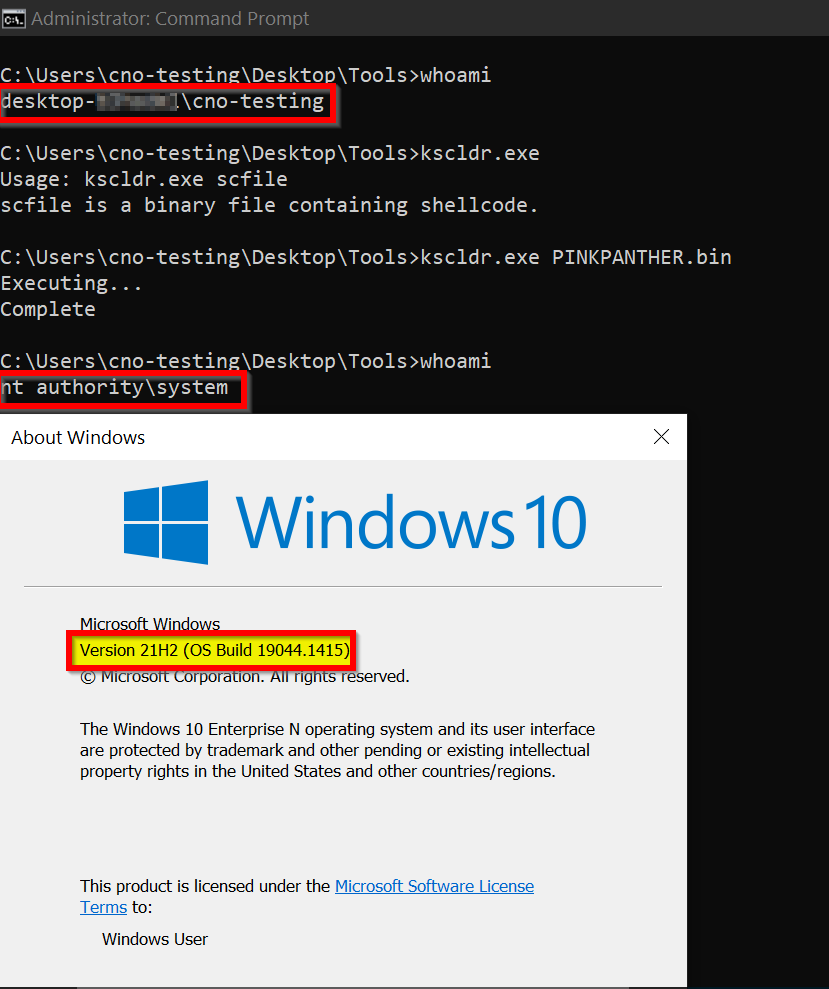 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
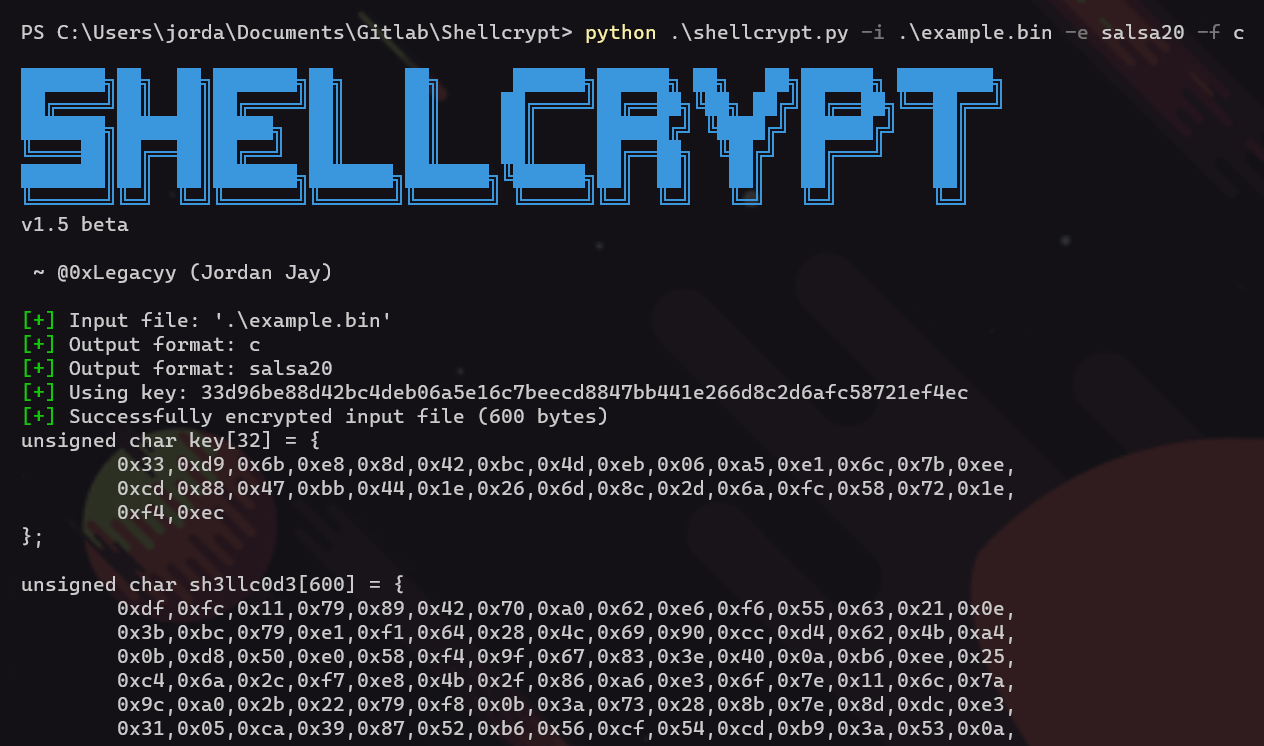 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 cryptogenic/ps4-6.20-webkit-code-execution-exploit
A WebKit exploit using CVE-2018-4441 to obtain RCE on PS4 6.20.
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC