
BrokenFlow
 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
binary-exploitationencryption-decryption-toolsexploitation+4
115
enkomio/brokenflowA simple PoC to invoke an encrypted shellcode by using an hidden call
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 d3fudd/cve-2017-7494_sambacry
SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit
 superzerosec/cve-2020-7247
OpenSMTPD version 6.6.2 remote code execution exploit
 k3ystr0k3r/cve-2026-24061
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 infenet/cve-2019-0708
Proof-of-concept exploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP, with shellcode for x86 systems. Intended for authorized security testing…
 vuducmanhno100-cloud/cve-2024-6387
CVE-2024-6387 POC (Currently being edited)
 thecybermind/w48crash
PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 u20024804/bash-3.2-fixed-cve-2014-6271
Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…
 ch0pin/aviator
Antivirus evasion project
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
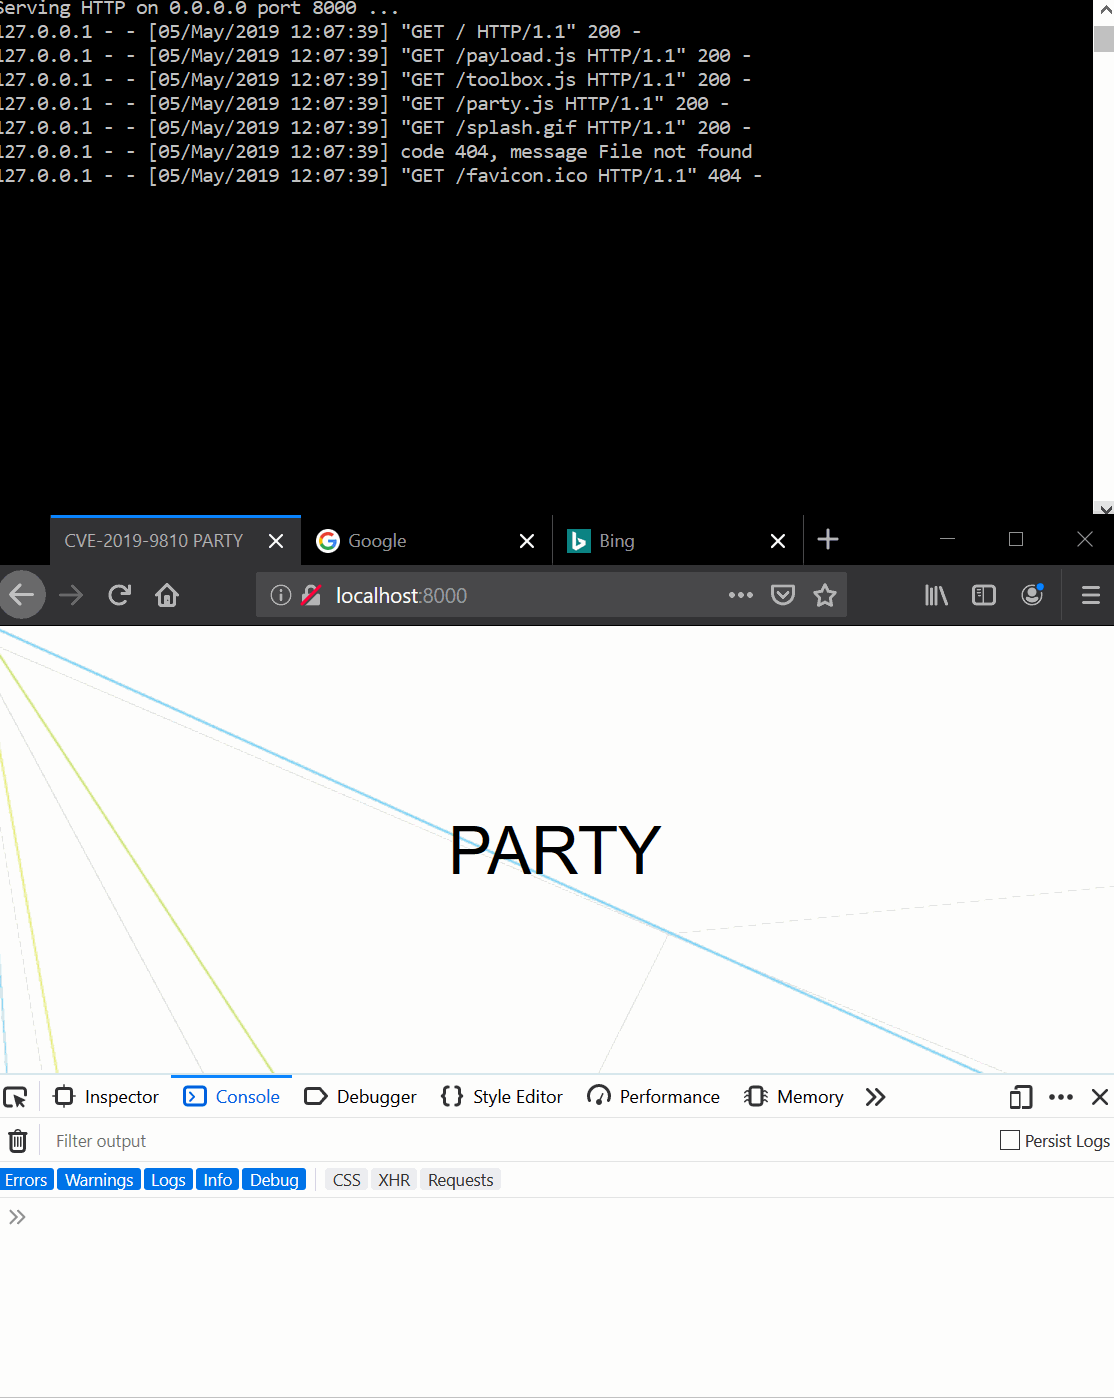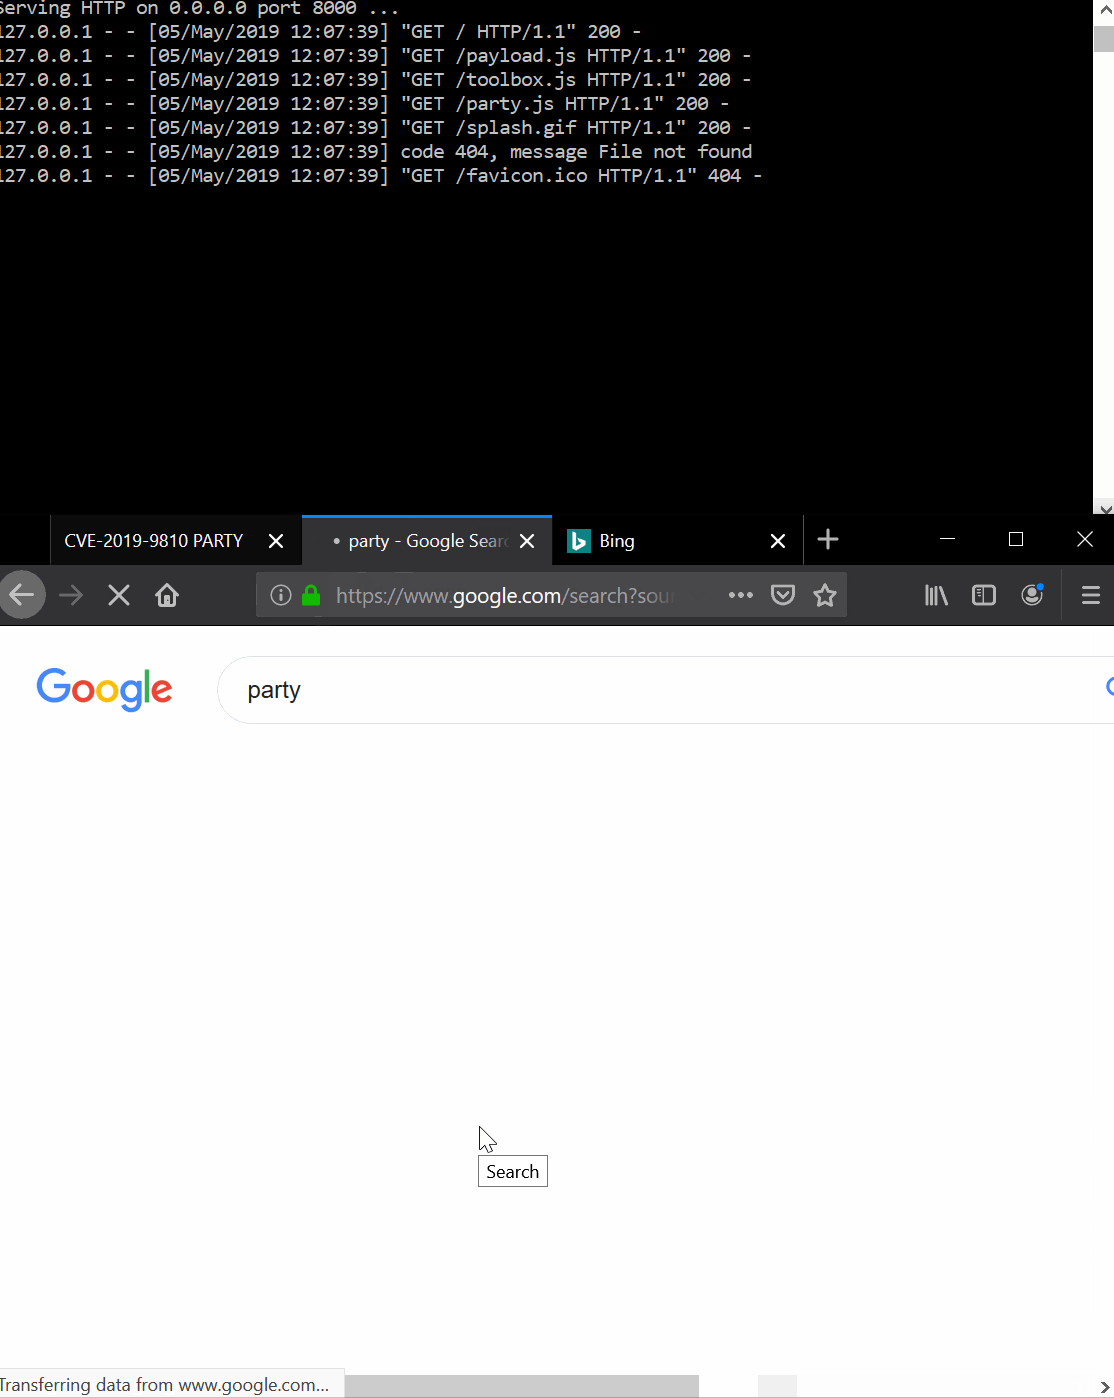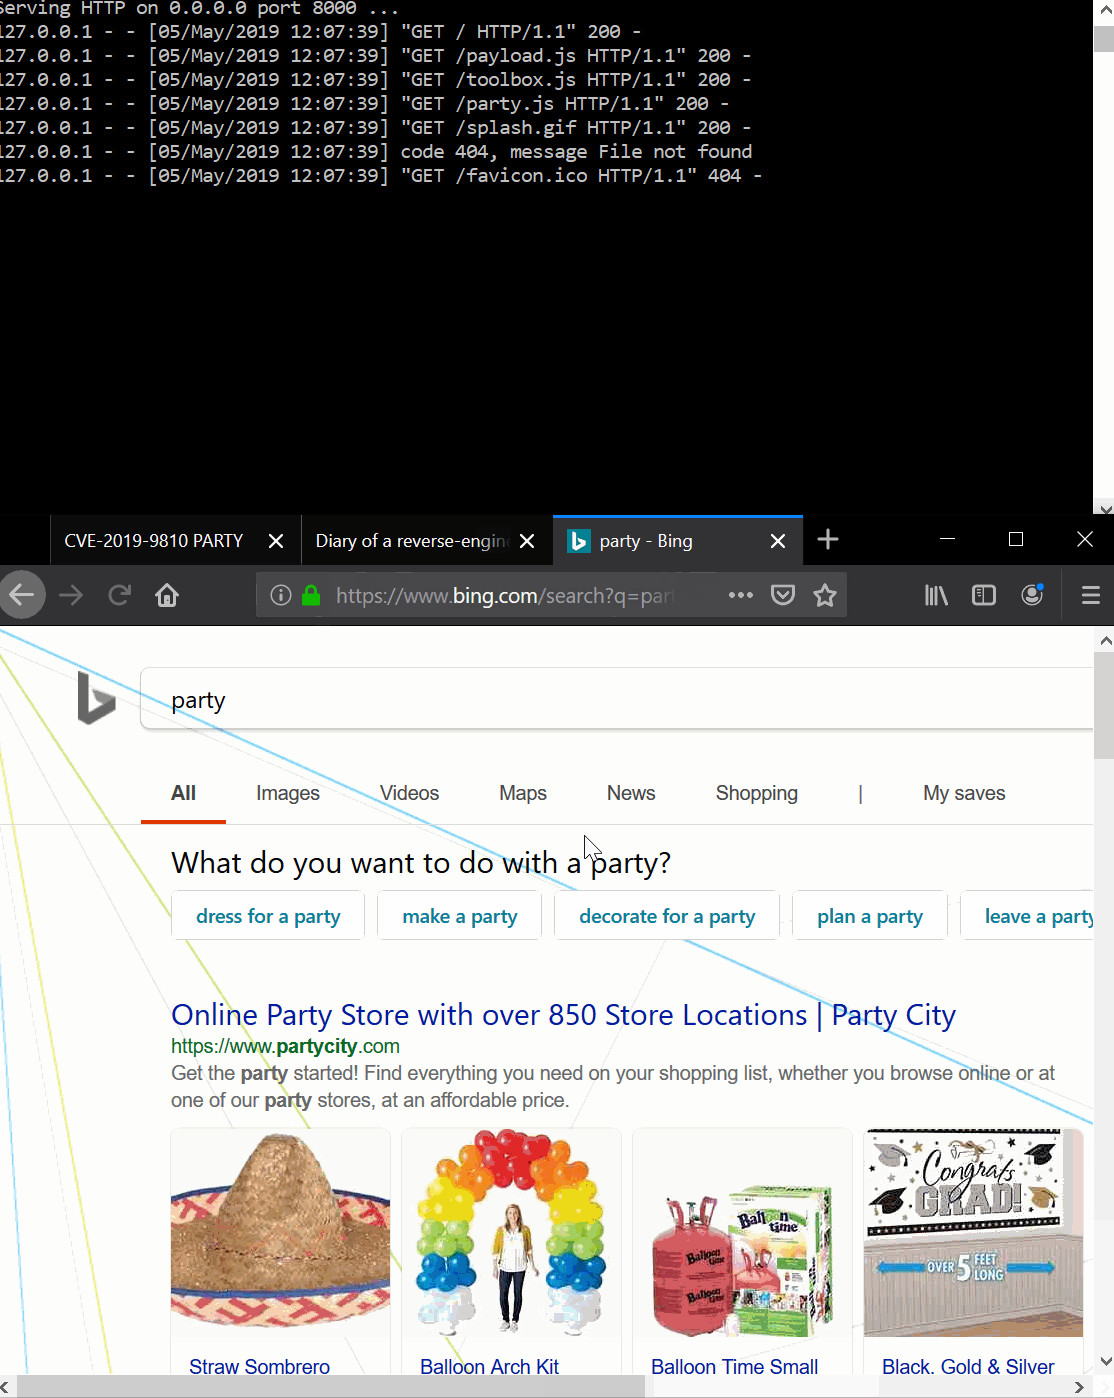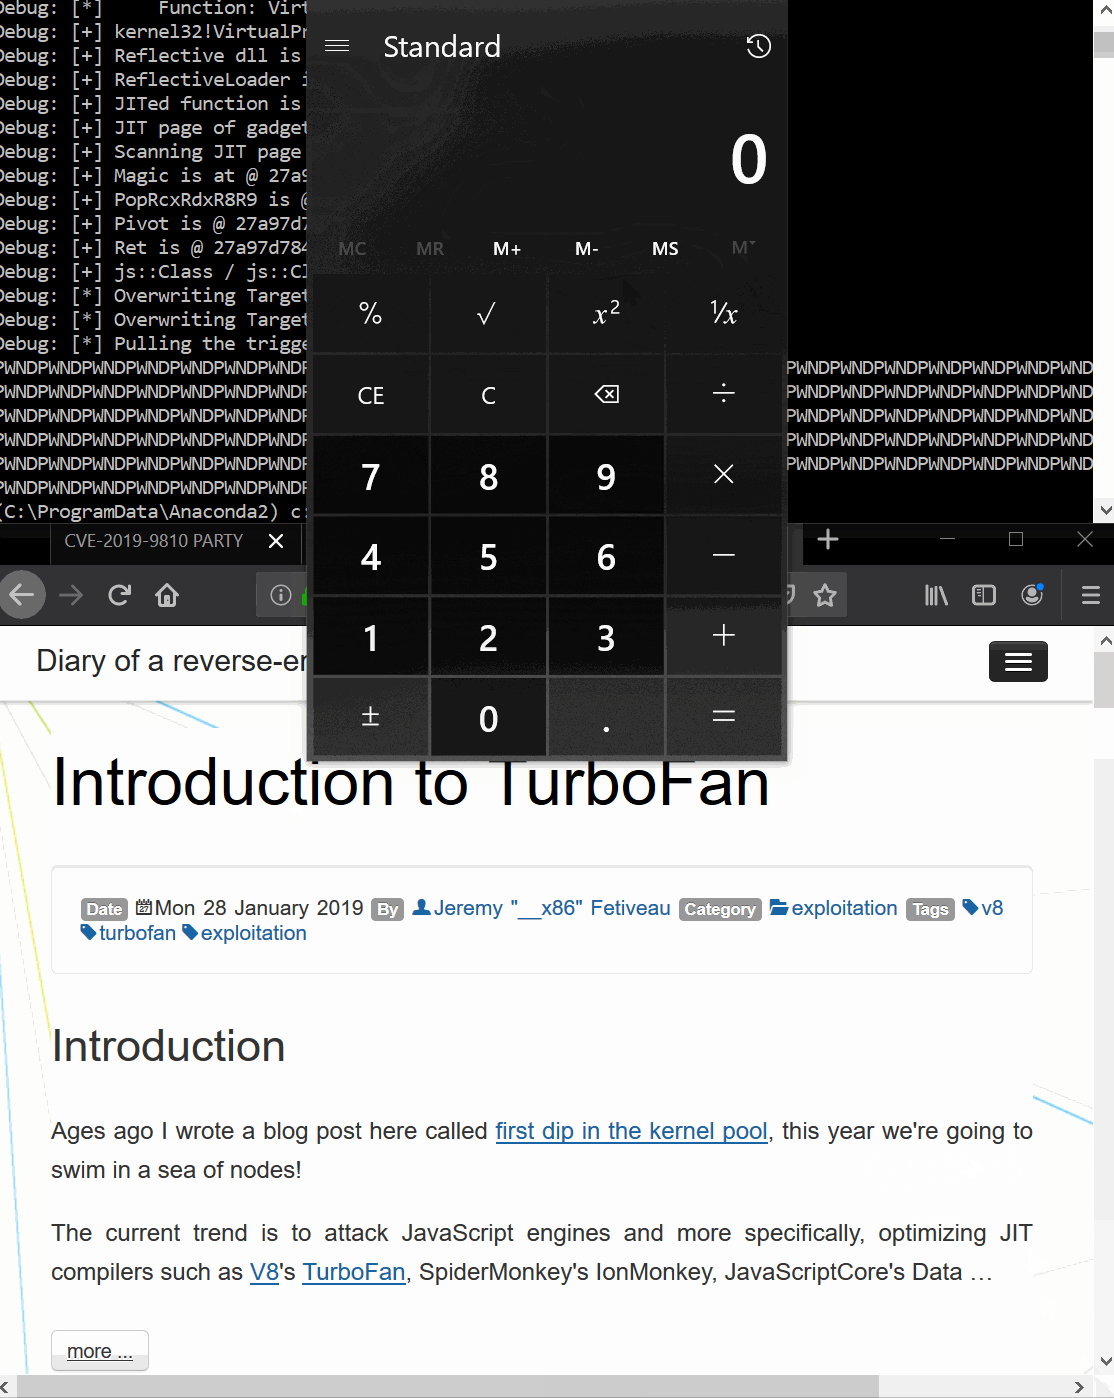 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
 algo7/bluekeep_cve-2019-0708_poc_to_exploit
An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits