

sploit
 zznop/sploit
Go package that aids in binary analysis and exploitation
binary-analysisbinary-exploitationctf+6
zznop/sploitGo package that aids in binary analysis and exploitation
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 struppigel/hedgehog-tools
Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
 bohops/dynamicdotnet
A collection of various and sundry code snippets that leverage .NET dynamic tradecraft
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
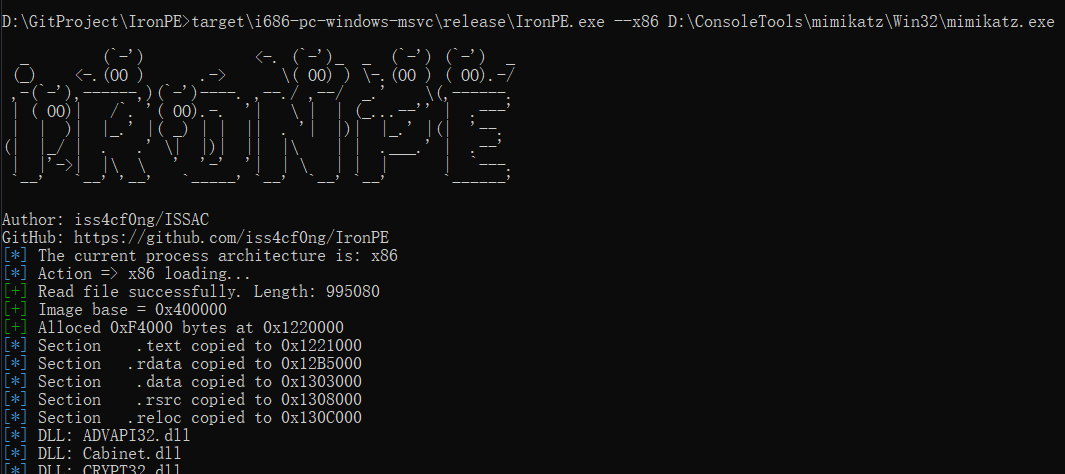 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 m0x41nos/timeafterfree
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.