
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
843 results
bowcaster preview

bowcaster

GitHubzcutlip/bowcaster

Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
binary-exploitationembedded-systems-securityexploitation+6
138
8 years ago
Phantom-Evasion-Loader preview

Phantom-Evasion-Loader

GitHubjm00nj/phantom-evasion-loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
binary-exploitationcommand-and-controleducation+6
1111 month ago
DuplexSpyCS preview

DuplexSpyCS

GitHubiss4cf0ng/duplexspycs

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…

command-and-controleducationpayload-development+5
2216 months ago
ntqueueapcthreadex-ntdll-gadget-injection preview

ntqueueapcthreadex-ntdll-gadget-injection

GitHublloydlabs/ntqueueapcthreadex-ntdll-gadget-injection

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
adversarial-attackids-ips-evasionpayload-development+3
2683 years ago
Simple-Polymorphic-Engine-SPE32 preview

Simple-Polymorphic-Engine-SPE32

GitHubpelock/simple-polymorphic-engine-spe32

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
encryption-decryption-toolsmalware-analysisreverse-engineering+1
1543 years ago
dropengine preview

dropengine

GitHubs0lst1c3/dropengine

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
defensive-toolsexploit-frameworkspayload-development+5
2145 years ago
ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent preview

ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent

GitHubjm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent

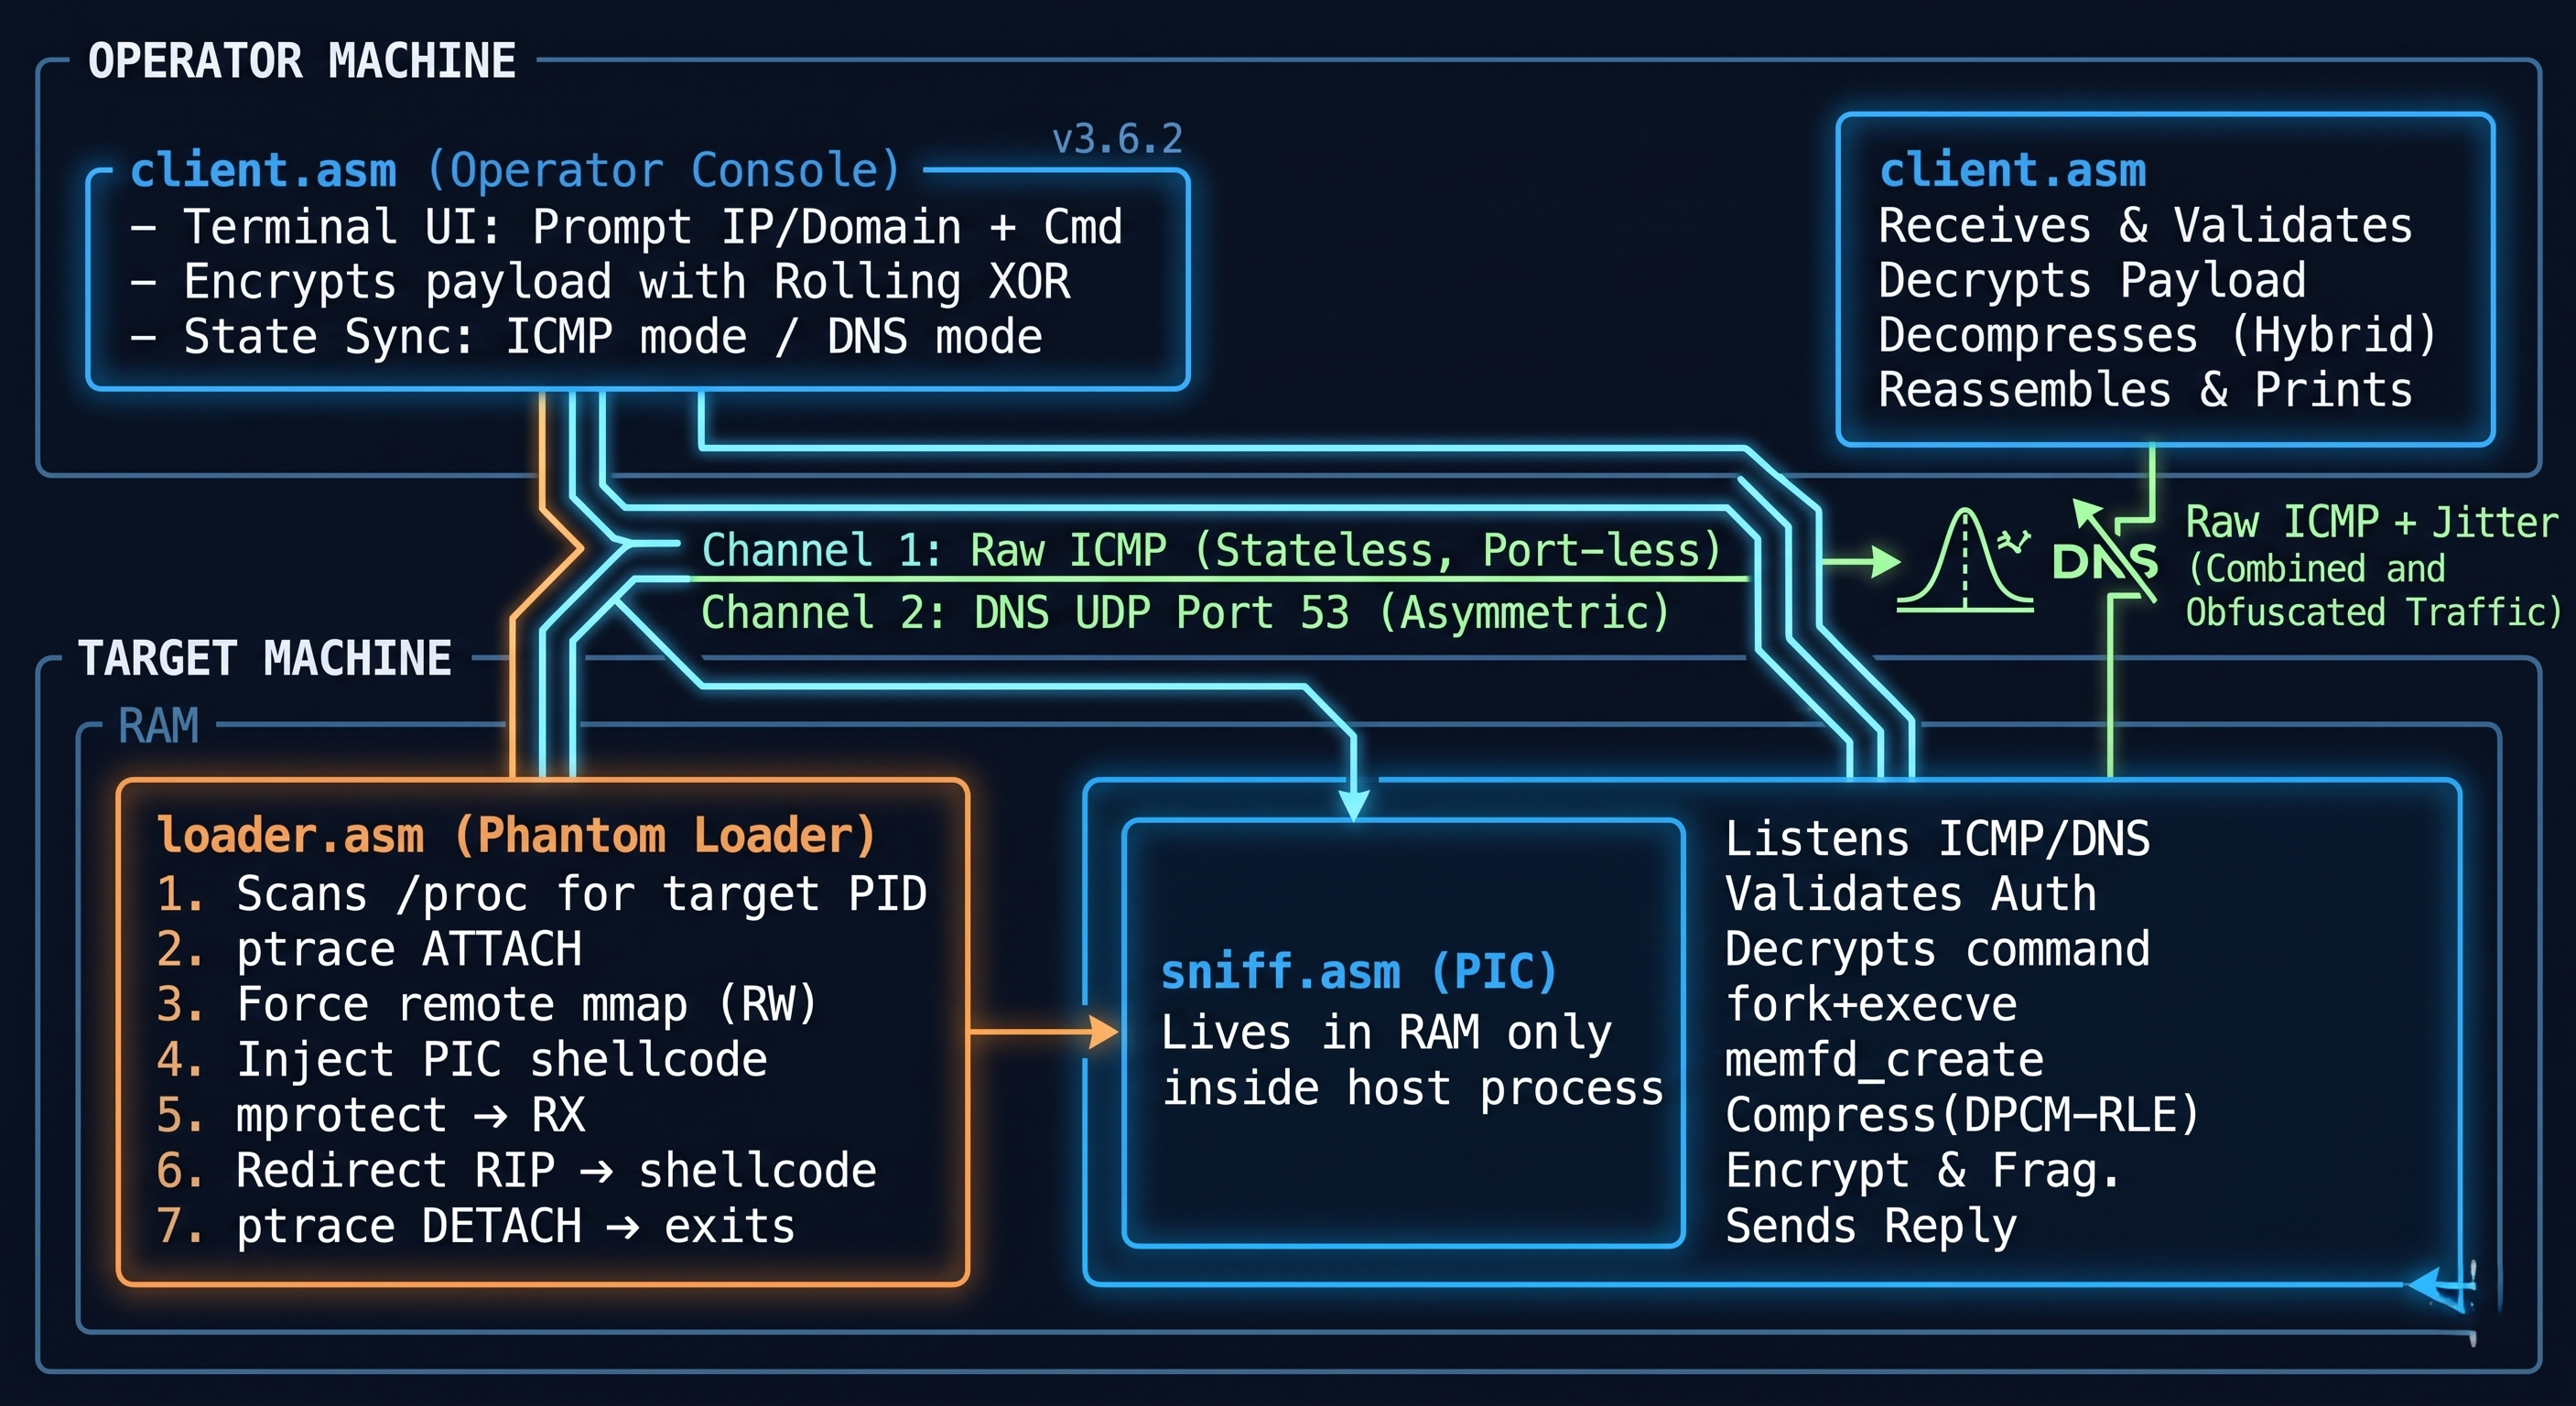
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
command-and-controlexploit-frameworksids-ips-evasion+5
9326 days ago
REW-sploit preview

REW-sploit

GitHubrew-sploit/rew-sploit

Emulate and Dissect MSF and *other* attacks
bluetooth-securitydebuggersdefensive-tools+6
1442 years ago
hedgehog-tools preview

hedgehog-tools

GitHubstruppigel/hedgehog-tools

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…

binary-analysisdynamic-analysis-sandboxingforensics+4
1442 months ago
ByteCaster preview

ByteCaster

GitHubprint3m/bytecaster

Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
encryption-decryption-toolspayload-developmentred-teaming+1
2306 months ago
CVE-2024-6387 preview

CVE-2024-6387

GitHubl0n3m4n/cve-2024-6387

PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
exploitationnetwork-securitypayload-development+6
1132 years ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
binary-analysiseducationlabs-practice+6
1591 year ago
asminject preview

asminject

GitHubbishopfox/asminject

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
container-escapepayload-developmentpenetration-testing+2
1493 years ago
ds3-nrssr-rce preview

ds3-nrssr-rce

GitHubtremwil/ds3-nrssr-rce

Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
binary-exploitationeducationexploitation+8
1694 years ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…

binary-exploitationexploitationmalware-analysis+6
1279 months ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
binary-analysiscommand-and-controlencryption-decryption-tools+5
1153 months ago
shellcodetester preview

shellcodetester

GitHubhelviojunior/shellcodetester

An application to test windows and linux shellcodes
binary-analysisexploitationpayload-development+2
941 year ago
DynamicDotNet preview

DynamicDotNet

GitHubbohops/dynamicdotnet

A collection of various and sundry code snippets that leverage .NET dynamic tradecraft

curated-resourceseducationmalware-analysis+4
1452 years ago
Previous1…567…47Next