chamilo-lms-unauthenticated-rce-poc

This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220

This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

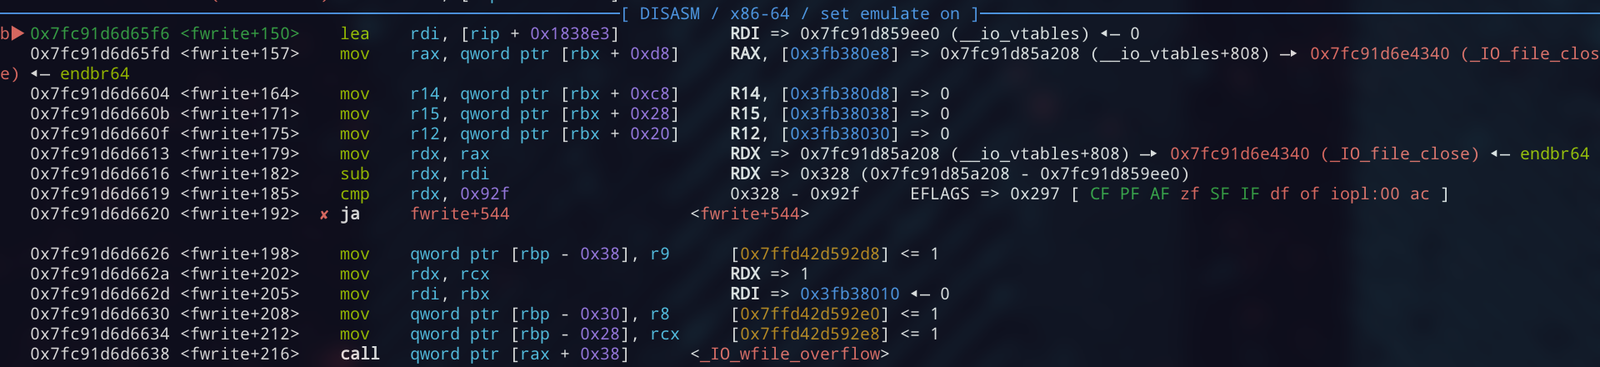
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…

Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…

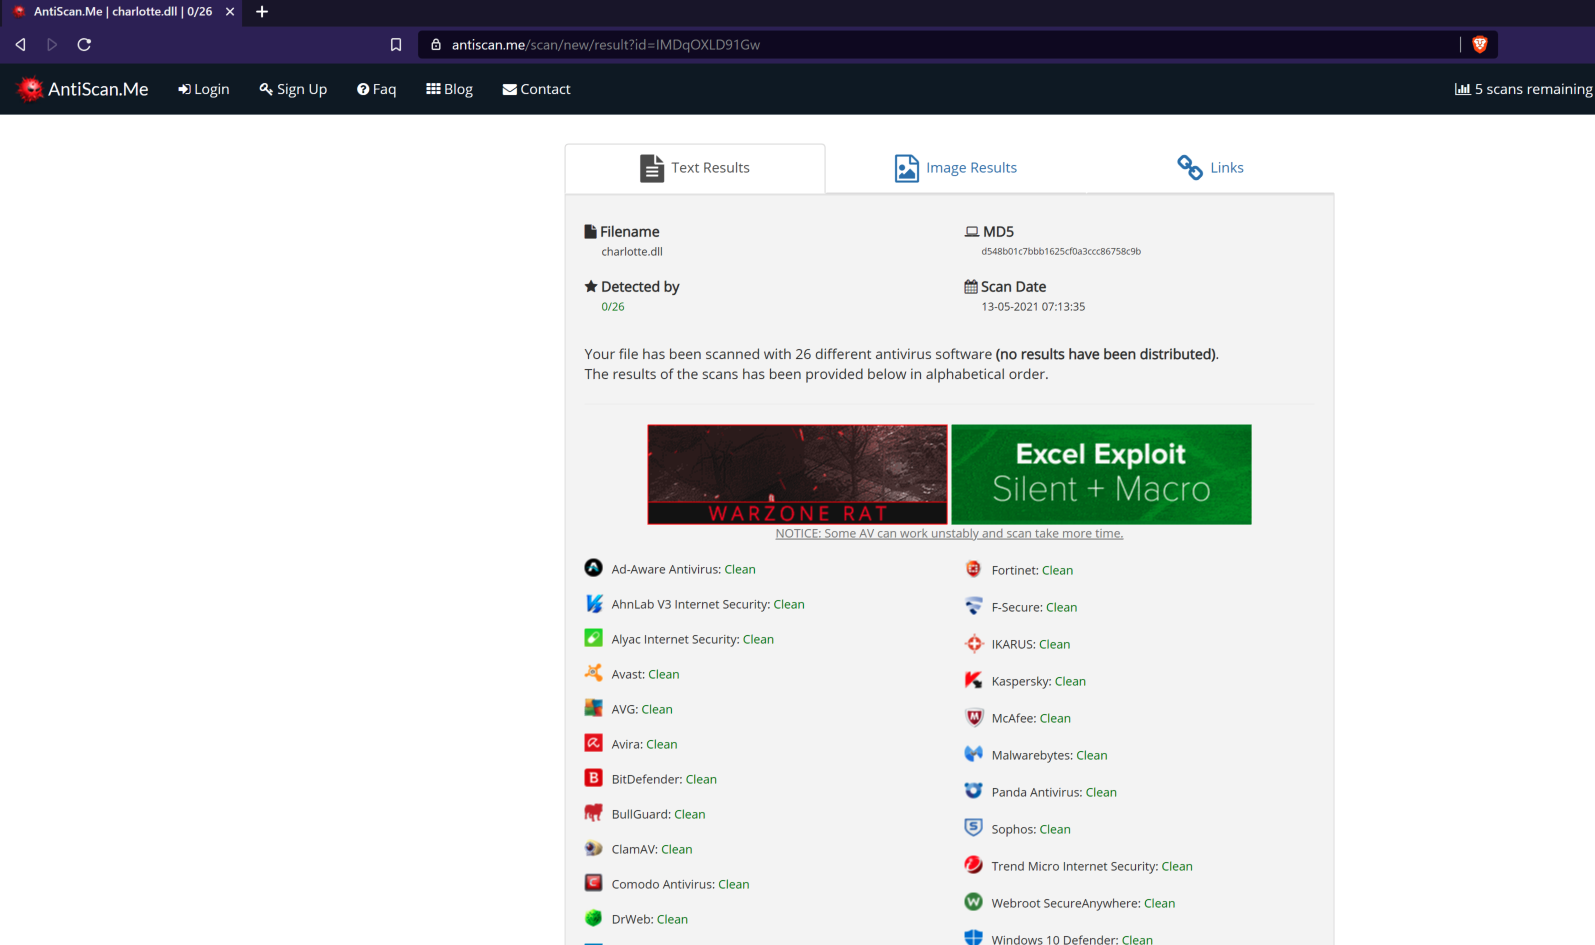
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…

A buffer overflow vulnerability in the control protocol of Flexense SyncBreeze Enterprise v10.4.18 allows remote attackers to execute arbitrary code…

Adversary Emulation Framework

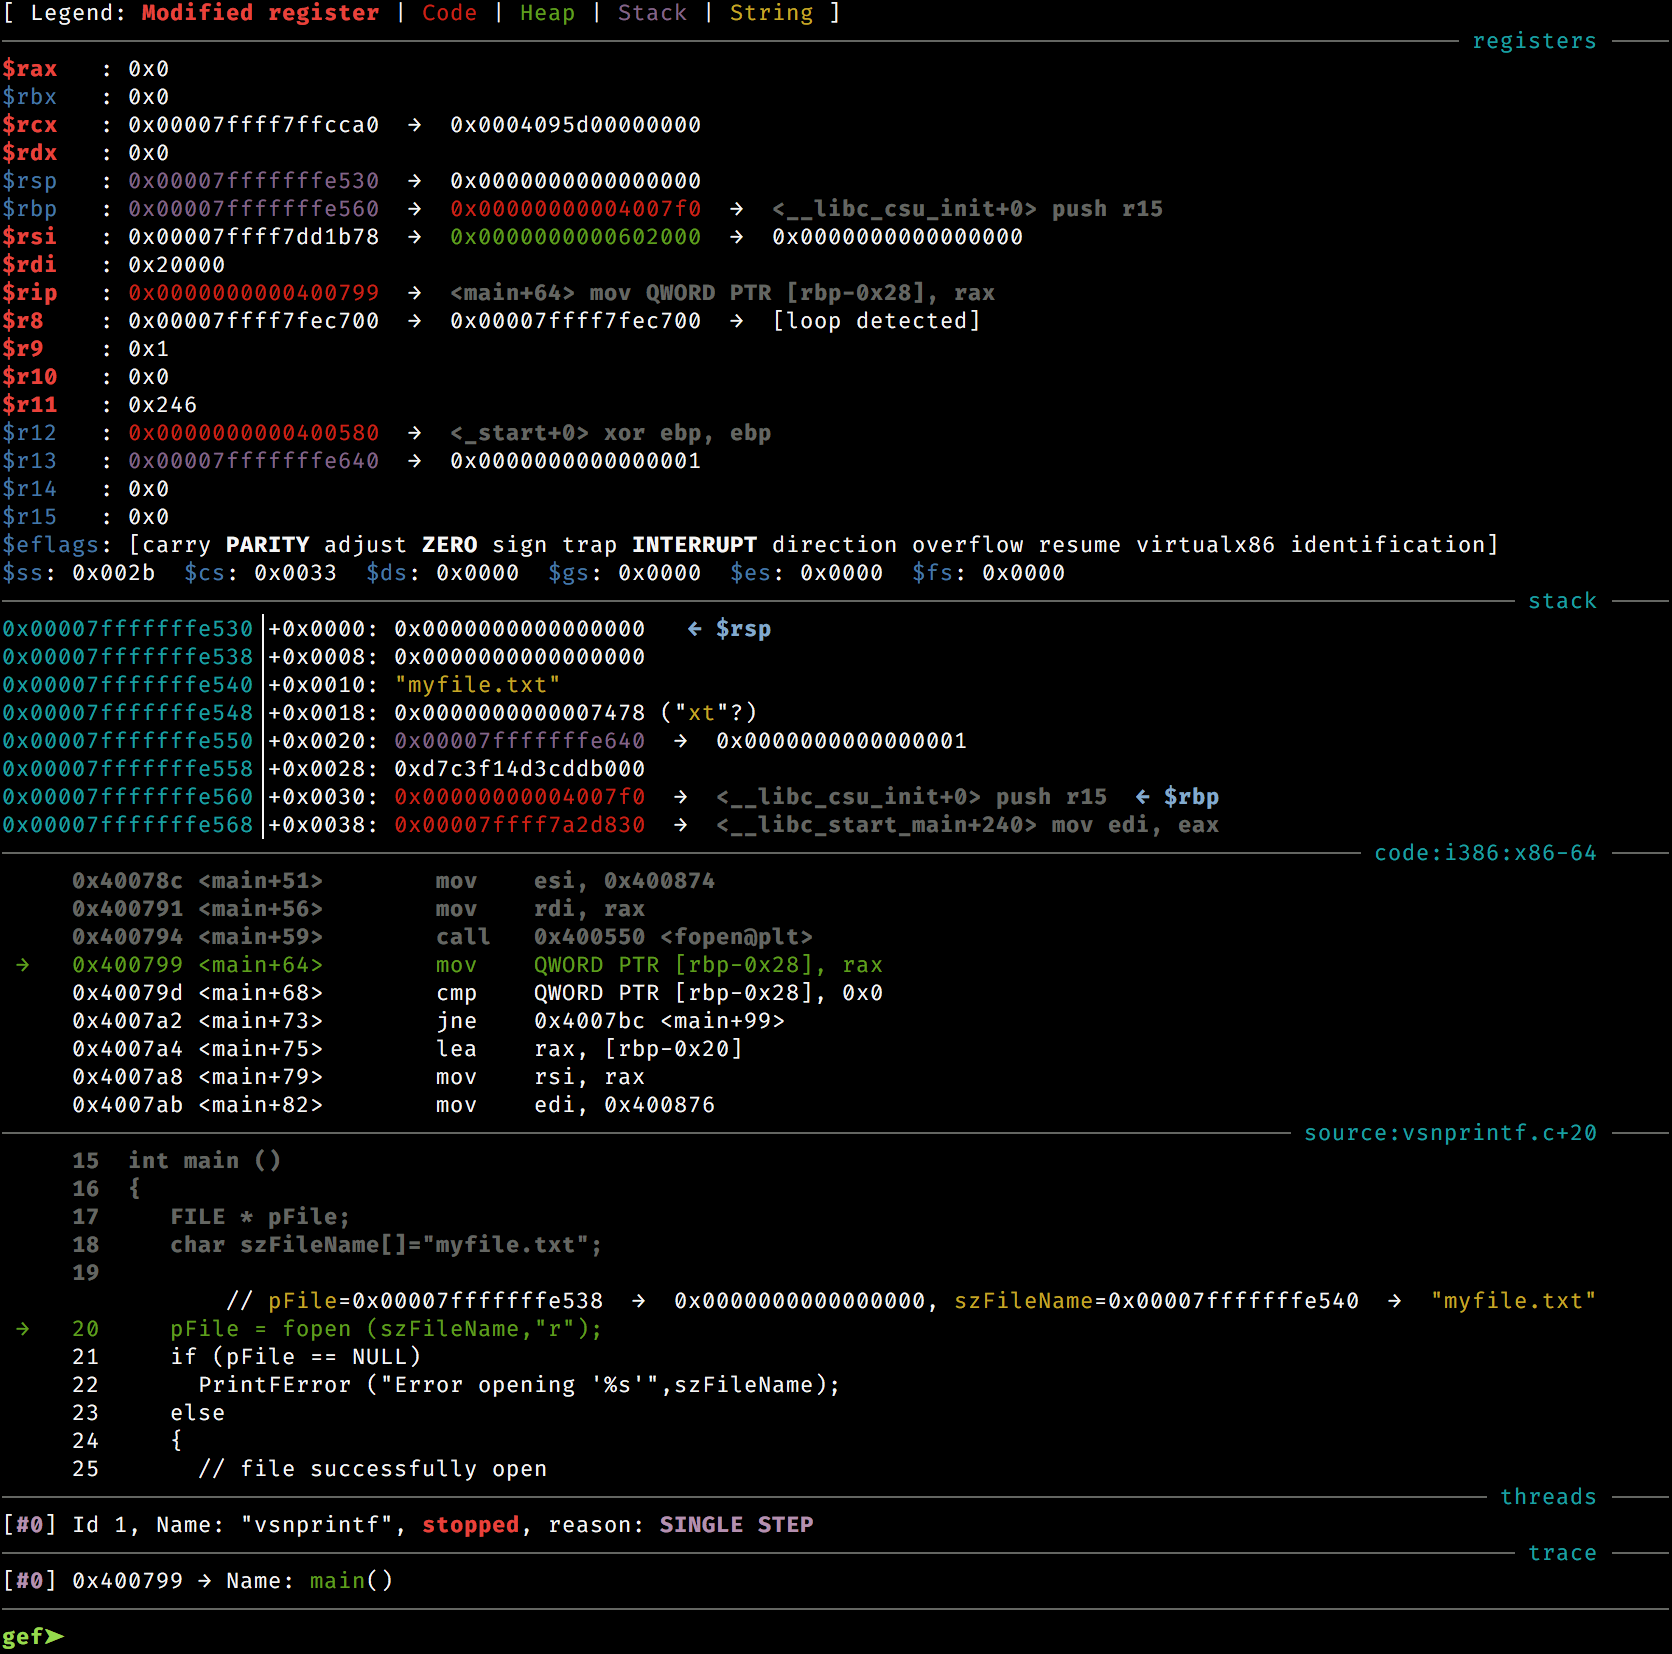
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

My experiments in weaponizing Nim (https://nim-lang.org/)

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

Payload Generation Framework

Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

Hide your Powershell script in plain sight. Bypass all Powershell security features

c++ fully undetected shellcode launcher ;)

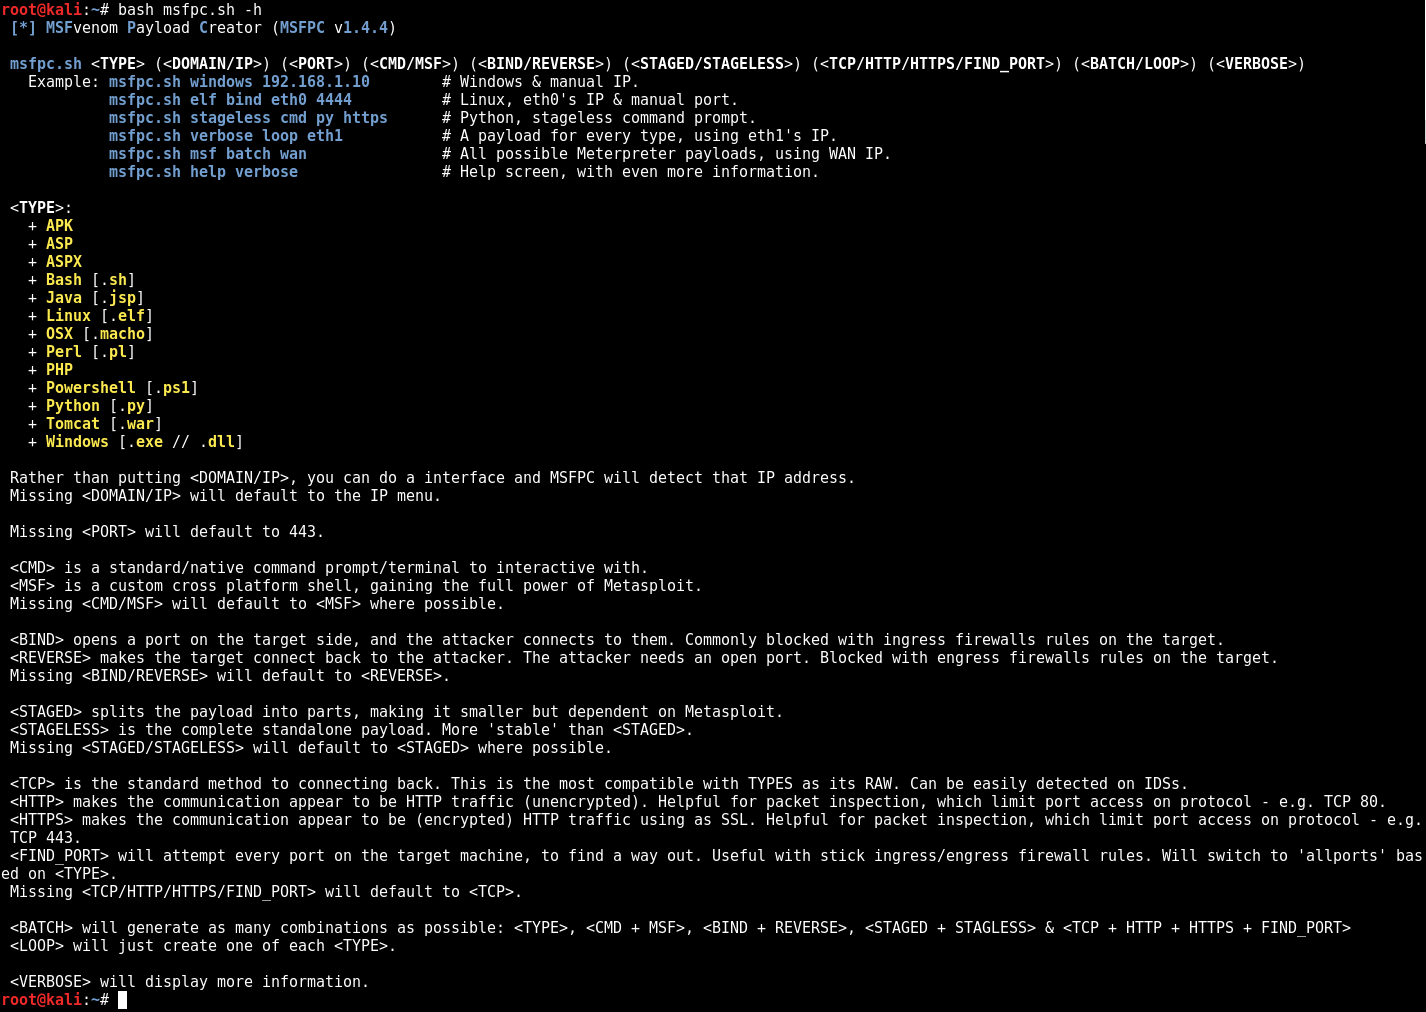
MSFvenom Payload Creator (MSFPC)