
SysWhispers
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
exploitationids-ips-evasionpayload-development+3
jthuraisamy/syswhispersAV/EDR evasion via direct system calls.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
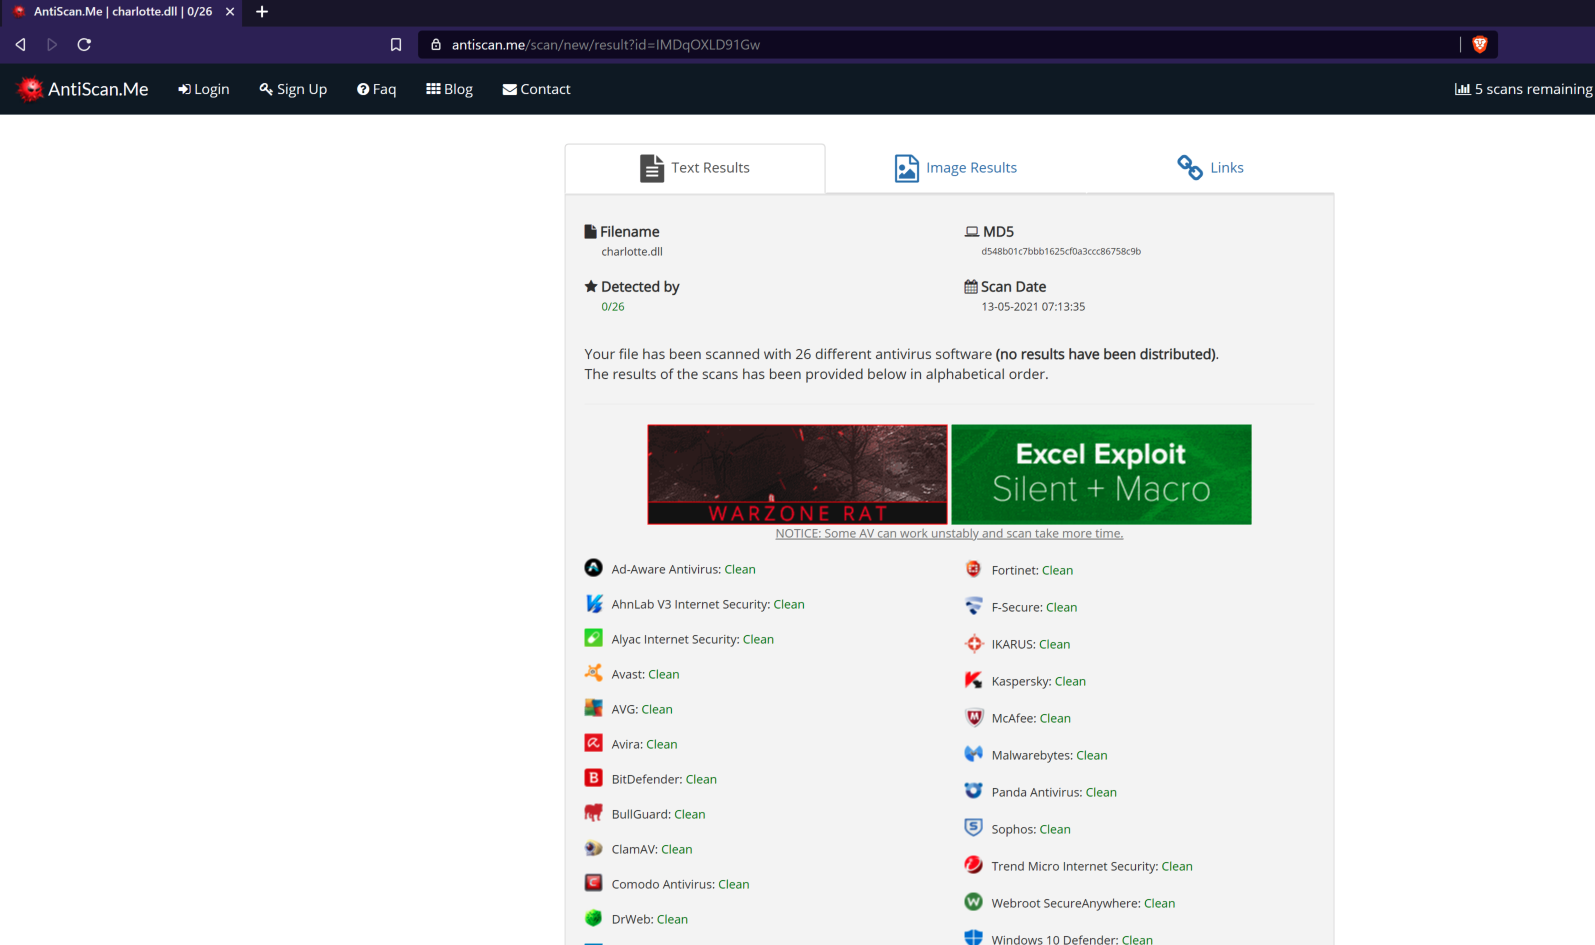 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
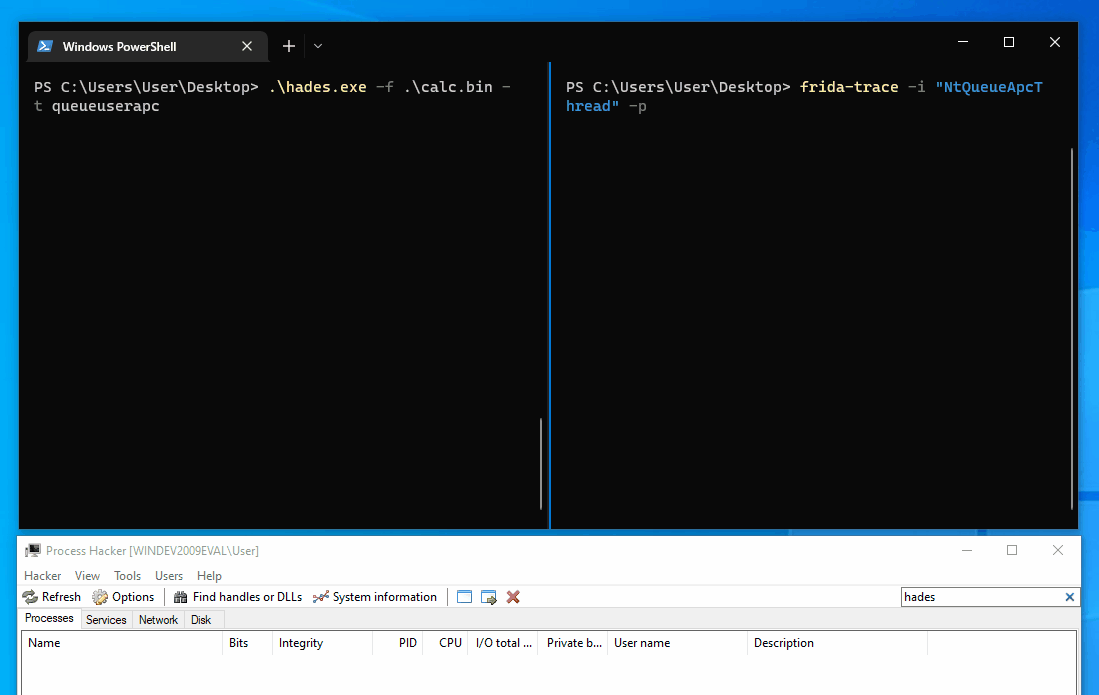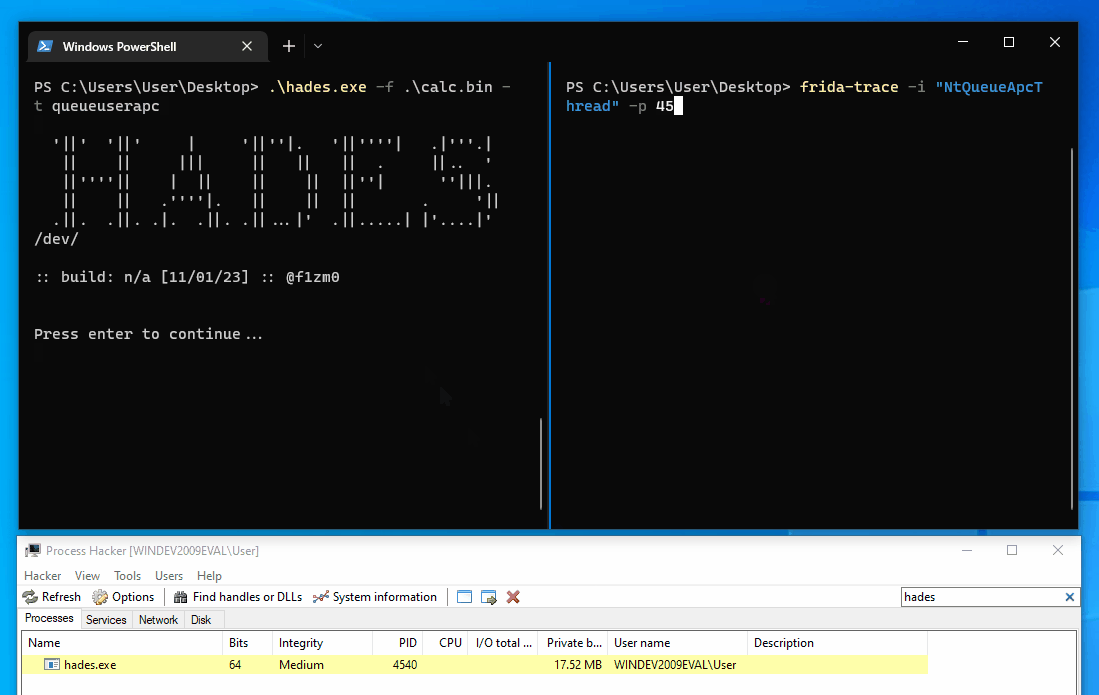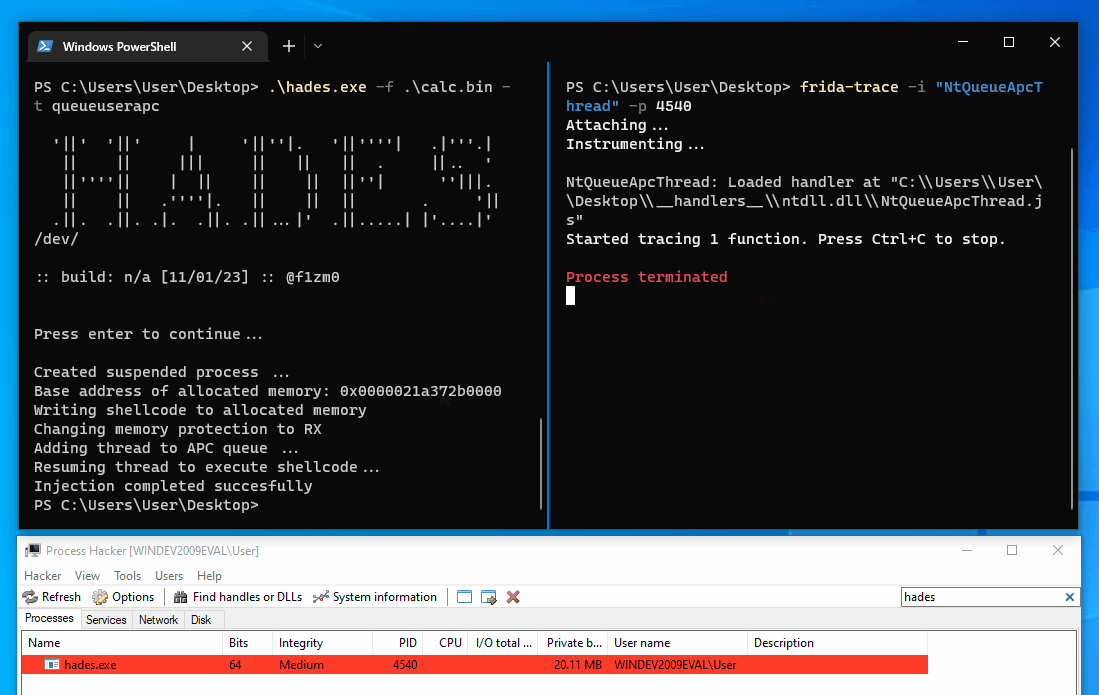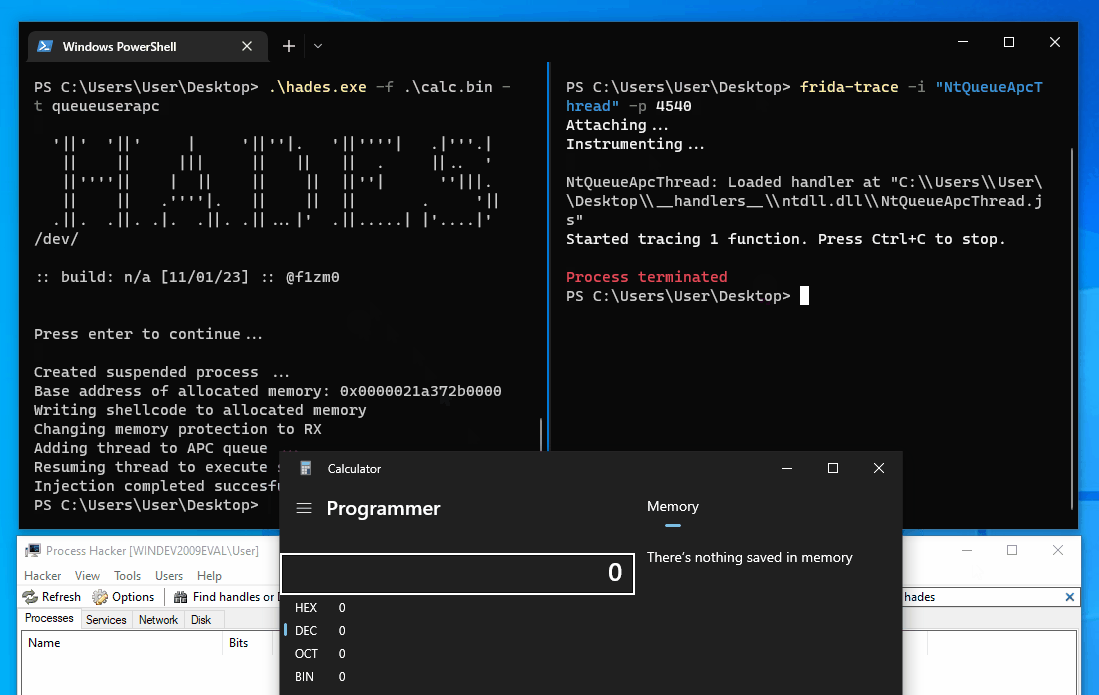 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 florylsk/execit
Execute shellcode files with rundll32
 wh1te4ever/webkit-bug-256172
Safari 1day RCE Exploit

 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level