
dicerosbicornis
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
command-and-controldata-exfiltrationencryption-decryption-tools+5
16
maldevel/dicerosbicornisA fully featured Windows backdoor that uses email as a C&C server
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 doggycheng/cnvd-2020-10487
CVE-2020-1938 / CNVD-2020-1048 Detection Tools
 cecio/xenoboxx
Hardware Sandbox Toolkit
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 faithtiannn/cve-2025-55182
CVE-2025-55182漏洞检测工具
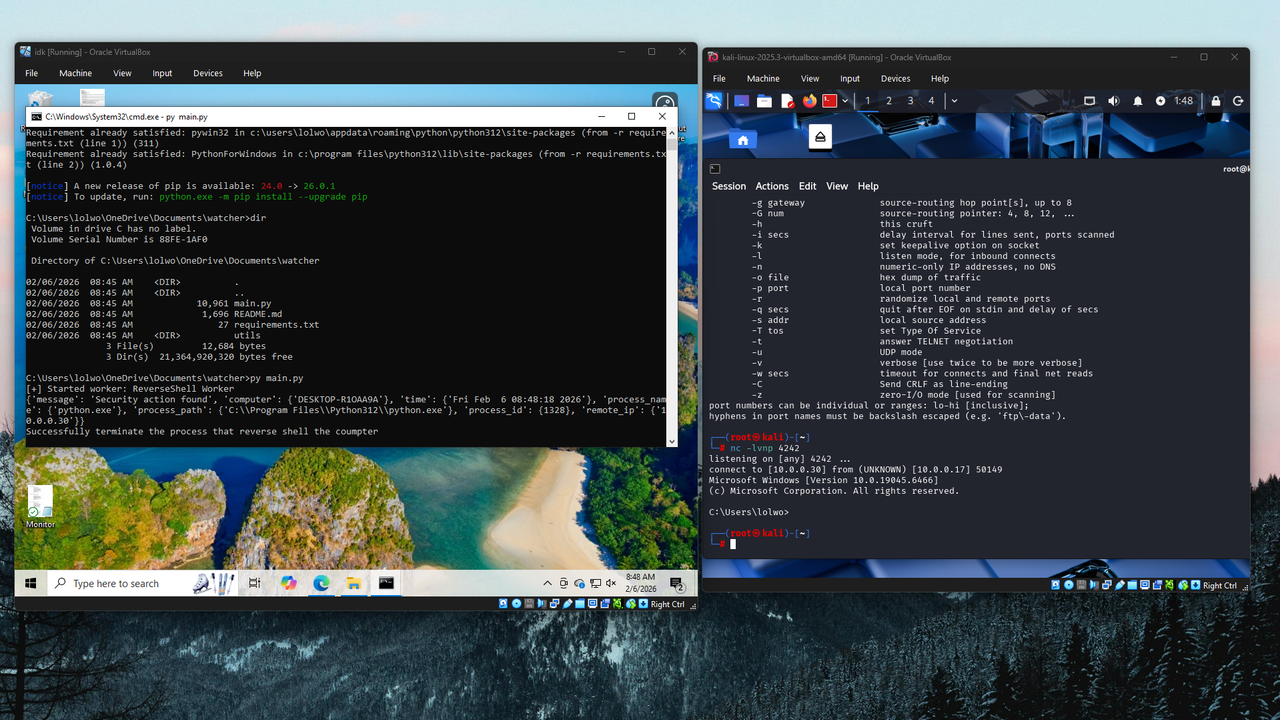 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
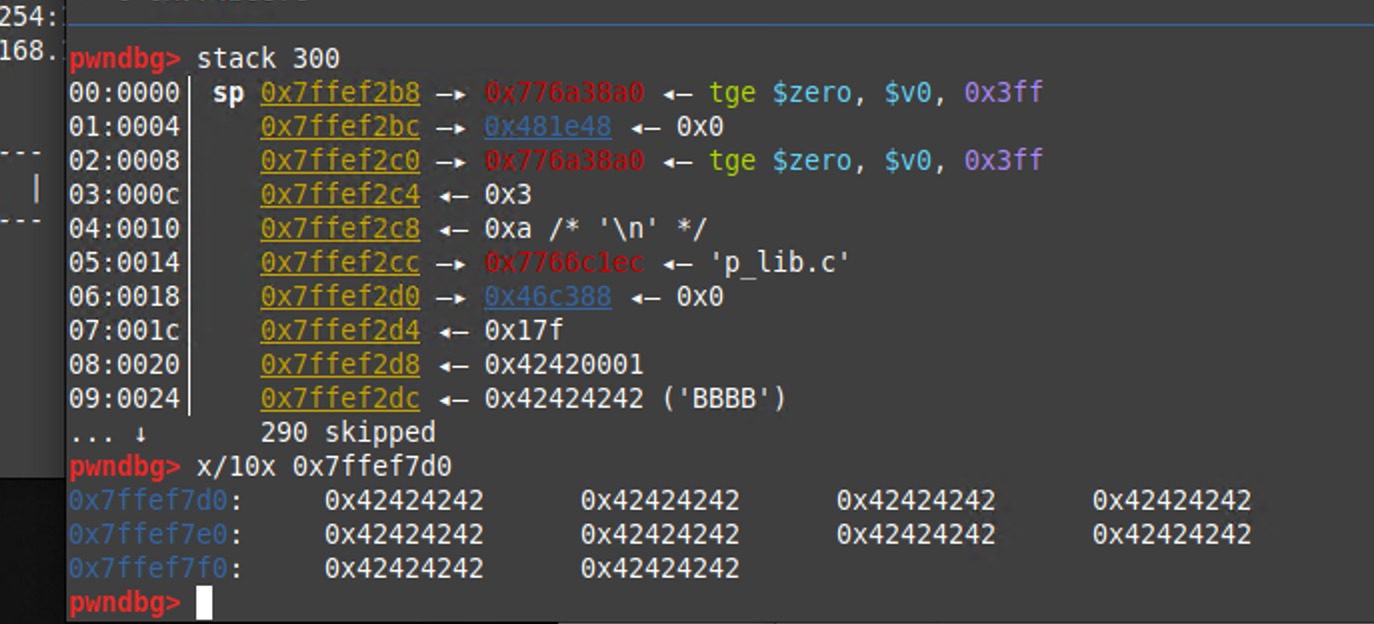 laskdjlaskdj12/cve-2024-29671-poc
This is POC of CVE-2024-29671
 makavellik/poc-cve-2021-42013-exploit
Una herramienta avanzada de escaneo, explotación e interacción remota diseñada para detectar y aprovechar la vulnerabilidad Apache Path Traversal +…
 charchit-subedi/chamilo-lms-unauthenticated-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 1llu50ry/mcp-gamehacking
MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
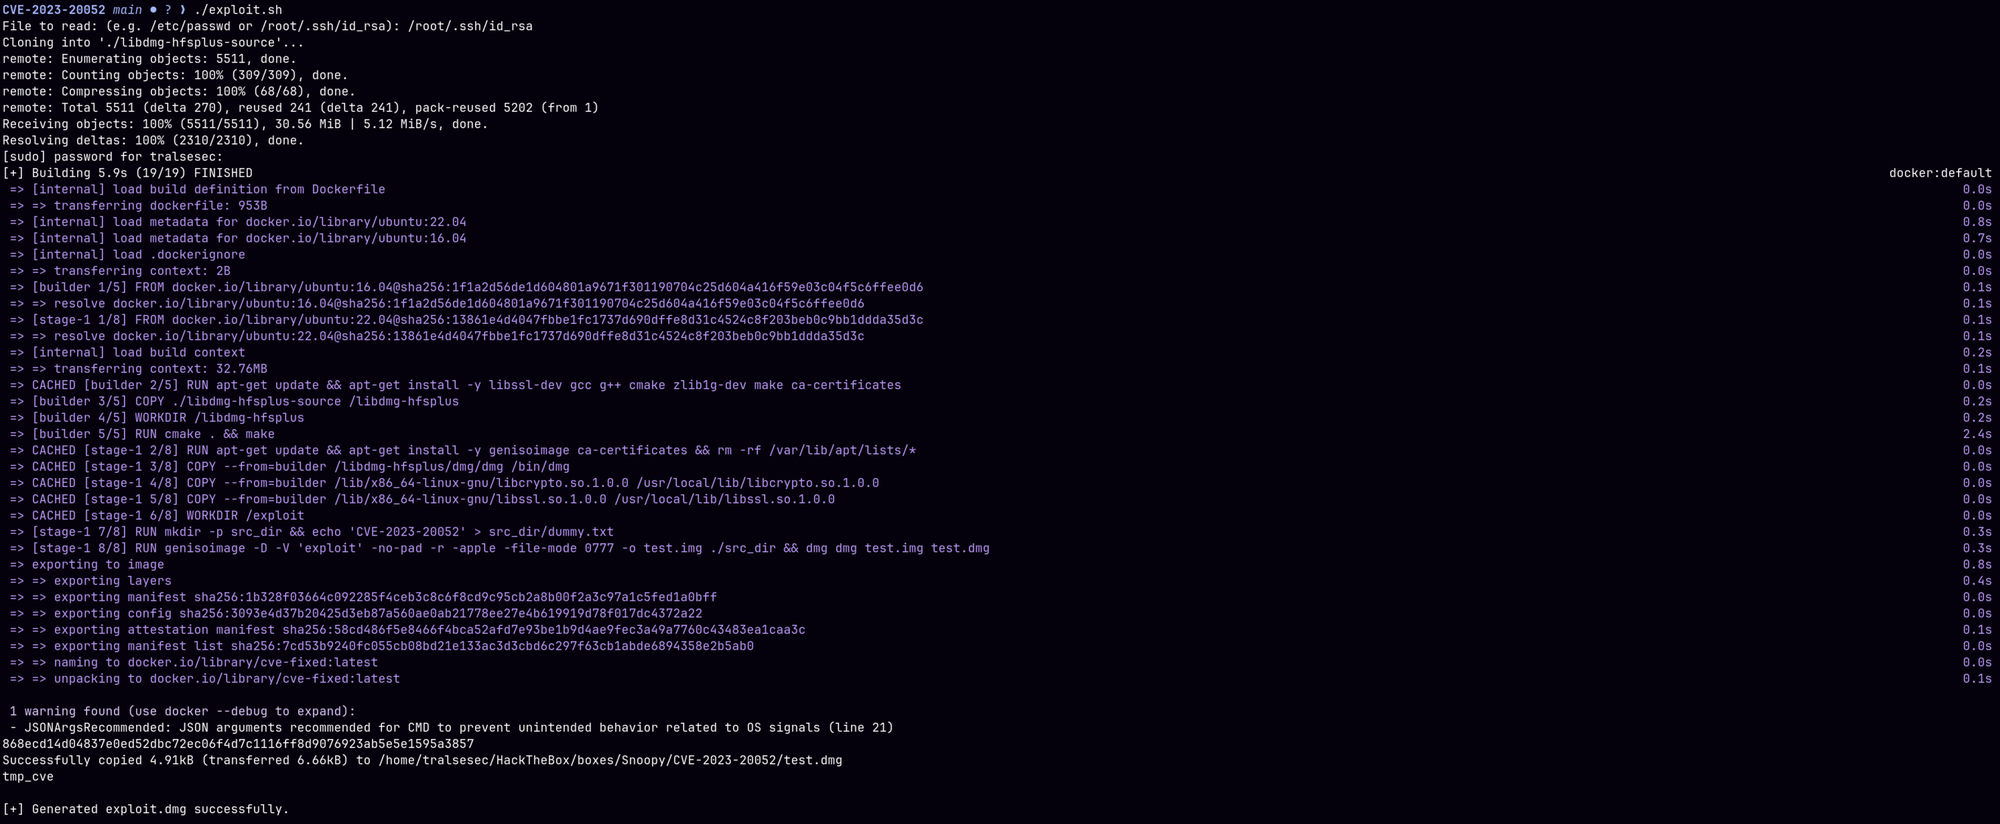 tralsesec/cve-2023-20052
Original standalone Proof-of-Concept exploit and execution harness for CVE-2023-20052 (ClamAV DMG XML Entity Expansion).
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 imnot-ye/cve-2019-17147
Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…