
Archived
ScareCrow
 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
exploit-frameworkspayload-developmentpayload-generation+3
2.9k
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
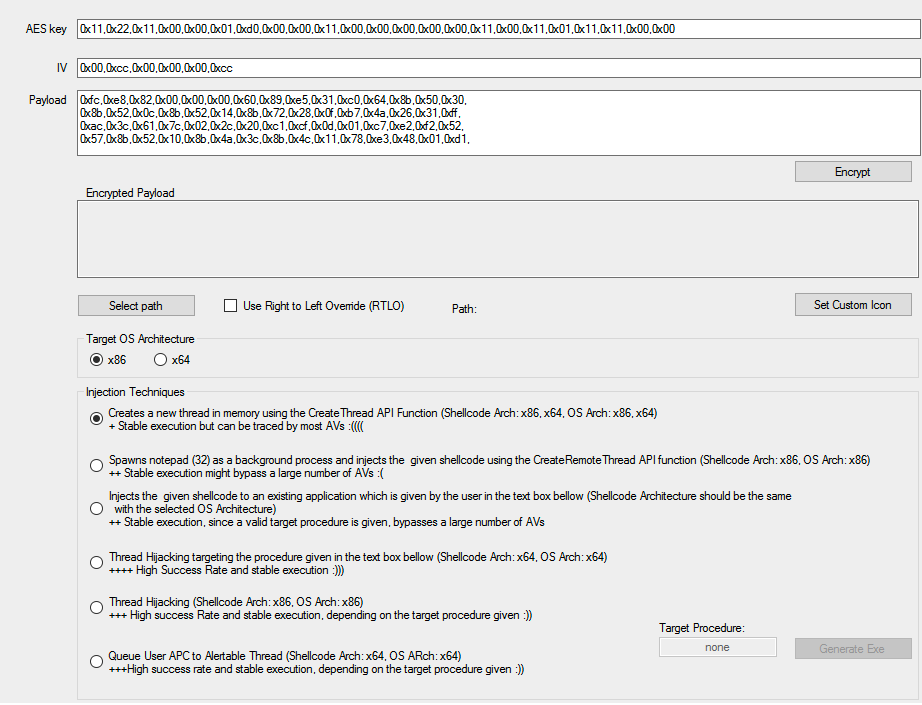 ch0pin/aviator
Antivirus evasion project
 mandiant/flare-ida
IDA Pro utilities from FLARE team
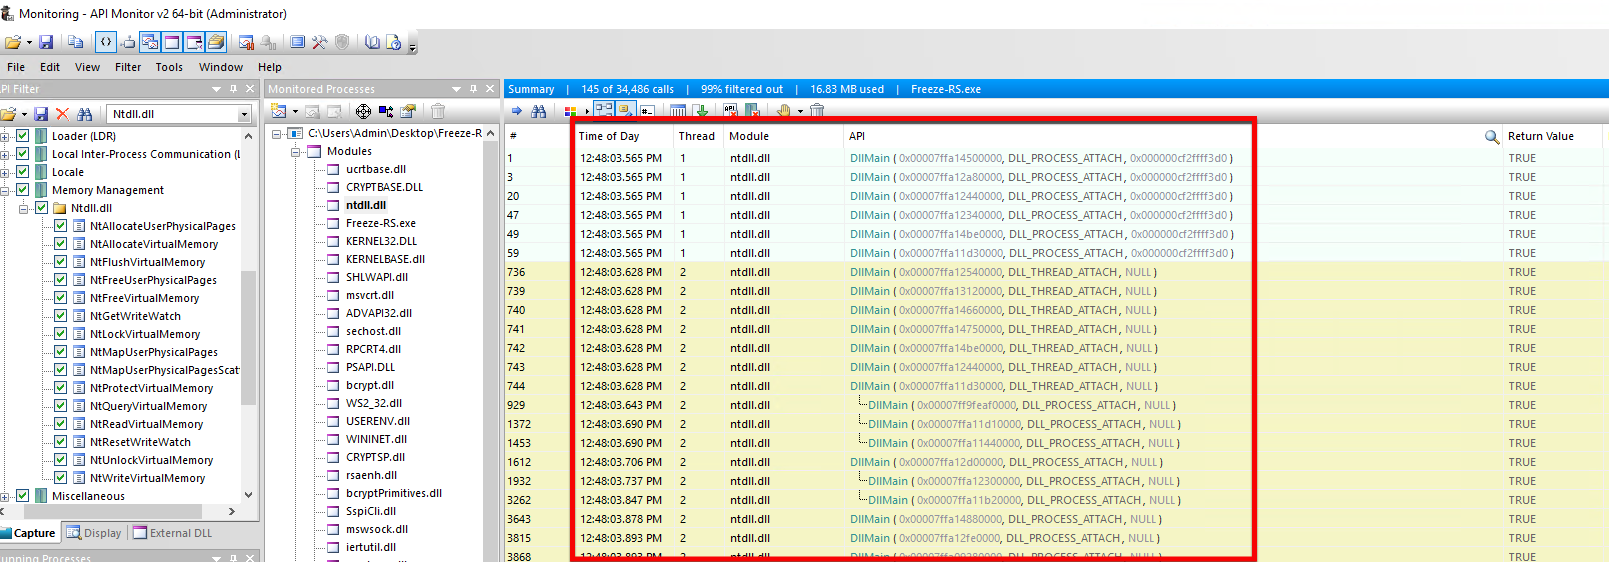 optiv/freeze.rs
Freeze.rs is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls written in RUST
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 optiv/dent
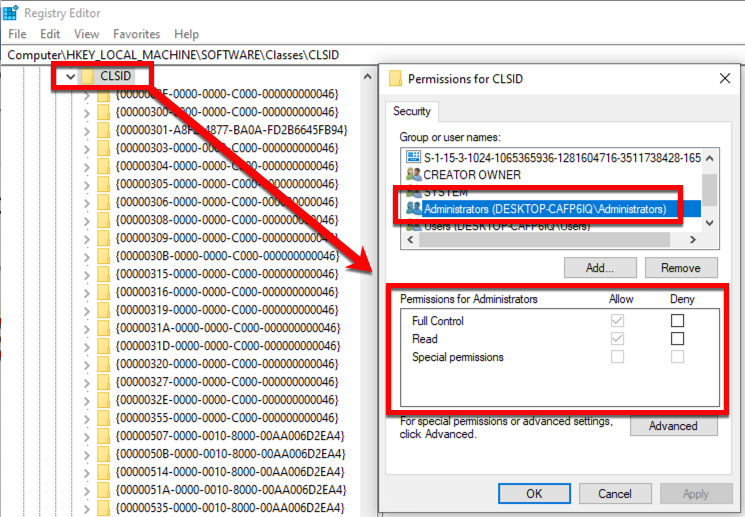
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 xaff-xaff/black-angel-rootkit
Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.
 redcode-labs/citadel
Collection of pentesting scripts
 algo7/bluekeep_cve-2019-0708_poc_to_exploit
An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 gmh5225/packer-kitsupe
Some PE hackery I'm working on (shellcode loader, packer, all WIP)
 nydubh3/cuiri
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。