
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
252 results
Project-Onyx preview

Project-Onyx

GitHubx-3306/project-onyx

Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
ai-securitycommand-and-controlcryptography+6
119
18 days ago
Split preview

Split

GitHubkudaes/split

Apply a divide and conquer approach to bypass EDRs

adversarial-attackids-ips-evasionpayload-development+3
2882 years ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
binary-analysisdebuggersexploitation+5
1133 years ago
SMBRat preview

SMBRat

GitHuboperatorequals/smbrat

A Windows Remote Administration Tool in Visual Basic with UNC paths

command-and-controlexploitationlateral-movement+8
227 years ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

exploitationids-ips-evasionmemory-forensics+7
2.6k4 years ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
ruler preview

ruler

GitHubsensepost/ruler

A tool to abuse Exchange services
email-securityexploitationinformation-gathering+3
2.3k2 years ago
go-shellcode preview

go-shellcode

GitHubne0nd0g/go-shellcode

A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
exploitationpayload-developmentpayload-generation+4
1.2k4 years ago
mortar preview

mortar

GitHub0xsp-srd/mortar

evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
exploit-frameworksids-ips-evasionpayload-generation+2
1.5k2 years ago
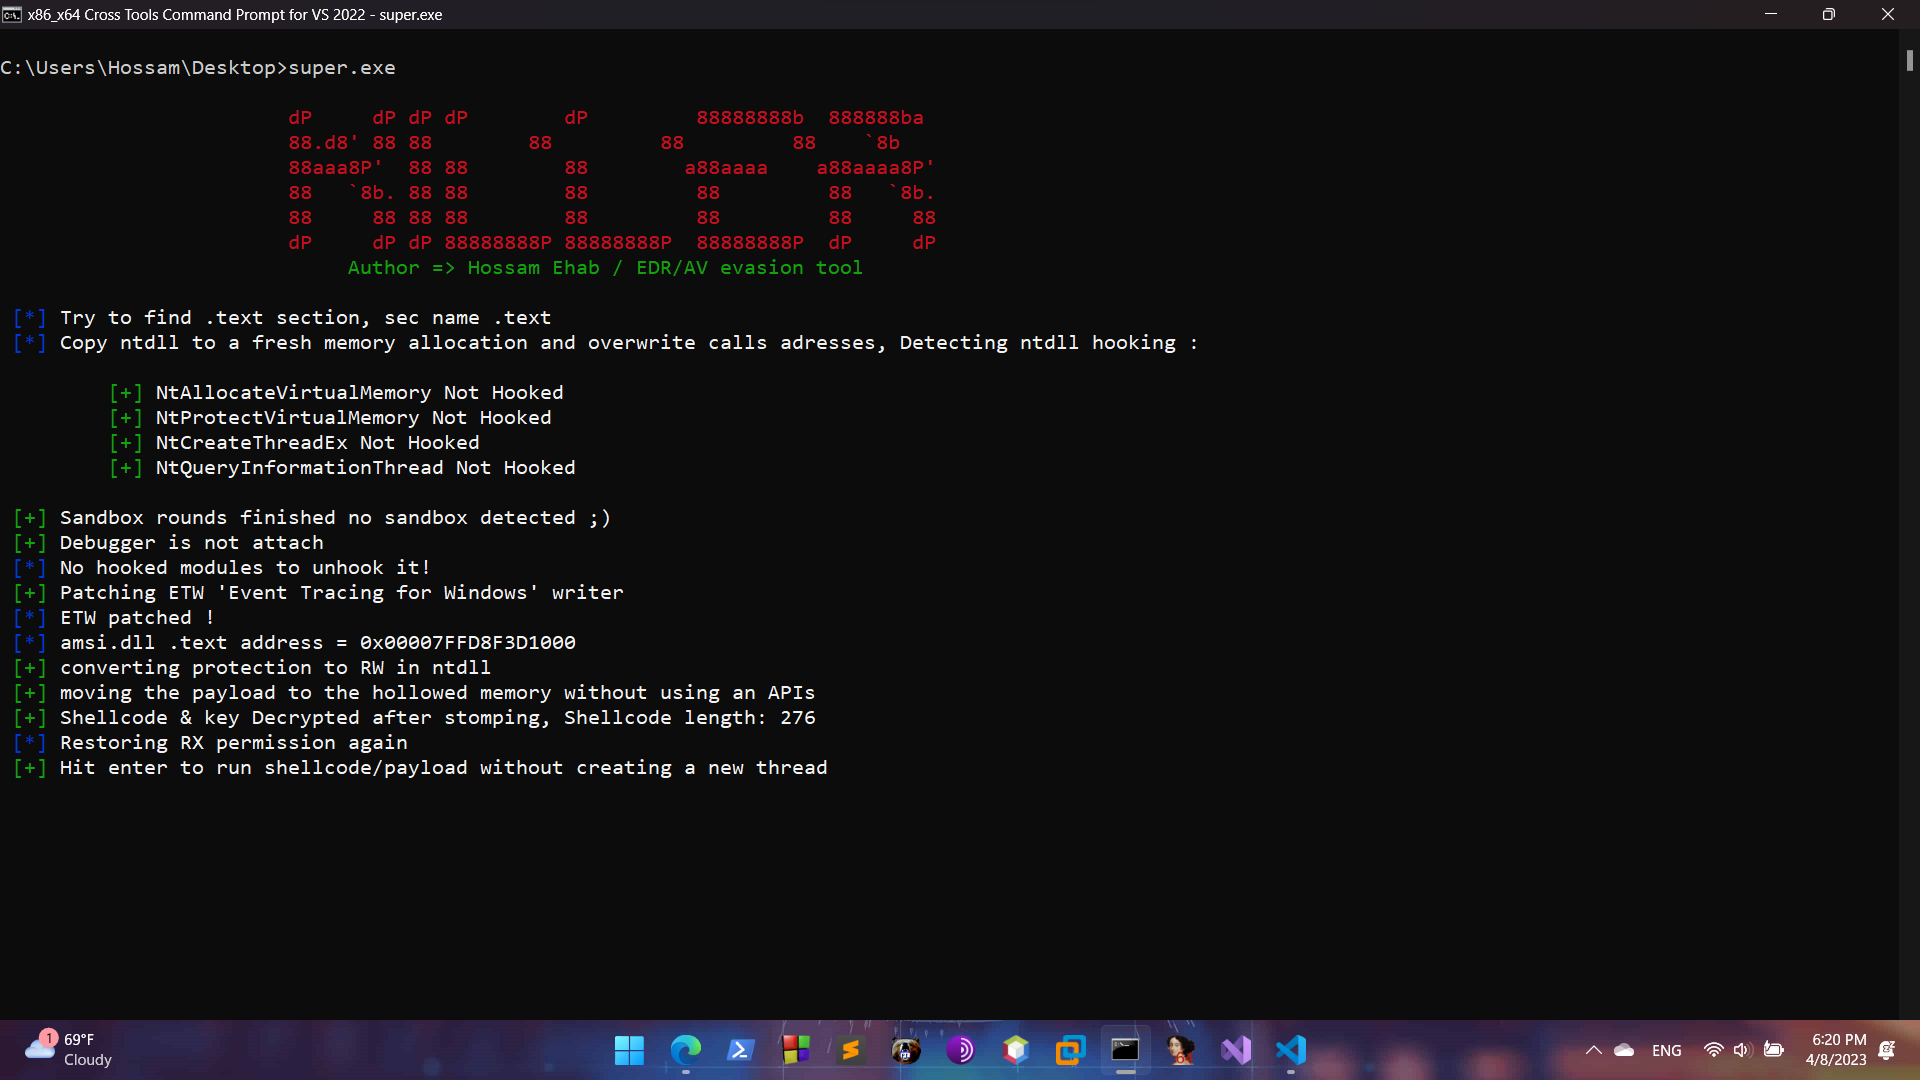
Killer preview

Killer

GitHub0xhossam/killer

Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
anti-boteducationexploitation+4
8442 years ago
PoolParty preview

PoolParty

GitHubsafebreach-labs/poolparty

A set of fully-undetectable process injection techniques abusing Windows Thread Pools

exploitationpayload-developmentpost-exploitation+3
1.3k2 years ago
meterssh preview

meterssh

GitHubtrustedsec/meterssh

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…

command-and-controlexploitationpayload-development+4
5309 years ago
DEFCON-31-Syscalls-Workshop preview

DEFCON-31-Syscalls-Workshop

GitHubvirtualalllocex/defcon-31-syscalls-workshop

Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".

educationlabs-practicepayload-development+2
7841 year ago
HandleKatz preview

HandleKatz

GitHubcodewhitesec/handlekatz

PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…

defensive-toolsmemory-forensicspayload-generation+3
5973 years ago
shellen preview

shellen

GitHubkonatabrk/shellen

:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
binary-analysisctfeducation+5
9085 years ago
Shellcode-Encryptor preview

Shellcode-Encryptor

GitHubplackyhacker/shellcode-encryptor

A simple shell code encryptor/decryptor/executor to bypass anti virus.
encryption-decryption-toolsexploit-frameworkspayload-development+2
4684 years ago
gmailc2 preview

gmailc2

GitHubmachine1337/gmailc2

A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions

command-and-controleducationpayload-generation+4
4891 year ago
win-exec-calc-shellcode preview

win-exec-calc-shellcode

GitHubpeterferrie/win-exec-calc-shellcode

A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)

binary-exploitationexploitationpayload-development+3
4502 years ago
Previous1…345…14Next