Simple-Polymorphic-Engine-SPE32

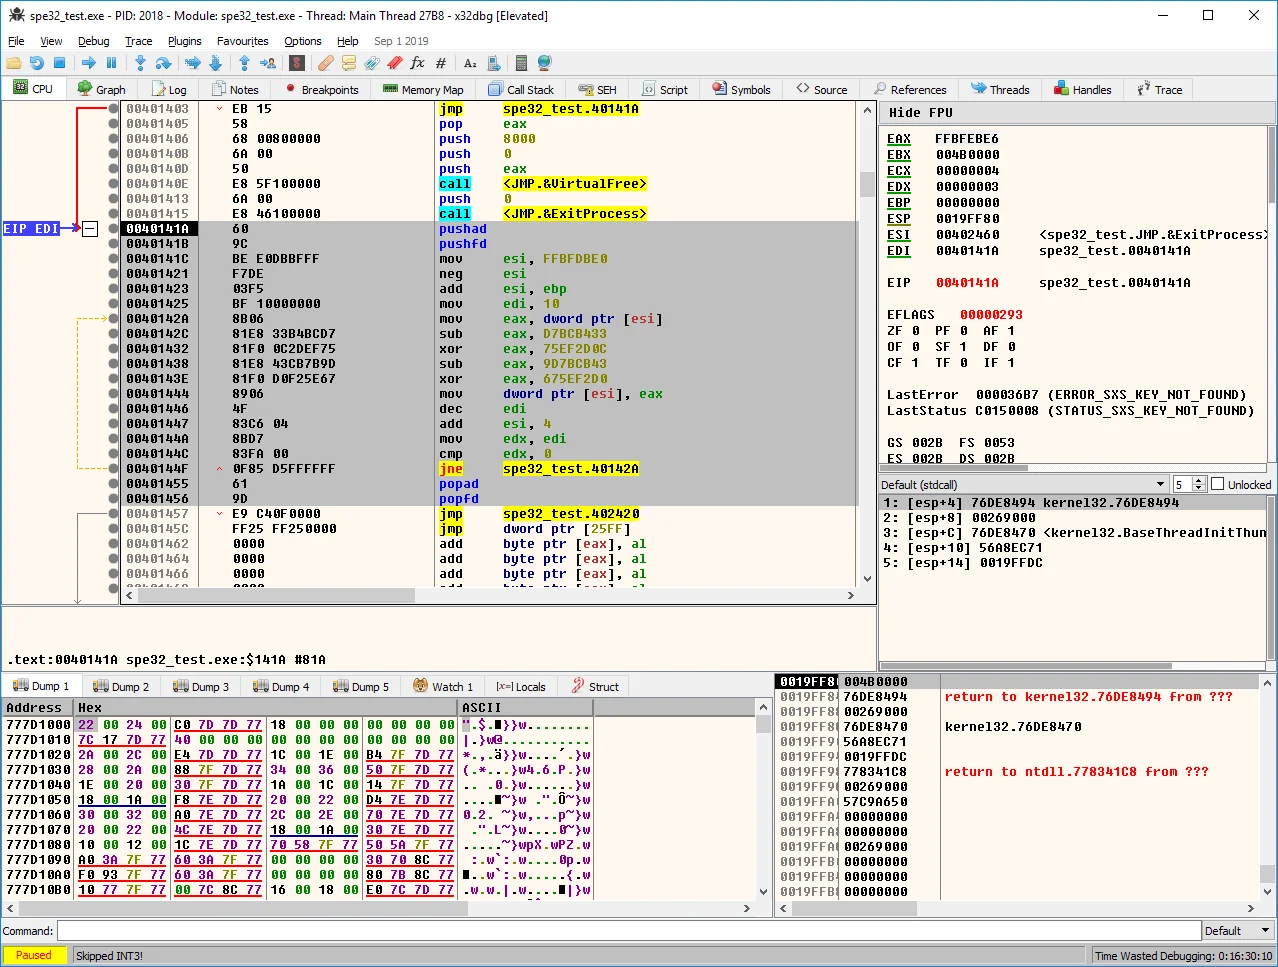
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

pinky - The PHP mini RAT (Remote Administration Tool)

Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️

Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.

A dynamic unpacking tool


NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.

A simple tool to interact with web shells and command injection vulnerabilities

A Windows Remote Administration Tool in Visual Basic with UNC paths

Universal stack-based buffer overfow exploitation tool

Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit

Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…

Proof-of-concept exploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP, with shellcode for x86 systems. Intended for authorized security testing…

Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing

Python exploit for CVE-2023-3519 targeting Citrix ADC with custom NASM shellcode, PHP backdoor deployment, and SUID privilege escalation.