
CVE-2020-0022
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
android-securitybinary-exploitationbluetooth-security+9
kalibb/cve-2020-0022Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 manojcode/cloudme-sync-1.10.9---buffer-overflow-seh-dep-bypass
My version - CloudMe-Sync-1.10.9---Buffer-Overflow-SEH-DEP-Bypass on Win7 x64 CVE-2018-6892
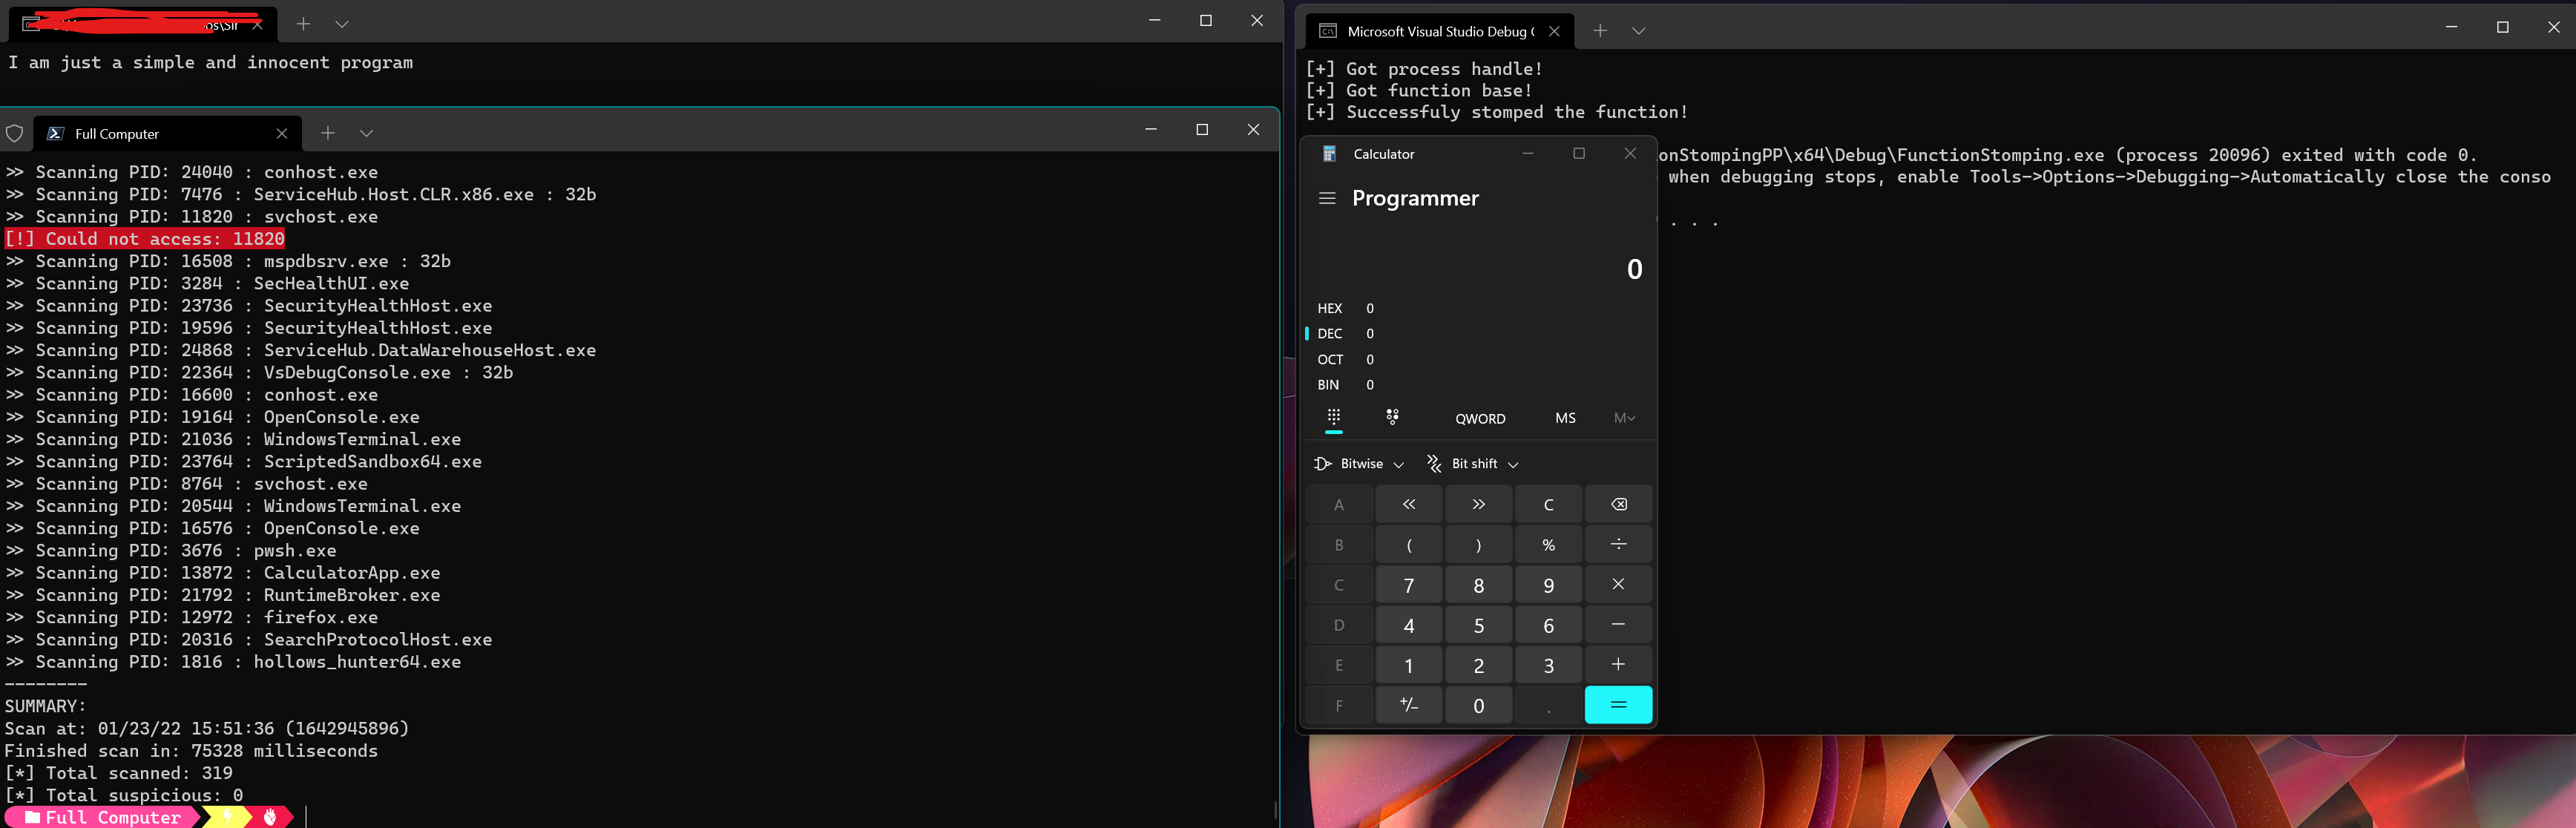 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 mdsecactivebreach/sharpshooter
Payload Generation Framework