
Dirty-Vanity
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
adversarial-attackexploitationpayload-development+4
676
deepinstinct/dirty-vanityA POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
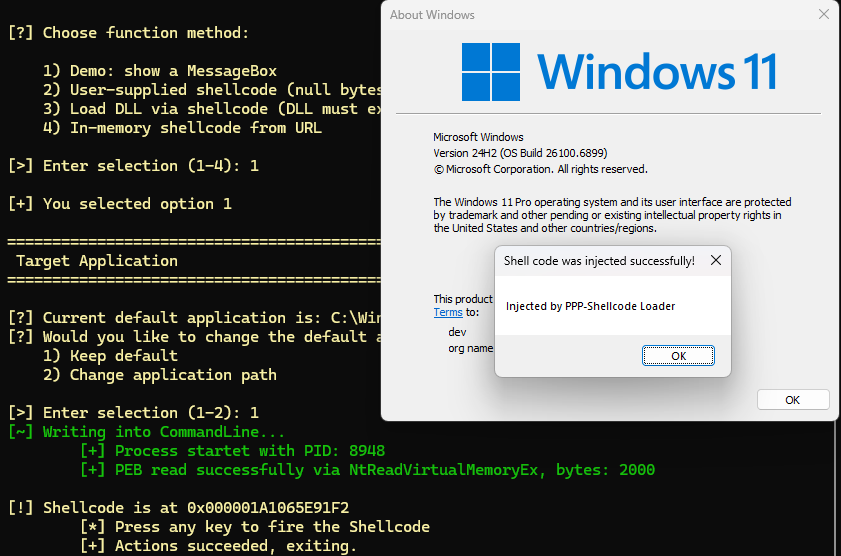 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
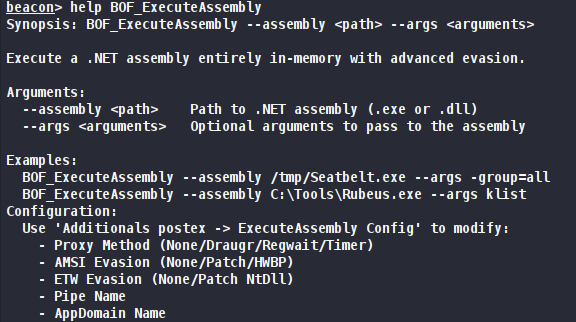 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 dreadlocked/drupalgeddon2
Exploit for Drupal v7.x + v8.x (Drupalgeddon 2 / CVE-2018-7600 / SA-CORE-2018-002)
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
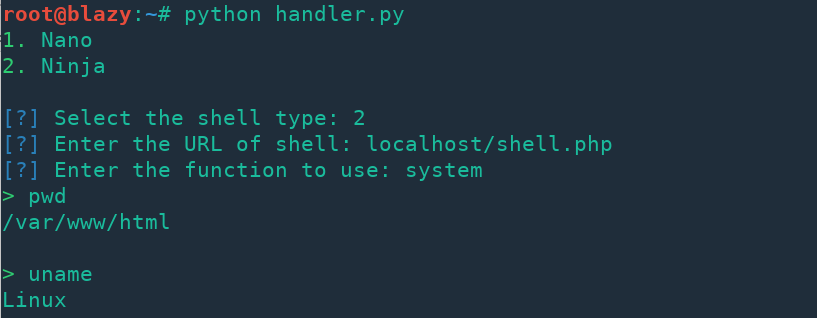 s0md3v/nano
Nano is a family of PHP web shells which are code golfed for stealth.
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 noperator/cve-2019-18935
RCE exploit for a .NET JSON deserialization vulnerability in Telerik UI for ASP.NET AJAX.
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
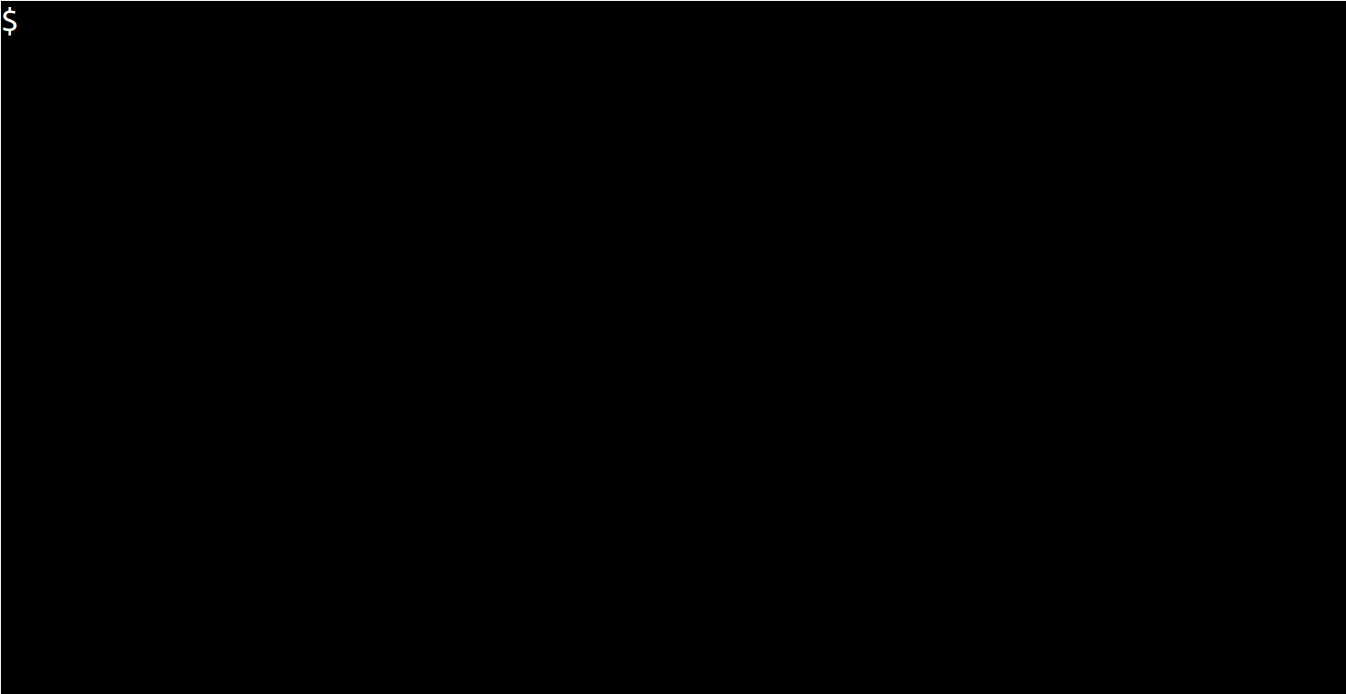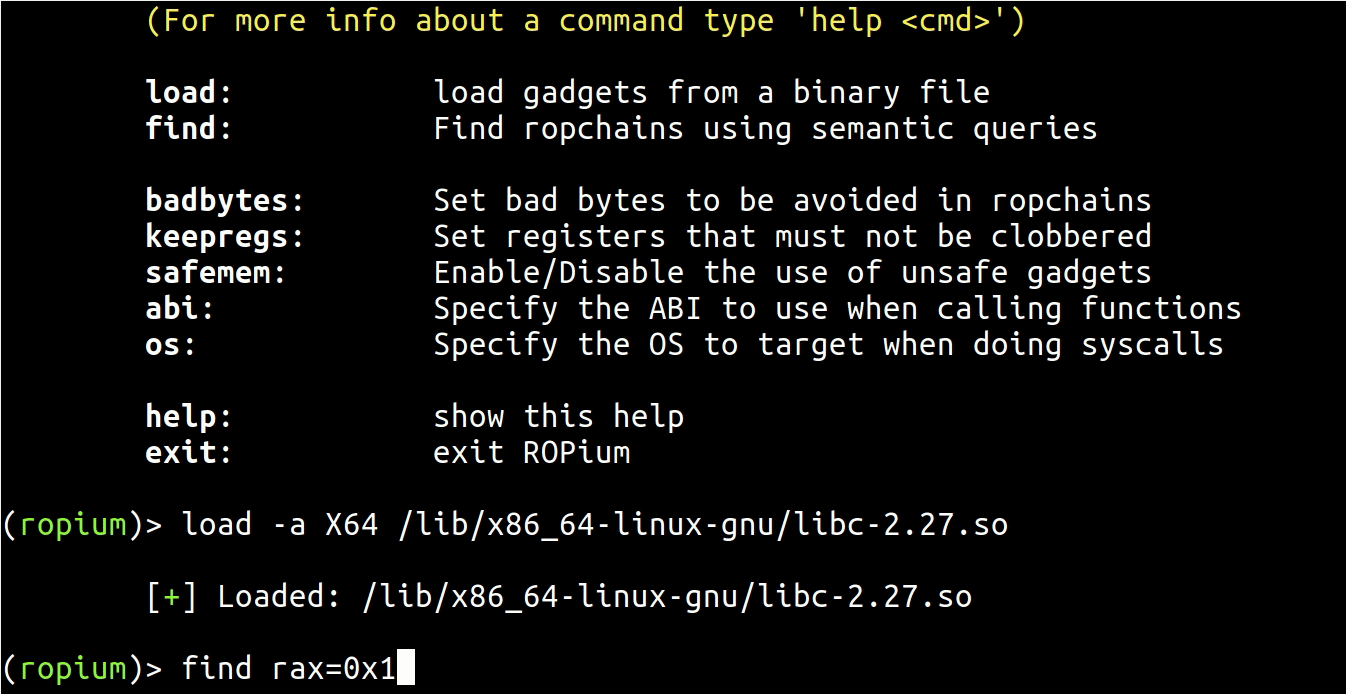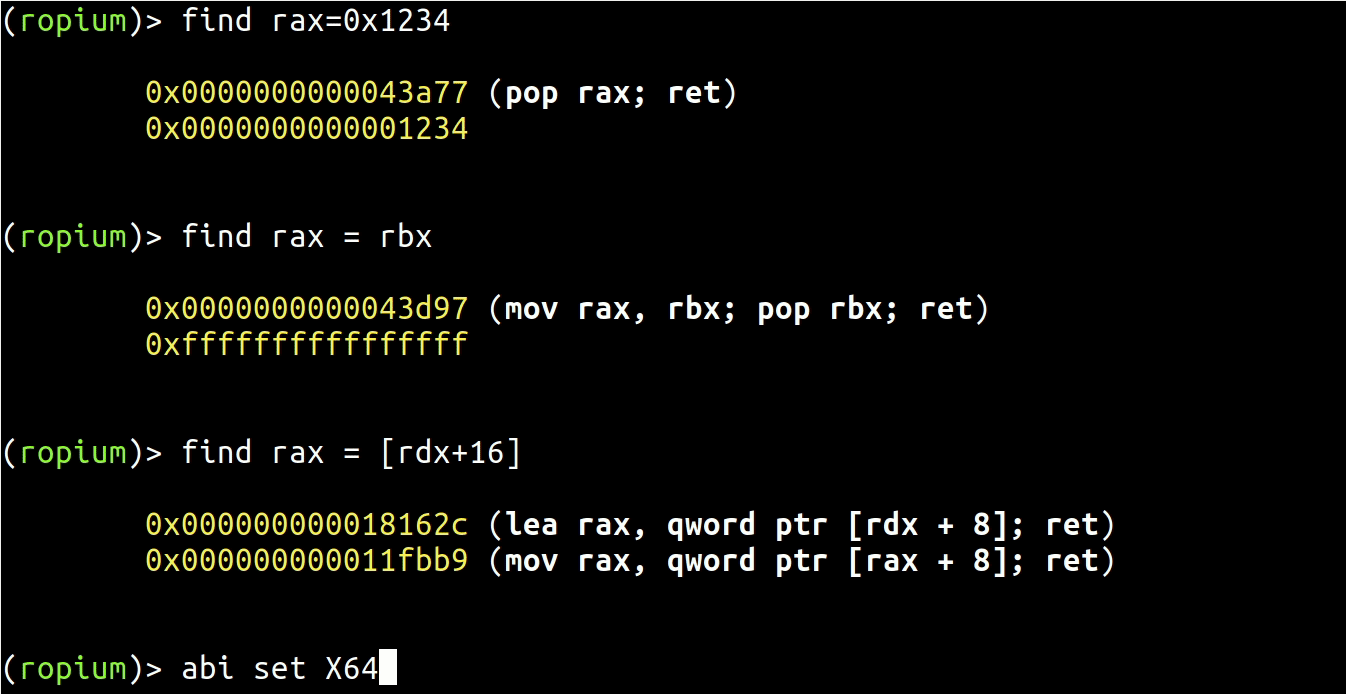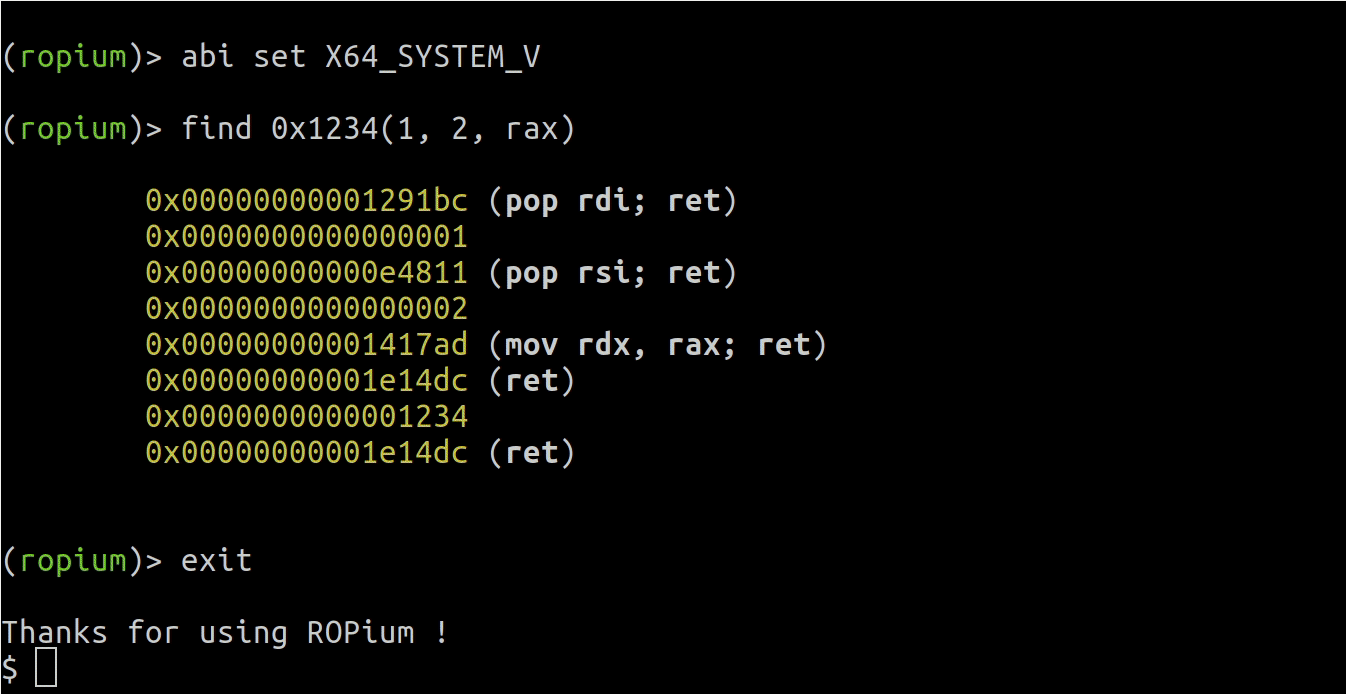 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit