
DInvoke_rs
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
binary-analysisids-ips-evasionpayload-development+3
367
kudaes/dinvoke_rsDynamically invoke arbitrary unmanaged code
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 hagrid29/peloader
PE loader with various shellcode injection techniques
 s3cur3th1ssh1t/nim-runpe
A Nim implementation of reflective PE-Loading from memory
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
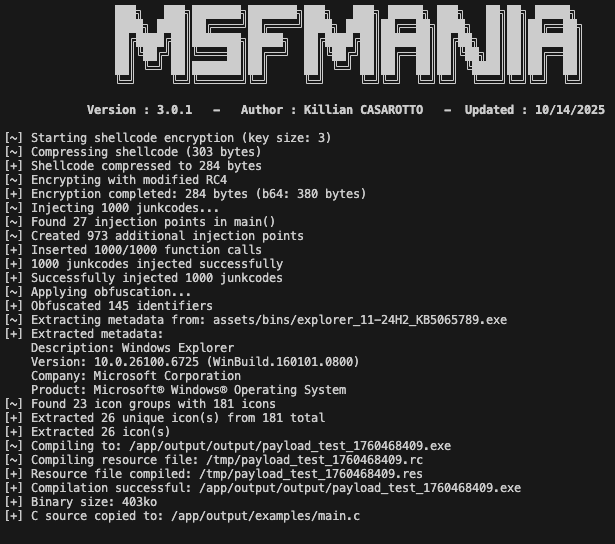 lepotekil/msfmania
Python AV Evasion Tools
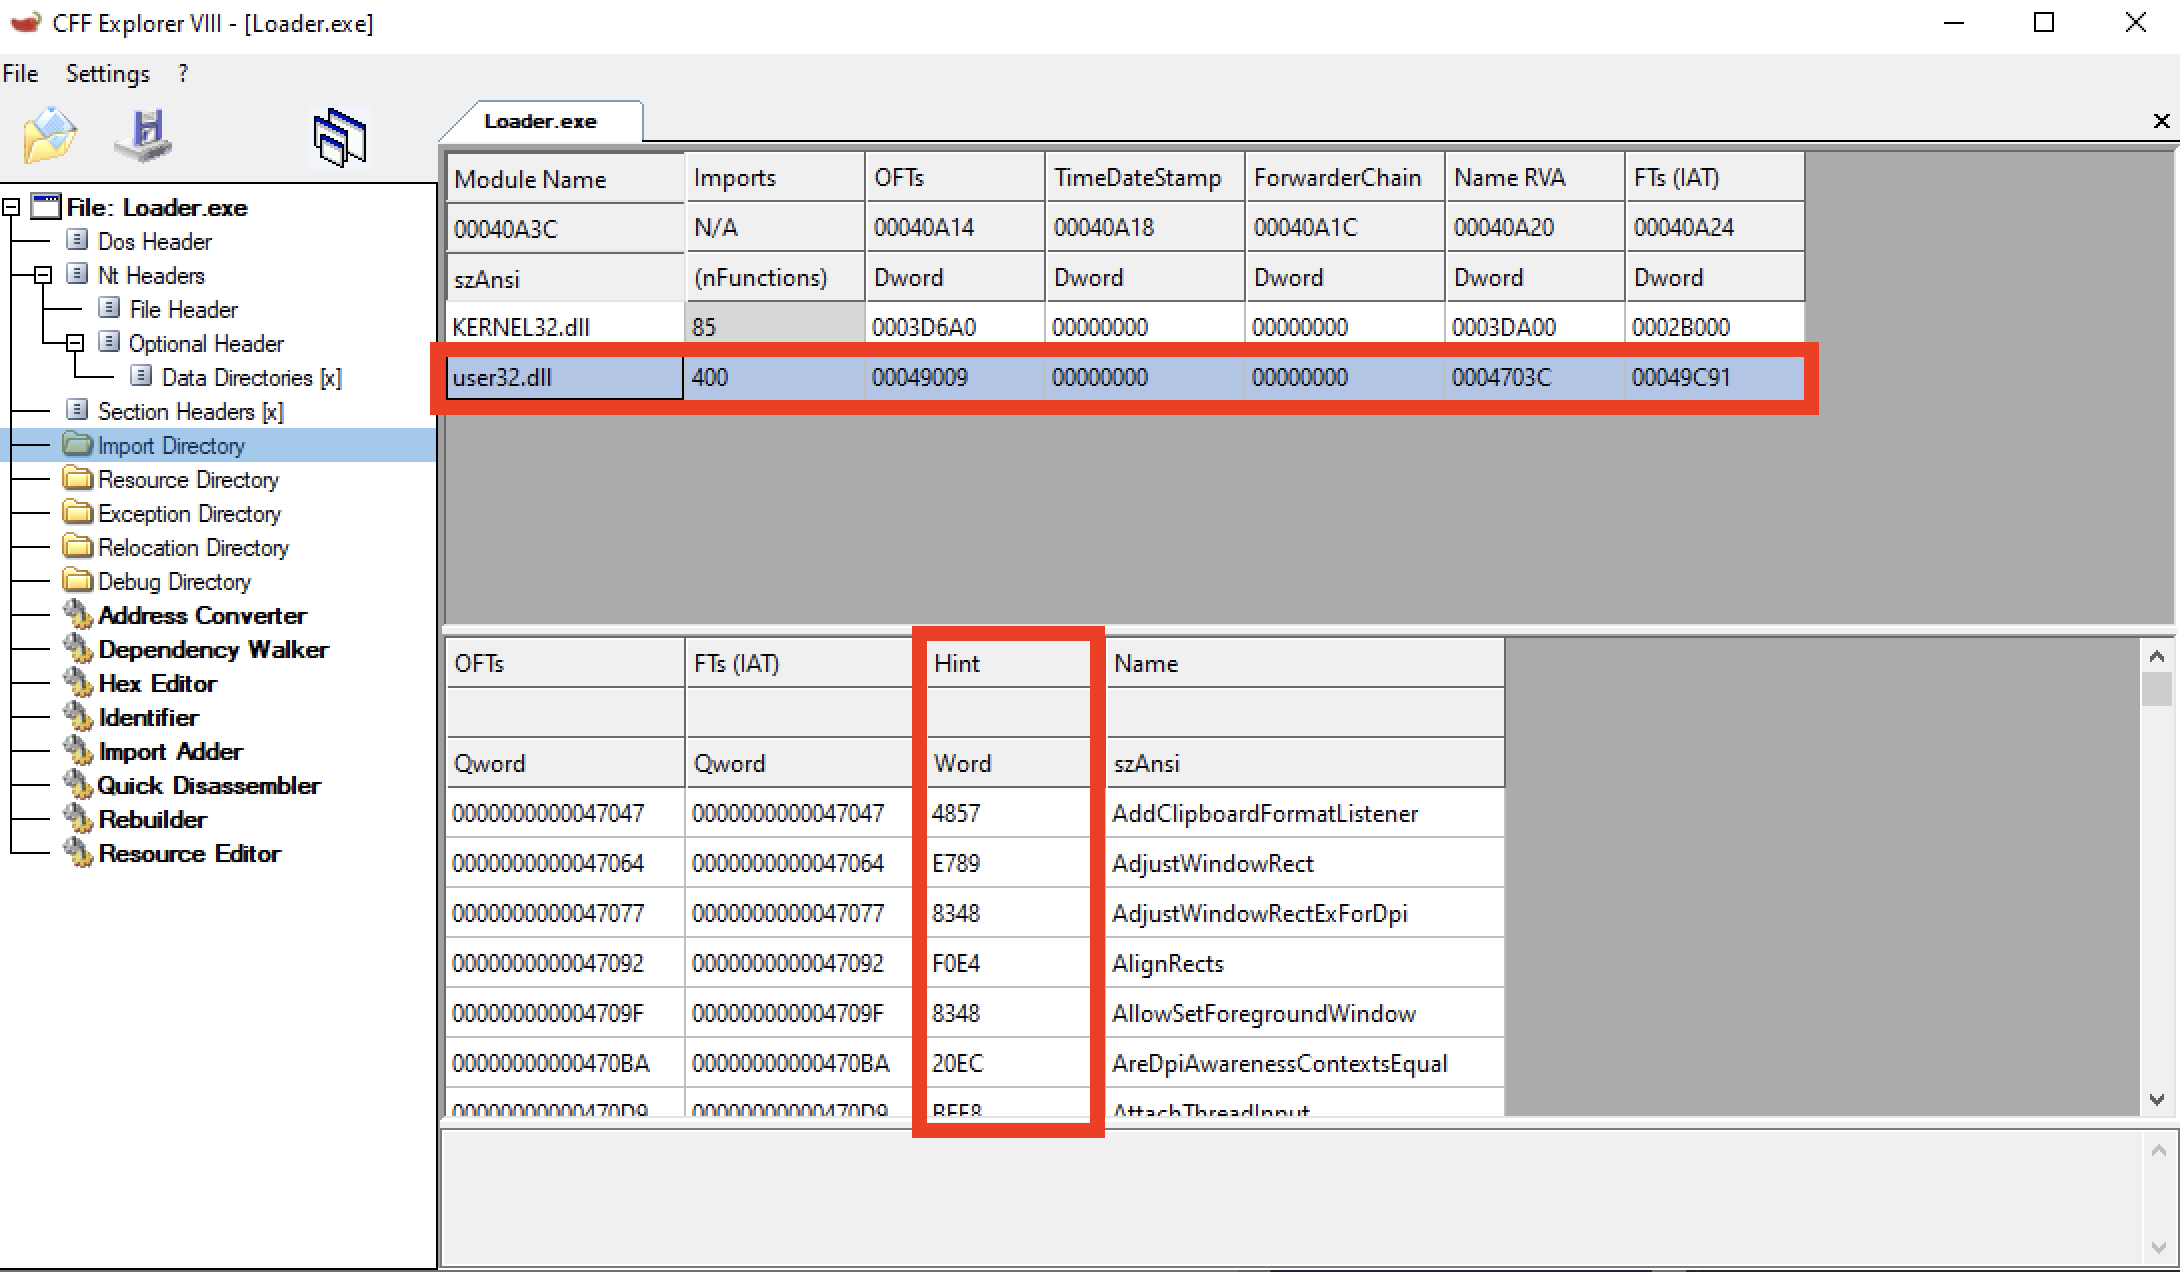 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 winterknife/evenstar
Intel 64/Windows low-level experiments
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 zznop/sploit
Go package that aids in binary analysis and exploitation