Shellcode-Injection-Techniques

C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…

C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment

My experiments in weaponizing Nim (https://nim-lang.org/)

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.

WNF Code Execution Library Using C#


Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll

PoCs and tools for investigation of Windows process execution techniques

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

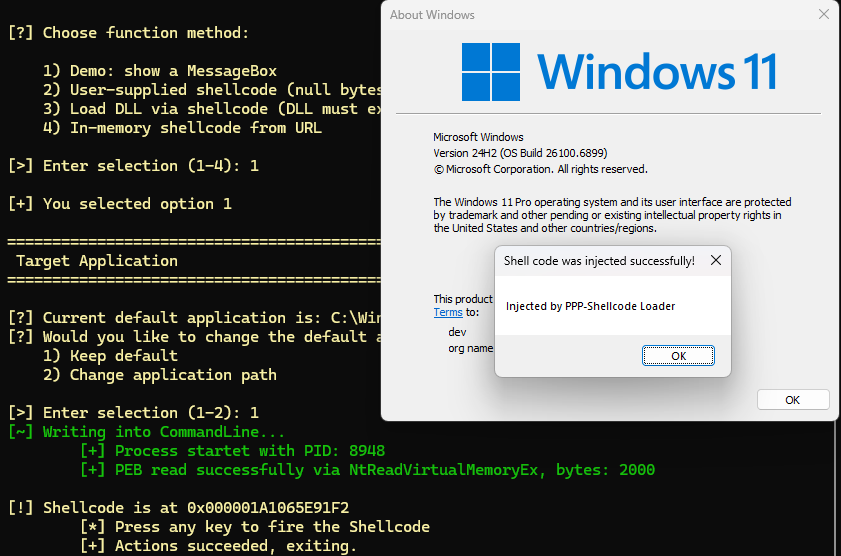
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…

PoC demonstrating a multi process injection chain aimed at remotely executing shellcode

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.

Windows memory hacking library

Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…