
sgn
 egebalci/sgn
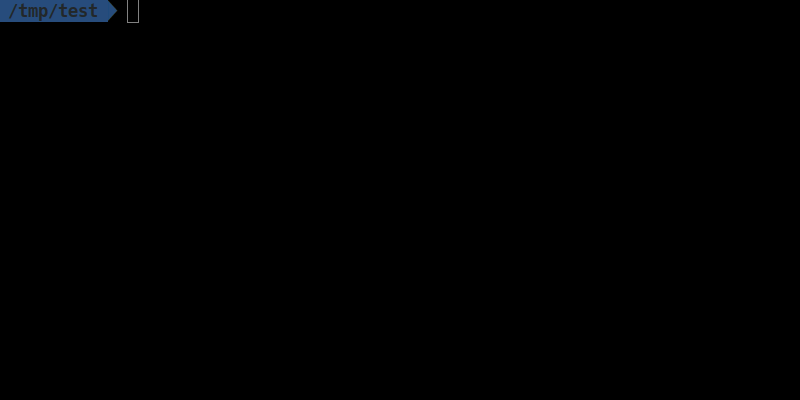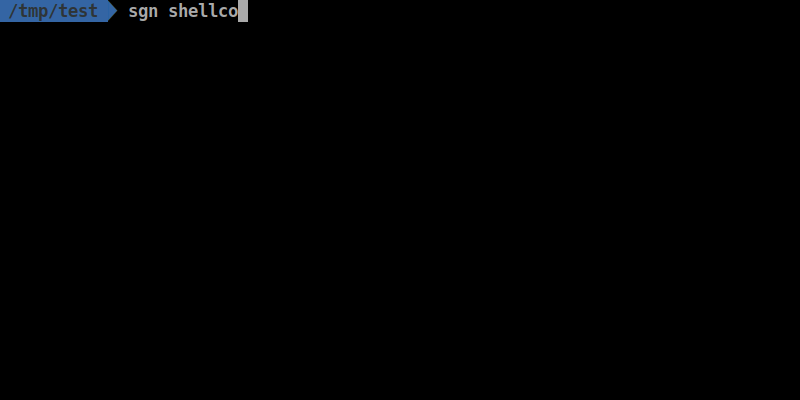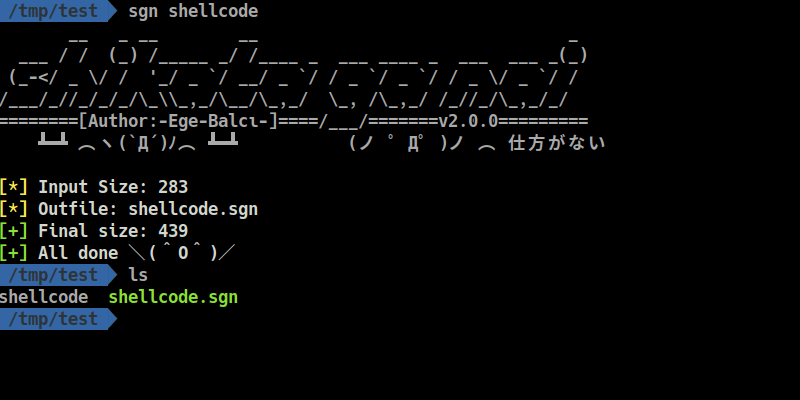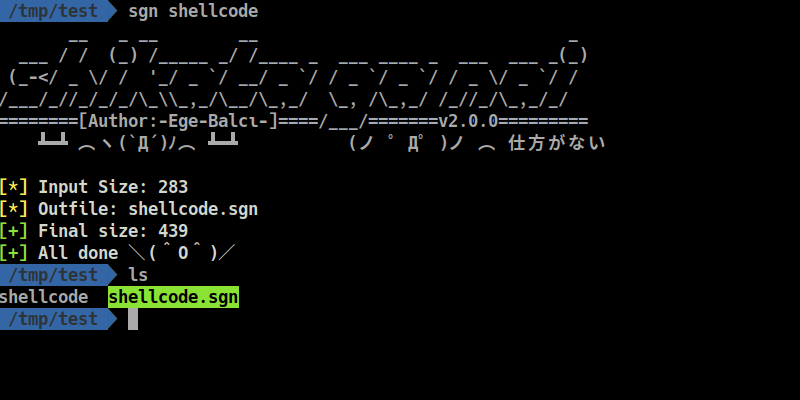
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
ids-ips-evasionpayload-developmentpayload-generation+2
2.0k
egebalci/sgnPolymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 sensepost/ruler
A tool to abuse Exchange services
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
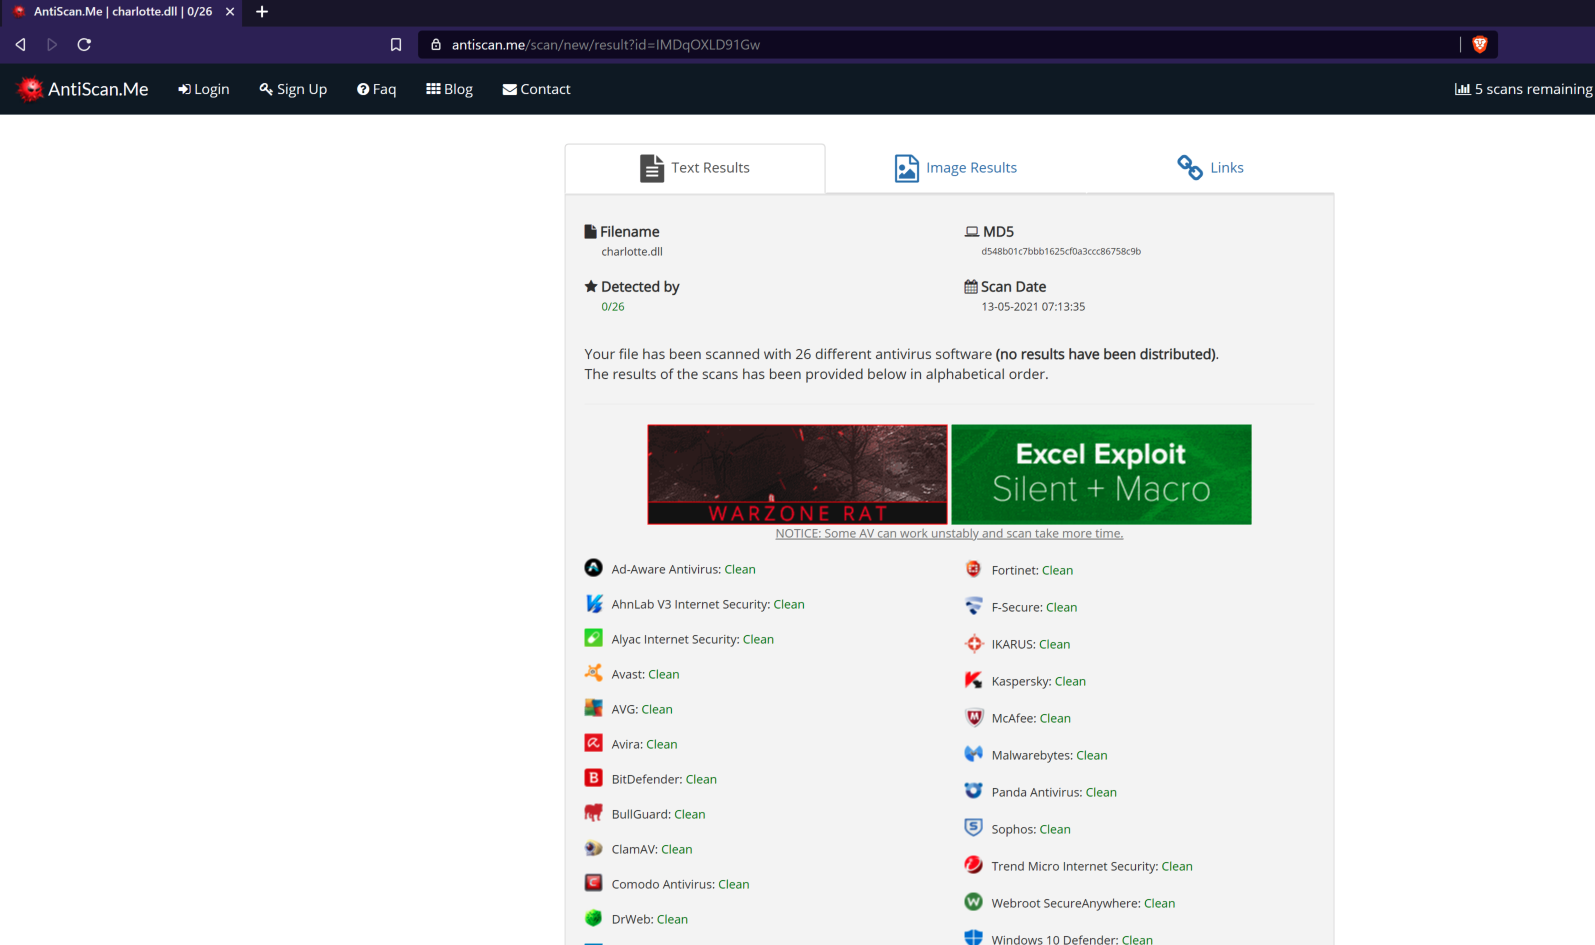 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 wireghoul/htshells
Self contained htaccess shells and attacks
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
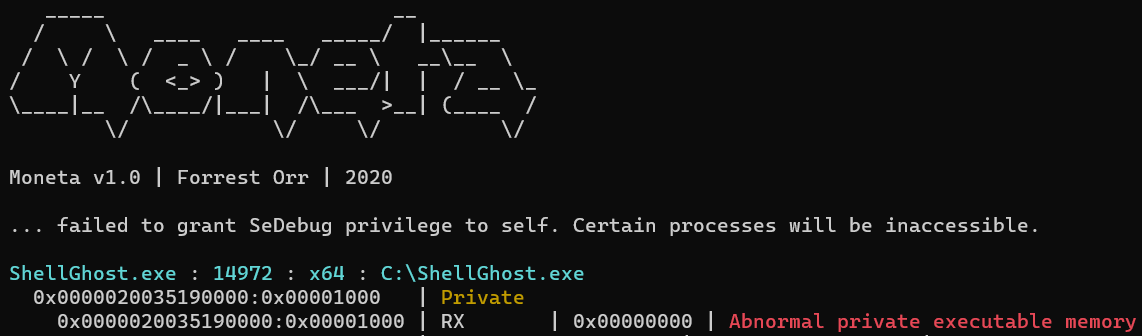 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 egebalci/amber
Reflective PE packer.
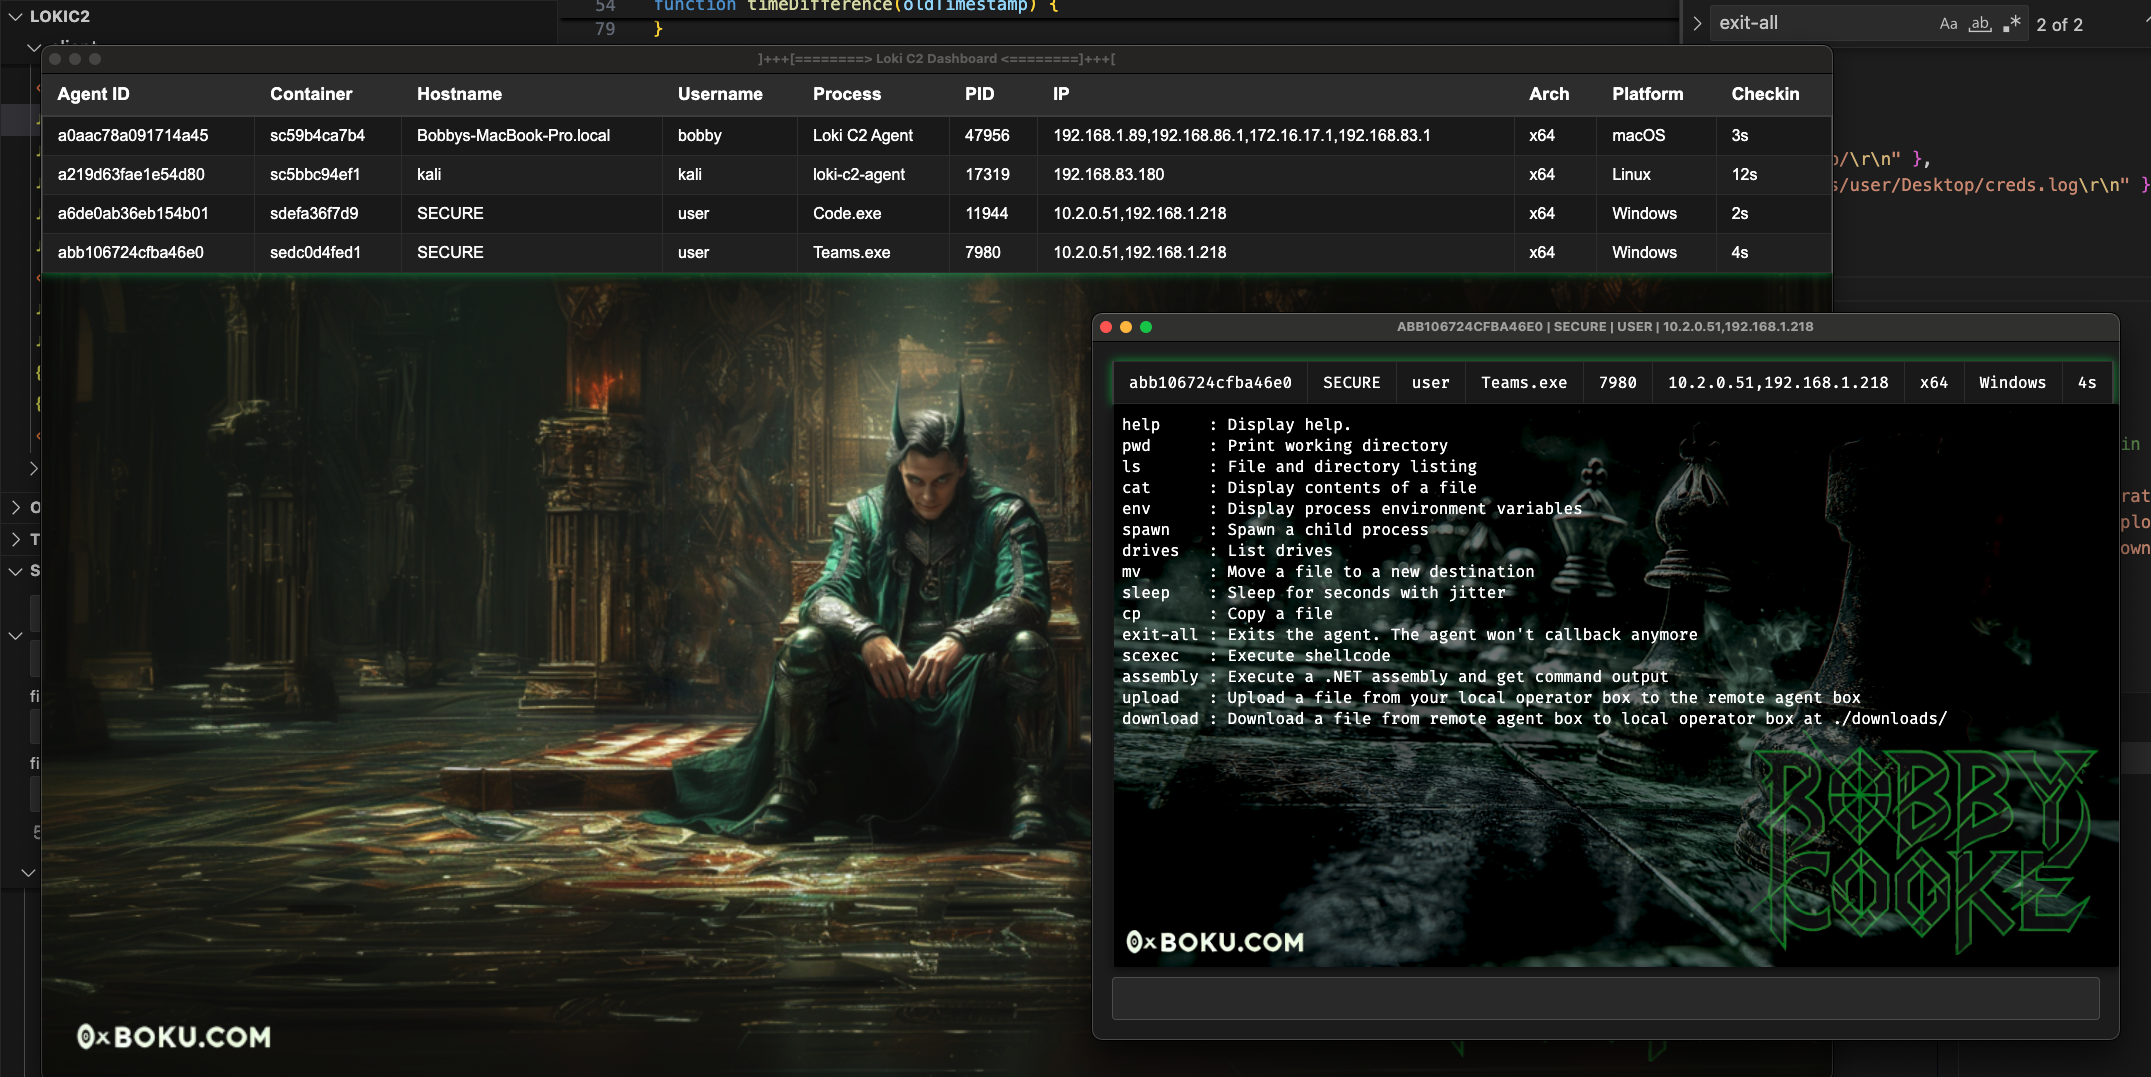 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
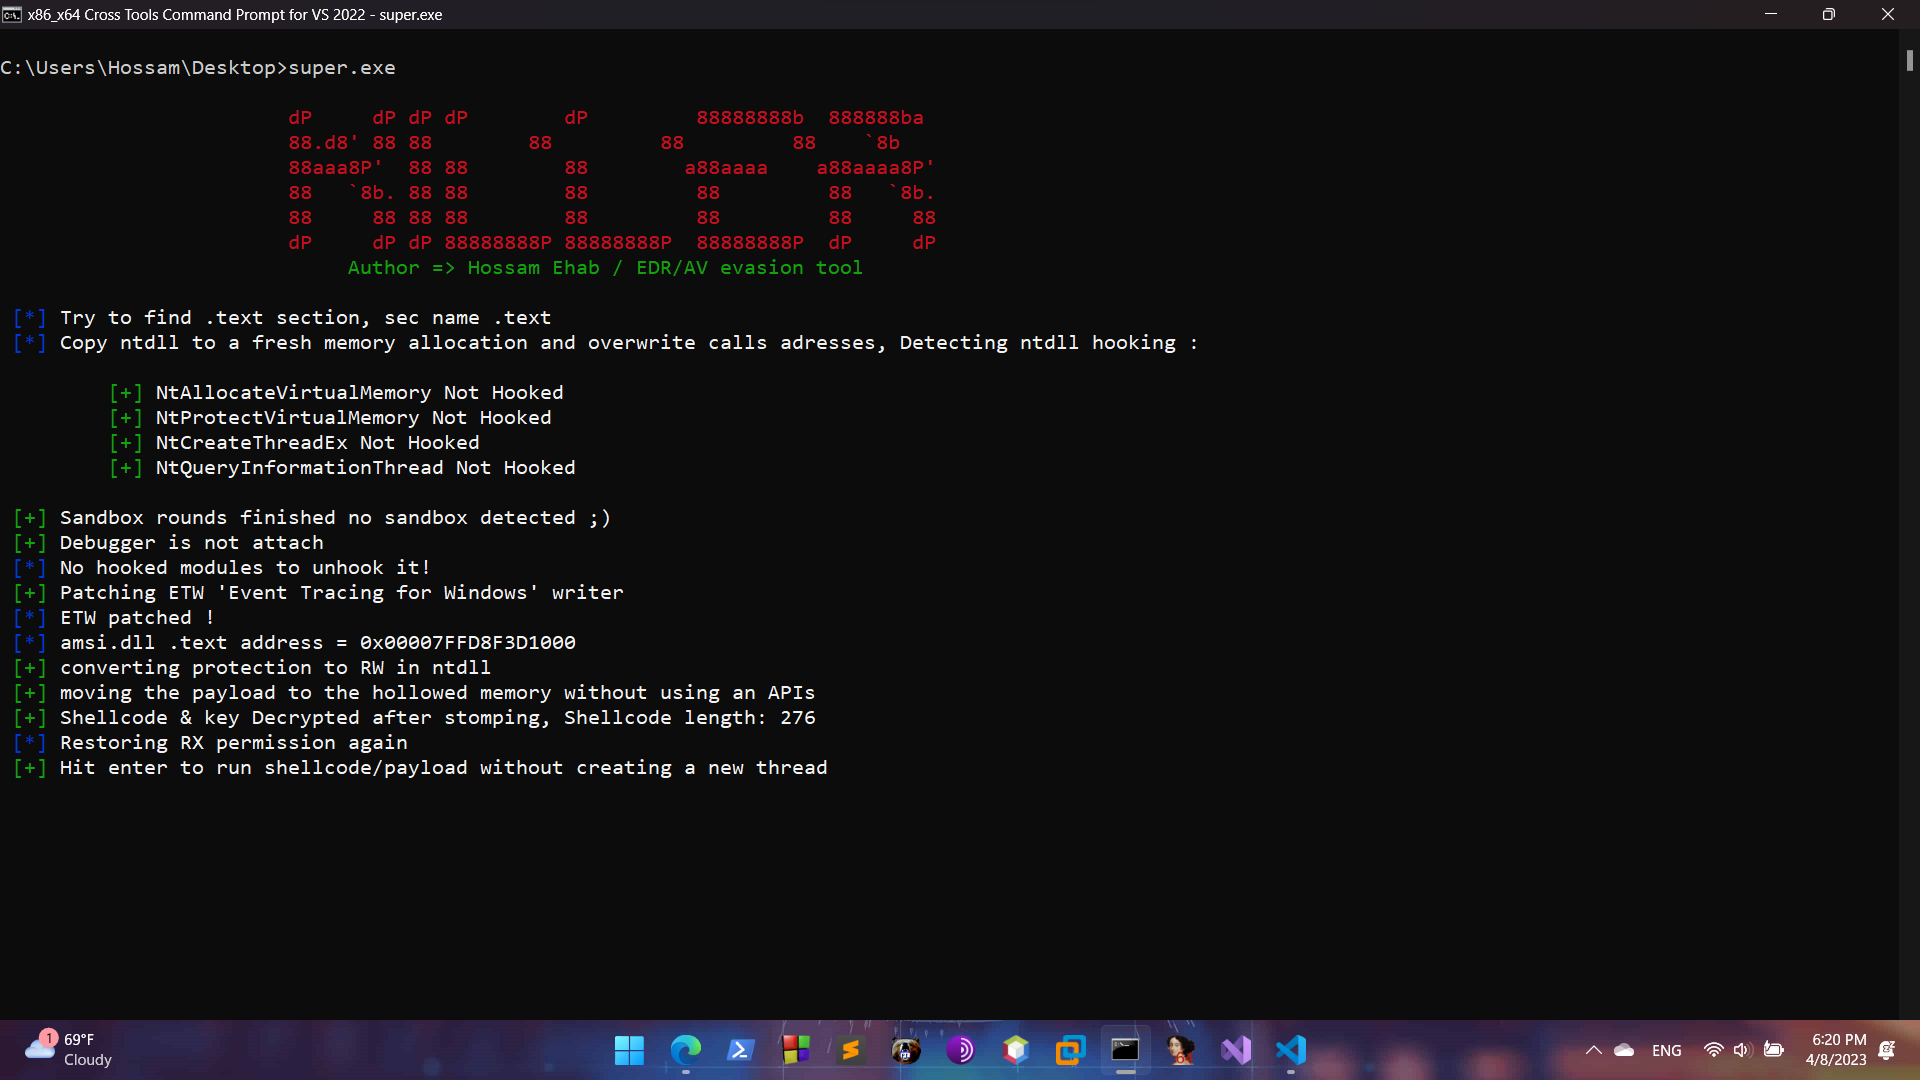 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
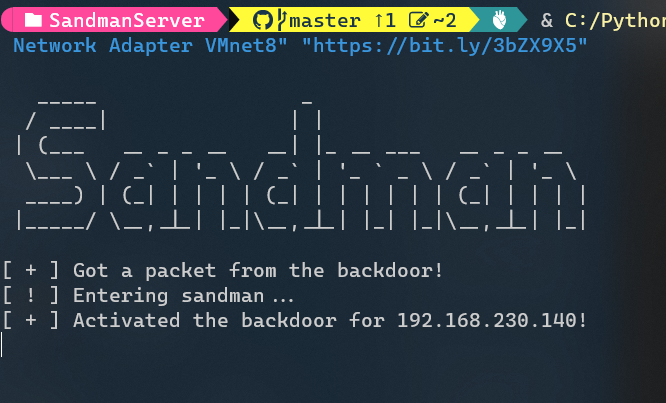 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。