
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
95 results
InjectSetConsole preview

InjectSetConsole

GitHubtwosevenonet/injectsetconsole

Proof of Concept for Process Code Injection Without Using WriteProcessMemory
command-and-controlexploitationids-ips-evasion+7
160
1 month ago
DuplexSpyCS preview

DuplexSpyCS

GitHubiss4cf0ng/duplexspycs

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
command-and-controleducationpayload-development+5
2347 months ago
RustyWater-ShellCode-Dropper preview

RustyWater-ShellCode-Dropper

GitHubs3n4t0r-0x0/rustywater-shellcode-dropper

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
binary-exploitationcommand-and-controlexploitation+9
1053 months ago
ProcessStomping preview

ProcessStomping

GitHubnaksyn/processstomping

A variation of ProcessOverwriting to execute shellcode on an executable's section
binary-exploitationeducationpayload-development+3
1472 years ago
Cobaltstrike_BOFLoader preview

Cobaltstrike_BOFLoader

GitHubcodextf2/cobaltstrike_bofloader

open source port/reimplementation of the Cobalt Strike BOF Loader as is
binary-exploitationexploit-frameworkspayload-development+3
7426 days ago
ds3-nrssr-rce preview

ds3-nrssr-rce

GitHubtremwil/ds3-nrssr-rce

Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
binary-exploitationeducationexploitation+8
1694 years ago
DynamicDotNet preview

DynamicDotNet

GitHubbohops/dynamicdotnet

A collection of various and sundry code snippets that leverage .NET dynamic tradecraft
curated-resourceseducationmalware-analysis+4
1442 years ago
Pokemon-Shellcode-Loader preview

Pokemon-Shellcode-Loader

GitHubtechryptic/pokemon-shellcode-loader

Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.

adversarial-attackpayload-developmentpayload-generation+3
1264 years ago
SyscallRevenant preview

SyscallRevenant

GitHubsilentisvox/syscallrevenant

Clean Indirect Syscalls with Syscall Tampering.
binary-exploitationexploitationids-ips-evasion+6
497 days ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
671 month ago
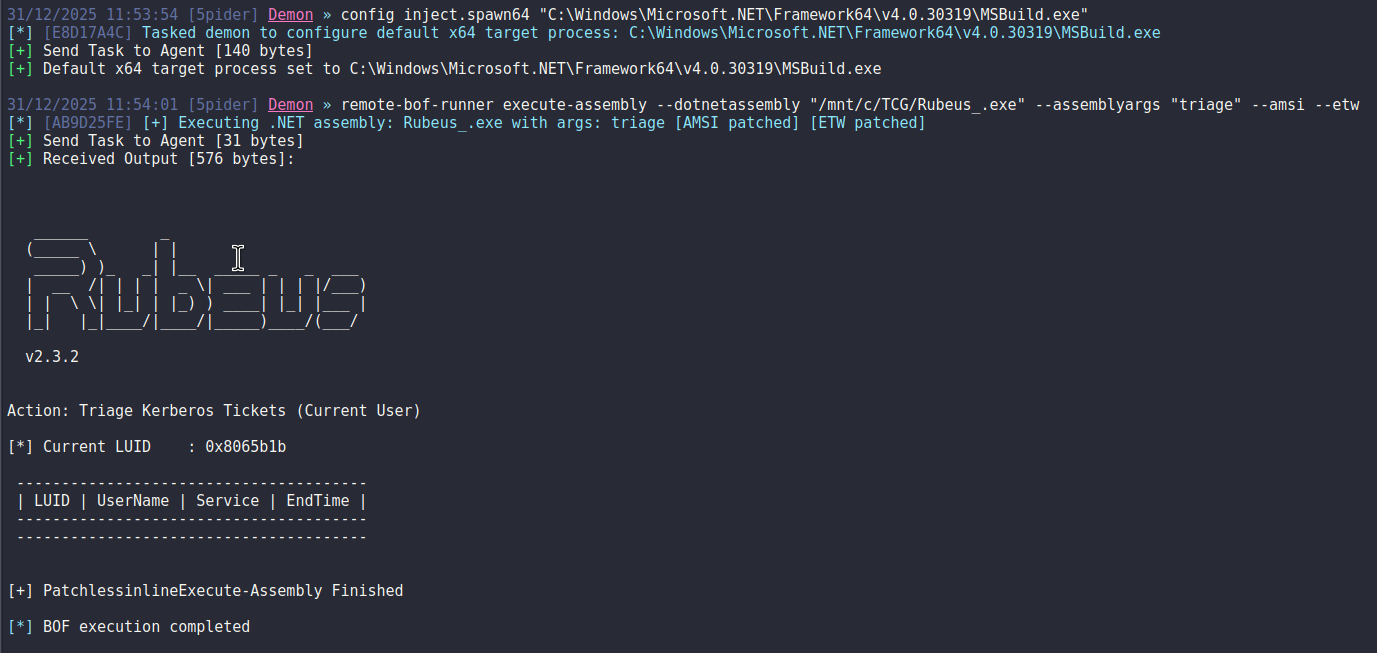
Remote-BOF-Runner preview

Remote-BOF-Runner

GitHubpard0p/remote-bof-runner

Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
binary-exploitationcommand-and-controleducation+8
10210 months ago
XeytanWin32-RAT preview

XeytanWin32-RAT

GitHubmelardev/xeytanwin32-rat

WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
207 years ago
CVE-2020-0022 preview

CVE-2020-0022

GitHubthemmokhtar/cve-2020-0022

A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
android-securitybinary-exploitationbluetooth-security+7
222 years ago
XeytanWxCpp-RAT preview

XeytanWxCpp-RAT

GitHubmelardev/xeytanwxcpp-rat

Work in Progress. RAT written in C++ using wxWidgets
command-and-controlinformation-gatheringpayload-development+3
117 years ago
CVE-2018-8941 preview

CVE-2018-8941

GitHubsecforce/cve-2018-8941

D-Link DSL-3782 Code Execution (Proof of Concept)
binary-exploitationembedded-systems-securityexploitation+6
98 years ago
GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC preview

GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC

GitHubchainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc

Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.

binary-exploitationeducationexploitation+5
131 year ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
52 months ago
Windows-X64-RAT preview

Windows-X64-RAT

GitHubmaorbuskila/windows-x64-rat

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…

binary-exploitationcommand-and-controleducation+5
22 years ago
Previous123456Next