
EXCELntDonut
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
exploitationpayload-generationphishing+4
5166 years ago
redsiege/excelntdonutExcel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
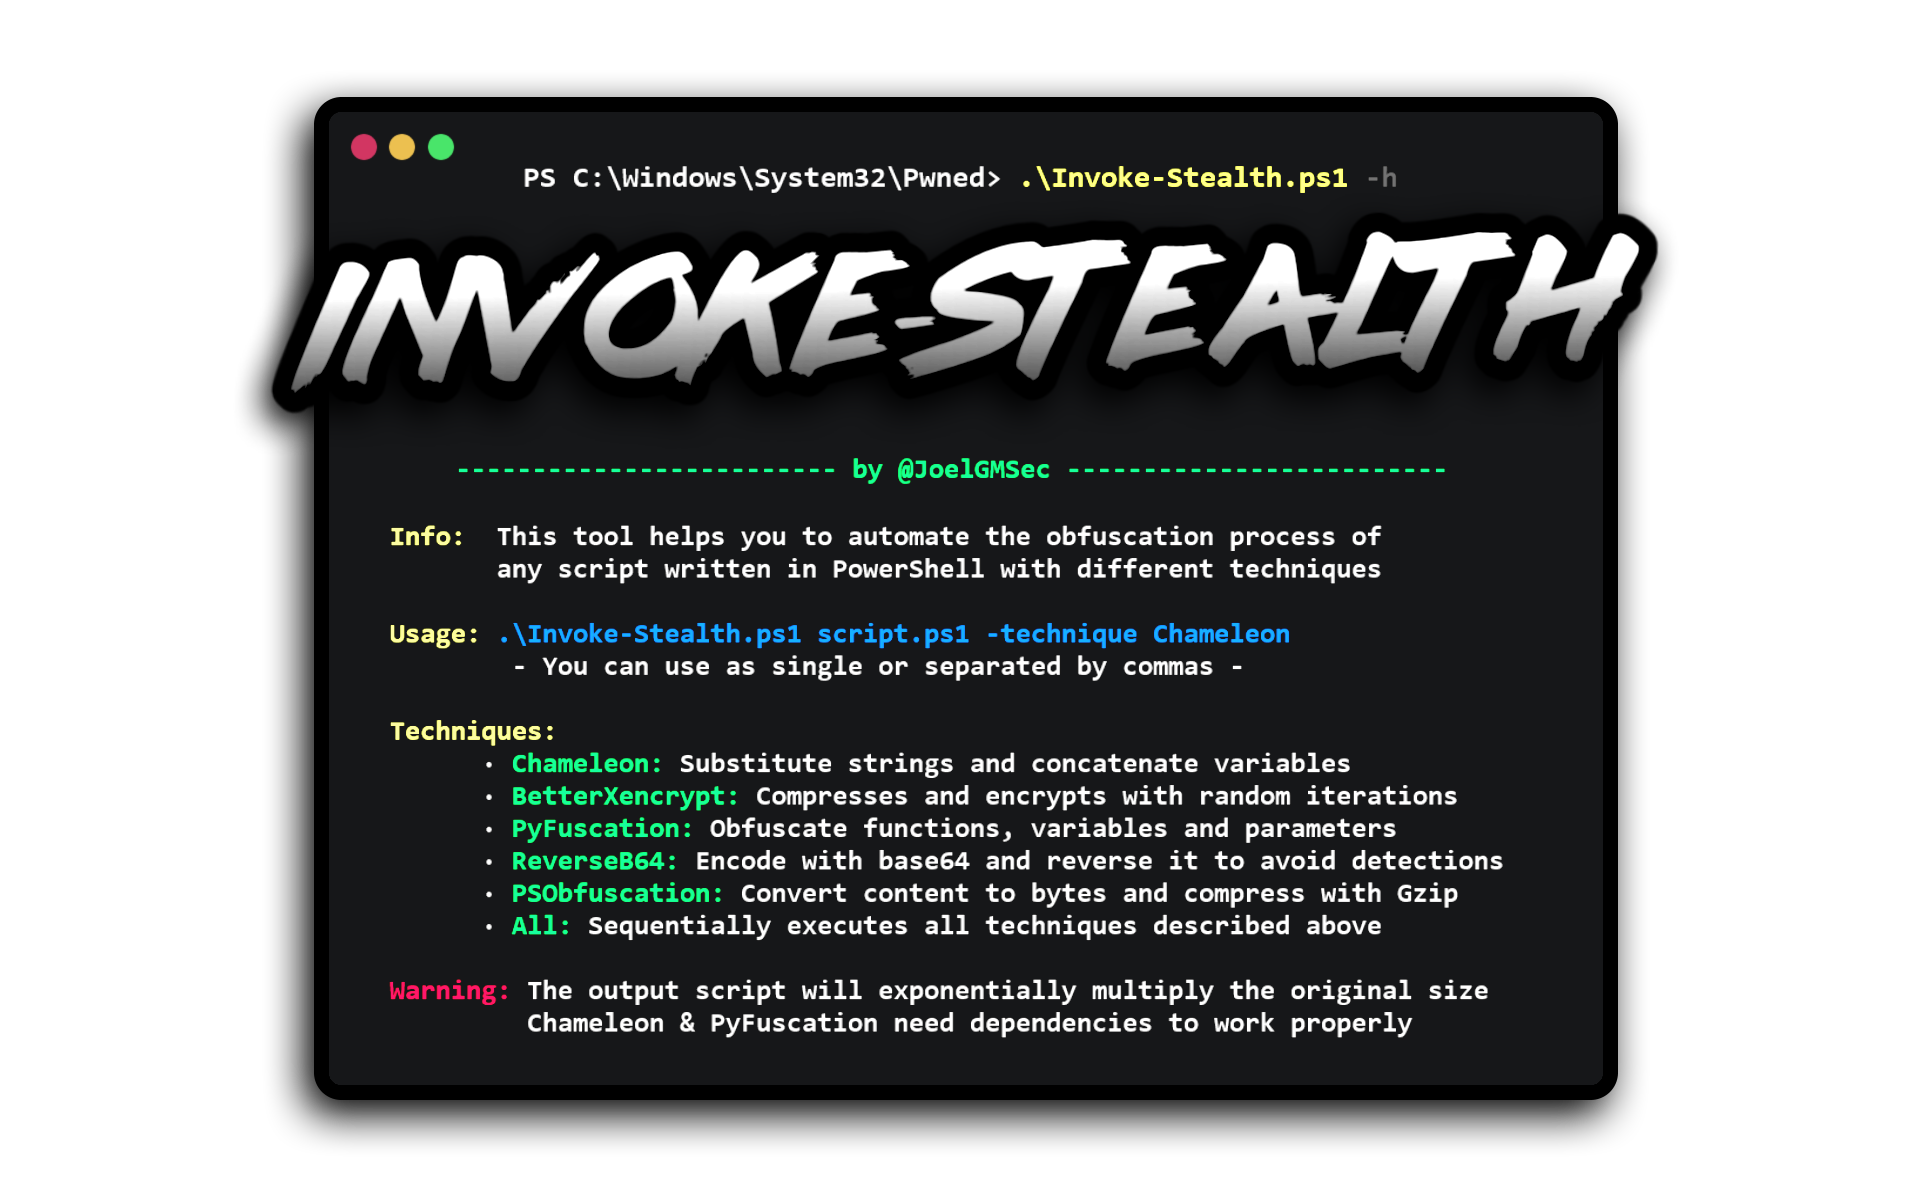 joelgmsec/invoke-stealth
Simple & Powerful PowerShell Script Obfuscator
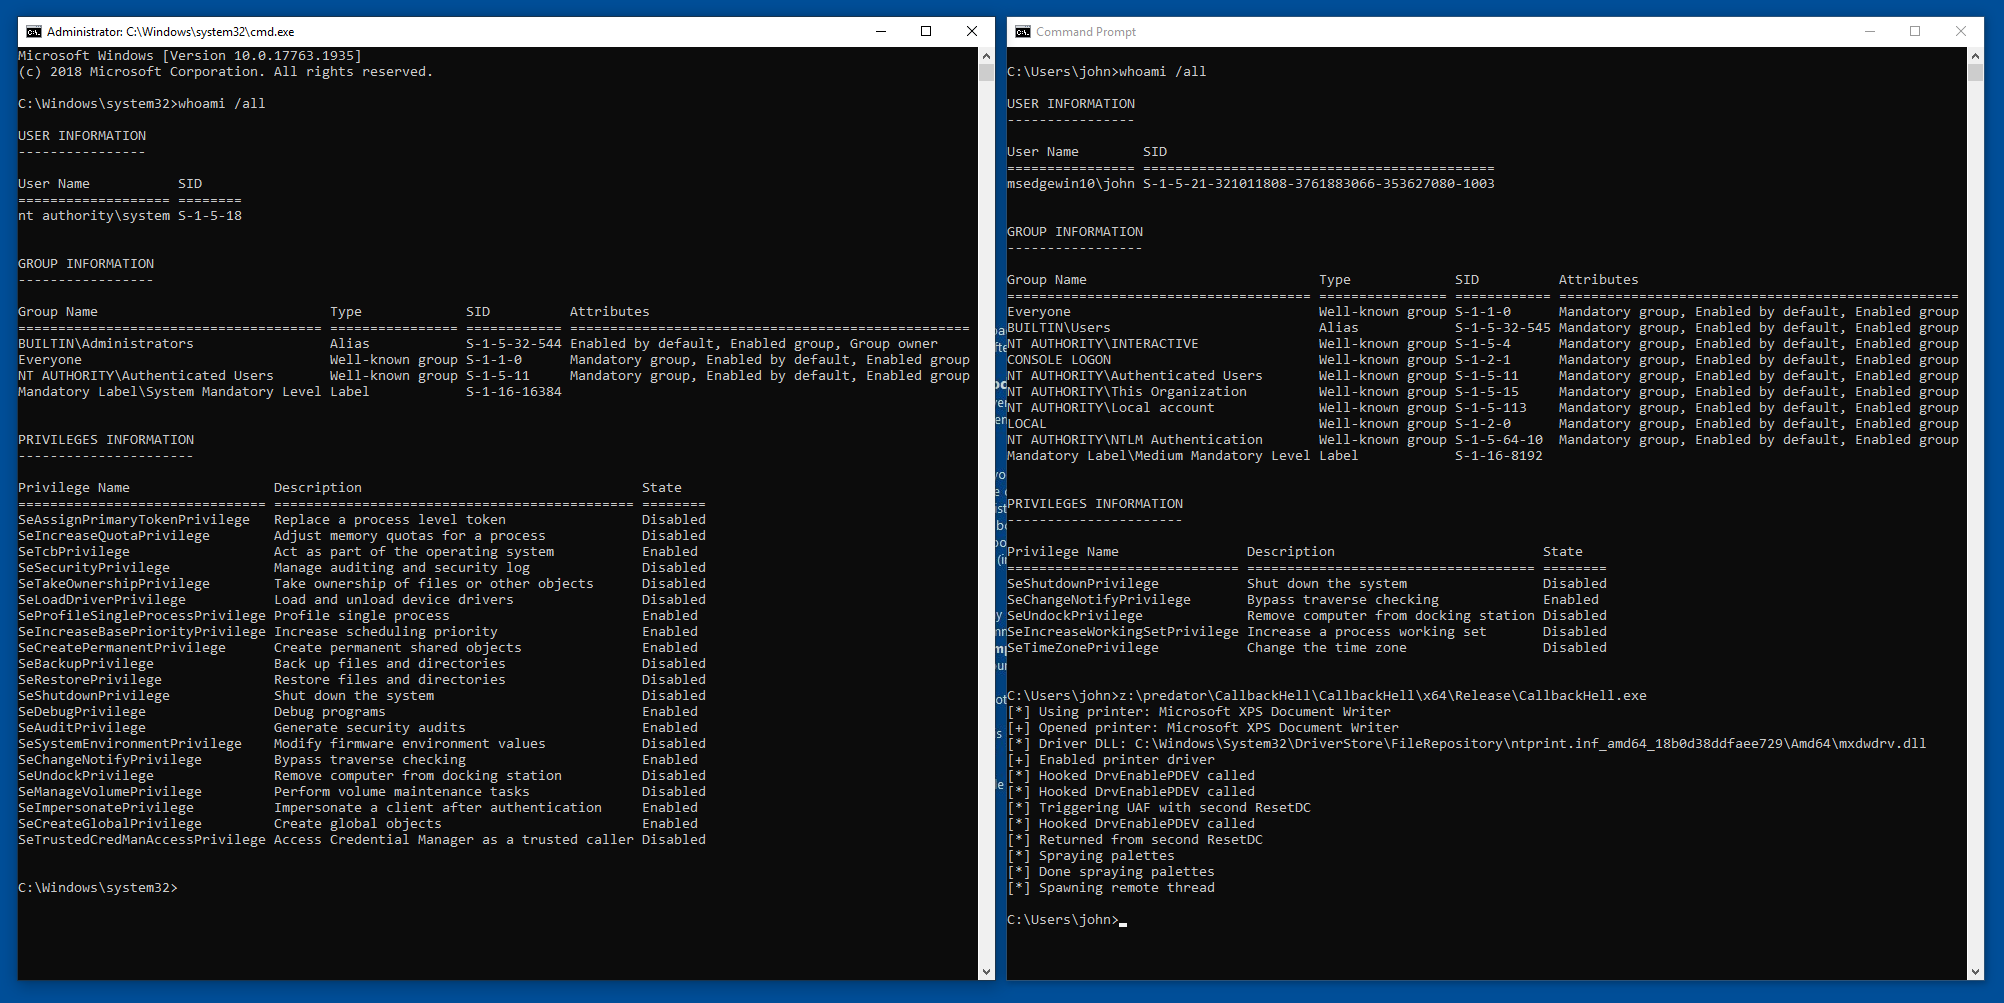 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 wra7h/flavortown
Various ways to execute shellcode
 peterferrie/win-exec-calc-shellcode
A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)
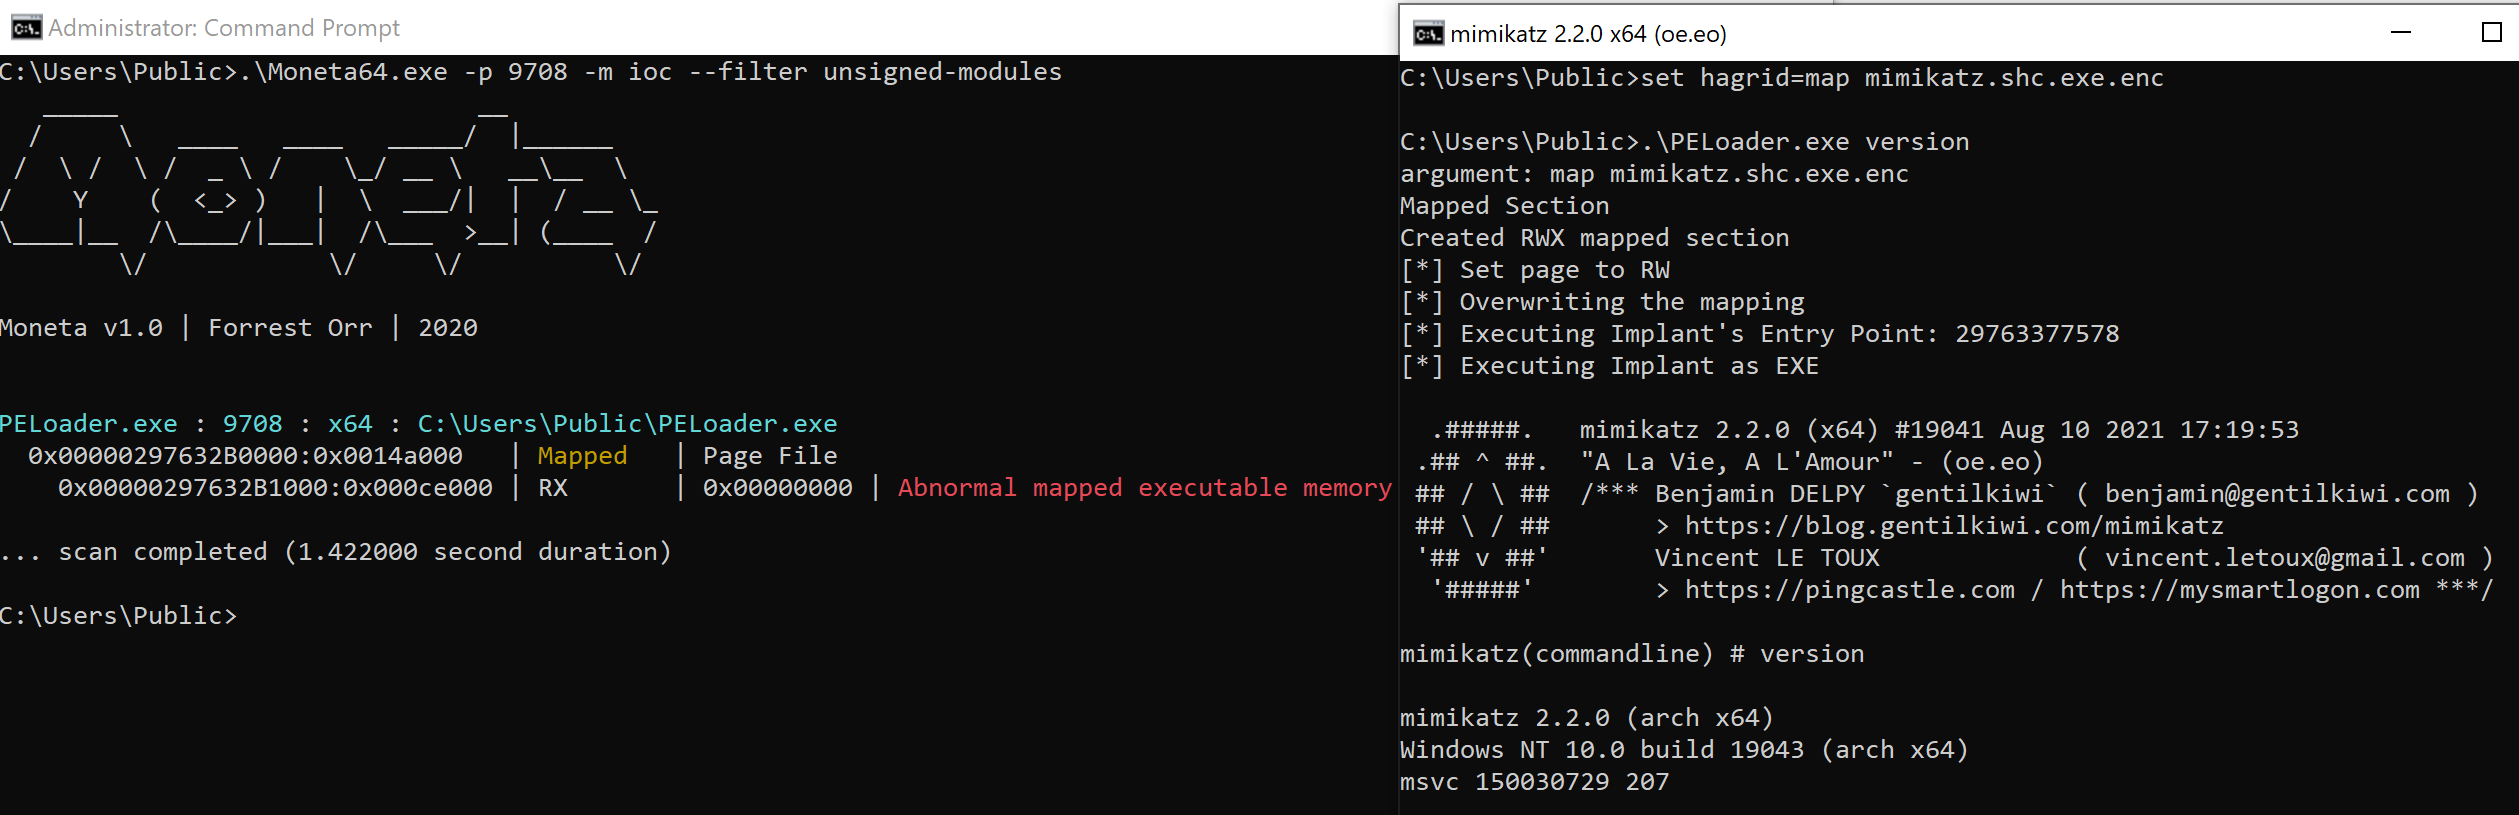 hagrid29/peloader
PE loader with various shellcode injection techniques
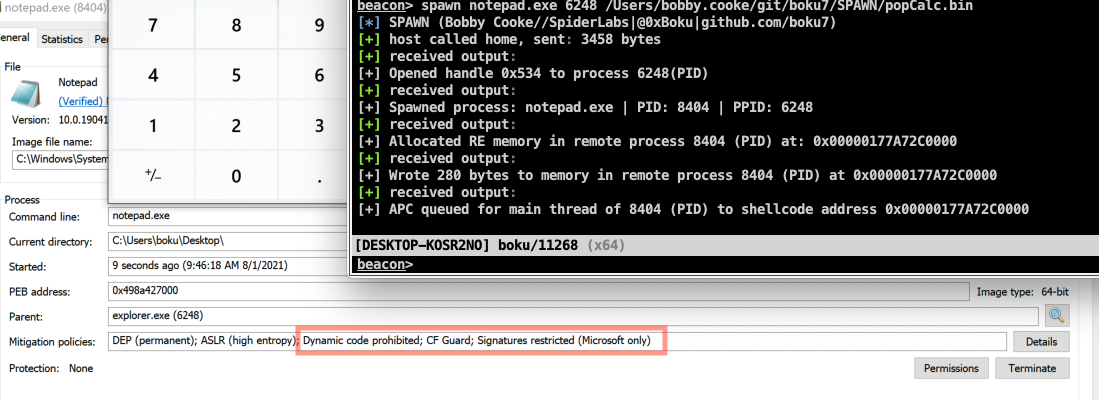 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server

 rip1s/cve-2017-11882
CVE-2017-11882 Exploit accepts over 17k bytes long command/code in maximum.
 noperator/cve-2019-18935
RCE exploit for a .NET JSON deserialization vulnerability in Telerik UI for ASP.NET AJAX.
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 barriuso/smbghost_automateexploitation
SMBGhost (CVE-2020-0796) Automate Exploitation and Detection
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing