
pwntools
 gallopsled/pwntools
CTF framework and exploit development library
binary-analysisbinary-exploitationctf+7
gallopsled/pwntoolsCTF framework and exploit development library
 bishopfox/sliver
Adversary Emulation Framework
 darthton/blackbone
Windows memory hacking library
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
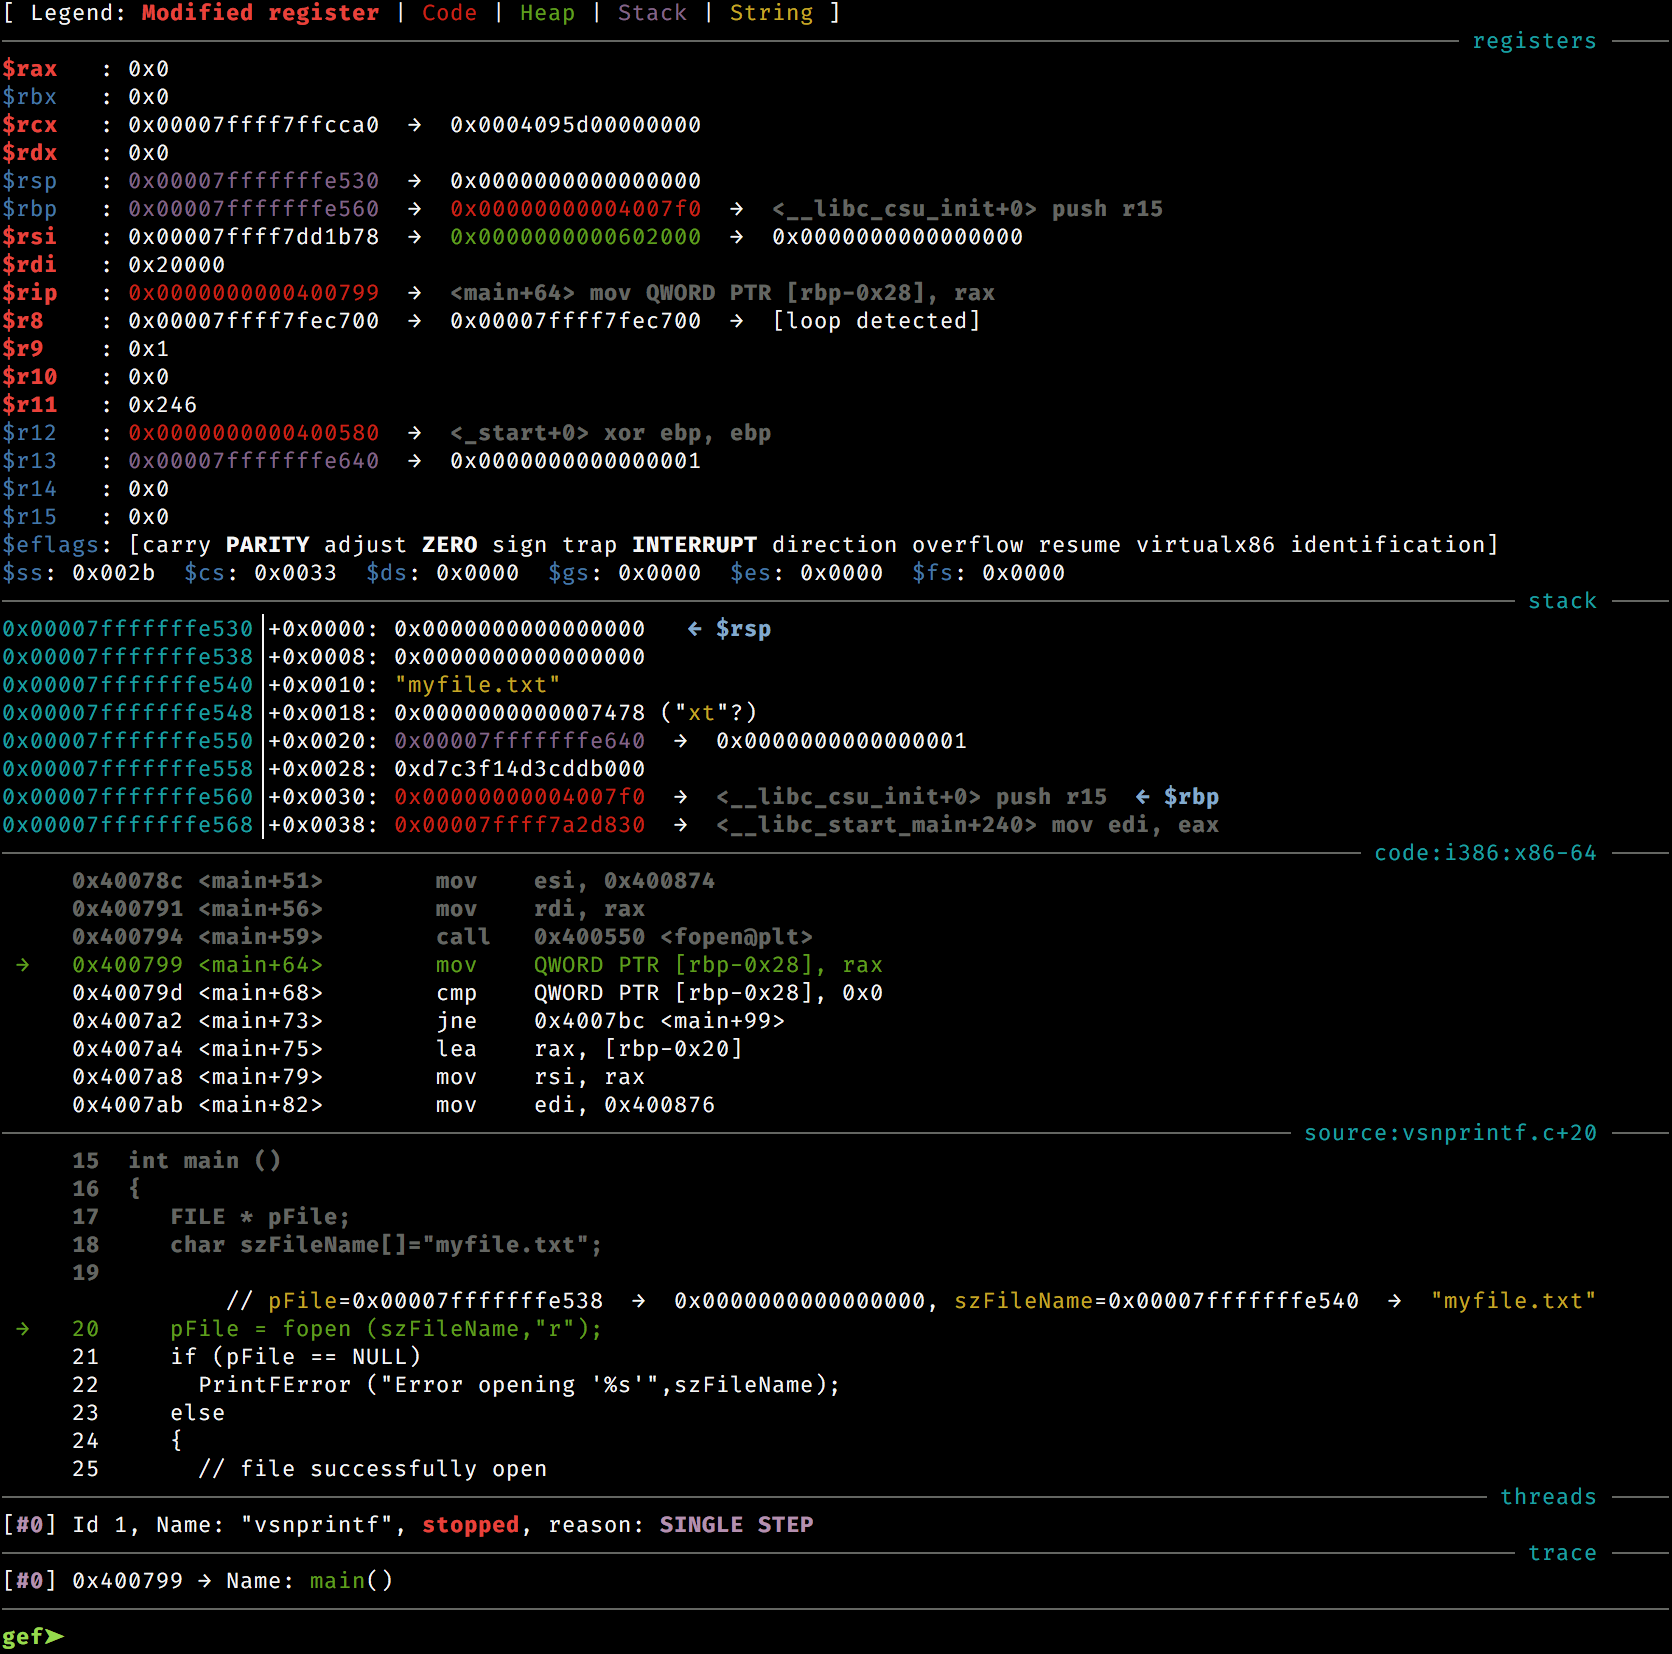 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 ashemery/exploitation-course
Offensive Software Exploitation Course
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
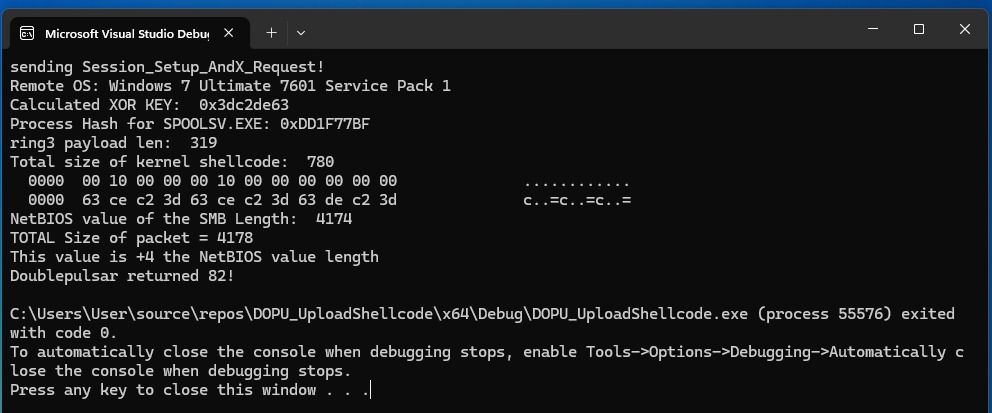 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
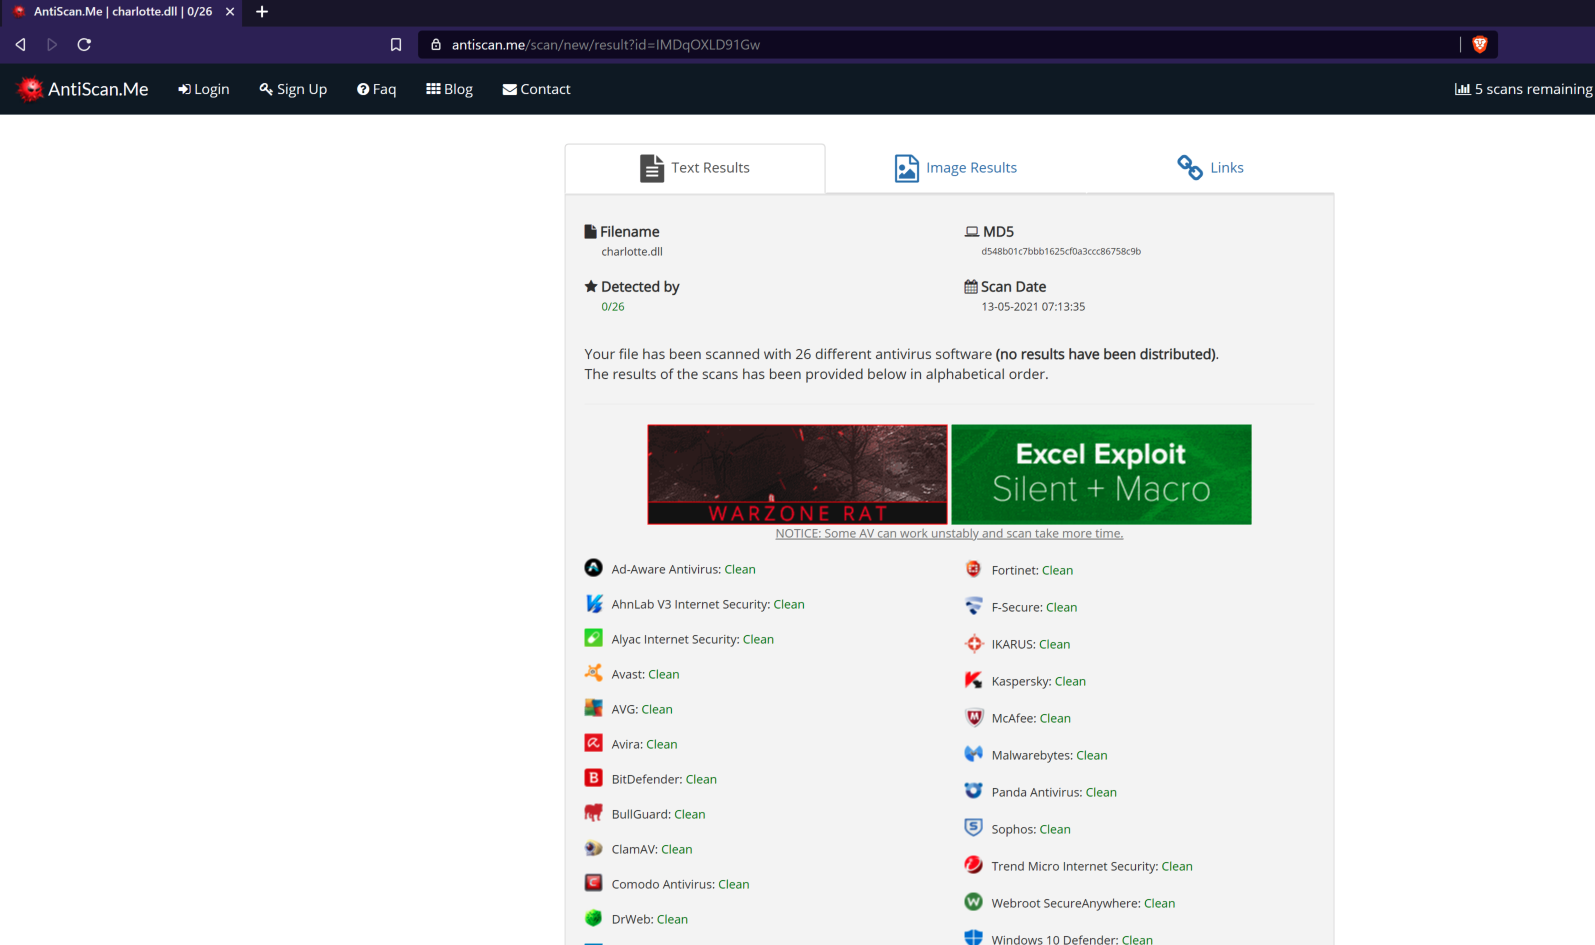 9emin1/charlotte
c++ fully undetected shellcode launcher ;)