
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
844 results
mcreator preview

mcreator

GitHubblacknbunny/mcreator

Encoded Reverse Shell Generator With Techniques To Bypass AV's
command-and-controlexploitationpayload-development+6
144
6 years ago
LdrShuffle preview

LdrShuffle

GitHubrwxstoned/ldrshuffle

Code execution/injection technique using DLL PEB module structure manipulation

binary-exploitationcode-analysisexploitation+6
2881 year ago
acheron preview

acheron

GitHubf1zm0/acheron

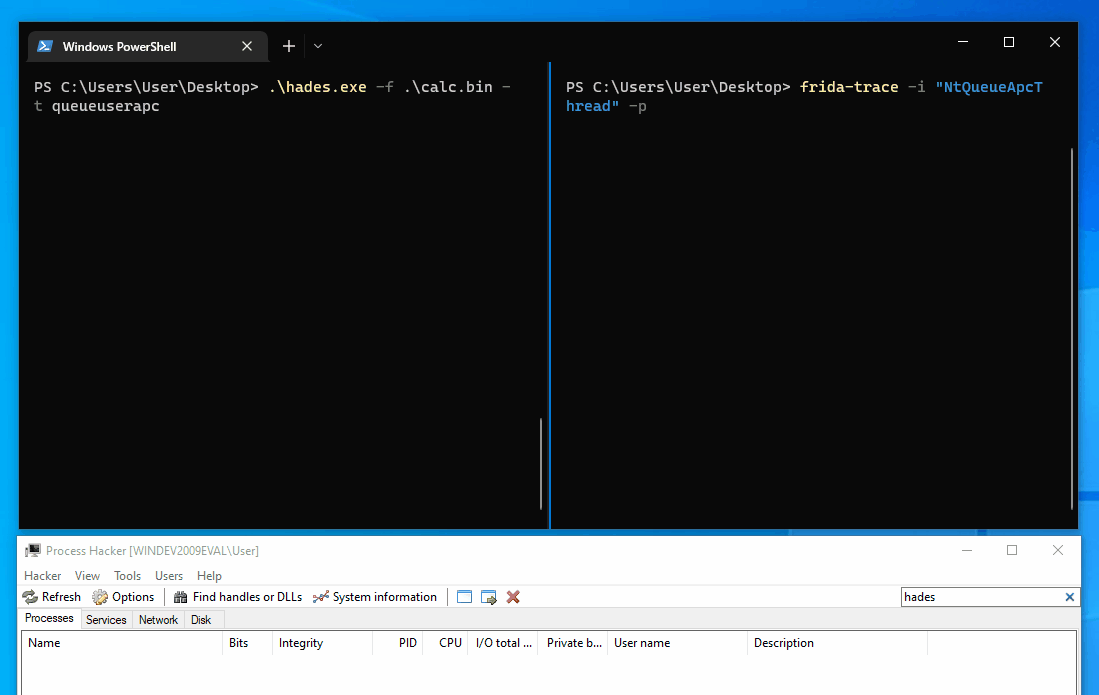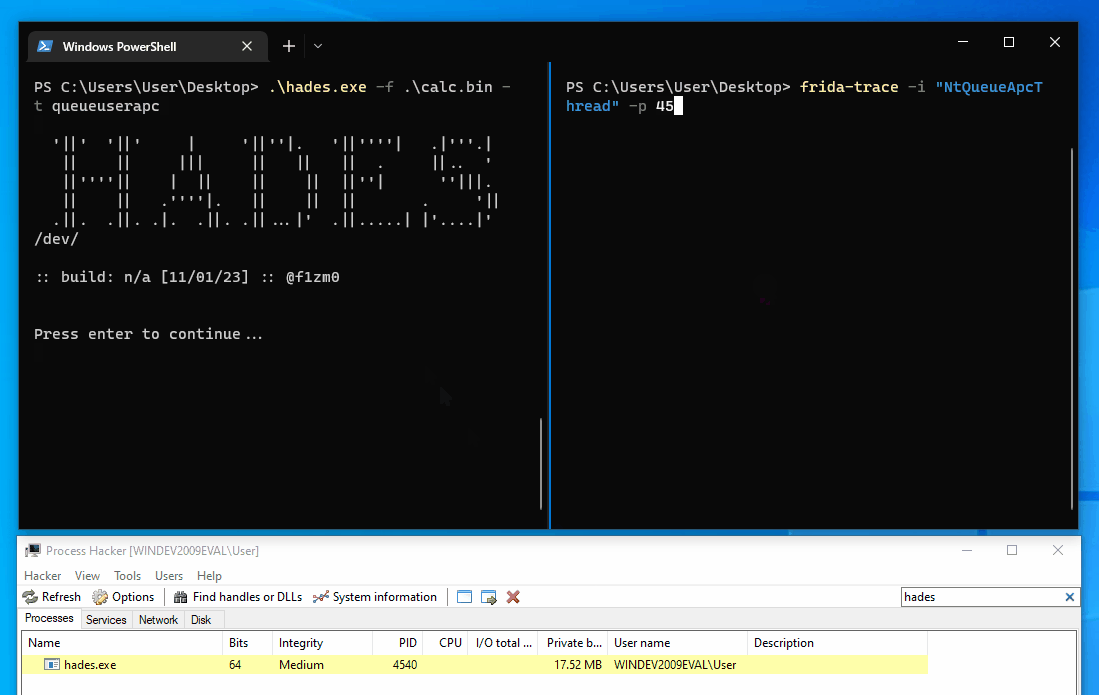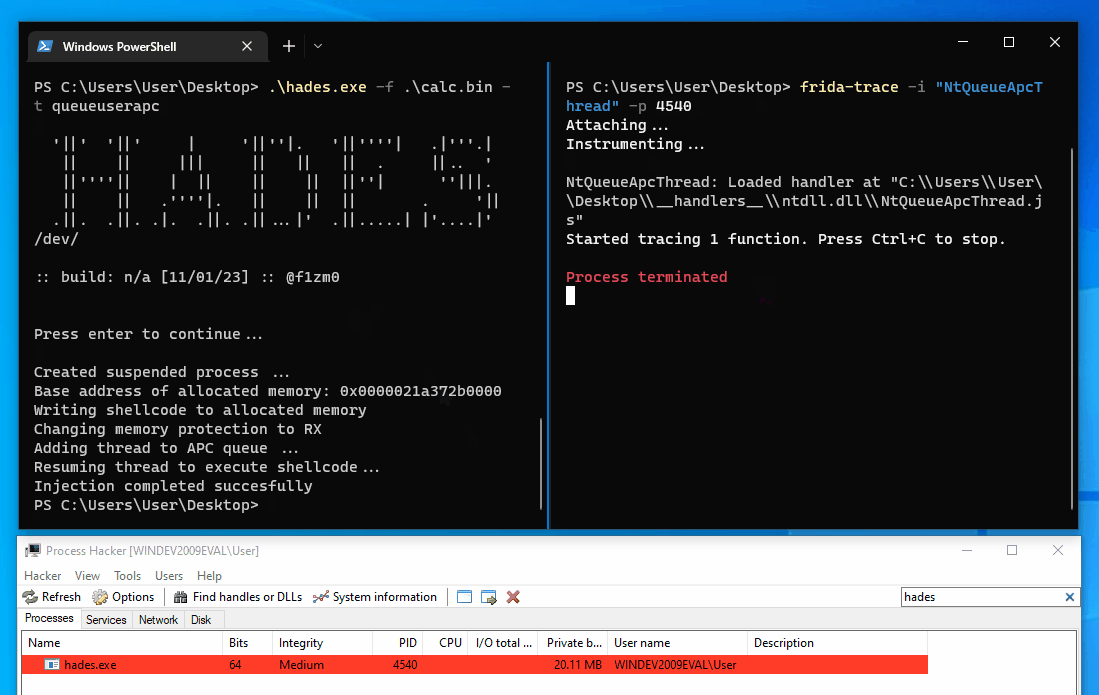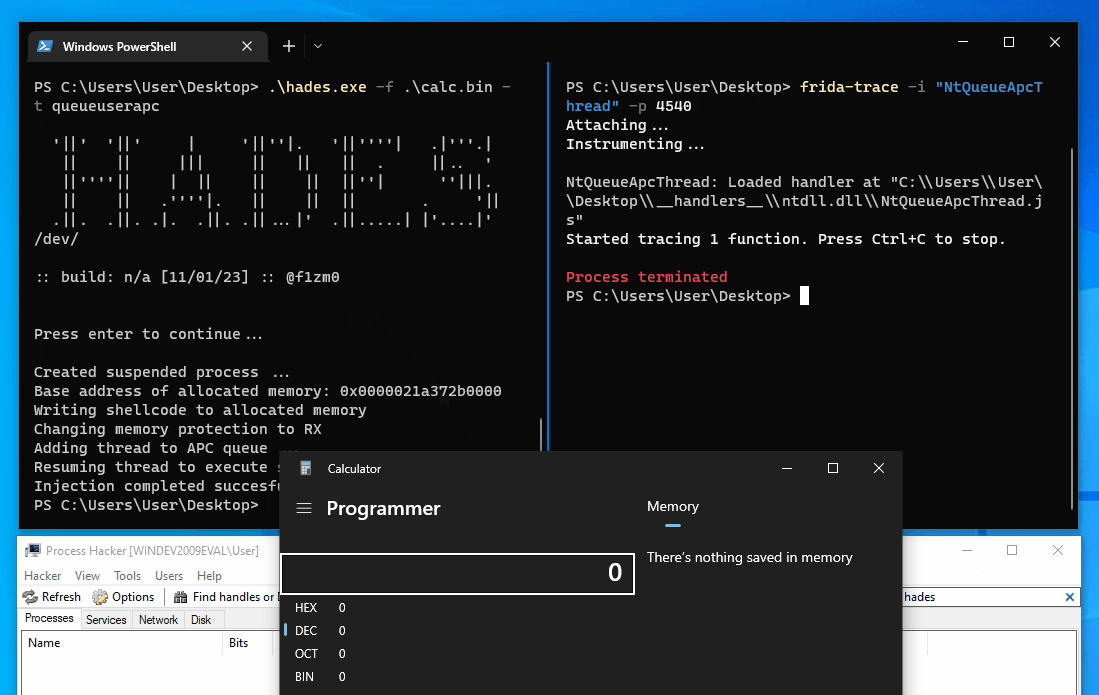
indirect syscalls for AV/EDR evasion in Go assembly
payload-developmentred-teamingshellcode
3933 years ago
hades preview

hades

GitHubf1zm0/hades

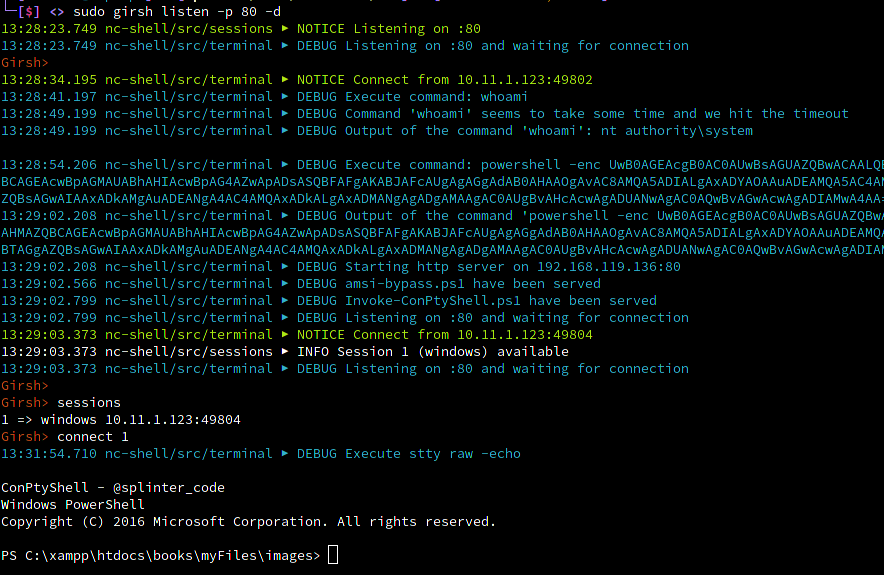
Go shellcode loader that combines multiple evasion techniques
ids-ips-evasionshellcodeshellcode-generation
3923 years ago
Girsh preview

Girsh

GitHubnodauf/girsh

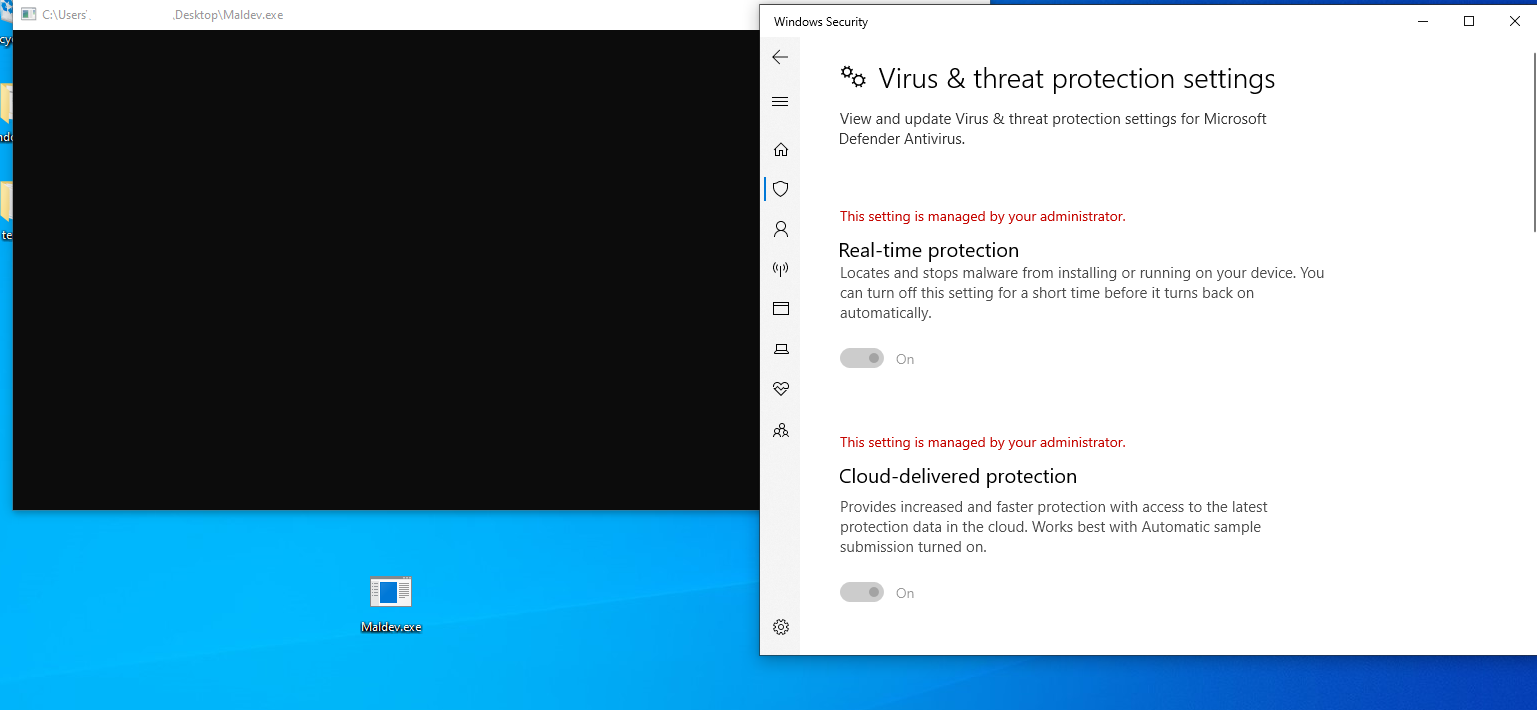
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
3593 years ago
Christmas preview

Christmas

GitHubmaldev-academy/christmas

PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
adversarial-attackids-ips-evasionpayload-development+3
2592 years ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.

exploitationforensicsmalware-analysis+5
2292 years ago
Shelltropy preview

Shelltropy

GitHubkleiton0x00/shelltropy

A technique of hiding malicious shellcode via Shannon encoding.

exploitationmalware-analysispayload-development+1
2693 years ago
NovaLdr preview

NovaLdr

GitHubblacksnufkin/novaldr

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)

code-analysiseducationexploitation+7
2652 years ago
EVENSTAR preview

EVENSTAR

GitHubwinterknife/evenstar

Intel 64/Windows low-level experiments
binary-analysisbinary-exploitationdebuggers+5
11819h 8m ago
LittleCorporal preview

LittleCorporal

GitHubconnormcgarr/littlecorporal

LittleCorporal: A C# Automated Maldoc Generator

code-analysisdynamic-analysis-sandboxingexploitation+7
2265 years ago
InflativeLoading preview

InflativeLoading

GitHubsenzee1984/inflativeloading

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

binary-exploitationexploitationmalware-analysis+3
3262 years ago
linux_injector preview

linux_injector

GitHubnamazso/linux_injector

A simple ptrace-less shared library injector for x64 Linux

adversarial-attackpayload-developmentpenetration-testing+3
2953 years ago
Obfuscator preview

Obfuscator

GitHub3xpl01tc0d3r/obfuscator

The program is designed to obfuscate the shellcode.
encryption-decryption-toolspayload-developmentpayload-generation+2
2025 years ago
ShellCodeEmulator preview

ShellCodeEmulator

GitHubohjeongwook/shellcodeemulator

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment

binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
1266 years ago
NimGetSyscallStub preview

NimGetSyscallStub

GitHubs3cur3th1ssh1t/nimgetsyscallstub

Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
binary-analysisexploitationpayload-generation+2
2314 years ago
Bitmancer preview

Bitmancer

GitHubzimawhit3/bitmancer

Nim Library for Offensive Security Development
binary-analysisids-ips-evasionpayload-development+4
2003 years ago
BOF_ExecuteAssembly preview

BOF_ExecuteAssembly

GitHubntdallas/bof_executeassembly

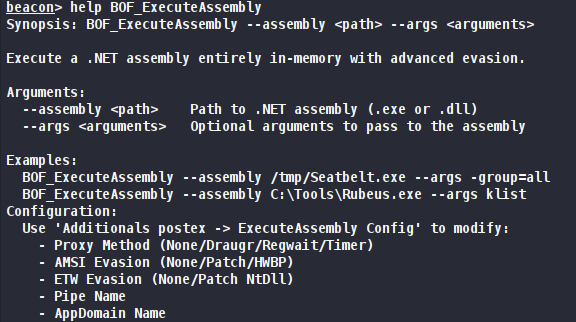
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.

binary-exploitationcommand-and-controlids-ips-evasion+4
1988 months ago
Previous1…282930…47Next