

CustomLoadImage
 backdoorskid/customloadimage
Stealthy .NET assembly loading using AssemblyNative::LoadFromBuffer
defensive-toolsexploitationpenetration-testing+3
58
backdoorskid/customloadimageStealthy .NET assembly loading using AssemblyNative::LoadFromBuffer
 hakivvi/cve-2021-40449
Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
 h3x0v3rl0rd/ms17-010_cve-2017-0143
MS17-010_CVE-2017-0143
 infobyte/exploit-cve-2021-21086
Python-based exploit for CVE-2021-21086 in Adobe Acrobat Reader DC, generating malicious PDFs with shellcode execution via crafted font charstrings.
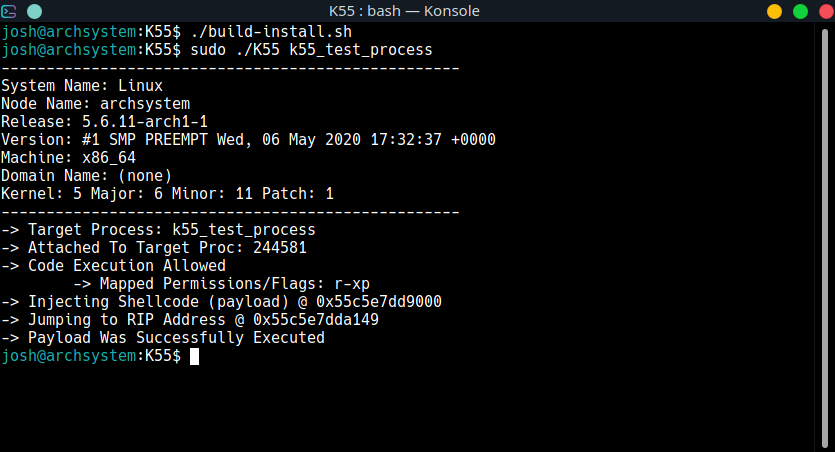
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 gmh5225/rust-mordor-rs
Rusty Hell's Gate / Halo's Gate / Tartarus' Gate / FreshyCalls / Syswhispers2 Library

 exploit-database/exploitdb-bin-sploits
exploitdb-bin-sploits // Exploit-Database's binary exploits (what was located in the /sploits directory)
 forrest-orr/wizardopium
Google Chrome Use After Free
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 forrest-orr/exploitdev
Various tools, PoCs and experiments related to my blog at https://www.forrest-orr.net/
 dump-guy/sc2pe
Simple dotnet Native AOT app that uses AsmResolver to convert shellcode to PE
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 pwnedshell/larascript
Laravel RCE exploit. CVE-2018-15133
 grisuno/blacksandbeacon
Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.
 prodigiousmind/cve-2023-41425
WonderCMS Authenticated RCE - CVE-2023-41425