

EATGuard
 connormcgarr/eatguard
Implementation of an export address table protection mitigation, like Export Address Filtering (EAF)
binary-exploitationdefensive-toolsshellcode
connormcgarr/eatguardImplementation of an export address table protection mitigation, like Export Address Filtering (EAF)
 wetw0rk/exploit-development
CVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
 secnn/springframework_cve-2022-22965_rce
SpringFramework 远程代码执行漏洞CVE-2022-22965
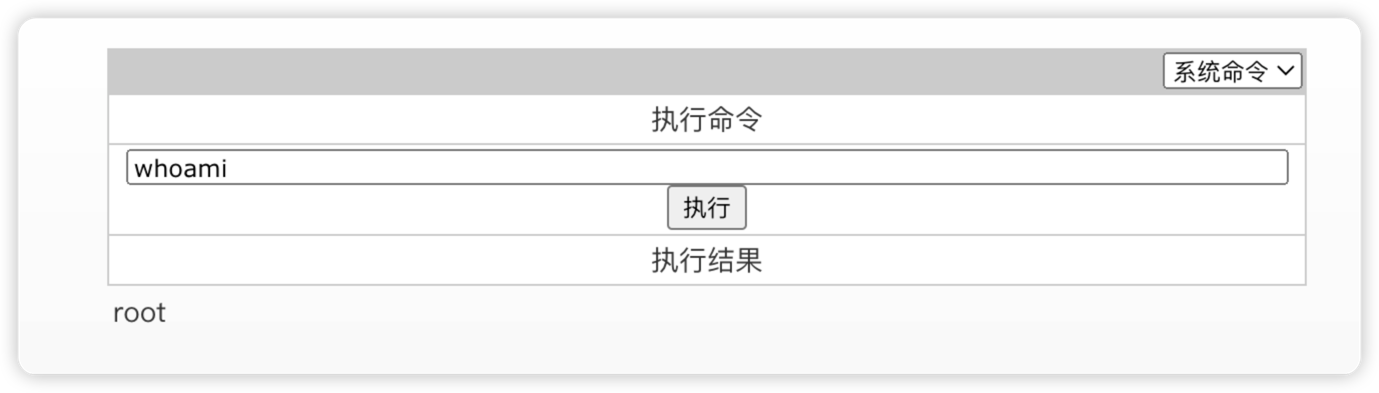 tangxiaofeng7/cve-2023-32315-openfire-bypass
rce
 forrest-orr/exploits
A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 ustayready/wnfexec
WNF Code Execution Library Using C#
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 n0qword/win32k-callback-detouring
Abusing the win32k.sys kernel callback mechanism for arbitrary code execution
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 buffer/pylibemu
A Libemu Cython wrapper
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems