

PINKPANTHER
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
binary-exploitationpayload-developmentpost-exploitation+2
515
winterknife/pinkpantherWindows x64 handcrafted token stealing kernel-mode shellcode
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 rashidkhanpathan/cve-2022-40471
RCE Exploit and Research
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…

 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
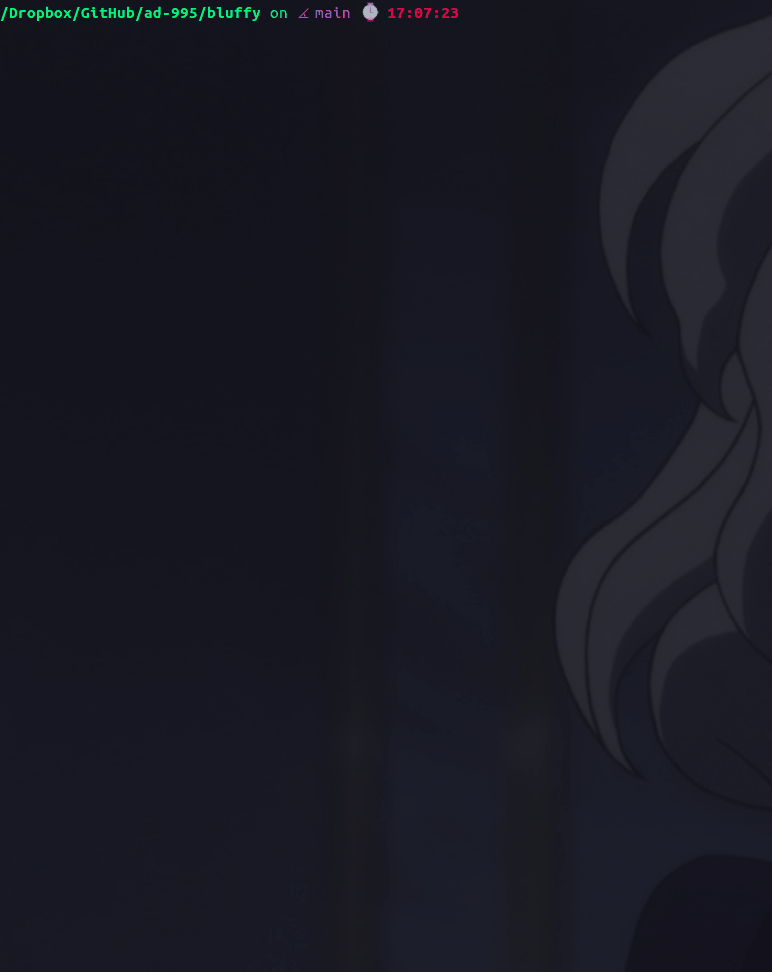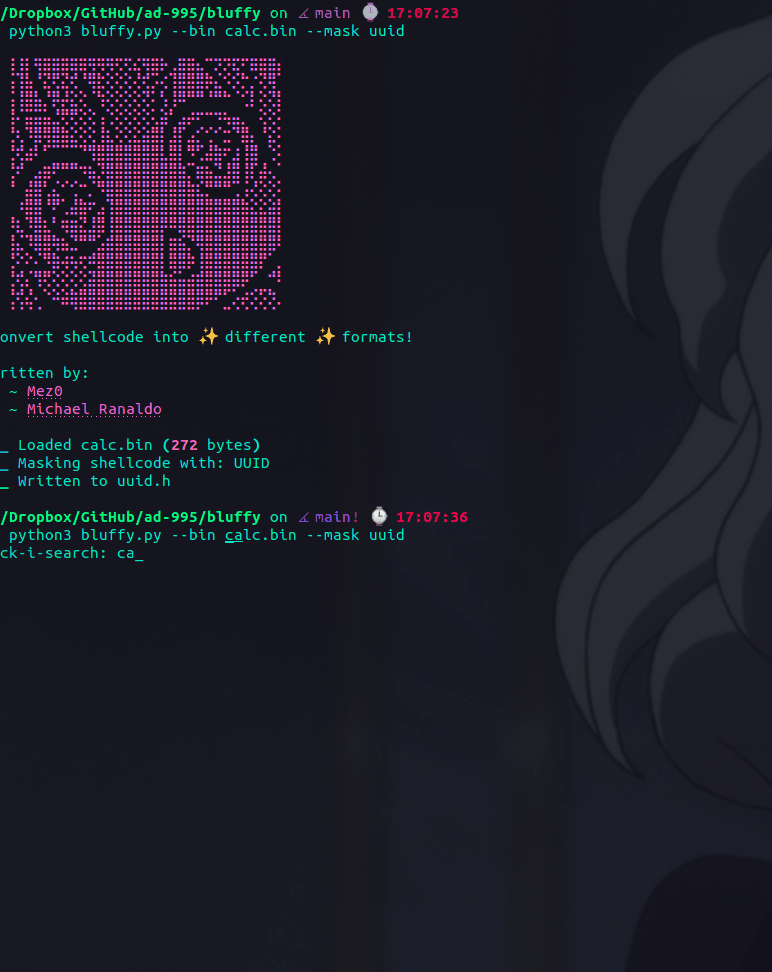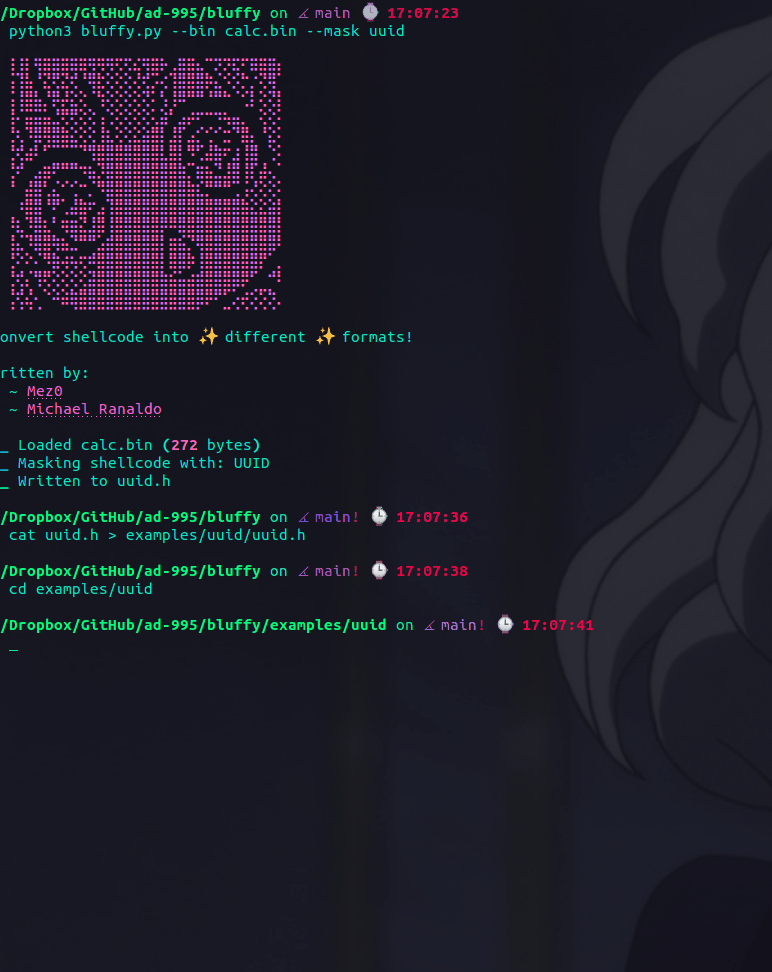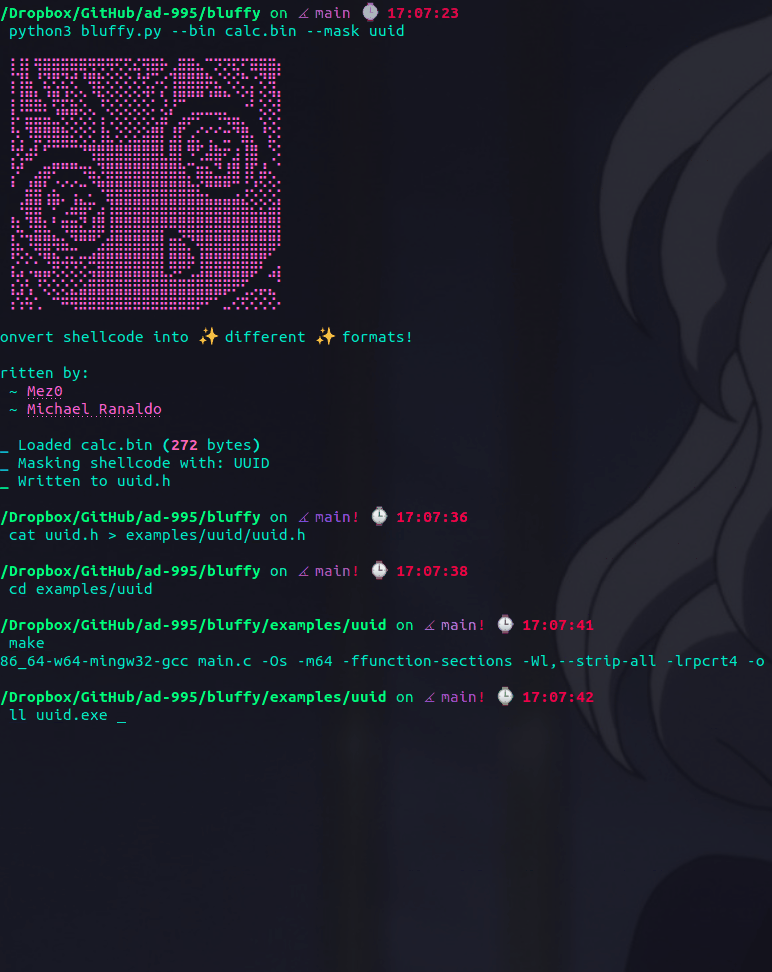 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 zimawhit3/bitmancer
Nim Library for Offensive Security Development