
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
39 results
MorphAES preview

MorphAES

GitHubcryptolok/morphaes

IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
binary-exploitationexploitationids-ips-evasion+4
325
4 years ago
hades preview

hades

GitHubf1zm0/hades

Go shellcode loader that combines multiple evasion techniques
ids-ips-evasionshellcodeshellcode-generation
3923 years ago
Christmas preview

Christmas

GitHubmaldev-academy/christmas

PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
adversarial-attackids-ips-evasionpayload-development+3
2572 years ago
Split preview

Split

GitHubkudaes/split

Apply a divide and conquer approach to bypass EDRs

adversarial-attackids-ips-evasionpayload-development+3
2882 years ago
Lastenzug preview

Lastenzug

GitHubcodewhitesec/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
command-and-controlids-ips-evasionpayload-development+3
2353 years ago
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
command-and-controlexploitationids-ips-evasion+6
2421 year ago
Bitmancer preview

Bitmancer

GitHubzimawhit3/bitmancer

Nim Library for Offensive Security Development
binary-analysisids-ips-evasionpayload-development+4
2003 years ago
ExecIT preview

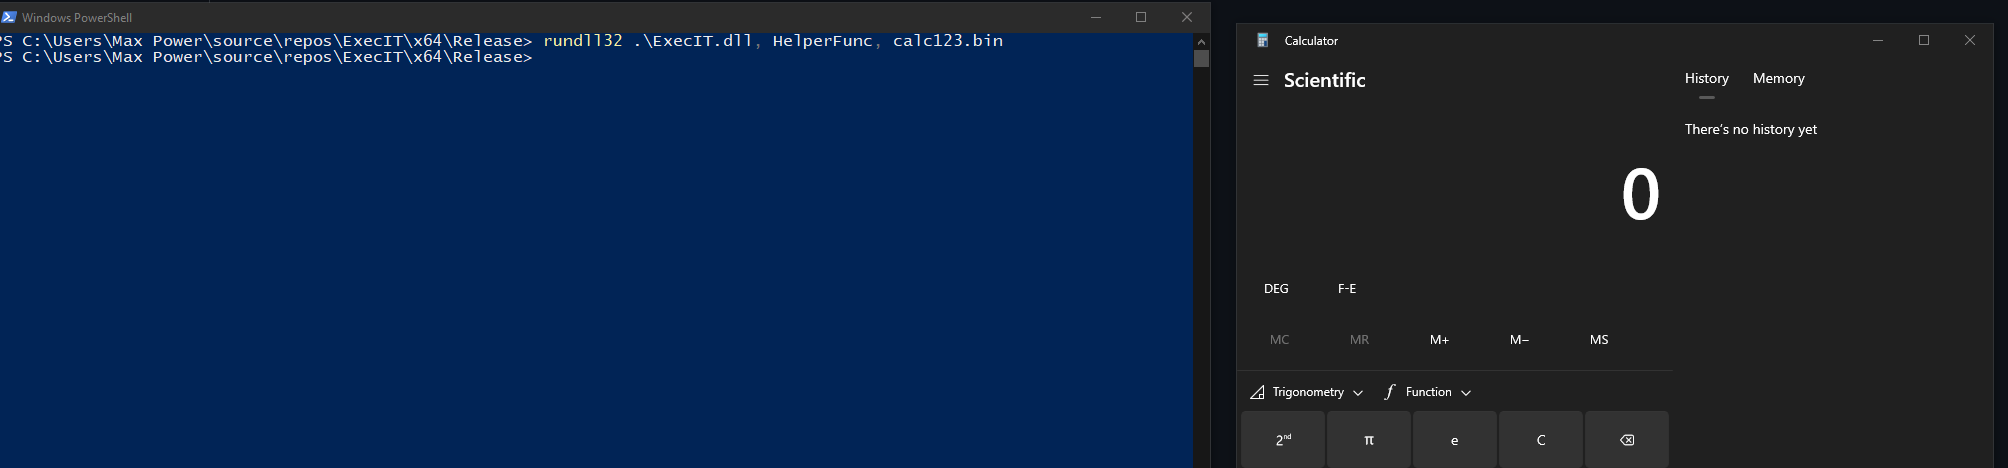
ExecIT

GitHubflorylsk/execit

Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2282 years ago
BOF_ExecuteAssembly preview

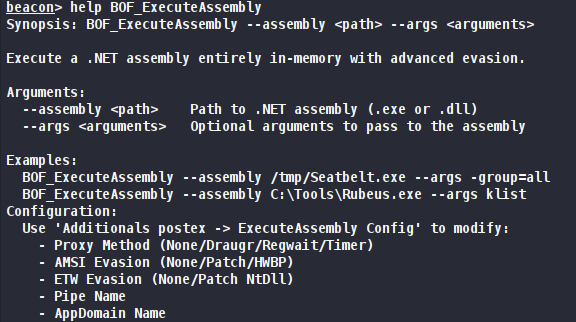
BOF_ExecuteAssembly

GitHubntdallas/bof_executeassembly

Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.

binary-exploitationcommand-and-controlids-ips-evasion+4
1989 months ago
ntqueueapcthreadex-ntdll-gadget-injection preview

ntqueueapcthreadex-ntdll-gadget-injection

GitHublloydlabs/ntqueueapcthreadex-ntdll-gadget-injection

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…

adversarial-attackids-ips-evasionpayload-development+3
2663 years ago
Percino preview

Percino

GitHubtunnelgre/percino

Evasive Golang Loader

adversarial-attackcommand-and-controlids-ips-evasion+4
1382 years ago
SharpWhispers preview

SharpWhispers

GitHubsecforce/sharpwhispers

C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
ids-ips-evasionpayload-developmentpost-exploitation+2
1123 years ago
Bypass_AV preview

Bypass_AV

GitHubhkl1x/bypass_av

Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
ids-ips-evasionpayload-developmentpayload-generation+2
10811 months ago
volana preview

volana

GitHubariary/volana

🌒 Shell command obfuscation to avoid detection systems
command-and-controlexploitationids-ips-evasion+3
1203 years ago
nimvoke preview

nimvoke

GitHubnbaertsch/nimvoke

Indirect syscalls + DInvoke made simple.
ids-ips-evasionpayload-developmentpost-exploitation+2
951 year ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver

adversarial-attackids-ips-evasionpayload-development+3
542 years ago
Lastenzug preview

Lastenzug

GitHubps1337/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
ids-ips-evasionpayload-developmentpost-exploitation+3
264 years ago
CVE-2024-0311 preview

CVE-2024-0311

GitHubcalligraf0/cve-2024-0311

Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…

binary-exploitationexploitationids-ips-evasion+4
91 year ago
Previous123Next