

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
70 results
asminject preview

asminject

GitHubbishopfox/asminject

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
container-escapepayload-developmentpenetration-testing+2
149
3 years ago
SdoKeyCrypt-sys-local-privilege-elevation preview

SdoKeyCrypt-sys-local-privilege-elevation

GitHubhypersine/sdokeycrypt-sys-local-privilege-elevation

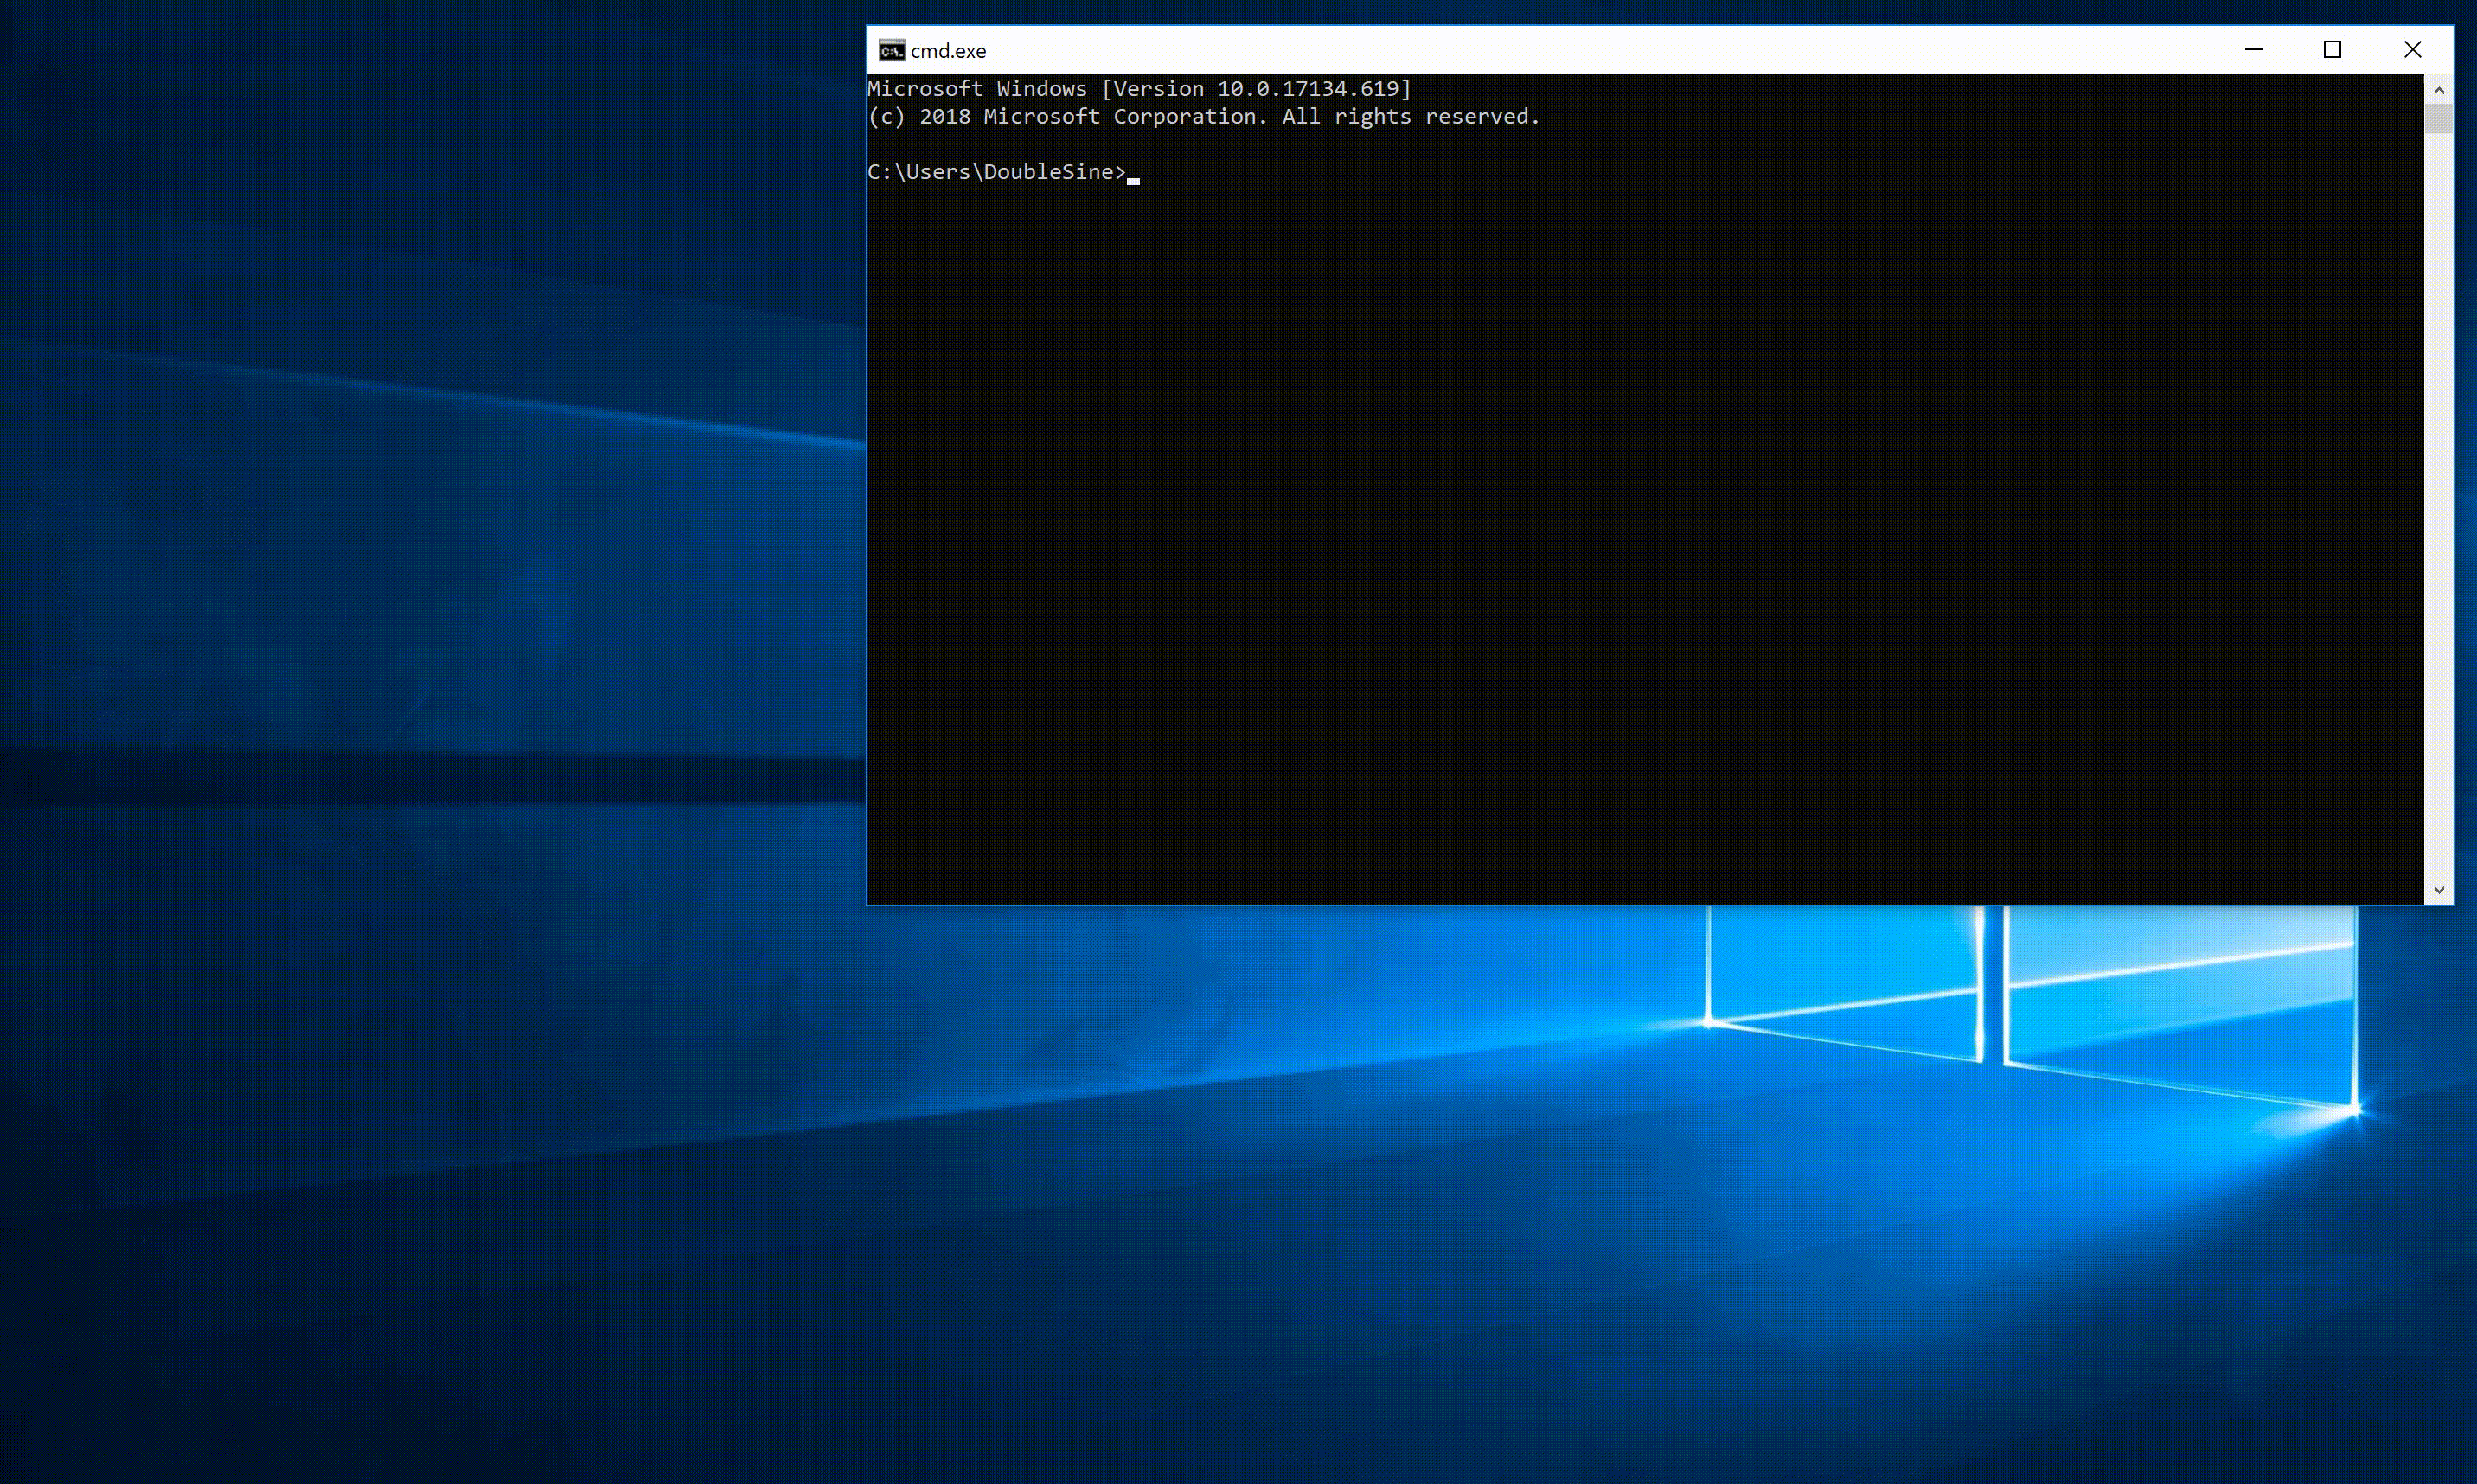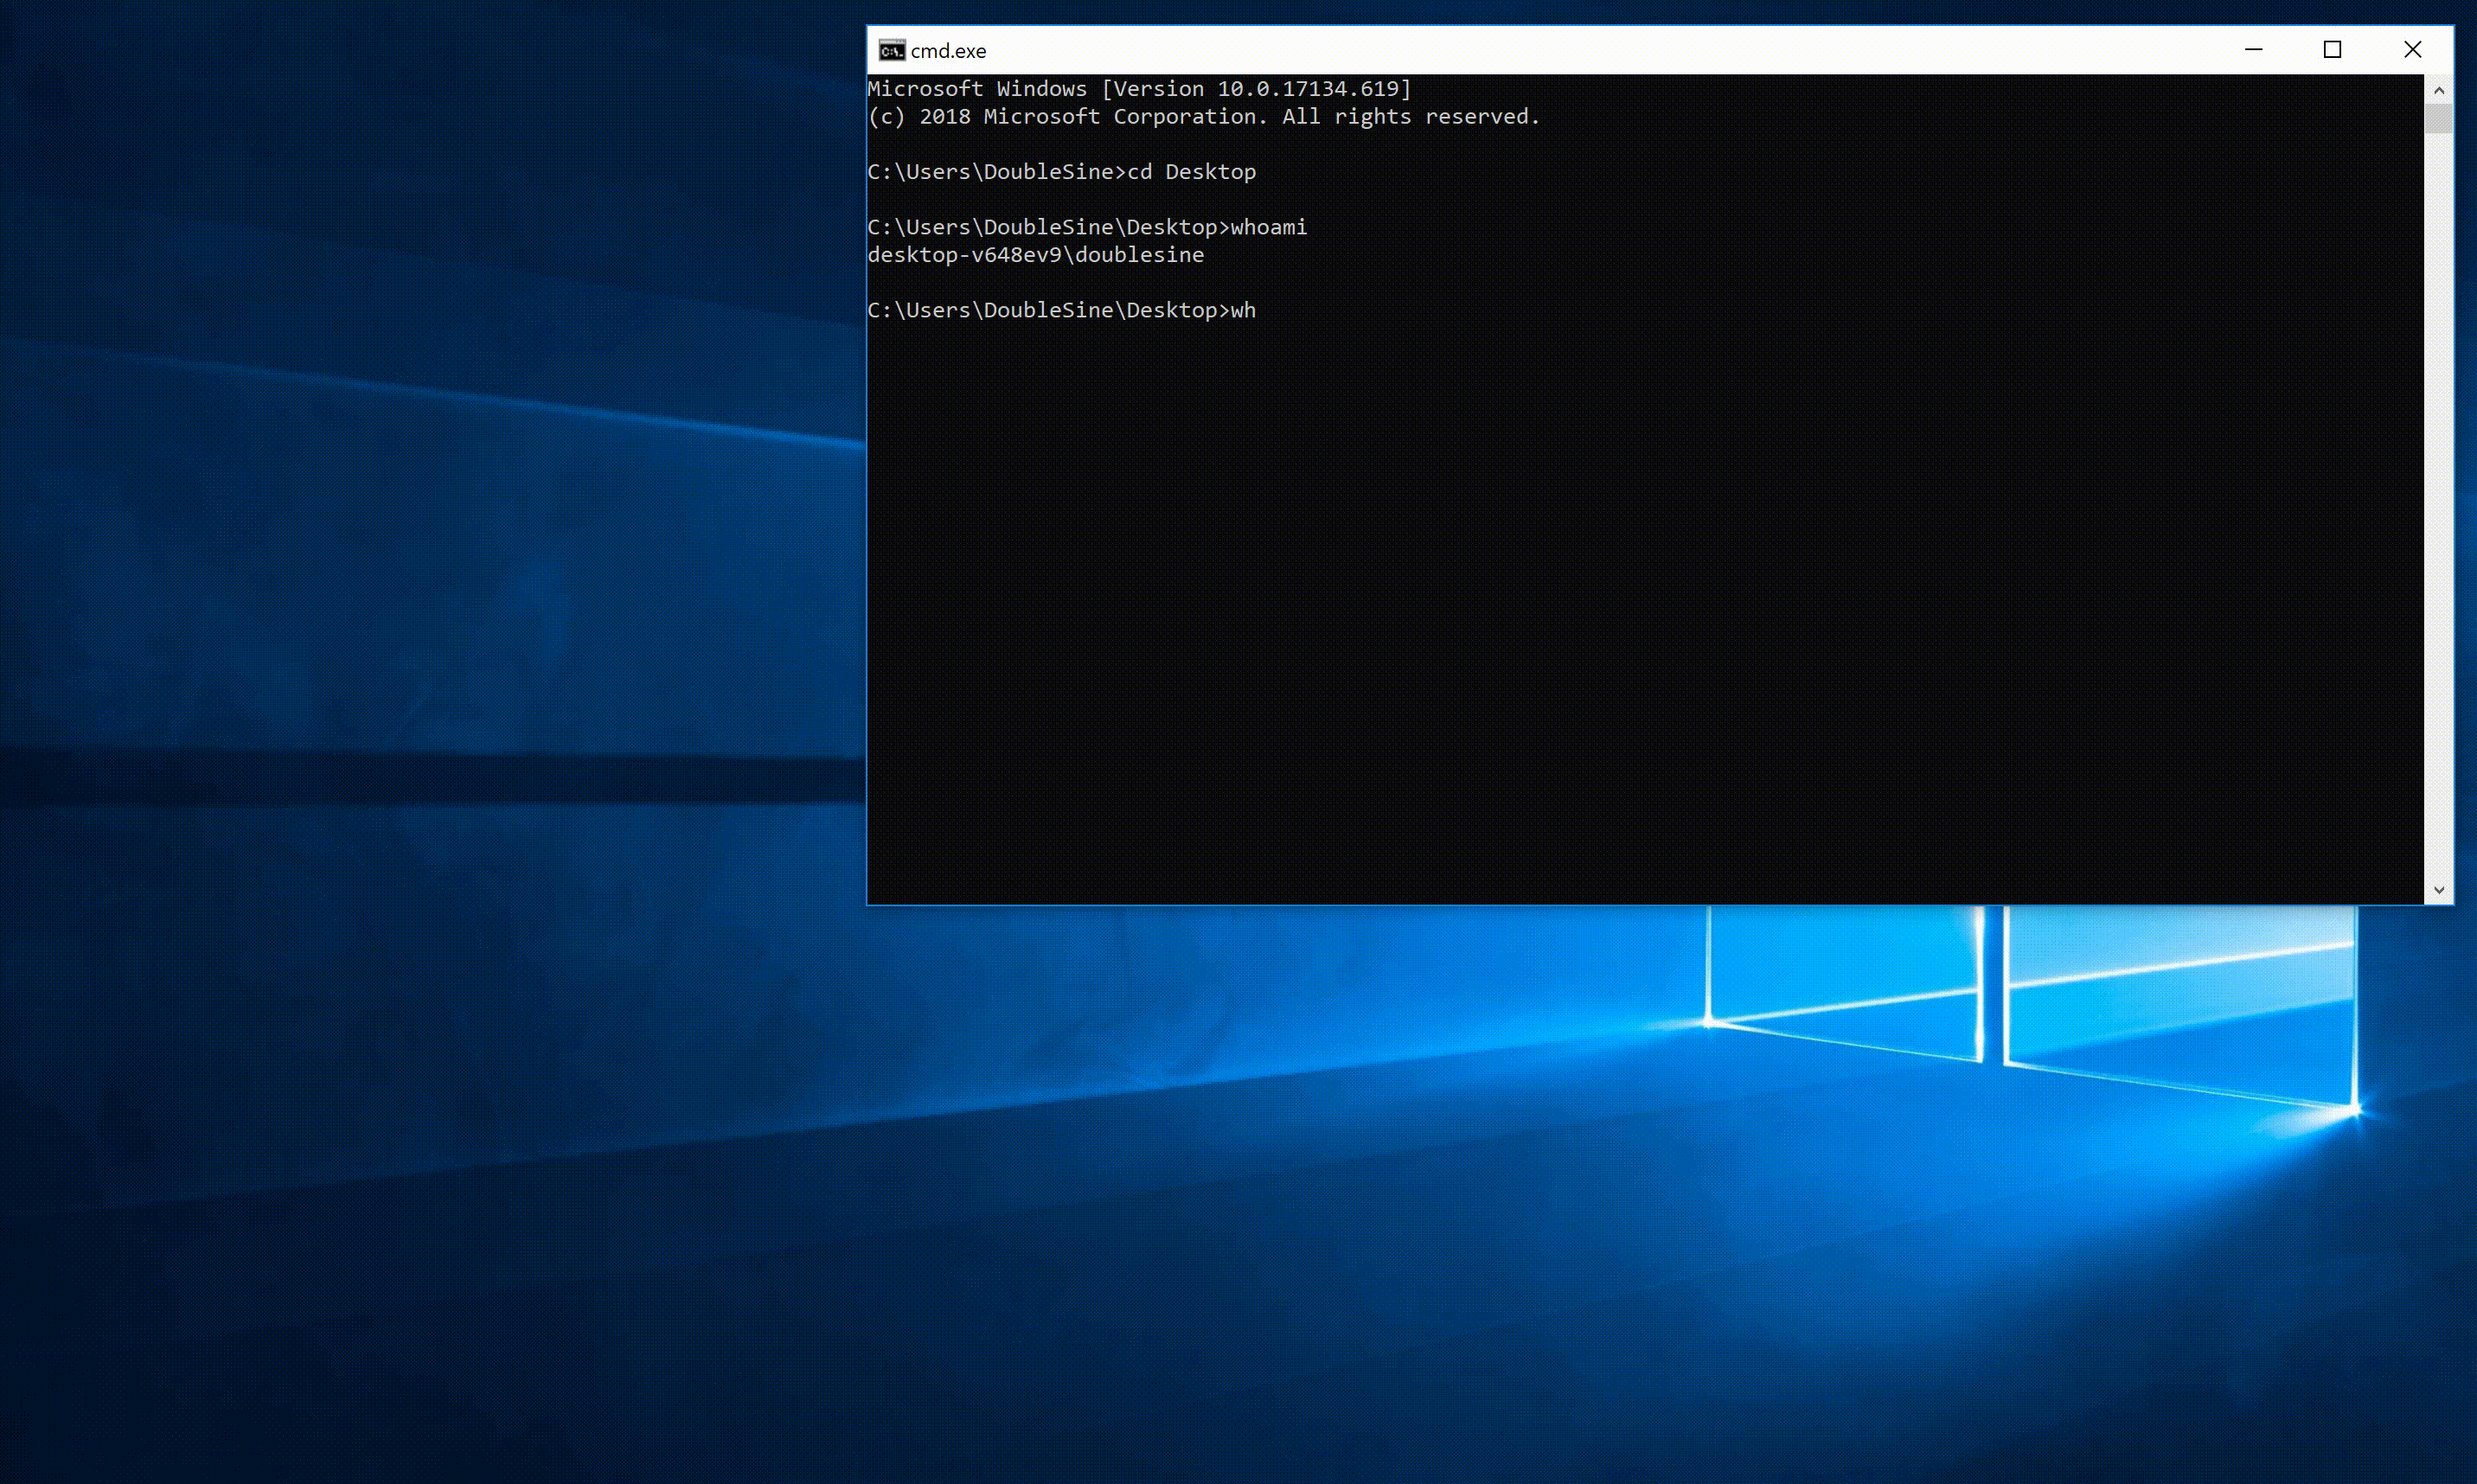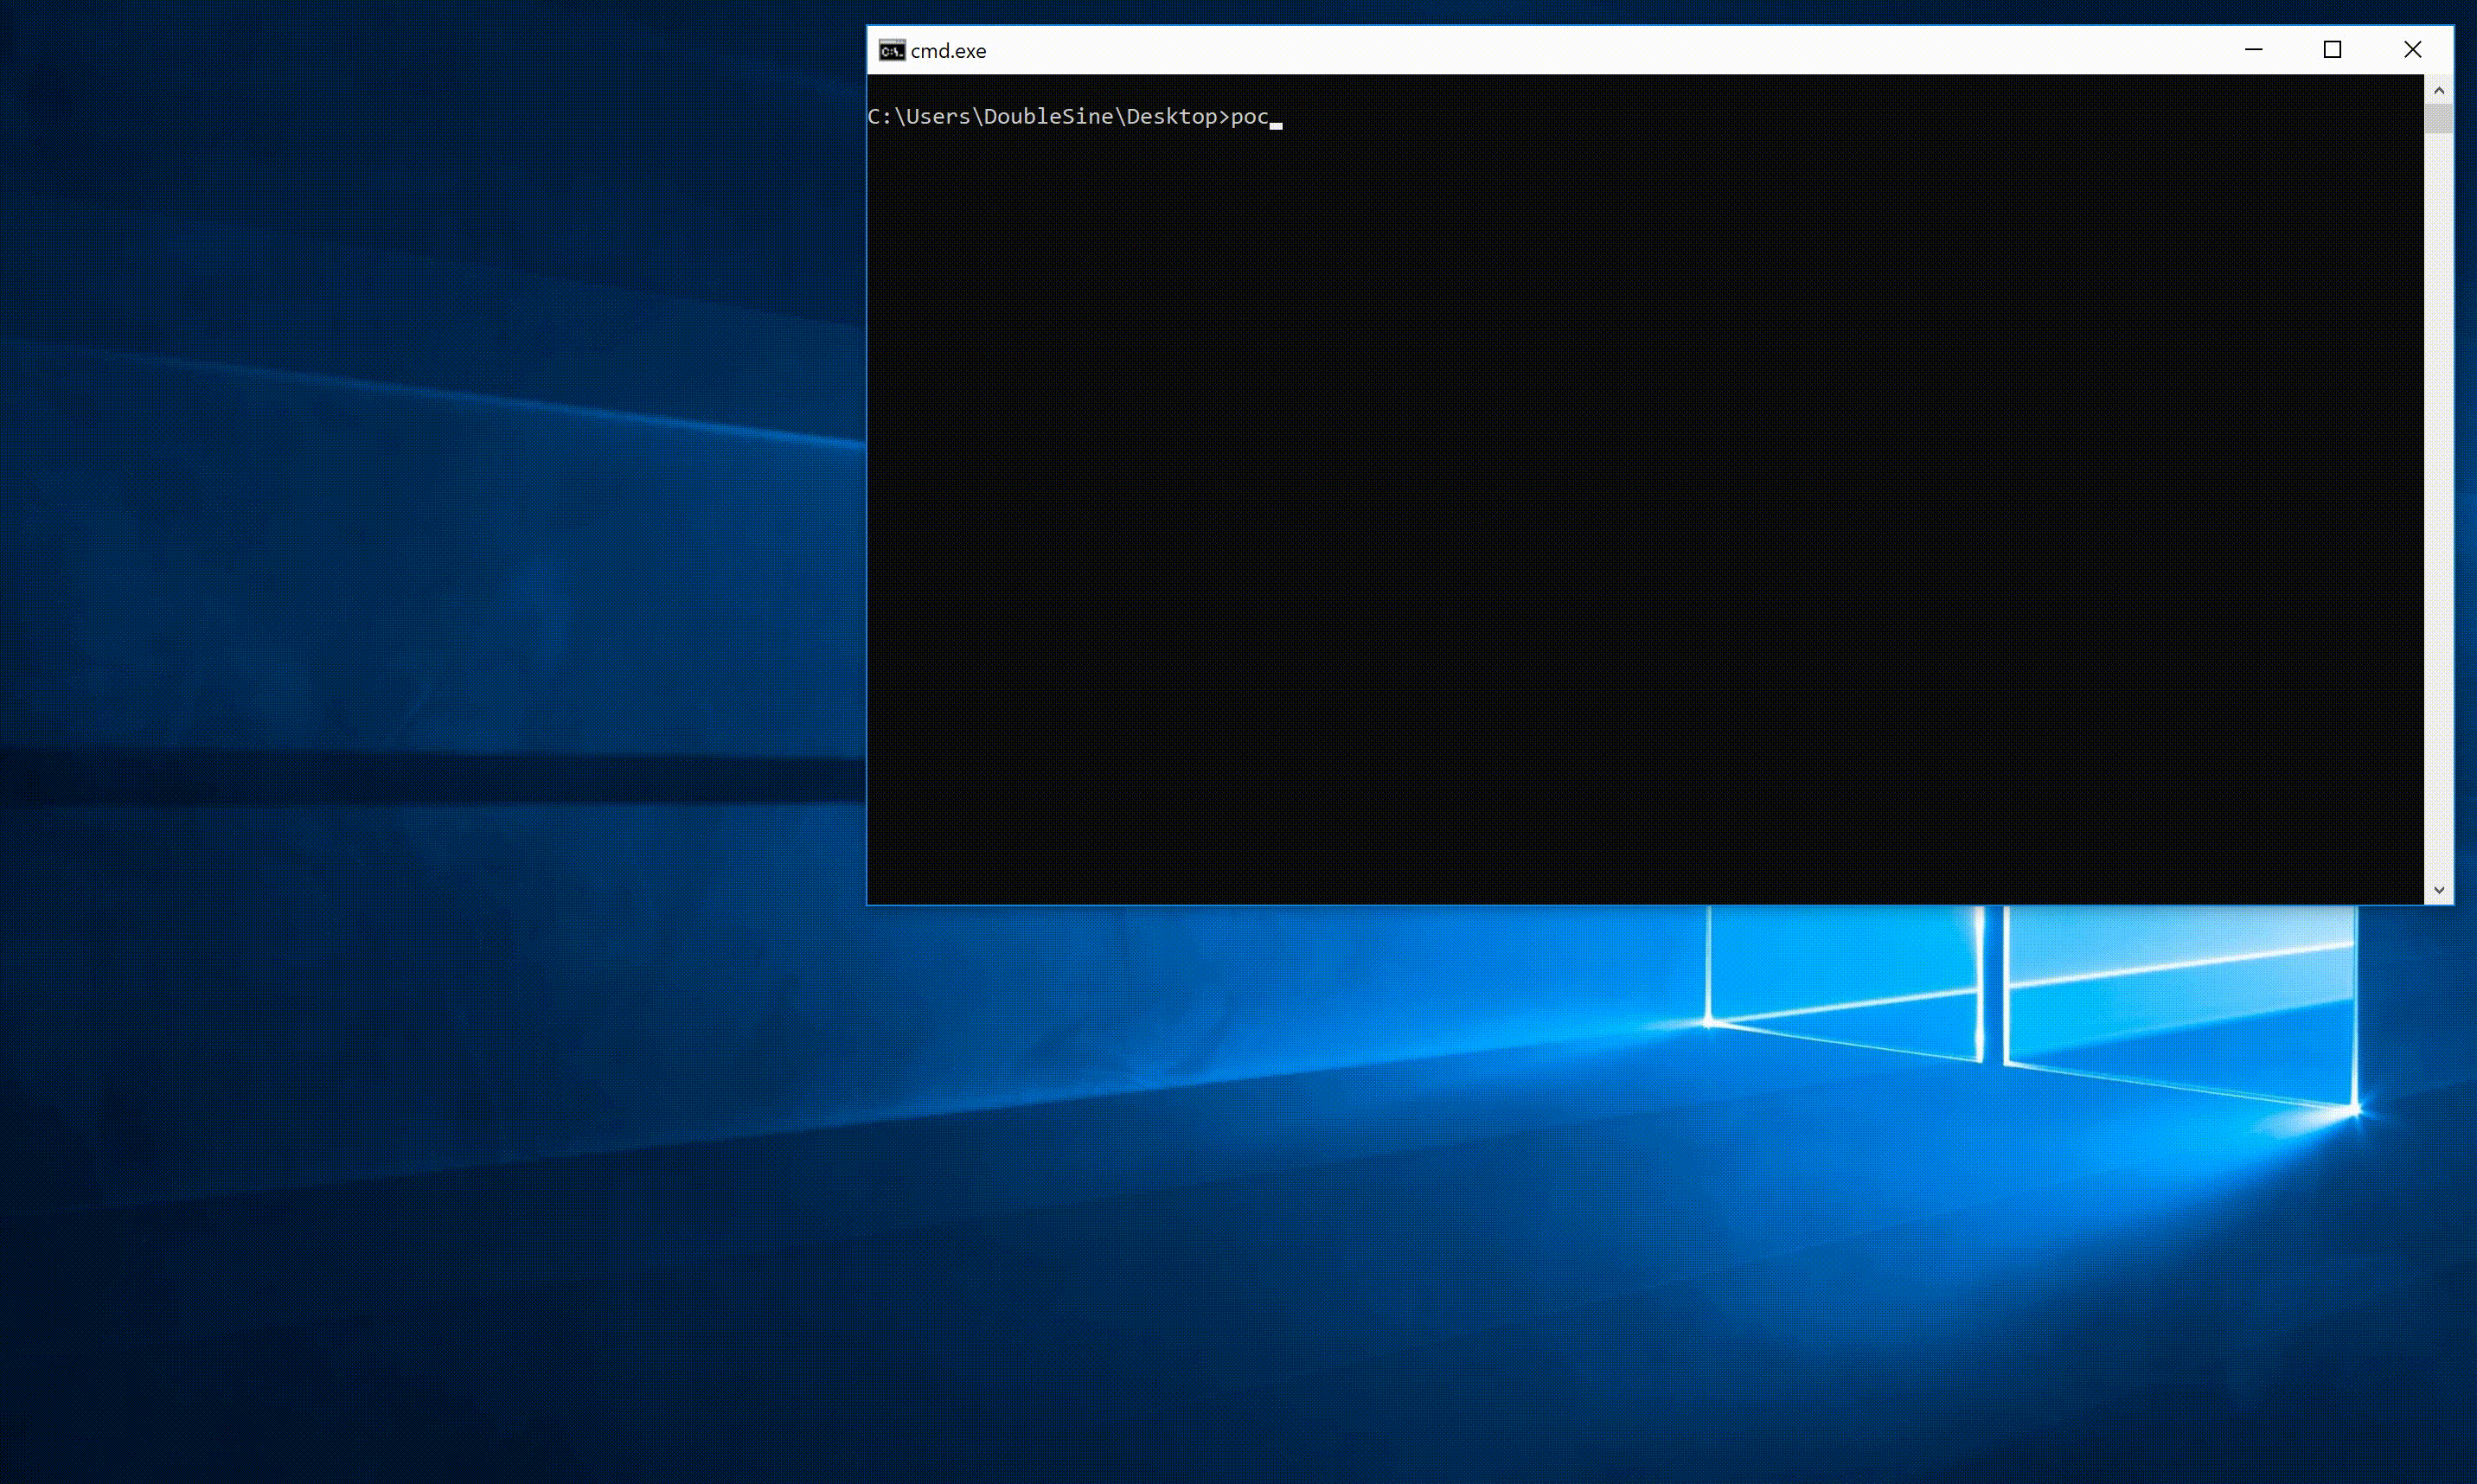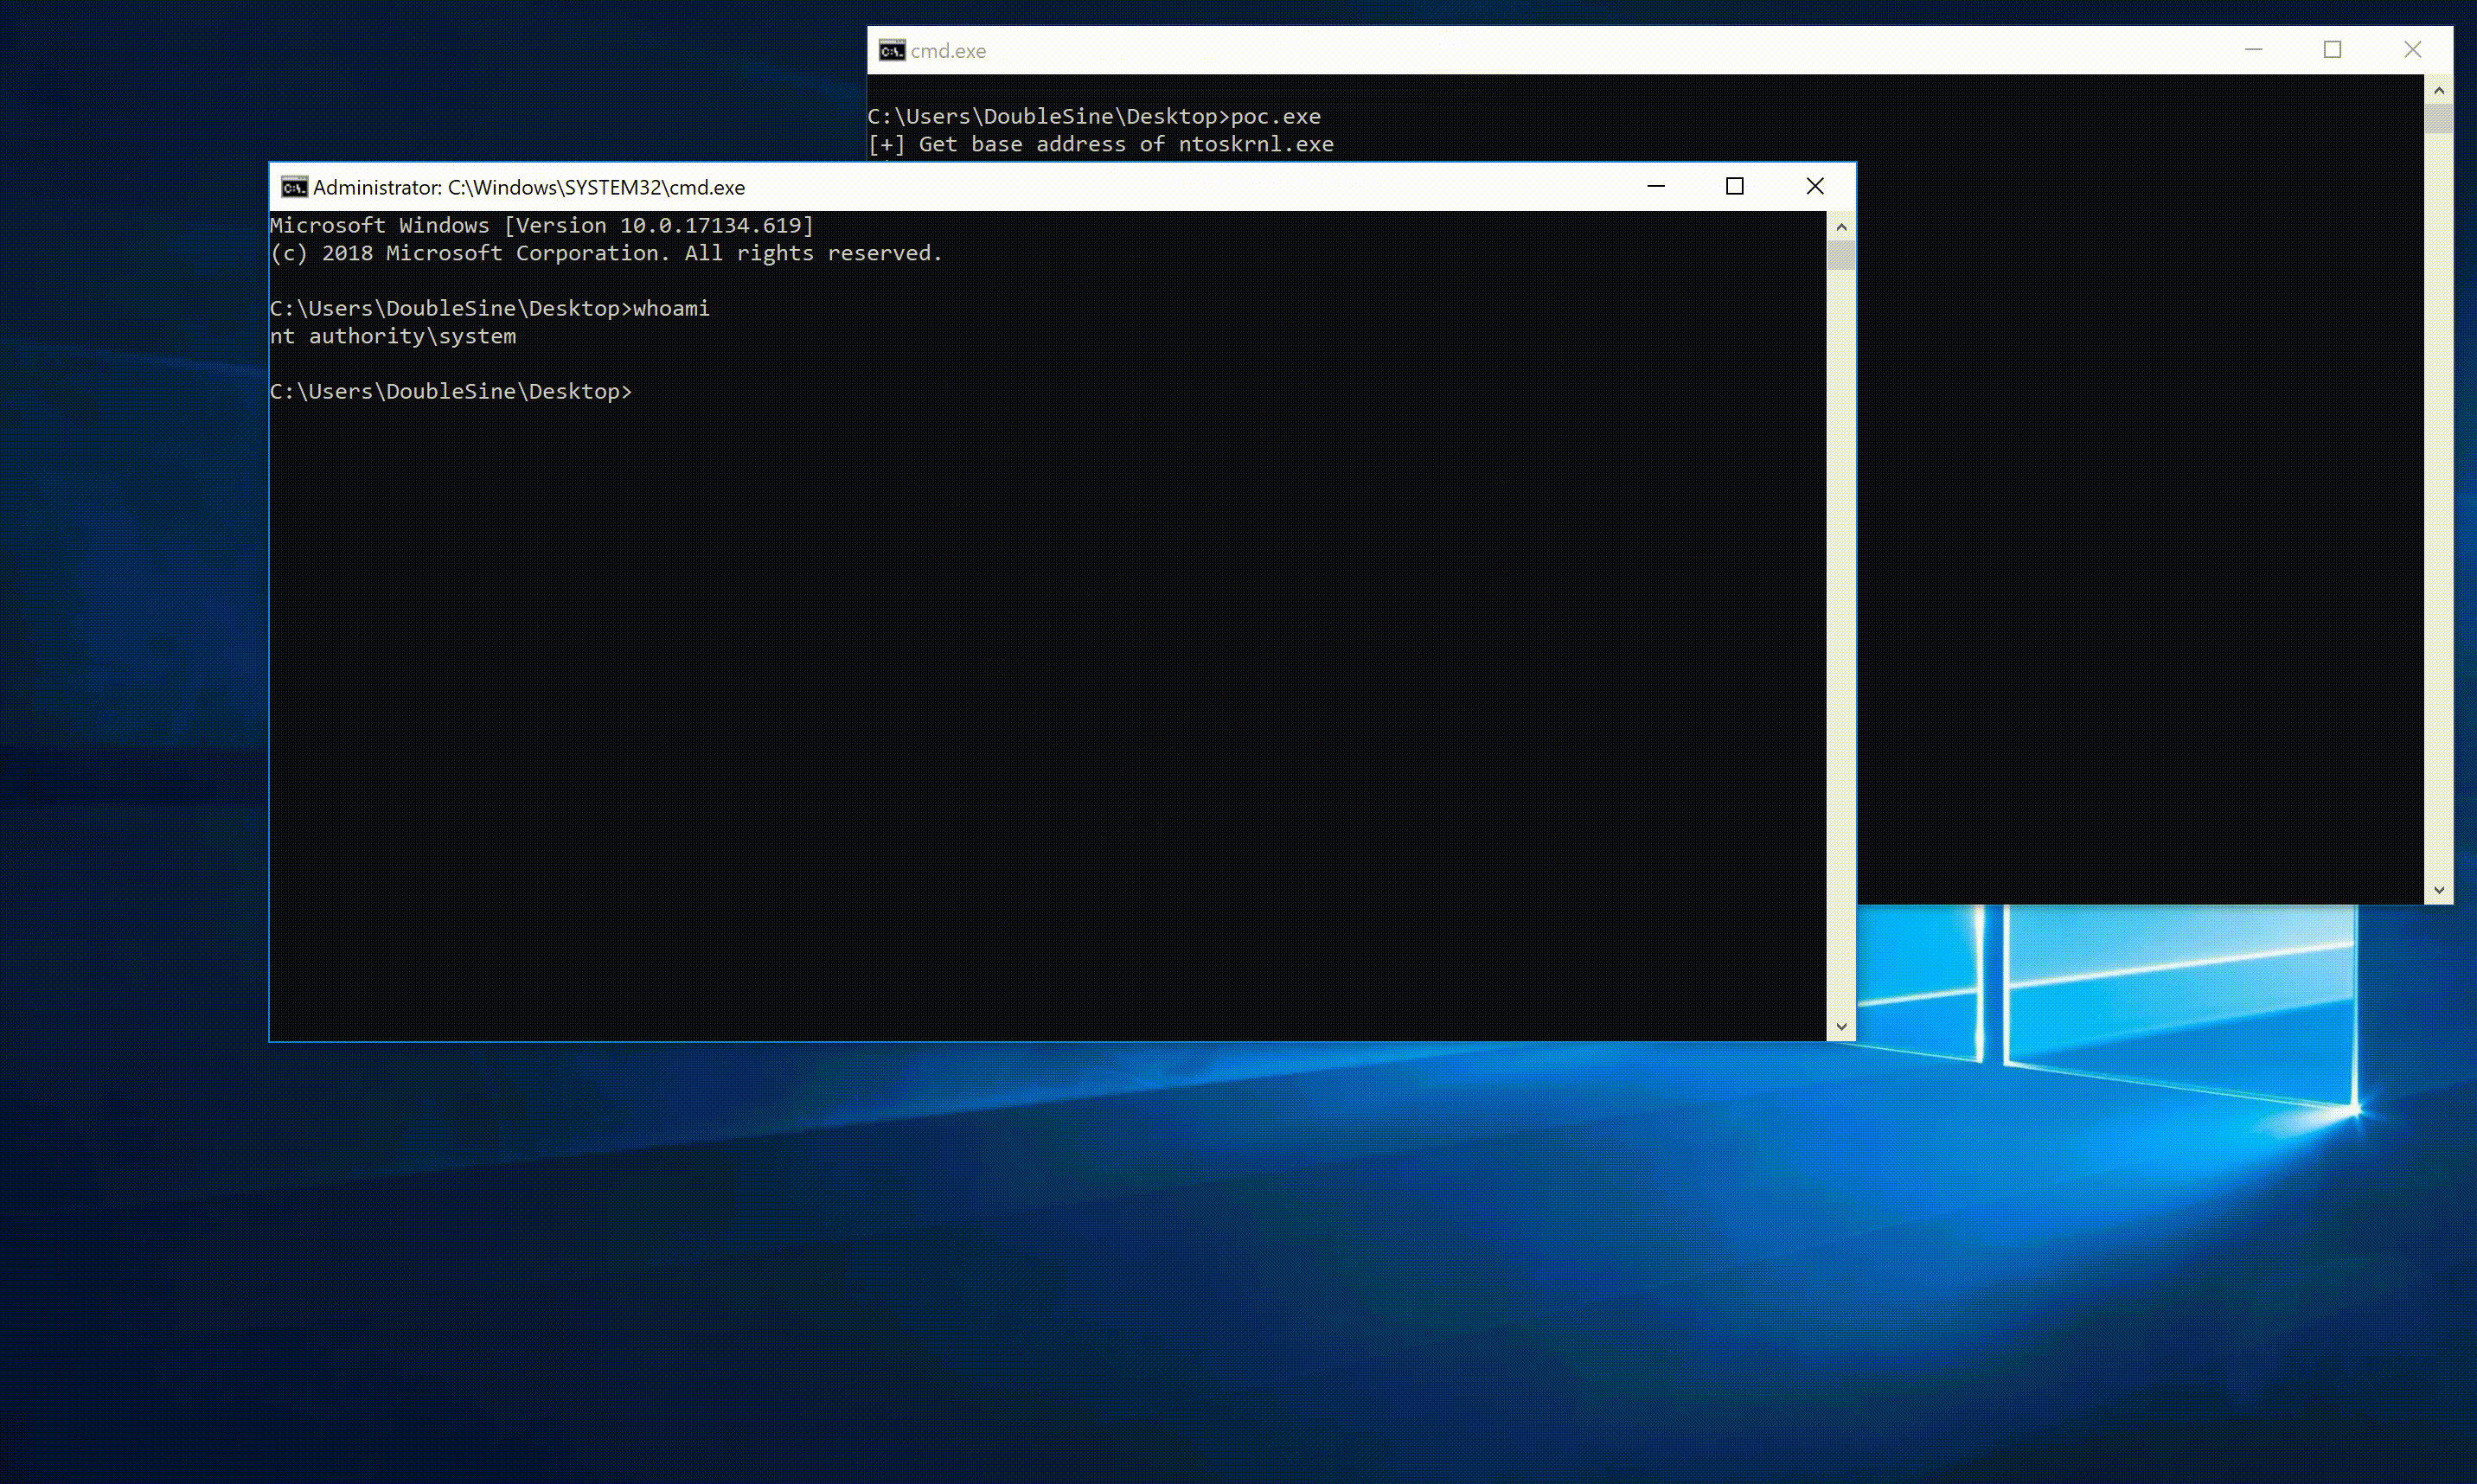
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
binary-exploitationexploitationprivilege-escalation+2
847 years ago
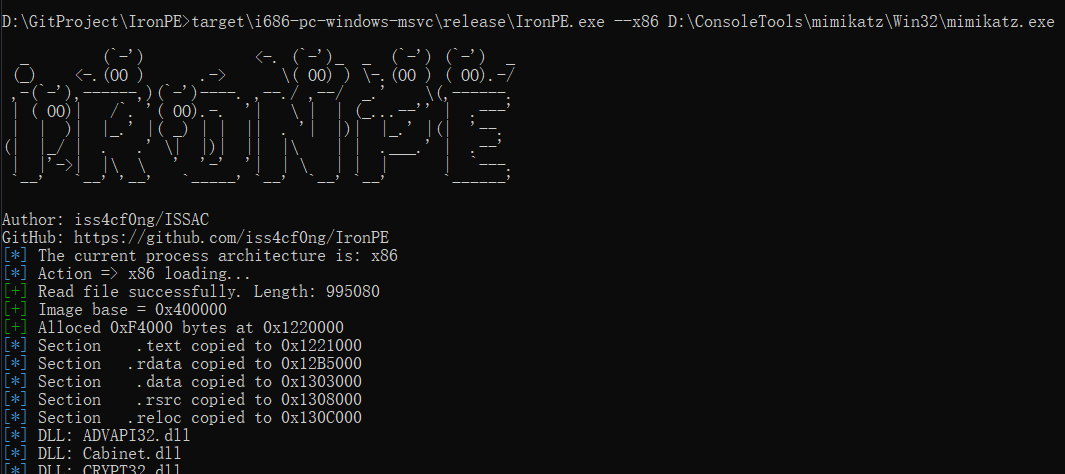
IronPE preview

IronPE

GitHubiss4cf0ng/ironpe

Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
binary-analysisbinary-exploitationeducation+5
1267 months ago
ManualRsrcDataFetching preview

ManualRsrcDataFetching

GitHubnul0x4c/manualrsrcdatafetching

Get your data from the resource section manually, with no need for windows apis
binary-analysispayload-developmentred-teaming+1
661 year ago
SHGenOb preview

SHGenOb

GitHuboldboy21/shgenob

Python based tool for generating Shellcode from PIC C

binary-analysiseducationencryption-decryption-tools+5
4311 months ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
PhantomEvasion preview

PhantomEvasion

GitHubesskumar/phantomevasion

Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…

exploit-frameworkspayload-generationpenetration-testing+5
176 years ago
bin2shell preview

bin2shell

GitHubtouhidshaikh/bin2shell

bin2shell is very small utils for extract shell code from the binary file
exploitationpayload-developmentpayload-generation+3
129 years ago
CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter preview

CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter

GitHubsneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
binary-exploitationexploitationmemory-forensics+3
51 month ago
Analysis-for-stage1-shellcode-loader-from-hacking- preview

Analysis-for-stage1-shellcode-loader-from-hacking-

GitHubspiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-

Analysis for stage1 shellcode loader from hacking

binary-analysiseducationmalware-analysis+2
31 year ago
LazZzy_Dump preview

LazZzy_Dump

GitHubtrustedsec/lazzzy_dump

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
binary-analysiscode-analysisdigital-forensics+6
11 month ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubcharlyrr/cve-2025-5548

Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…

binary-exploitationdebuggerseducation+7
7 months ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
metasploit-framework preview
Archived

metasploit-framework

GitHubmarkoarmitage/metasploit-framework

app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…

command-and-controlexploitationexploit-frameworks+8
56 years ago
flare-ida preview
Archived

flare-ida

GitHubmandiant/flare-ida

IDA Pro utilities from FLARE team
binary-analysisdebuggersdynamic-analysis-sandboxing+3
2.4k1 year ago
bluekeep_CVE-2019-0708_poc_to_exploit preview
Archived

bluekeep_CVE-2019-0708_poc_to_exploit

GitHubalgo7/bluekeep_cve-2019-0708_poc_to_exploit

An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits

exploitationpayload-developmentpenetration-testing+3
3425 years ago
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
command-and-controldata-exfiltrationexploit-frameworks+10
5.6k5 days ago
c0ntextomy preview

c0ntextomy

GitHubc0ntextomy/c0ntextomy

CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…

data-exfiltrationdebuggersexploitation+9
736 years ago
Previous1234Next