
Bypass_AV
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
ids-ips-evasionpayload-developmentpayload-generation+2
107
hkl1x/bypass_avEvades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
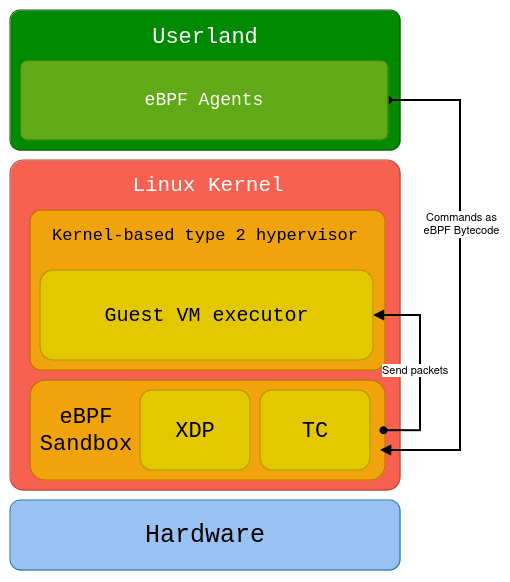 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
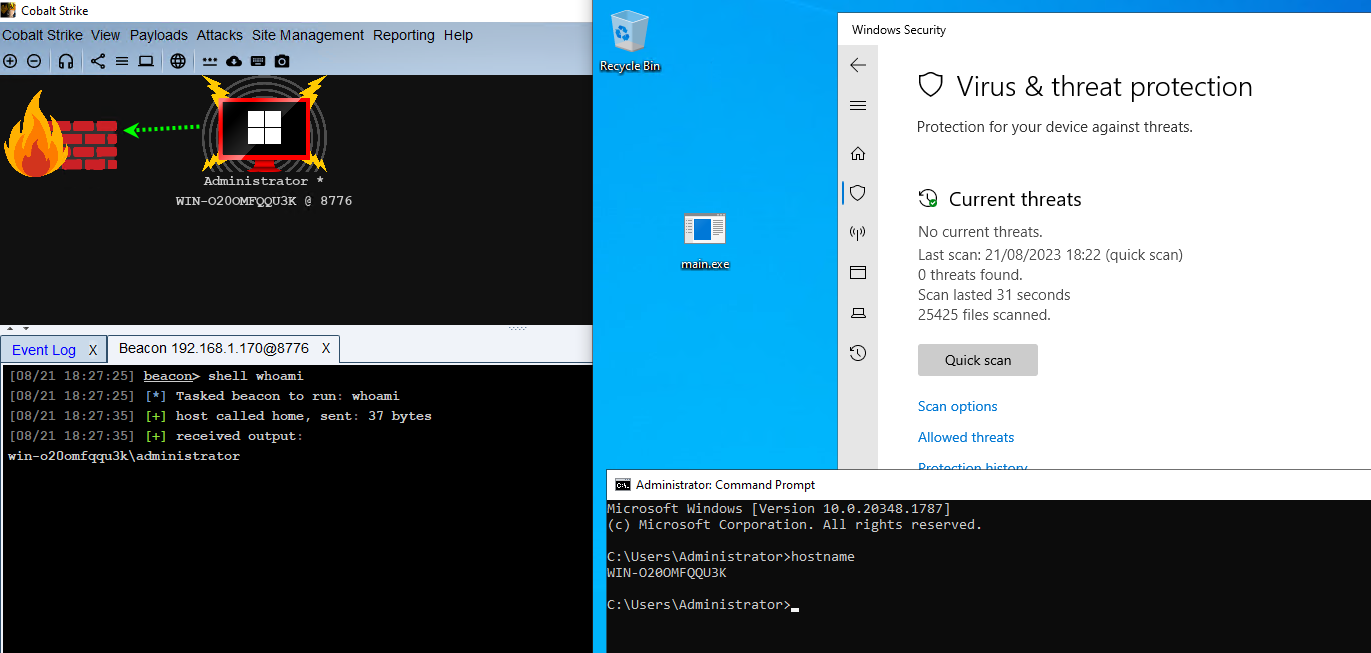
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features