

OffensiveDLR
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
code-analysiscommand-and-controldynamic-code-analysis+9
525
byt3bl33d3r/offensivedlrToolbox containing research notes & PoC code for weaponizing .NET's DLR
 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 barriuso/smbghost_automateexploitation
SMBGhost (CVE-2020-0796) Automate Exploitation and Detection
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
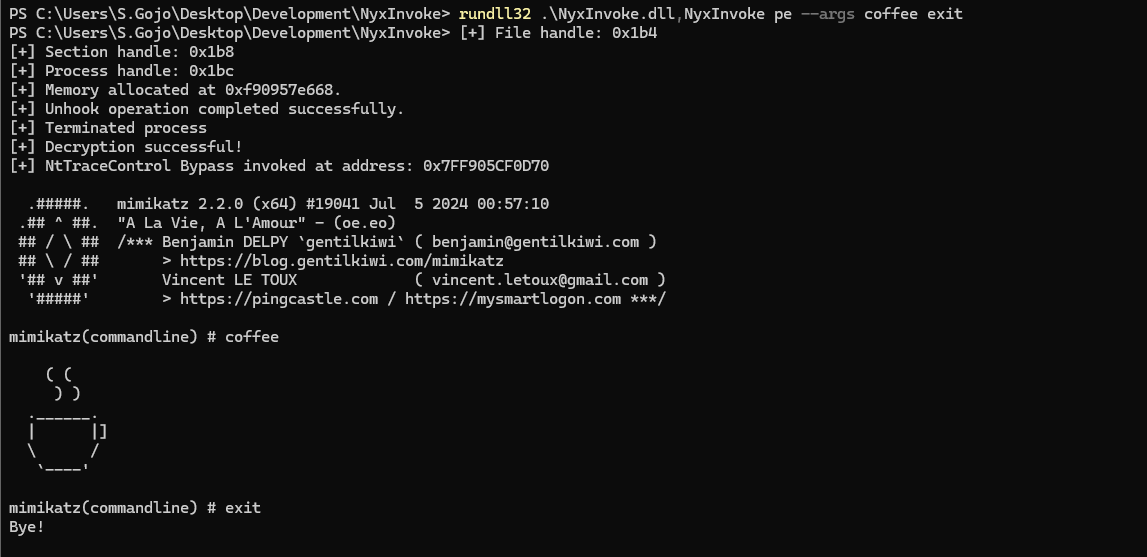 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
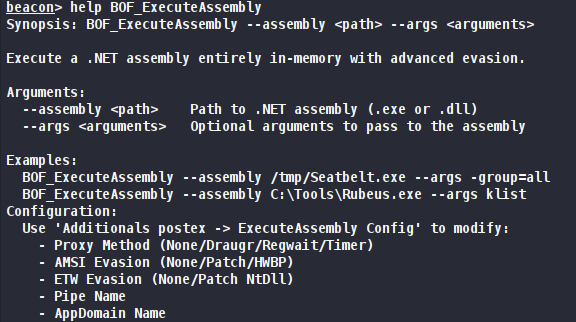 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
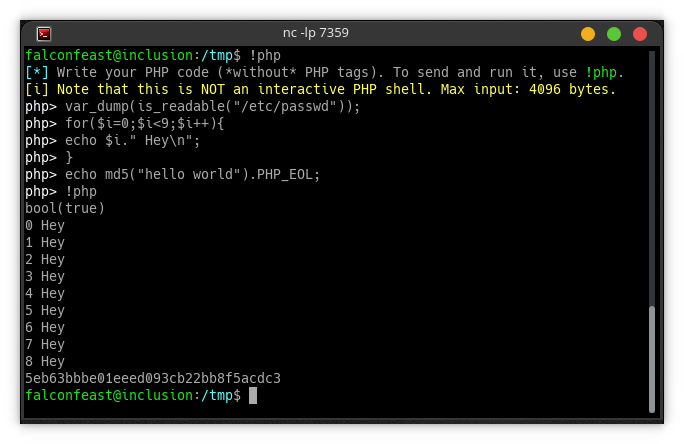 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 doggycheng/cnvd-2020-10487
CVE-2020-1938 / CNVD-2020-1048 Detection Tools
 otsmane-ahmed/cve-2025-2620-poc
Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…
 im-hanzou/jbwper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2022-4061 - JobBoardWP < 1.2.2 - Unauthenticated Arbitrary File Upload
 gelukcrab/react-server-components-rce
React Server Components 远程代码执行漏洞(CVE-2025-55182)
 madfxr/cve-2024-26581-checker
[CVE-2024-26581] Vulnerability Checker for BGN Internal