

SLAE
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
binary-exploitationcryptographyeducation+5
kkirsche/slaeSecurityTube Linux Assembly Expert x86 Exam
 brunopujos/cve-2011-1237
POC for exploit of CVE-2011-1237
 gartonchan/redis-cve-2025-62507
Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 kaleth4/cve-2025-60751
Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…
 zer0matt/cve-2025-60751
PoC of CVE-2025-60751
 benmevic/cve-2025-22457
Altay takımı haftalık sunumu için yaptığım cve-2025-22457 zafiyeti demo uygulaması
 tematemaru/cve-2026-31431-simple-test
Educational proof-of-concept demonstrating CVE-2026-31431 with a vulnerable target application, demonstration payload, and shellcode extraction…
 themalwareguardian/cve-2003-0264
Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.
 chicken3962/cve-2025-3500-poc
Educational lab environment for researching CVE-2025-3500, an integer overflow privilege escalation exploit in Avast Antivirus 25.1.981.6 on Windows,…
 themalwareguardian/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.
 themalwareguardian/cve-2007-1567
Classic stack-based buffer overflow in War FTP Daemon 1.65 demonstrating old-school remote code execution through malformed FTP commands.
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
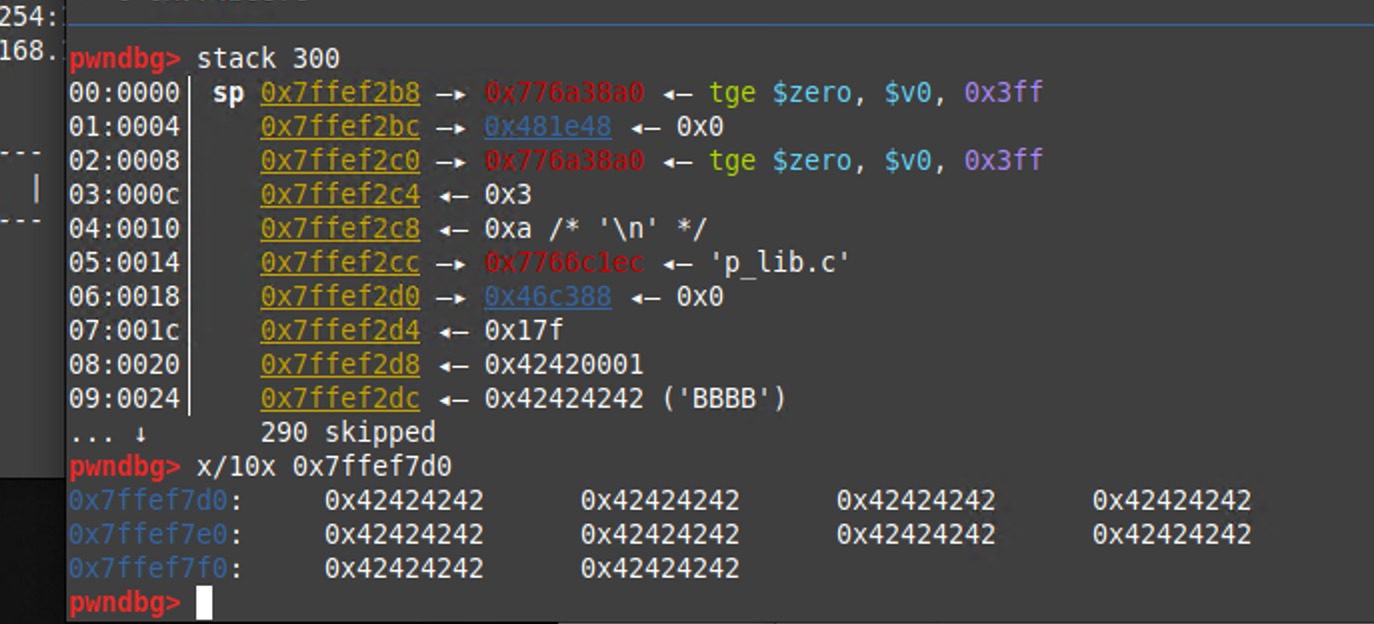 laskdjlaskdj12/cve-2024-29671-poc
This is POC of CVE-2024-29671
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…