redpill
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
defensive-toolsinformation-gatheringlateral-movement+6
r00t-3xp10it/redpillAssist reverse tcp shells in post-exploration tasks
 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
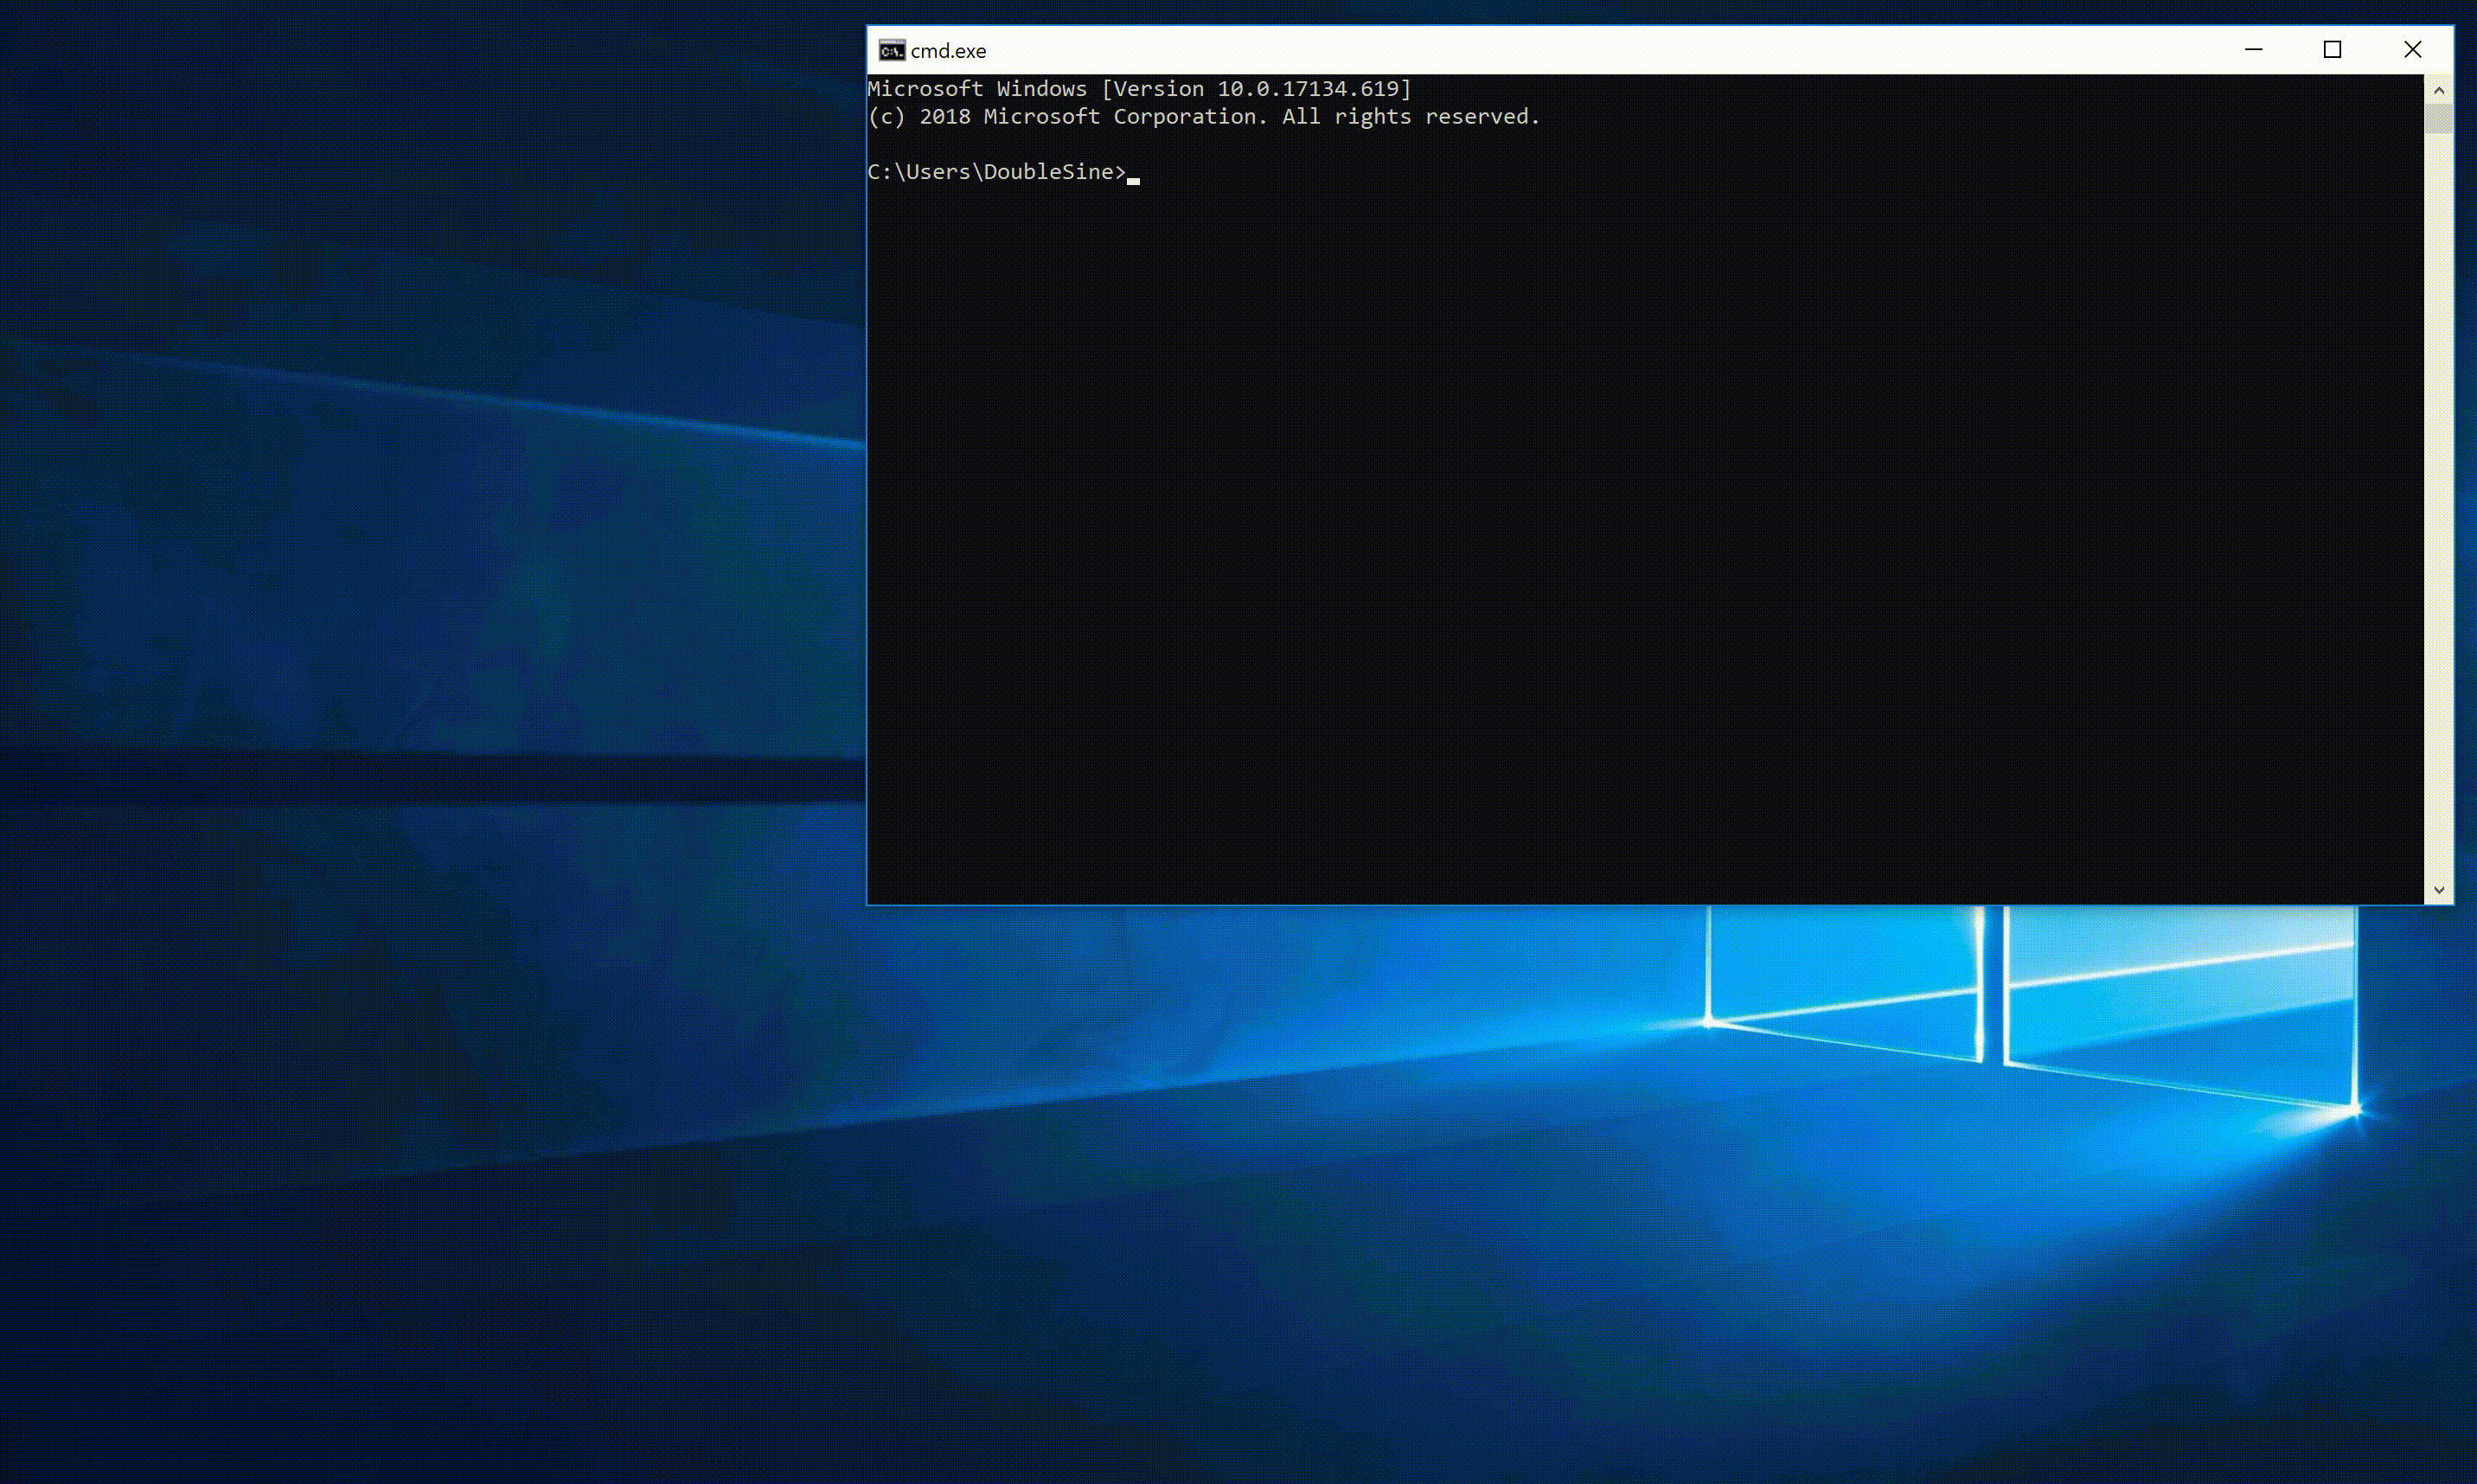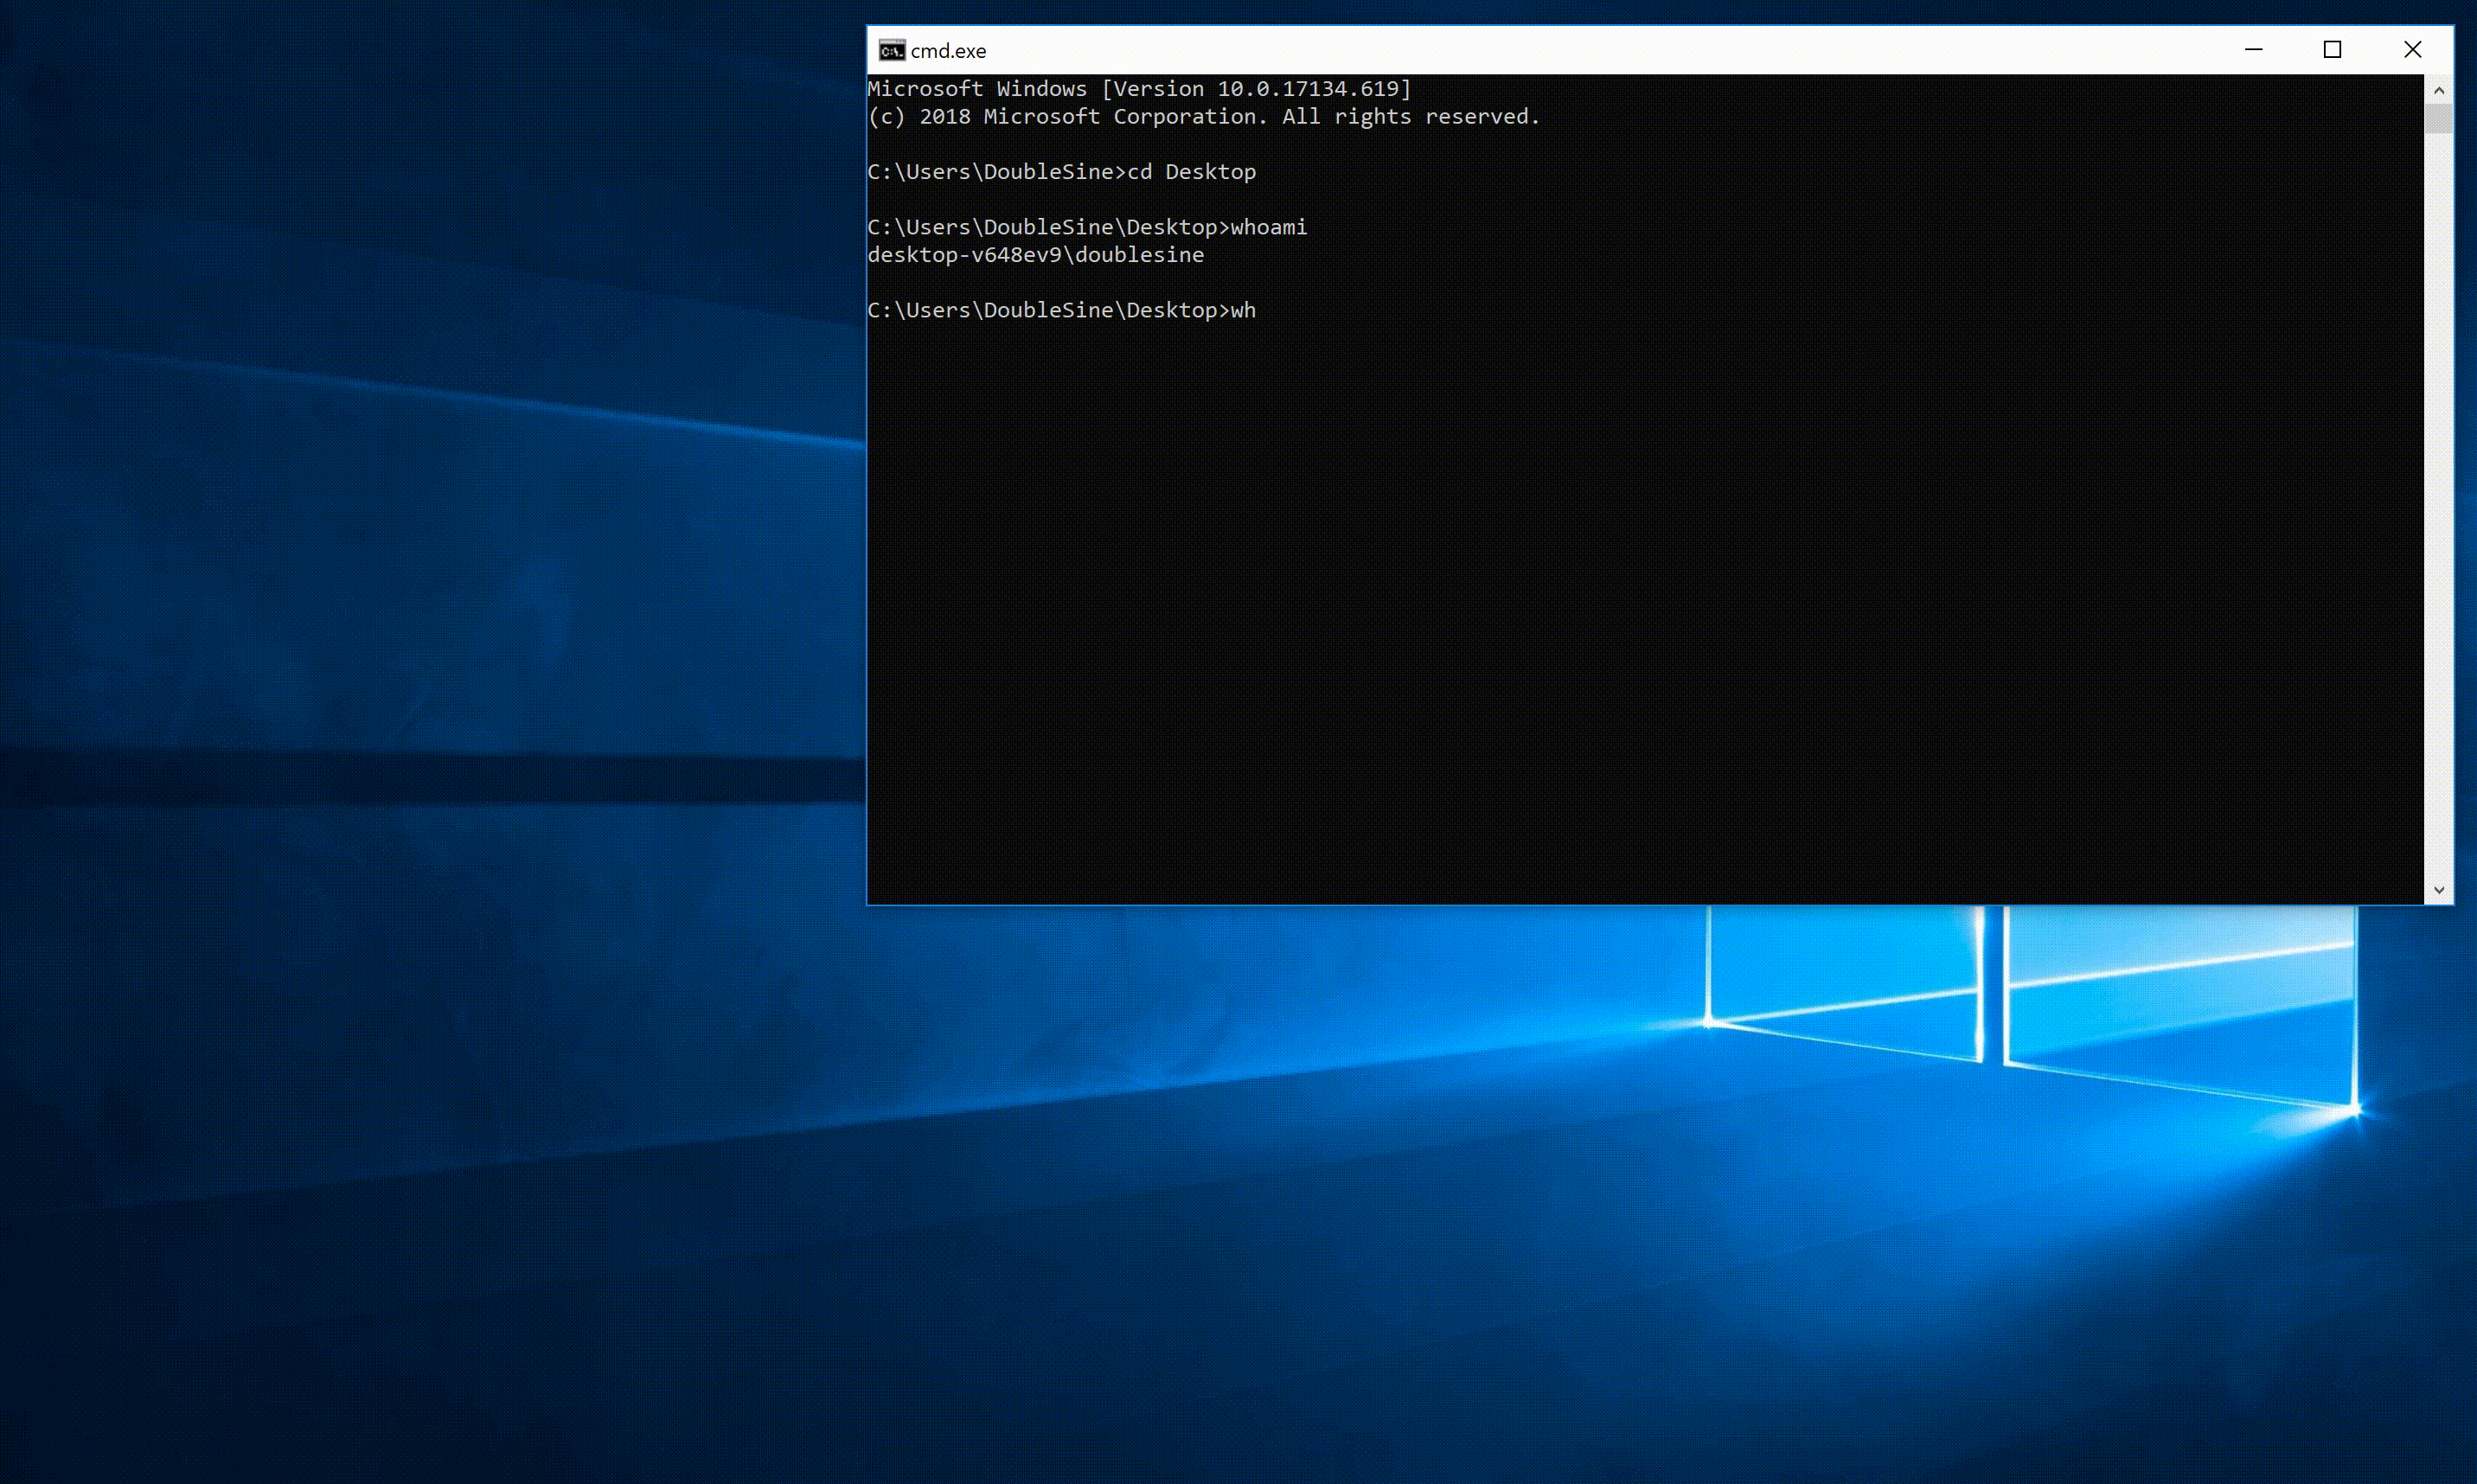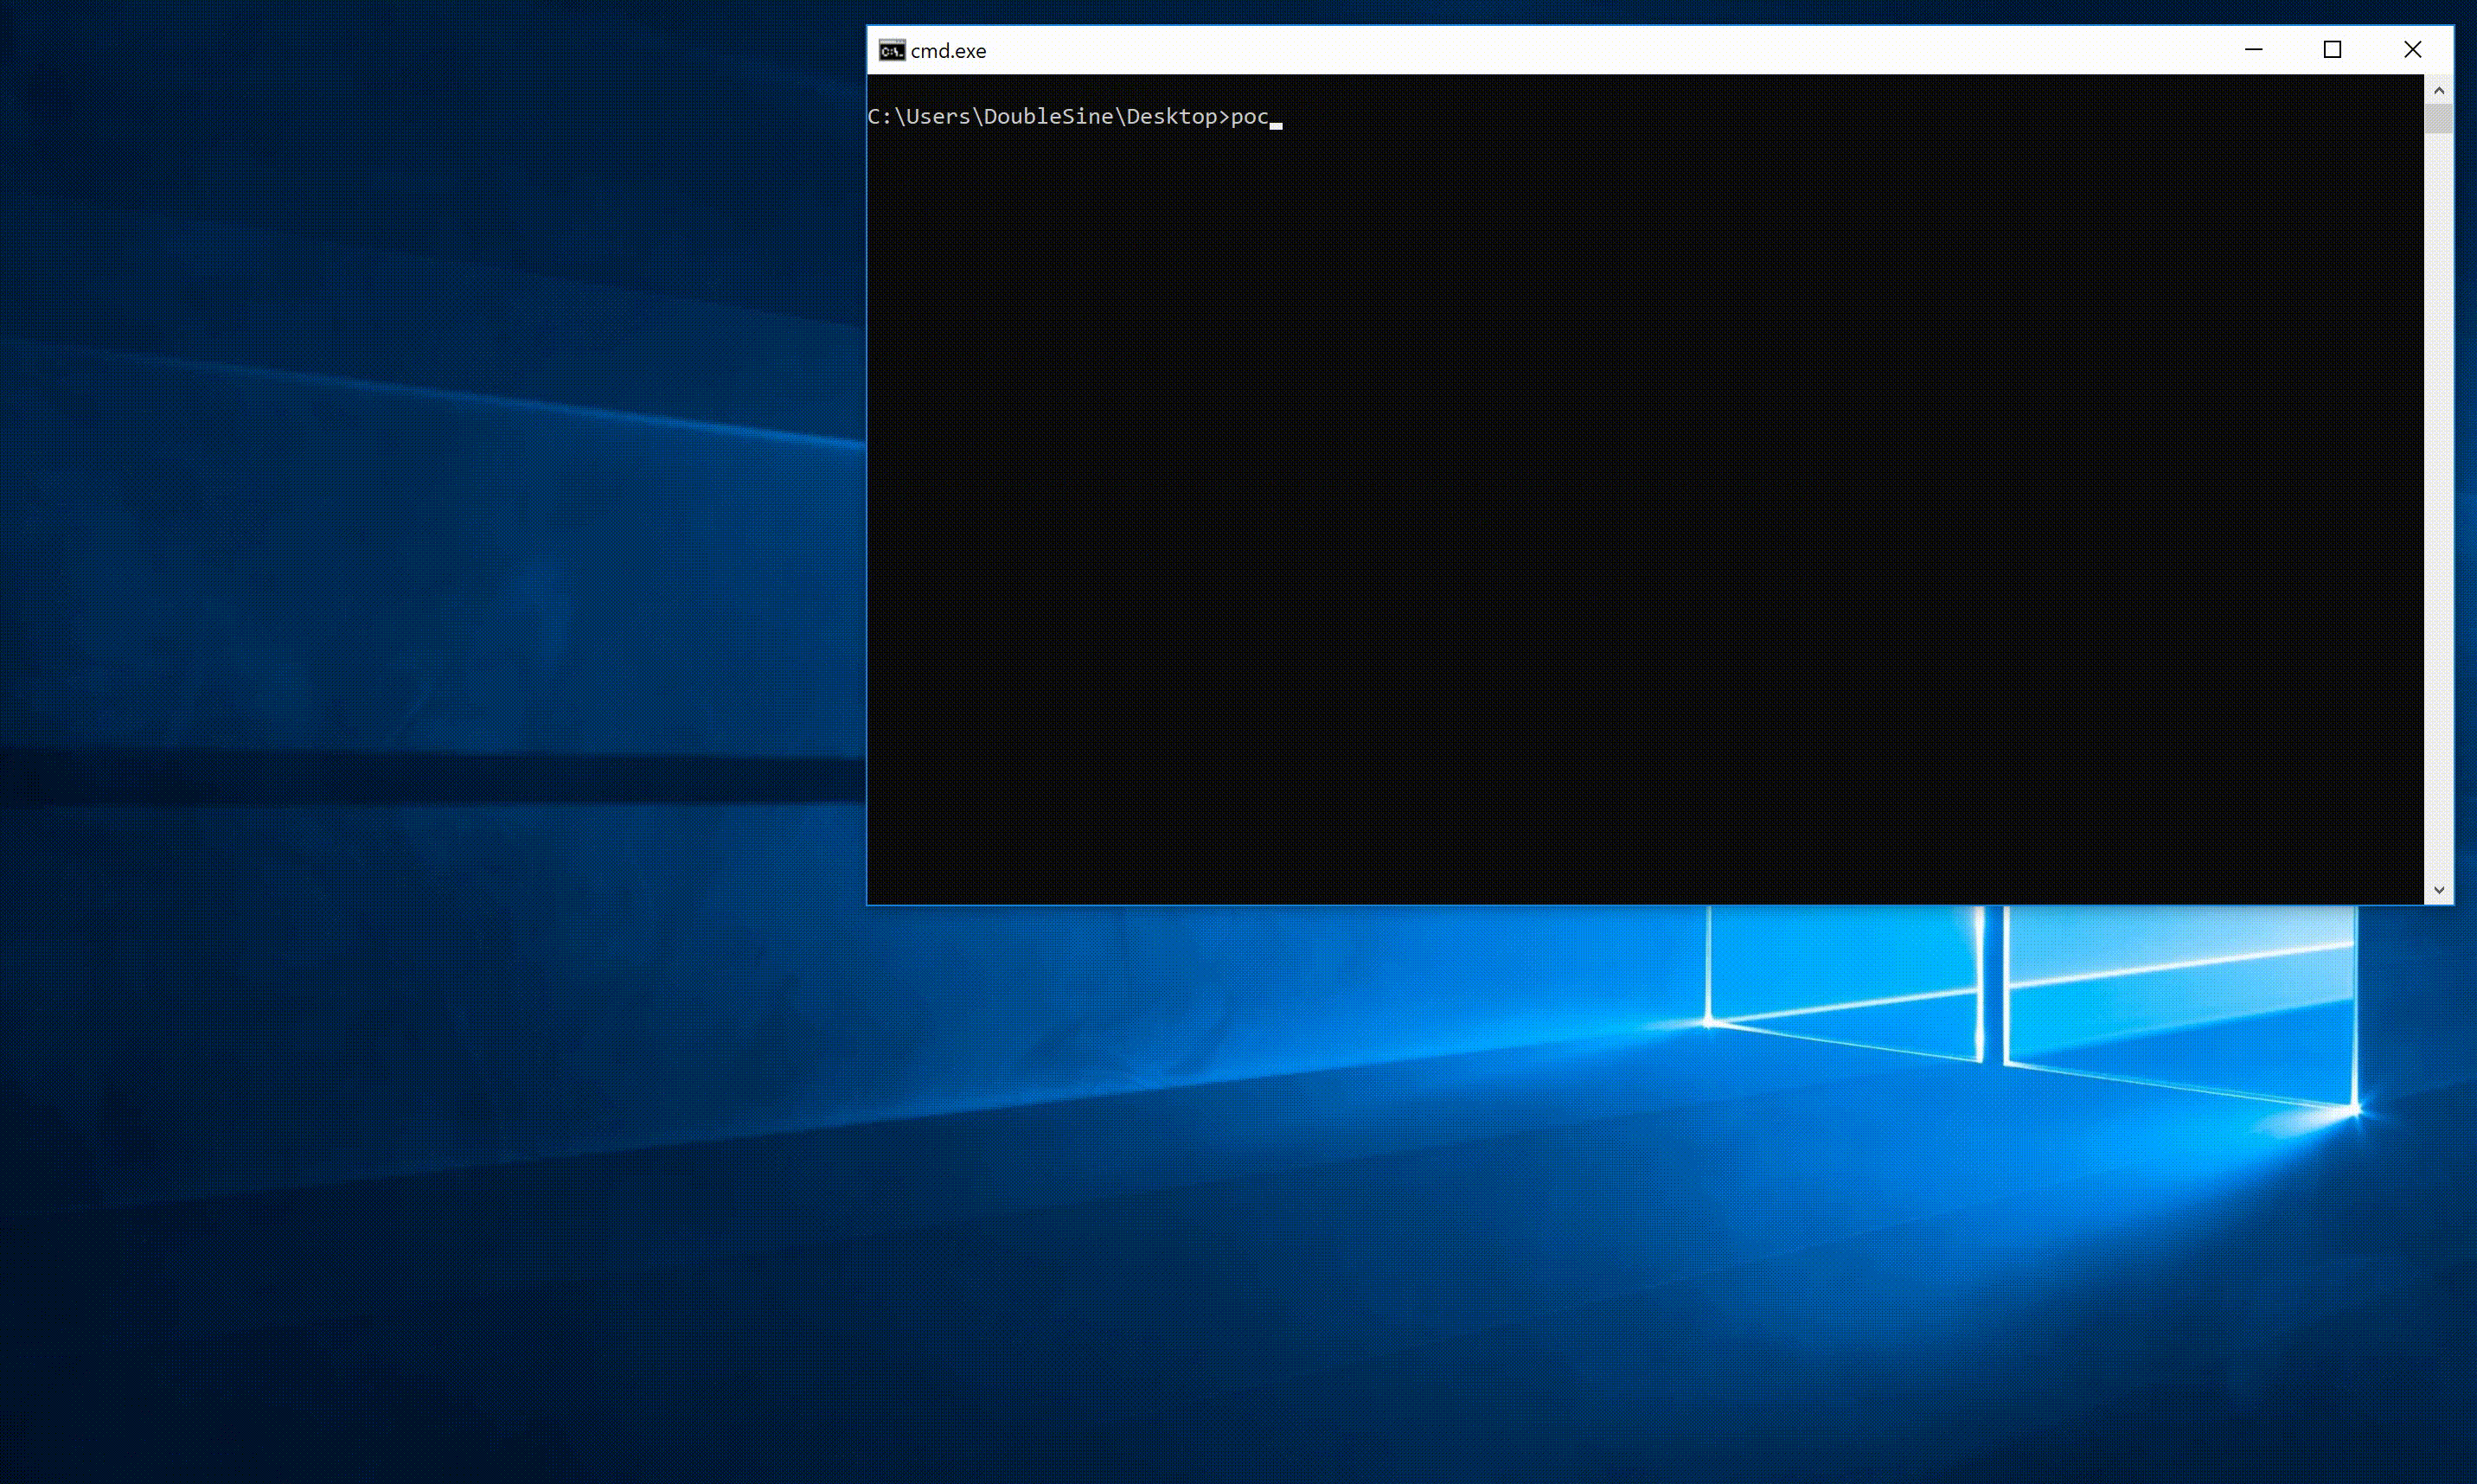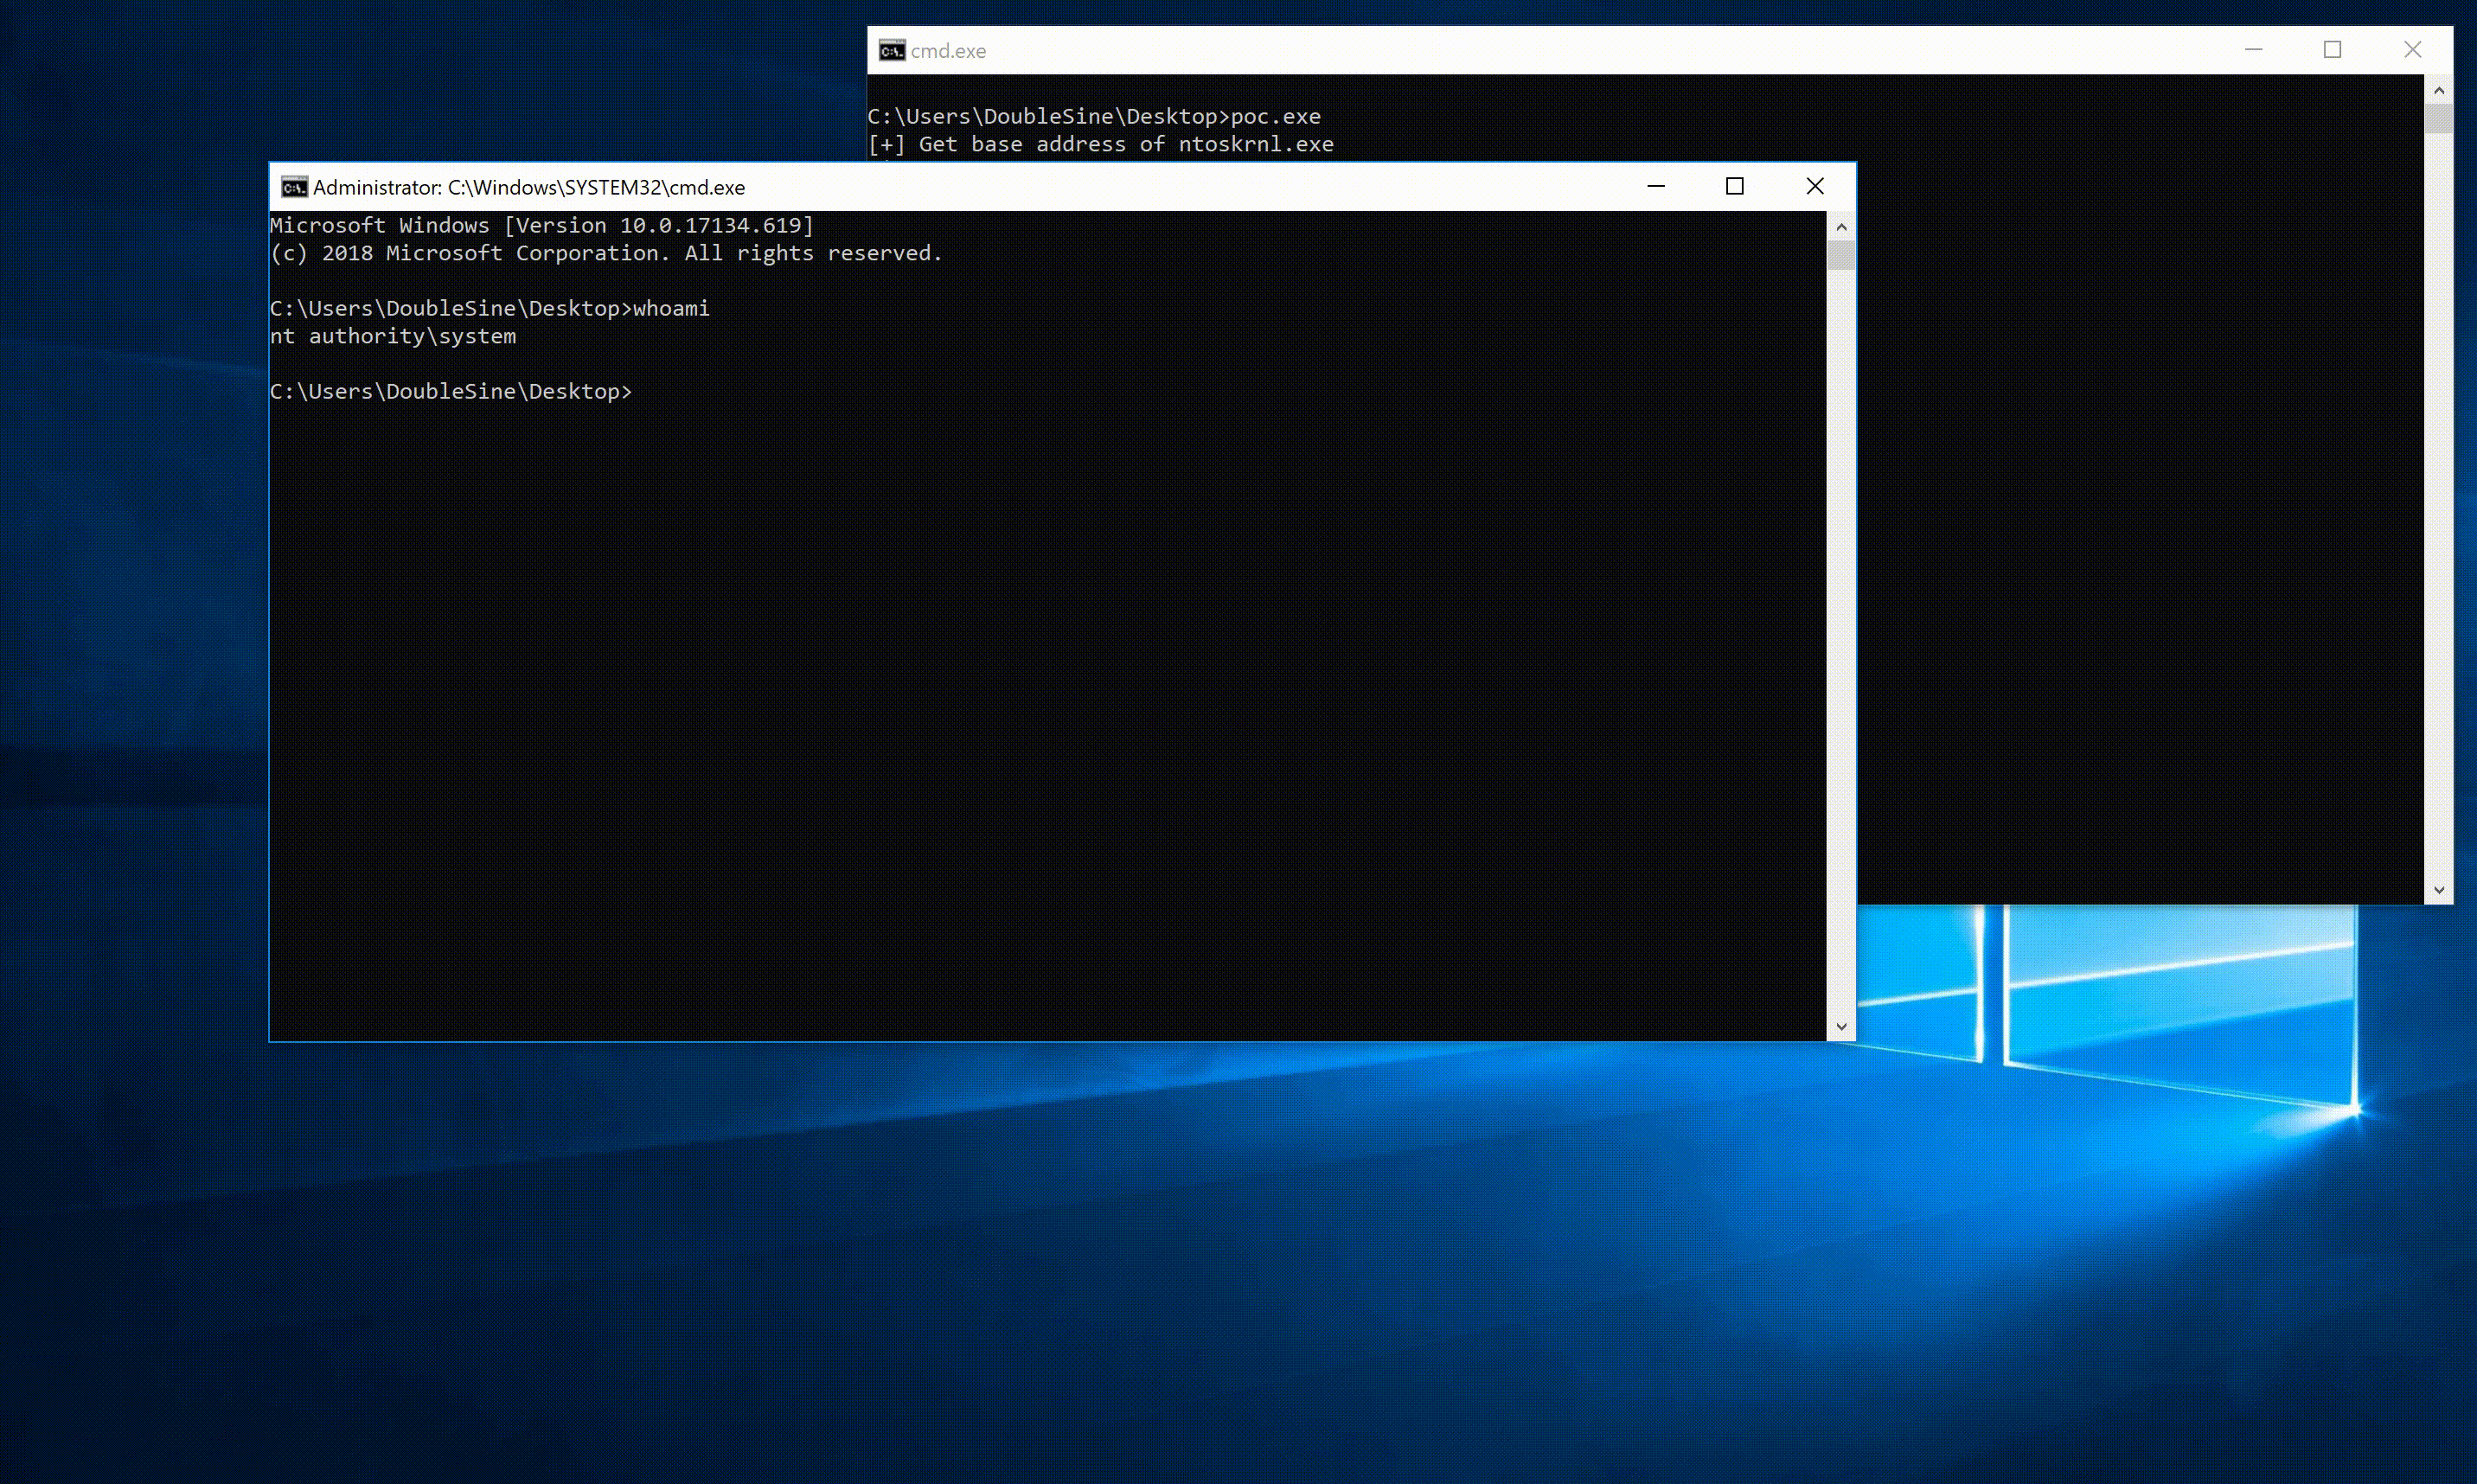 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
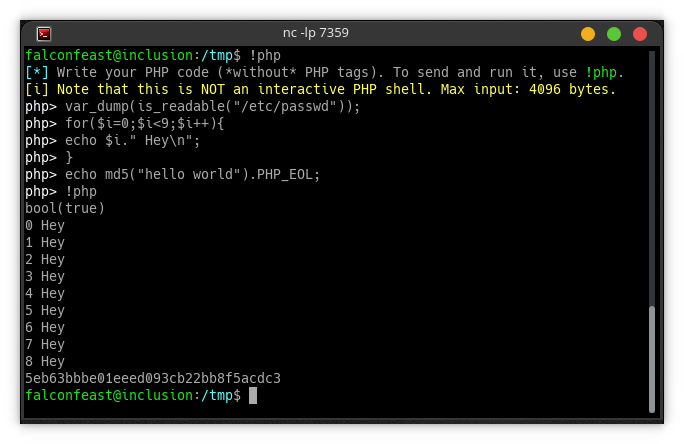 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
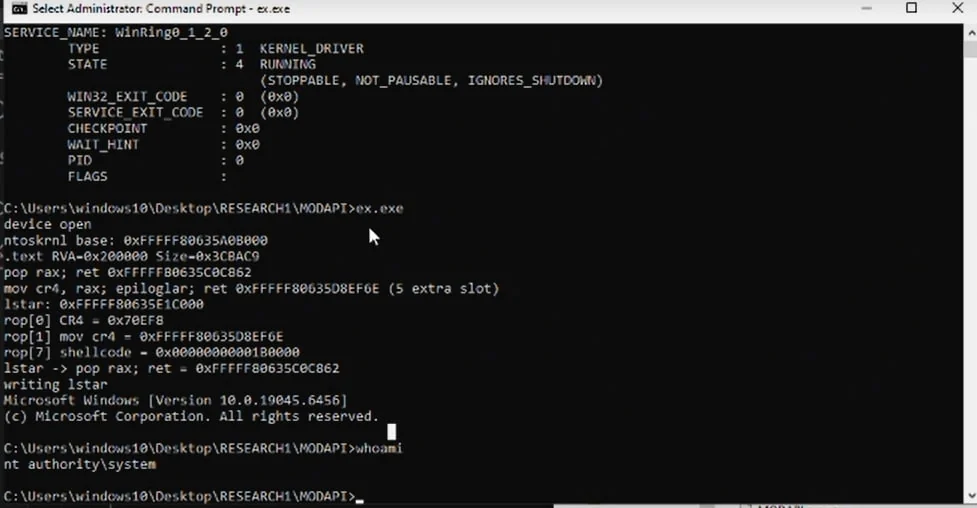 mein-0/lolmodapi
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 milo-d/cve-2016-6187_lpe
Kernel Exploit for CVE-2016-6187 (Local Privilege Escalation)
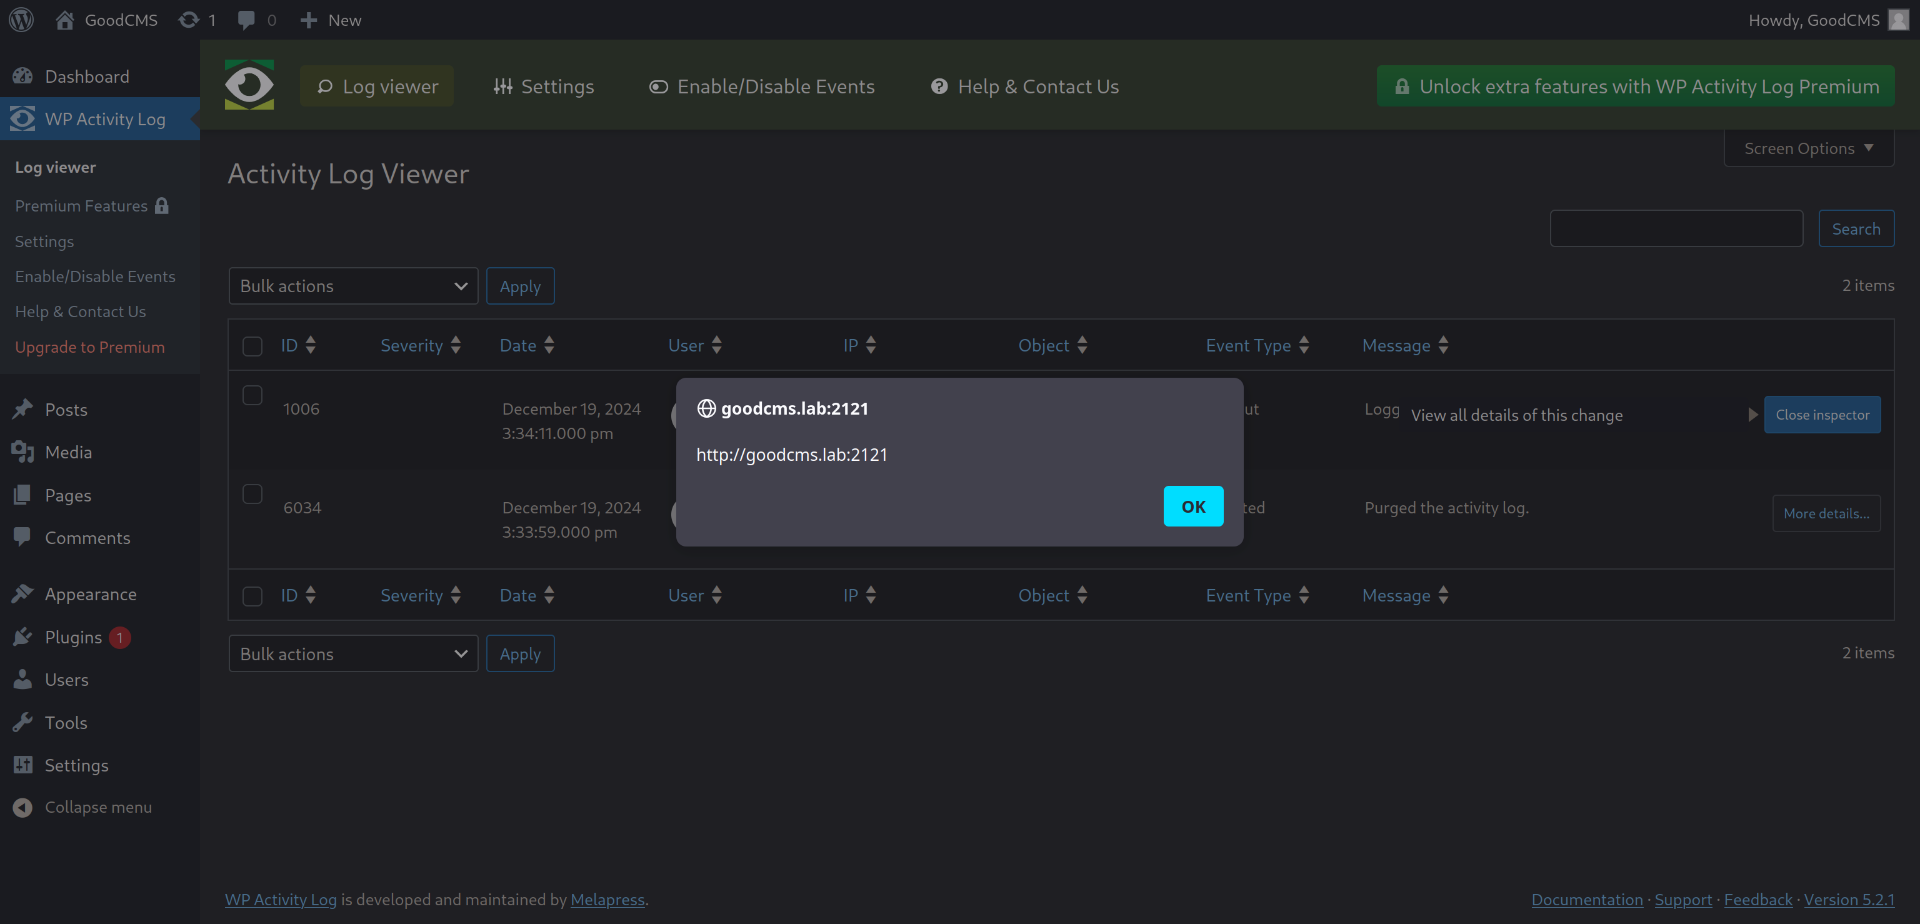 mahajian/cve-2024-10793
Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…
 luke0x90/cve-2021-21551
Proof-of-concept exploit for CVE-2021-21551: Windows local privilege escalation via Dell dbutil_2_3.sys driver. Implements read/write primitives,…