Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
275 results
CVE-2003-0264_EXPLOIT preview

CVE-2003-0264_EXPLOIT

GitHubvrikodar/cve-2003-0264_exploit

Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
binary-exploitationdebuggerseducation+5
5 years ago
CVE-2023-4911 preview

CVE-2023-4911

GitHubguffre/cve-2023-4911

Python-based proof-of-concept exploit for CVE-2023-4911 (Looney Tunables) targeting glibc dynamic loader's parse_tunables() for local privilege…

binary-exploitationexploitationpayload-development+3
2 years ago
CVE-2009-1330 preview

CVE-2009-1330

GitHubadenkiewicz/cve-2009-1330

Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.

binary-exploitationexploitationpayload-generation+3
7 years ago
HackerLife.exe preview

HackerLife.exe

GitHubspiralbl0ck/hackerlife.exe

Write up exploit failed chain and experience tryin to sell your first nday

binary-exploitationeducationexploitation+5
1 year ago
CVE-2017-16994 preview

CVE-2017-16994

GitHubjedai47/cve-2017-16994

Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…

binary-exploitationexploitationmemory-forensics+2
2 years ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
94 days ago
CVE-2015-8522.RCE preview
Archived

CVE-2015-8522.RCE

GitHubdamariion/cve-2015-8522.rce

Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…

binary-exploitationexploitationexploit-frameworks+8
5 months ago
avscript preview
Archived

avscript

GitHubtaviso/avscript

Avast JavaScript Interactive Shell

binary-analysisdebuggersexploitation+5
6736 years ago
EvilVM preview

EvilVM

GitHubjephthai/evilvm

Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…

command-and-controlexploit-frameworkspayload-development+7
2084 years ago
AVIator preview
Archived

AVIator

GitHubch0pin/aviator

Antivirus evasion project

encryption-decryption-toolsexploit-frameworkspayload-generation+3
1.2k1 year ago
Phantom-Evasion preview
Archived

Phantom-Evasion

GitHuboddcod3/phantom-evasion

Python antivirus evasion tool

dynamic-analysis-sandboxingexploit-frameworkspayload-development+6
1.4k2 years ago
CVE-2019-12735 preview
Archived

CVE-2019-12735

GitHubst9007a/cve-2019-12735

A demo for cve-2019-12735
binary-exploitationeducationexploitation+3
4 years ago
HRShell preview
Archived

HRShell

GitHubchrispetrou/hrshell

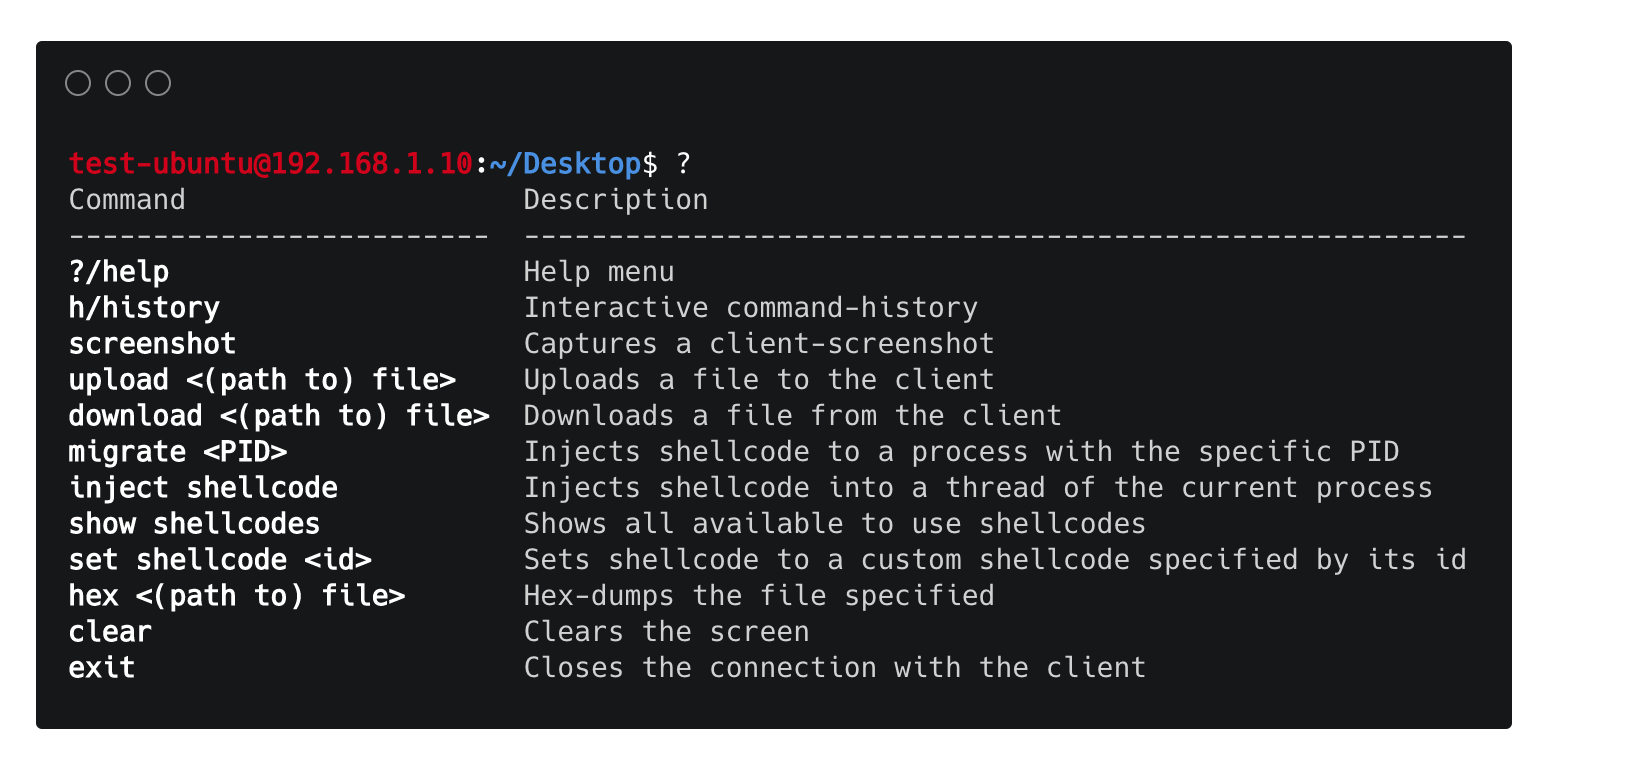
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
command-and-controlencryption-decryption-toolsexploitation+7
2485 years ago
Cmulator preview
Archived

Cmulator

GitHubcoldzer0/cmulator

Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…

binary-analysisdebuggersdynamic-analysis-sandboxing+4
3044 years ago
flare-ida preview
Archived

flare-ida

GitHubmandiant/flare-ida

IDA Pro utilities from FLARE team
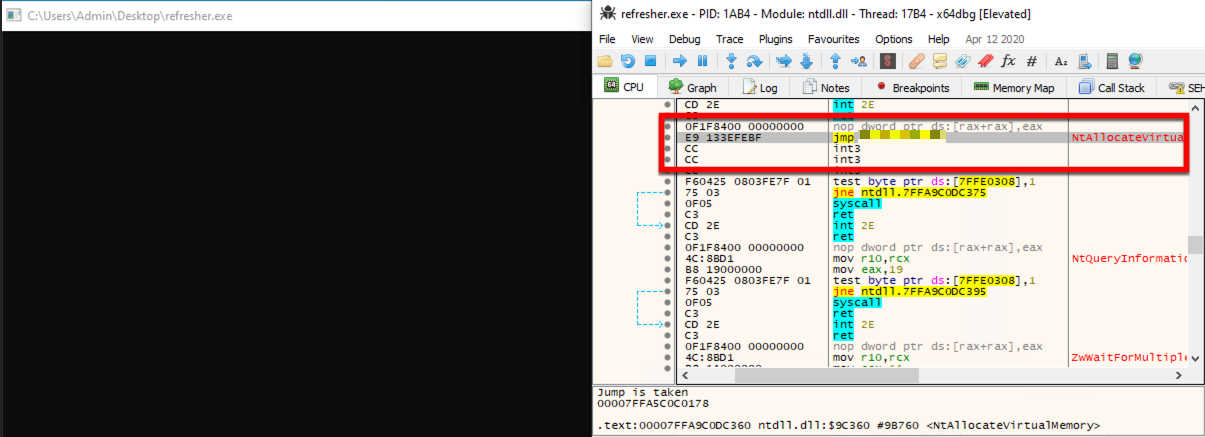
binary-analysisdebuggersdynamic-analysis-sandboxing+3
2.5k1 year ago
ScareCrow preview
Archived

ScareCrow

GitHuboptiv/scarecrow

ScareCrow - Payload creation framework designed around EDR bypass.
exploit-frameworkspayload-developmentpayload-generation+3
2.9k3 years ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
binary-exploitationdefensive-toolseducation+7
4311 days ago
Ivy preview
Archived

Ivy

GitHuboptiv/ivy

Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…

exploitationpayload-developmentpayload-generation+4
7433 years ago
Previous1…141516Next